

Interactive Sandbox & Threat Intelligence trusted by 16K+ SOC & MSSP teams. Triage and respond to phishing & malware faster: https://teapawt.net/t.co/DHC75KqDh1
Joined February 2017
- Tweets5.6K
- Following192
- Followers34.7K
- Likes6.7K





Pinned Tweet
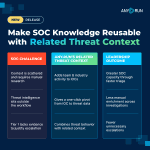
🚀 𝗕𝗜𝗚 𝗡𝗘𝗪𝗦: Introducing Related Threat Context, Your New MTTR Shortcut.
SOC & MSSP teams used to manually rebuild the picture around every suspicious IOC. With this new #ANYRUN update, you can see related team analyses, historical context, and industry-related activity for every IOC and uncover related infrastructure in one connected workflow.
⚡️ 𝗜𝘁’𝘀 𝗿𝗲𝗮𝗹𝗹𝘆 𝘀𝗶𝗺𝗽𝗹𝗲: review the context around each indicator in the Sandbox, then pivot to TI Lookup in one click to uncover additional threat activity and give Tier 1 evidence to justify escalation.
See the workflow in action and try it yourself: app.any.run/tasks/390e708f-2…
🔍 Connected context brings a whole new level of speed and clarity to triage: faster decisions, fewer uncertainty-driven escalations, more focused use of Tier 2 expertise, better knowledge reuse across shifts, and stronger visibility into industry-relevant activity.
🎉 𝗧𝗵𝗲 𝘁𝗿𝗶𝗮𝗴𝗲 𝗯𝗼𝗼𝘀𝘁 𝘆𝗼𝘂’𝘃𝗲 𝗯𝗲𝗲𝗻 𝘄𝗮𝗶𝘁𝗶𝗻𝗴 𝗳𝗼𝗿 𝗶𝘀 𝗵𝗲𝗿𝗲. Explore Related Threat Context in your security workflows: any.run/cybersecurity-blog/r…

🚨 US SOC teams are drowning in alerts. But the real bottleneck is manual checks, fragmented evidence, and escalations without context.
❗️ Explore five pain points holding US security operations back and practical ways to make investigations faster: any.run/cybersecurity-blog/u…

❗️ A breach can start with an alert your team can’t validate fast enough.
#ANYRUN TI Feeds bring fresh, investigation-backed IOCs into SIEM, SOAR and EDR workflows.
⚡️ Enrich alerts before manual investigation begins: any.run/threat-intelligence-…

🚨 The danger behind fake job interviews has once again put North Korean cyber operations in the spotlight. But how do these actors actually gain access and operate?
⚡️ Get a rare look inside DPRK operations with hours of footage capturing attackers in action:
1️⃣ Inside the fake IT worker scheme: We recorded Famous Chollima operatives in action, revealing the fake identities, remote-access tools, and infrastructure behind their operation. Learn more: any.run/cybersecurity-blog/l…
2️⃣ An insider at work: Researchers hired IT workers into a fake DeFi startup, revealing what they did after gaining access to development environments, accounts, and code. Learn more: any.run/cybersecurity-blog/l…
3️⃣ From fake meeting to compromise: The investigation into Lazarus’s Mach-O Man malware kit reveals how fake meeting invitations lead to credential theft, browser session collection, and data exfiltration. Learn more: any.run/cybersecurity-blog/l…
❗️ The tactics may differ, but the goal is the same: use trust to get inside a company’s systems and reach valuable data. Use these investigations to assess your exposure and strengthen detection and response to Lazarus-linked threats.

👨💻 NIS2 puts cybersecurity effectiveness in focus for EU organizations.
Can your security stack prove it meets the standard?
See how independent threat intelligence helps support compliance, strengthen security, and improve ROI 👇
any.run/cybersecurity-blog/t…

🏦 A 12-person bank SOC team was overwhelmed by alerts and couldn’t see what suspicious files did.
✅ In week one with #ANYRUN Interactive Sandbox, it processed alerts 2× faster. Email API integration automated submissions, while interactive analysis replaced environments that took a week to prepare.
🔥 Over 18 months, it stopped hundreds of ransomware and credential-theft attempts, including a loader hidden in a password-protected supplier ZIP.
🔍 #ANYRUN Threat Intelligence provided fresh IOCs, enriched context, and real-time finance-threat monitoring.
📈 See how #ANYRUN supports financial institutions: any.run/by-industry/finance/…

📈 What does it take to scale without sacrificing service quality?
This US MSSP knows the answer.
⚡️ See how actionable threat intelligence helped a five-analyst SOC handle 30% more alerts while maintaining SLA quality ⬇️
any.run/cybersecurity-blog/u…

🚨 #Formbook is targeting European businesses with localized order and procurement lures.
Discover how obfuscated JavaScript, PowerShell loaders, process hollowing, and browser credential theft drive this multi-stage attack.
Read the full analysis 👇
any.run/cybersecurity-blog/f…


Explore how to add first-hand threat intelligence to your existing security workflows with #ANYRUN 👇
any.run/cybersecurity-blog/h…

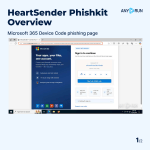
🚨 We’re tracking the #HeartSender phishkit, with 52% of activity concentrated in the US over the past six months. It uses Microsoft 365, Google, and other branded phishing pages for Device Code and credential-harvesting flows.
👨💻 Review the phishing flow and collect #IOCs: app.any.run/tasks/3f353cd4-c…
⚠️ Across versions, its pages call shared admin infrastructure: /assets/js/mg.js connects to office-panel[.]com, while another version uses office-token[.]com. This gives analysts a durable pivot even when the lure or authentication flow changes.
⚡️ With #ANYRUN’s new Related Threat Context, office-panel[.]com becomes a pivot from one phishing page to industry-related activity and #ANYRUN Threat Intelligence.
🔍 One click opens TI Lookup, where analysts can trace recurring endpoints and shared admin infrastructure to expand the HeartSender cluster: intelligence.any.run/analysi…
#ExploreWithANYRUN 1/2 🧵

❗️ Despite 2025 arrests, the service and its related phishing infrastructure remain active: sales channels still offer phishing panels, SMTP access, and logs.
The panel lets operators switch phishing themes on the same URL in real time, helping campaigns adapt without rebuilding delivery infrastructure.
💡 #IOCs:
office-panel[.]com
office-token[.]com
103.153.182[.]197
🚀 Strengthen phishing detection in your SOC with #ANYRUN: any.run/use-case/phishing/?u…
#ExploreWithANYRUN 1/2 🧵

Phishing activity in the past 7 days 🐟
Track latest #phishing threats in TI Lookup: intelligence.any.run/analysi…
#TopPhishingThreats


Explore how to reduce repeat research and build a more consistent SOC workflow with #ANYRUN 👇
any.run/cybersecurity-blog/r…

🚨 #SkyW4lker uses business-themed phishing lures and fraudulent device-code authentication to compromise M365 accounts, putting corporate identities, mailboxes, and sensitive documents at risk.
Understand the threat and the signals that expose it: any.run/malware-trends/skyw4…

⚠️ Malware activity shifted toward loaders and stealers last week. #DonutLoader surged 85%, #AgentTesla climbed 65%, and #ReverseLoader gained 54%. Meanwhile, #AsyncRAT rose 28% as #Remcos and #XWorm declined.
📌 Trend to watch: growing loader activity puts more focus on the early stages of infection. For SOC teams, investigating execution chains and follow-on payloads can help identify the full scope of a threat before containment decisions are made.
Monitor the malware driving today’s attacks: any.run/malware-trends/?utm_…
#Top10Malware

❗️ AI can reduce repetitive SOC work, but a phishing alert can still look harmless until someone opens the file, follows the embedded link, and gets past a CAPTCHA — time Tier 1 analysts rarely have.
With Automated Interactivity enabled, #ANYRUN Sandbox opens a legitimate Adobe-hosted PDF, follows its embedded URL, and exposes the Microsoft OAuth phishing flow in this #SkyW4lker case. See it in action: app.any.run/tasks/2573e1ee-3…
⚡️ #ANYRUN's new Related Threat Context then surfaces 70+ related analyses, while a SOC-ready Tier 1 Report combines the evidence with an AI Summary & Recommendations for the next steps, helping analysts make faster decisions and give Tier 2 a documented starting point instead of repeating the initial analysis.
🚀 How to turn AI capabilities into faster, evidence-backed SOC decisions: any.run/cybersecurity-blog/a…


👨💻 Better threat coverage starts at the source. When new malicious infrastructure is already visible in your telemetry but absent from feeds, analysts have to close the intelligence gap manually.
Where does late intelligence hurt your SOC first?
12%Slower triage
75%More manual IOC checks
0%Delayed containment
12%Missed detections
8 votes • Final resultsHow to close threat intelligence blind spots with fresh, validated indicators 👇
any.run/cybersecurity-blog/h…
🚨 Active in the US: Multi-stage #RGBLoader reconstructs .NET payloads from image pixel data and executes them directly in memory.
The chain changes extraction techniques across three stages: Bitmap RGB values ➡️ .NET Stage 2 ➡️ ARGB pixel data + XOR ➡️ .NET Stage 3 ➡️ encrypted byte array from .NET resources ➡️ final payload.
👨💻 Explore the full in-memory #DarkCloud delivery chain and collect IOCs in #ANYRUN Sandbox: app.any.run/tasks/5ae24575-7…
⚠️ RGBLoader also delivers #MassLogger, #SnakeKeylogger, #Quasar, #Remcos, cryptominers, and other malware:
🔷 #Formbook: app.any.run/tasks/648e990d-5…
🔷 #XWorm: app.any.run/tasks/2b69f5c9-b…
❗️ #RGBLoader passes configuration between stages to locate and decode payloads, then launches them in memory through Assembly.Load() and reflection. As names vary by sample, static strings alone can miss variants. Hunt for pixel extraction, staged .NET loading, and XOR-decoded resources.
🔍 Pivot from #IOCs and track related activity and evolution in TI Lookup: intelligence.any.run/analysi…
⚡️ See how #ANYRUN helps SOC teams detect and investigate complex threats faster: any.run/enterprise/?utm_sour…
#ExploreWithANYRUN

🔄 #ANYRUN TI Feeds turn IOCs into continuous monitoring by streaming fresh, validated indicators and behavior-based threat data into your security stack.
🔍 #IOCs:
85d1791847636949606bc1c87cdbfe019a43c5723333971dc820963016000c1b
5240b38a9efe67747c29da0026e03421942d4bb76d5619ed398e854480f6a076
38173492fece33a703a67140785e02cbd0749329b7cd9433bb7e122fbb9f803a
676e61504a6d6ab4d90b5068bc487fb19c804b0b1ef0db814aa04fbe035195dd
cdcd92f9e3af2925829eaf9e8d366ae2e750bded64d212484995378eb1839025
66d3101e3b2207acdbdd9d0c14a1c3ea064e14a771705d8a4583faecaba98544
7250576a3cb7164bf383d89683267604dd1a5d36e1a35f22b5bef2d9f29402e5
5da16030099b484460213d2031dc3683197eedbe54517c23e440f4f5af4c5daa
#ExploreWithANYRUN