

Delivering #LibericaJDK: supported, @Java standard compatible binaries. Among Top-5 @OpenJDK contributors.
San Jose, CA
Joined January 2018
- Tweets1.7K
- Following375
- Followers4.1K
- Likes1.2K



44% of Java developers we surveyed at Devoxx Belgium would let AI approve a pull request without human review in some cases. Fewer than 1% said their team already does.
See what teams do delegate to AI in code review in our free report:
bell-sw.com/state-of-ai-in-j…
1
132
Liberica JDK November CSPU updates are out for Java 6, 7, 8, 11, 17, 21, 25, and 27.
11 CVEs addressed and 111 fixes overall, with BellSoft contributing to 21 resolved issues.
The release also includes the Java4Shell fix for affected Java 17+ builds.
Details: bell-sw.com/blog/liberica-jd…
Download: bell-sw.com/pages/downloads

Java4Shell, CVE-2026-114938, is a memory corruption bug in Java’s built-in Base64 decoder.
Affected deployments depend on the JDK build, x86-64/AVX-512, and whether untrusted Base64 input reaches the vulnerable path. Updating app dependencies won’t fix a JDK-level flaw.
Liberica JDK guidance and temporary mitigations:
bell-sw.com/blog/addressing-…

Why can the same request get faster after your Java app has been running for a while?
@cat_edelveis explains what the JVM is still doing after startup in her guide to the JDK, JRE and JVM.
youtu.be/3KxfvBWL1OY
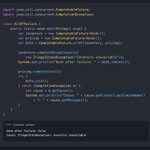
CompletableFuture.allOf() returns a future that completes only after all supplied futures complete, even if one fails.
Here, inventory completes exceptionally, but both remains incomplete until pricing completes. Calling join() then throws CompletionException, with the original IllegalStateException as its cause. #Java

Taking a Spring Boot app to production in Docker? @cat_edelveis builds the same app with a Dockerfile and with Paketo Buildpacks. Pick the version that matches your setup and follow along.
youtu.be/FaNxoP41fIM
Java, Kotlin, JavaScript, TypeScript, Python. One toolchain.
Tomorrow, Catherine talks with Sam Gammon, founder of Elide, about building and running polyglot applications and what happens to performance when multiple language ecosystems share a runtime.
Join us live tomorrow: youtube.com/watch?v=fjlS_-BP…

1
232
SSHole (CVE-2026-123158) can bypass OpenSSH password authentication on some musl-based Linux systems running without PAM.
BellSoft shipped fixed packages for every supported Alpaquita branch within a day of disclosure. If you run sshd, update OpenSSH and restart the service.
Details and affected configurations: bell-sw.com/blog/securing-al…

50 MB is possible for a real Java REST service.
But once you assess the footprint gains against the trade-offs, things get interesting.
@cat_edelveis tested it with Spring Boot and Quarkus:
youtu.be/2f0LUg5_GvQ
Catch potential NullPointerExceptions while building your Java app.
@cat_edelveis shows how to set up JSpecify + NullAway and try them on a Spring Boot project with a deliberately planted null bug.
Follow the tutorial: bell-sw.com/blog/java-nullpo…

Our Spring container security survey found that 64% of respondents did not recognize how Dockerfile maintenance can affect security.
InfoQ picked up that number in a new piece on patching at scale.
With dozens or hundreds of services, base-image updates stop being a repo-by-repo task and become a platform problem. The article shows where buildpacks fit into that shift:
infoq.com/news/2026/08/build…

8
271
What happens when a value object reaches synchronized through an Object reference? With JDK 28 preview features enabled, only identity objects have monitors. If the reference points to a value object, monitor acquisition throws IdentityException.
Use a separate identity object when you need a lock. #Java

Migration to buildpacks can be smooth.
@cat_edelveis shows how to choose a starting point, switch from a Dockerfile to buildpacks, and test the new image before deployment.
Read the guide: medium.com/buildpacks/migrat…

3
239
Liberica JDK updates addressing compromised eMudhra certificate chains are now available.
Fixed builds: 8u513+9, 11.0.33.0.3+7, 17.0.21.0.3+5, 21.0.13.0.3+5, 25.0.5.0.3+5, and 27.0.1.0.3+5.
Download: bell-sw.com/pages/downloads

Couldn’t make it to @Devoxx? Catch @asm0di0’s Mission Possible on video.
Pasha tackles a Java container image full of CVEs and shows the changes that reduce its exposure, with Dockerfile examples you can reuse.
Watch here: youtu.be/1yndLHw9mbo
3
187
You can try JSpecify without annotating your whole Java project.
@cat_edelveis starts with one package and uses NullAway to catch a bug that would otherwise crash the app.
See how to get the checks working: youtu.be/Ymx4hwCsia4
Liberica JDK CPU and PSU updates are out for 6, 7, 8, 11, 17, 21, 25, and 27.
52 CVEs addressed and 1438 fixes and backports overall, with BellSoft contributing to 144 resolved issues.
Details: bell-sw.com/blog/liberica-jd…
Download: bell-sw.com/pages/downloads

Security alert: Mitigate risk from compromised eMudhra certificate chains in your Java apps.
Liberica JDK updates are underway. To protect your systems now, check your JDK and container images and apply the temporary mitigation:
bell-sw.com/blog/distrusting…

