

Trusted by Coinbase, MetaMask, Stellar, and more to detect, understand, and protect against fraud, scams, and exploits in real time.
New York & Tel Aviv
Joined February 2023
- Tweets1.9K
- Following447
- Followers26.8K
- Likes1.7K




Pinned Tweet
The biggest theft in crypto history: an attacker hijacked Binance’s signing service and drained $6.3B from its hot wallets.
Using advanced AI models and our industry-leading exploit detection engine, Blockaid detected it in under two minutes.
Read more: blockaid.io/blog/binance-55b…

🚨 Community Alert: Our system has detected a potential frontend attack targeting @flapdotsh and @Kintsu:
• flap[.]sh
• kintsu[.]xyz
Please refrain from signing transactions and avoid interactions with these dApps until the issue is resolved.
In addition to our earlier alert, the same attack has now been identified on additional sites. These are actively serving the Step Drainer:
• stonkfun[.]xyz
• pickle[.]finance
• echelon[.]market
• origami[.]finance
• fluxbeam[.]xyz
• stakepoint[.]app
• supswap[.]xyz
• longbow[.]cash
• shprd[.]finance
• apexdefi[.]xyz
We’re actively investigating and gathering more data.
“It’s no coincidence that the largest hacks in the history of the world have happened over the past months. We saw it with Binance, we had it with Bitget, we had it with Bybit.” - @idobn, Blockaid Co-Founder and CEO, on @CNBC this morning.
- Binance: $6.3B
- Bybit: $1.5B
- Bitget: $350M
Three exchanges share one root cause, with each drain traced back to an operational security failure that led to unauthorized signing.

Yesterday’s $6.3B Binance hack was the largest in history. With advancements in AI, over the last year exploits have continued to get larger and increasingly sophisticated.
AI-powered exploits are only going to accelerate, and detection has to run in real time to keep up. I joined @CNBC this morning to break it down:
Blockaid retweeted

🚨 INSIGHT: Ethereum’s EIP-7702 didn’t cause Binance’s $6.3B hack but may have helped attackers bypass security checks and drain funds in one sweep, @blockaid_ CEO Ido Ben-Natan tells Cointelegraph.
ct.com/news/binance-hack-sec…

Blockaid retweeted

Existing security solutions could have prevented this hack...
"The delegation transaction was the point where this attack could have been stopped. Blockaid's transaction security engine classified the type-4 transaction that delegated Binance 14 as malicious on sight"

The biggest theft in crypto history: an attacker hijacked Binance’s signing service and drained $6.3B from its hot wallets.
Using advanced AI models and our industry-leading exploit detection engine, Blockaid detected it in under two minutes.
Read more: blockaid.io/blog/binance-55b…
Use our tool to see where the stolen Binance funds are right now and check your own addresses against the ones tied to the attack:
binance-hack-funds.blockaid.…

Six months ago we launched our Risk Exposure product on one belief: tracing stolen funds after the fact is not enough. Exposure has to be flagged in real time, while the funds are still in flight.
Yesterday, our AI models flagged the Binance drain at 20:26 UTC, under two minutes after the first sweep and before any public report, within seven seconds after that detection, the findings had propagated into Risk Exposure.
We are actively tracing fund movement across nine chains and counting, from the first collector through each hop to where the funds sit now.
Use our tool to trace the funds and check your own addresses against the 72 tied to the attack:
binance-hack-funds.blockaid.…
Blockaid retweeted

For financially motivated attackers, crypto is a primary target.
With the rise of AI, we're only going to see more of these.


Blockaid retweeted

Crypto is the money agents will choose.
As agents become better at cyber than humans, crypto will continue to be the most targeted infrastructure in the world.
Now by DPRK, in the future by Super intelligence agents

Blockaid retweeted
The common thread across the biggest hacks in history - blind signing.
Attackers are financially motivated, stealing the actual private key is hard, causing the signer to sign a malicious payload is the chosen attack vector.
Every signer needs to simulate and validate transactions using @blockaid_!

Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
binance.com/en/support/annou…

Blockaid retweeted
Using advanced AI models @blockaid_ detected what is likely the biggest hack in the history of the world.
We are investigating a cluster of large outflows from Binance hot wallets that began at approximately 20:24 UTC on 29 October 2026. On-chain, the transfers look consistent with unauthorized movement from those wallets, but this has not been confirmed by Binance, and we cannot yet rule out an internal treasury or operational sweep.
Observed chains: Ethereum, Arbitrum, and Avalanche, with related receipts also visible on Optimism.
Observed scale (approximate, still being reconciled):
Ethereum: about $2.5 billion from Binance 14 and Binance 16, plus an additional 780,000,000 USDC from a Binance smart account
Arbitrum: about 8,426 ETH (~$19.5 million)
Avalanche: about 1.81 million AVAX and 8.4 million USDT (~$24 million)
Affected Binance wallets include:
Ethereum Binance 14: 0x28C6c06298d514Db089934071355E5743bf21d60
Ethereum Binance 16: 0xDFd5293D8e347dFe59E90eFd55b2956a1343963d
Ethereum smart account: 0xEe7aE85f2Fe2239E27D9c1E23fFFe168D63b4055
Arbitrum Binance 56 / Hot Wallet 1 / Binance 89: 0x1b5b4e441f5a22bfd91b7772c780463f66a74b35, 0xf92402bb795fd7cd08fb83839689db79099c8c9c, 0x3931dab967c3e2dbb492fe12460a66d0fe4cc857
Avalanche Binance 49 / 85 / 110 / 118: 0x9f8c163cBA728e99993ABe7495F06c0A3c8Ac8b9, 0x6D8bE5cdf0d7DEE1f04E25FD70B001AE3B907824, 0xABa2D404C5C41da5964453A368aFF2604Ae80A14, 0x3BCE63C6C9ABf7A47f52c9A3a7950867700B0158
Primary collection address (same across the affected chains): 0x5227f603C1eE34CE3C06eFe6477003BDfCCB2f8c
Further destination wallets currently holding a large share of the funds include: 0x9749292D74Fd460982d0912eA9515EA24736C762, 0x0Ddf0480016e6bCb2C1F5d190D221FBA1320697e, 0x8532fa14acaf483729c449b8458aeddb900543d4, and 0x8d53903625b8e839b9DF4bd28B0EFb1CD6b8639A.
We recommend treating this as unconfirmed until Binance issues an official statement. We will update as we verify more.

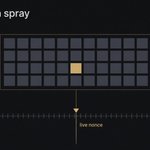
The attacker didn't know Binance 14's live nonce.
So they sprayed 50 EIP-7702 auths (18914775-18914824) in one type-4 tx.
Only 1 of 50 was a hit.
A 7702 auth is valid only for the current nonce at inclusion. The hot wallet was still firing. One nonce in that window landed.

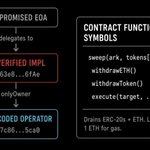
This EOA was 7702-upgraded to an unverified sweeper contract.
Impl: 0x63e842b054bd624a465454d533c33f573e9c6fae
Only hardcoded operator 0x7c8601d4645b93cea45f71e118a729332e6b5ca0 can drain it.
sweep() pulls every ERC-20 + ETH (leaves 1 ETH for gas). Incoming funds stay stealable.

We are investigating a cluster of large outflows from Binance hot wallets that began at approximately 20:24 UTC on 29 October 2026. On-chain, the transfers look consistent with unauthorized movement from those wallets, but this has not been confirmed by Binance, and we cannot yet rule out an internal treasury or operational sweep.
Observed chains: Ethereum, Arbitrum, and Avalanche, with related receipts also visible on Optimism.
Observed scale (approximate, still being reconciled):
Ethereum: about $2.5 billion from Binance 14 and Binance 16, plus an additional 780,000,000 USDC from a Binance smart account
Arbitrum: about 8,426 ETH (~$19.5 million)
Avalanche: about 1.81 million AVAX and 8.4 million USDT (~$24 million)
Affected Binance wallets include:
Ethereum Binance 14: 0x28C6c06298d514Db089934071355E5743bf21d60
Ethereum Binance 16: 0xDFd5293D8e347dFe59E90eFd55b2956a1343963d
Ethereum smart account: 0xEe7aE85f2Fe2239E27D9c1E23fFFe168D63b4055
Arbitrum Binance 56 / Hot Wallet 1 / Binance 89: 0x1b5b4e441f5a22bfd91b7772c780463f66a74b35, 0xf92402bb795fd7cd08fb83839689db79099c8c9c, 0x3931dab967c3e2dbb492fe12460a66d0fe4cc857
Avalanche Binance 49 / 85 / 110 / 118: 0x9f8c163cBA728e99993ABe7495F06c0A3c8Ac8b9, 0x6D8bE5cdf0d7DEE1f04E25FD70B001AE3B907824, 0xABa2D404C5C41da5964453A368aFF2604Ae80A14, 0x3BCE63C6C9ABf7A47f52c9A3a7950867700B0158
Primary collection address (same across the affected chains): 0x5227f603C1eE34CE3C06eFe6477003BDfCCB2f8c
Further destination wallets currently holding a large share of the funds include: 0x9749292D74Fd460982d0912eA9515EA24736C762, 0x0Ddf0480016e6bCb2C1F5d190D221FBA1320697e, 0x8532fa14acaf483729c449b8458aeddb900543d4, and 0x8d53903625b8e839b9DF4bd28B0EFb1CD6b8639A.
We recommend treating this as unconfirmed until Binance issues an official statement. We will update as we verify more.
Blockaid retweeted
We are investigating a cluster of large outflows from Binance hot wallets that began at approximately 20:24 UTC on 29 October 2026. On-chain, the transfers look consistent with unauthorized movement from those wallets, but this has not been confirmed by Binance, and we cannot yet rule out an internal treasury or operational sweep.
Observed chains: Ethereum, Arbitrum, and Avalanche, with related receipts also visible on Optimism.
Observed scale (approximate, still being reconciled):
Ethereum: about $2.5 billion from Binance 14 and Binance 16, plus an additional 780,000,000 USDC from a Binance smart account
Arbitrum: about 8,426 ETH (~$19.5 million)
Avalanche: about 1.81 million AVAX and 8.4 million USDT (~$24 million)
Affected Binance wallets include:
Ethereum Binance 14: 0x28C6c06298d514Db089934071355E5743bf21d60
Ethereum Binance 16: 0xDFd5293D8e347dFe59E90eFd55b2956a1343963d
Ethereum smart account: 0xEe7aE85f2Fe2239E27D9c1E23fFFe168D63b4055
Arbitrum Binance 56 / Hot Wallet 1 / Binance 89: 0x1b5b4e441f5a22bfd91b7772c780463f66a74b35, 0xf92402bb795fd7cd08fb83839689db79099c8c9c, 0x3931dab967c3e2dbb492fe12460a66d0fe4cc857
Avalanche Binance 49 / 85 / 110 / 118: 0x9f8c163cBA728e99993ABe7495F06c0A3c8Ac8b9, 0x6D8bE5cdf0d7DEE1f04E25FD70B001AE3B907824, 0xABa2D404C5C41da5964453A368aFF2604Ae80A14, 0x3BCE63C6C9ABf7A47f52c9A3a7950867700B0158
Primary collection address (same across the affected chains): 0x5227f603C1eE34CE3C06eFe6477003BDfCCB2f8c
Further destination wallets currently holding a large share of the funds include: 0x9749292D74Fd460982d0912eA9515EA24736C762, 0x0Ddf0480016e6bCb2C1F5d190D221FBA1320697e, 0x8532fa14acaf483729c449b8458aeddb900543d4, and 0x8d53903625b8e839b9DF4bd28B0EFb1CD6b8639A.
We recommend treating this as unconfirmed until Binance issues an official statement. We will update as we verify more.

Blockaid has partnered with @project0 to bring onchain monitoring to its DeFi prime brokerage.
Onchain Monitoring covers its program and venue positions, catching upstream risk in real time for the trading firms and institutions it serves.
Learn more: blockaid.io/blog/blockaid-br…

🚨Blockaid detected an ongoing exploit on @zkLink_Official bridge on ethereum.
Used a public relayer to inject a forged batch root on Ethereum, then finalized ETH and ERC20 withdrawals from zkLink Nova L1 escrow to attacker-chosen receivers.
~$786k drained from L1 ETH escrow and ERC20 bridge so far. Attack still ongoing.🧵
Exploiter addresses: etherscan.io/address/0xaCA06… etherscan.io/address/0xD5f16…
Example exploit tx: etherscan.io/tx/0x4f3c23e75b…
Victim contract: etherscan.io/address/0x5fD9F…
Victim bridge: etherscan.io/address/0xAd16e…
