Censys (@censysio) header
Censys (@censysio) profile picture

The Intelligence for AI-Powered Security. Real-time defense requires real-time intelligence and visibility.

Ann Arbor, MI
Joined September 2015
Photo by Censys (@censysio)Photo by Censys (@censysio)Photo by Censys (@censysio)Photo by Censys (@censysio)Photo by Censys (@censysio)Photo by Censys (@censysio)Photo by Censys (@censysio)Photo by Censys (@censysio)Photo by Censys (@censysio)Photo by Censys (@censysio)
Drawing on more than two years of Internet intelligence, Censys ARC examines what's changing, what's staying the same, and what it means for security teams. From the rapid growth of exposed AI infrastructure to shifting threat actor infrastructure and persistent risks across enterprise software and industrial control systems, the report reveals where the Internet is evolving fastest and where exposures aren't going away. Download the 2026 State of the Internet Report: bit.ly/4imYFSf
2
550
On Nov 16, a third-party script on Zoom, BBC, CNN, and other major sites was redirecting users to a malicious exploitation kit (1688360[.]cc/track.js). The script fingerprints visitors and attempts card skimming, cookie and screenshot theft, wallet swapping, and iPhone visitors routed to an exploit kit. The exploit kit matches a commercial iOS exploit kit called Caishen, carrying DarkSword exploit chains that route each device by iOS version, 13 through 26.
🤖 Made with AI
3
6
15
1,486
One host often runs the whole stack: control panel, exploit backend, crypto storefronts, side by side. A domain manager manages backup domains, traffic fails over between them, and an emergency switch can 404 every delivery link while a Telegram bot is the only way back in.
1
263
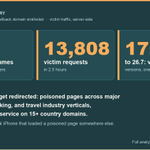
We sinkholed one of the kit's fallback domains. In 2.5 hours: 509 victim hostnames, 13,808 victim requests. Victims redirected from major news, transportation and shopping brands. Victims ran iOS 17.4 to 26.7, one channel code.
194
🚨 Critical Atlassian Confluence RCE (CVE-2026-90436, CVSS 9.8) is being actively exploited. Censys identified 1.2M Internet-exposed Confluence web properties. This does not confirm vulnerability. Read the full advisory for additional details and queries: bit.ly/4kSG6ab
5
21
1
87
5,729
AI offensive tools like ARTEX are making attacks faster and cheaper. The fundamentals of defense haven't changed. Learn how Censys helps teams monitor exposure, fingerprint emerging threats, and investigate adversary infrastructure using first-party Internet intelligence: bit.ly/3UXmx6b
2
17
1,288
AI-assisted offensive frameworks like ARTEX are gaining attention, and Censys ARC is tracking their growing Internet footprint. In the latest Censys ARC Flash, researcher Silas Cutler discusses ARTEX and what Censys is observing as activity increases. Research: bit.ly/4iSZG3u #CensysARC
1
1
10
961
Censys scan history captured ARTEX-related infrastructure 7 weeks before public reporting. Our new blog shows why first-party Internet data, threat fingerprints, and historical scans matter for investigations, and includes queries to put them to work. bit.ly/4jeA8ze
1
12
45
2,609
🚨 Critical Apache HTTP Server RCE (CVE-2026-119618, CVSS 9.8) Censys ARC observes ~166 million Apache HTTP Server web properties on the Internet. HTTP/2 is required and exposure does not confirm vulnerability. Fixed in 2.4.71. Advisory with queries: bit.ly/4iC6CmT
3
6
2
30
2,377
Censys principal security researcher @silascutler offered encouraging words. Because the underlying tradecraft is conventional, the fundamentals still hold, he said, "Enforce MFA, monitor your attack surface, and practice good credential hygiene." Read the full coverage in @DarkReading darkreading.com/cyberattacks…
1
22
988
Censys ARC Flash is back tomorrow at 11 AM ET! Join @silascutler and @himajedi to discuss vulnerability response in the era of the vulnpocalypse, the latest ARTEX findings, and more. Bring your questions for the live Q&A! Register: info.censys.com/arc-webcast?…
421
Hosts exposing AI-related tools online grew more than 63% from October 2025 to July 2026, per the @censysio 2026 State of the Internet Report. Censys and @DropzoneAI walk through what it means for security teams on Tuesday, December 1st, 11:30 AM ET. Register to attend 👉 bit.ly/3WwyQXA
1
1
177
Stale data means stale answers. With Censys, you’ll get real-time visibility and the insights you need to respond faster and manage risks confidently. Built on the world’s most comprehensive and accurate map of the Internet, the Censys Platform delivers actionable intelligence needed to accelerate triage, investigate threats, hunt adversaries, and manage Internet exposure. bit.ly/48QEZk1
1
397
Censys ARC Principal Security Researcher Emily Austin joined @DecipherSec to discuss discuss the growing Internet attack surface, findings from our 2026 State of the Internet Report, and what these trends mean for defenders. Watch or listen 👇
1
1
465
"Now, Censys says ARTEX is being paired with other offensive tools. At least 70 hosts were seen running both ARTEX and CyberStrikeAI, and others were seen deploying PentAGI, HexStrike AI, and RedAmon. Ironically enough, the researchers also found some actors had inadvertently exposed sensitive information through poorly secured directories."
1
10
1
82
4,759
"@silascutler, principal security researcher at Censys, said that not every instance of Artex is operated maliciously and many are used for authorized testers. But it’s unclear why hundreds of these Artex systems are exposed to the web, as the software does not require them to be accessible from the internet." via @TechCrunch
1
2
13
1,279
"Following the first campaign, we wanted to know the impact of the campaign. @sekoia_io observed via Censys more than 2,700 Danfoss systems exposed worldwide as of October 11, including approximately 1,700 in France."
French authorities have attributed the attacks on internet-exposed Danfoss refrigeration controllers to Iran’s #IRGC, specifically the Shahid Kaveh unit, aka #CyberAv3ngers. That matches one of the hypotheses in our private report shared on 15 October. buff.ly/GRg4NbV
1
5
569
🚨 N-able is responding to the public disclosure of multiple alleged critical vulnerabilities in its N-central remote monitoring and management platform. Censys identified 1,728 exposed hosts. The claims remain unvalidated. N-able advises taking servers offline. Read the full advisory for additional details and queries: bit.ly/4iJKEgv
2
7
1
13
1,440
Censys and Abstract are bringing real-time Internet intelligence directly into the detection pipeline. See how we are helping security teams modernize detection and response. bit.ly/4iCQNLm
1
4
550
Government agencies are warning that hackers could soon target refrigeration systems across the U.S. Recent refrigerator hacks across Europe are a reminder of Internet-exposed industrial control systems (ICS). Our latest blog explores 4 reasons ICS exposure isn't declining: bit.ly/4BM4eBx
2
4
561