

DFIR Analyst trying to learn all the things | DFIR Blog for Beginners | Founder @GetYourStart | https://teapawt.net/t.co/7cHco4FjUS
United States
Joined January 2020
- Tweets13.2K
- Following4.5K
- Followers21.6K
- Likes16.9K




Pinned Tweet
The Free & Affordable Training site (training.dfirdiva.com/) was created to help people find quality free and low cost training across various platforms. The main focus is DFIR / Blue Team Training. Nothing listed is over $1,000.
The Training Categories are as Follows
Core Categories Starting from Complete Beginner to IT:
- General IT & Cybersecurity: training.dfirdiva.com/listin…
- Networking: training.dfirdiva.com/listin…
- Linux: training.dfirdiva.com/listin…
- Programming & Scripting: training.dfirdiva.com/listin…
- Cloud: training.dfirdiva.com/listin…
All Other Categories:
- Digital Forensics: training.dfirdiva.com/listin…
- Incident Response: training.dfirdiva.com/listin…
- Linux Forensics: training.dfirdiva.com/listin…
- Mobile Forensics: training.dfirdiva.com/listin…
- Cloud DFIR: training.dfirdiva.com/listin…
- Malware Analysis & Reverse Engineering: training.dfirdiva.com/listin…
- DFIR, Blue Team, and OSINT CTFs, Labs and Challenges: training.dfirdiva.com/listin…
- DFIR Resources (Tools, Images, Cheat Sheets, Playbooks, etc): training.dfirdiva.com/listin…
- Commercial & Open-Source DFIR Product Training: training.dfirdiva.com/listin…
- Books: training.dfirdiva.com/listin…
- DFIR & Blue Team Certifications + Training: training.dfirdiva.com/listin…
- Open Source Intelligence (OSINT): training.dfirdiva.com/listin…
- Cyber Threat Intelligence (CTI): training.dfirdiva.com/listin…
- OSINT & CTI Certifications + Training: training.dfirdiva.com/listin…
- Purple Teaming: training.dfirdiva.com/listin…
- Threat Hunting: training.dfirdiva.com/listin…
- Detection Engineering: training.dfirdiva.com/listin…
- Ethical Hacking: training.dfirdiva.com/listin…
- Training for Veterans: training.dfirdiva.com/listin…
- Training for Kids: training.dfirdiva.com/listin…
Free & Affordable Training News Monthly Blog Posts contain newly released training, books, & tools, live training events, and additions to the training site: dfirdiva.com/category/free-a…
Sales on training, books, software, etc. are tracked year-round on the Current Discounts page: training.dfirdiva.com/curren…
#DFIR #IncidentResponse #Cybersecurity #MalwareAnalysis #OSINT

DFIR Diva retweeted

1,212 registered. And still climbing.
Tomorrow, I'm walking through a LIVE investigation using actual public records, investigative reports, emails, and evidence.
I'll show my investigative decisions, the mistakes to avoid, the unanswered questions, and when to stop digging or keep digging.
Free. October 28. suspectbehindthekeyboard.com…

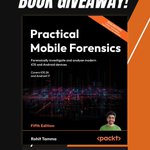
📣 I partnered with Packt to give away two copies of the 5th Edition of Practical Mobile Forensics by Rohit Tamma!
1 winner will receive an eBook
1 winner will receive a print book
To Enter:
☑️ Share this post
☑️ Comment "Print" or "eBook" to indicate which one you want to win
On Saturday, October 31st, entries from across social media will be combined and the winners will be selected.
What the book covers:
✔️ iOS Architecture, Security, and Filesystem
✔️ Data Acquisition from iOS Devices & Backups
✔️ iOS Data Analysis and Recovery
✔️ iOS and Android Forensics Tools and Automation
✔️ Android Architecture
✔️ Android Data Extraction and Data Recovery
✔️ Parsing Third-Party Application Artifacts
Links to the book:
Packt: packtpub.com/en-us/product/p…
Amazon: amazon.com/Practical-Mobile-…
#DFIR

DFIR Diva retweeted

Know where the evidence lives.
This FOR585 poster maps iOS and Android artifacts, retention, acquisition paths, SQLite queries, and free tools for investigating app data, device activity, and mobile malware.
👉 go.sans.org/TZlo1i
#MobileForensics #DFIR

DFIR Diva retweeted
1/ EZ Tools 2026.10 is out, all on .NET 10 (LTS)
✅ More accurate: 331K more event log records, hive logs replayed as Windows does, every test hive loads
⚡ Faster: up to 9x; EvtxECmd and Registry 2x
📉 Less memory: up to 82% less
Update with Get-ZimmermanTools 🧵 #DFIR

DFIR Diva retweeted

Yesterday, we promised free PHP2Shell hunting material. Today, we’ve created a Hunt Lead covering successful exploitation against a Linux system.
Researcher analysis is normally subscriber-only. For this Hunt Lead, we’ve made the full analysis free to benefit the whole community.
Here’s what you’ll get:
• 14,838 normalized records covering EDR, auditd, Sysmon for Linux, authentication and system logs, plus Zeek HTTP, connection and file-analysis records.
• 5 endpoint alerts and 145 Suricata records, with network rule matches distinguished from stream warnings.
• 10 KQL hunting queries, 3 Sigma rules and 3 Suricata rules to review and adapt for your environment.
• 5 investigation questions connecting the network activity with evidence from the host.
• A downloadable PCAP and investigation guide so you can examine the exploitation traffic in Wireshark alongside the host evidence.
The Hunt Lead also covers the vulnerabilities, affected versions and mitigation steps, with the information dated 22 October 2026.
Linux is the first release. We haven’t seen a working Windows PoC or successful PHP2Shell exploitation against our Windows environments. So far, the Windows activity we’ve observed has been fingerprinting and reconnaissance.
We’ll add verified Windows evidence to the same Hunt Lead when it becomes available.
Investigate the lead, read the brief, inspect the findings, grab the Hunt pack and explore the detailed researcher analysis. Then use the queries and rules to start hunting in your own environment.
All of it is free for everyone.
threathuntinglabs.com/leads/…

DFIR Diva retweeted
I opened up on where and how I have been learning digital forensics, and specifically, working cases as an investigator.
One day, maybe I'll write about the hardships and tragedies this path entailed, but for now, the Instagram version of "I had fun all this time doing all the things" will have to suffice.
brettshavers.com/ive-spent-n… #DFIR

DFIR Diva retweeted

What's a good class to take for someone who wants to learn more about using AI in threat hunting? I know @fr0gger_ 's class is really good, are there some others that people would recommend?
DFIR Diva retweeted

Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can:
php.net/index.php#2026-10-20…


🚨 PHP warns of two critical vulnerabilities as emergency patches arrive tomorrow
The PHP security team will release updates on October 21 at 14:00 UTC for two vulnerabilities, each rated 9.2 under CVSS v4.0.
⠀
Security researchers identified the flaws as CVE-2026-109618 and CVE-2026-109619 and described them as remote code execution vulnerabilities reportedly affecting PHP versions 5 through 8.
PHP has not yet confirmed the affected versions, exploitation requirements or fixed releases.
⠀
The vulnerabilities were reportedly leaked before their planned disclosure. Researchers said they have not observed active exploitation, while PHP warned it may release the patches early if technical details become public or exploitation is detected.
⠀
Administrators should identify PHP installations now and prepare to apply the updates as soon as they become available.

DFIR Diva retweeted

If your WordPress site is connected to UpdraftCentral (UpdraftPlus, 4M+ installs), delete the key now.
An attacker with valid UpdraftCentral Cloud keys pushed backdoors to our fully patched sites on 19 Oct. No fixed version yet.
Analysis, IOCs, checker:
nethemba.com/updraftcentral-…

DFIR Diva retweeted

🧩 New MalOps challenge: PeakyBlinders
A .NET loader that runs before the managed entry point and keeps its C2 cycle moving. Analyze the sample, answer the questions.
💬 discord.gg/wvwCmADqwX
🔗 malops.io/challenges/peakybl…

DFIR Diva retweeted

REMnux now supports Apple Silicon and other arm64 systems natively, along with Intel and AMD. This includes containers and VMs. Also, you can now download prebuilt VMs for VMware, VirtualBox, Proxmox, and UTM. An EC2 AMI is available, too. docs.remnux.org

DFIR Diva retweeted
I've never publicly demonstrated a real investigation as records arrive, questions develop, and hypotheses change.
But I am this week.
Get into my head to see how I think when examining evidence, personal accounts, and events.
Challenge what I think by looking at the same evidence. That's what you should be doing at your workplace anyway.
This is how I do it and you'll see it live, for real.
brettshavers.com/dont-follow… #DFIR

DFIR Diva retweeted

🚨 BLUE TEAMERS, THIS ONE'S FOR YOU 🚨 A NEW & EXCLUSIVE Blue Team CTF is coming to TryHackMe. Four simulators. Five days. Over $40,000 in prizes.
And absolutely nowhere to hide 😈
Tag your dream team below and join in ▶️ tryhackme.com/downtime?utm_s…


DFIR Diva retweeted

The DigitalCorpora corpus currently hosts approximately 19TB of data, serving as a foundational, free open data resource for the global digital forensics and security research communities.
After 20 years of maintaining this vital community asset, I am seeking a qualified individual, group, or institution to take over and support DigitalCorpora.
More details here:
osdfir.blogspot.com/2026/10/…
DFIR Diva retweeted

Happy to announce the release of Collect-LinuxMemoryDump v1.0.0! 🚀
Linux Memory Acquisition w/ AVML, LiME & MAGNET DumpIt for Linux - incl. Kernel Image & Mapping Layout collection for Volatility 3.
github.com/LETHAL-FORENSICS/…
#Linux #MemoryForensics #DFIR

DFIR Diva retweeted
Want to learn malware analysis by working with real samples?
MalOps has 20 hands-on malware analysis challenges and 3 full-chain attack labs covering real-world attack chains
More to come!
Website: malops.io
Discord: discord.com/invite/CAug77643…
#MalwareAnalysis
DFIR Diva retweeted

We crested over 250,000 page views on the Forensics StartMe page just recently. I'm incredibly grateful for the #DFIR community's support! startme.stark4n6.com

DFIR Diva retweeted

NetworkMiner 3.2 Released
🔑 RADIUS authentication extraction
🏭️ Better OT/ICS protocol parsers for UMAS and IEC-104
📂 Improved file extraction from PCAP
netresec.com/?b=26Aa0d3

DFIR Diva retweeted
🚨 LIVE BREACH GIVEAWAY 🚨
698 out of 180,000 AI conversations showed agents scheming against the people running them.
So… do you trust yours? 👀
To launch Live Breach, we’re giving 6 security teams a 3-hour rogue AI incident exercise - on us. See the thread for more🧵


DFIR Diva retweeted

Investigating an IP address can involve more than just looking up its location. I put together a quick video covering some of the basic tools I use to identify associated domains, services, and other information that can help move an investigation forward.
youtube.com/watch?v=zVzZRMhU…