

Co-founder & CGO @ https://teapawt.net/t.co/JlzXgM3Hwz - Marketplace for Crypto M&A, Secondaries, and OTC Digital Marketing Expert, Investor, Crypto Lover, Adventurer
Joined June 2021
- Tweets704
- Following360
- Followers1.4K
- Likes521





Pinned Tweet
We Finalized the sale of a business today.
Official announcement scheduled for Monday. Stay tuned . @Acquire_Fi #web3 #crypto

1
9
1,270
Excited to moderate tomorrow! – at Central Region, Singapore

As AI gets more powerful, who actually owns the intelligence?
@marshallzzcc of @AISkillFun, Dany Vaiman of @stack0G + 0G's @0xAgenticAlpha join @FryeCryptoGuy to dig into it.
Panel: Who Owns AI? The Battle for Intelligence

1
1
54

The team has arrived in Korea!!!
@Acquire_Fi @RamboJackson5 @FuddCrypto
#crypto #kbw #korea #web3 – at Gangnam-gu, Republic of Korea

4
97
Will also be attending in Korea! See you there!

Our Title Sponsor @Ripple is joining @kbwofficial as a Gold Sponsor 👏
📅 Sep 30-Oct 1, 2026 | 📍 Walkerhill, KBW 2026
📅 Oct 3, 2026 | 📍 Grand Hyatt Seoul, XRP Seoul 2026
This KBW2026 with @Official_Upbit, come see the scale and energy of Korea's XRP/XRPL community for yourself 🇰🇷
🎟 Get Tickets: luma.com/wm5ub5wk
🎙 Apply to speak: bit.ly/4cteDH2
🤝 Become a sponsor: bit.ly/4wboCI5

202
🚨 Scam Alert: Hyperlink Spoofing
This is a new one for me and a good reminder to slow down before clicking any link.
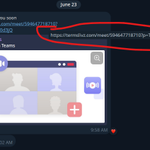
I received what looked like a normal meeting invite / Teams link. The visible text made it look like it was going to Microsoft Teams, but when hovering over the link, the actual destination was a completely different domain.
A few quick checks before clicking:
-Hover over links before opening them on desktop.
-On mobile, press and hold to preview the actual destination.
-Be extra careful with “joining now?” messages or anything creating urgency.
-When in doubt, open Teams, Google Calendar, or Calendly directly instead of clicking through a message.
These scams are getting cleaner. The invite can look real, the branding can look real, and the timing can feel normal.
Always check the actual link, not just the text you see.
#ScamAlert #CyberSecurity #Phishing #BusinessSecurity #OnlineSafety

128
❗ Alert!!! scam hack attempt! Honestly one of the best one I have seen
- Verified Twitter Account
- Stolen TG account with TG stories of a real person
-AI generated website
Its all there.
AI is a wonderful tool but its making scams that much easier! Stay safe.
2
93
🚨Scam Alert! Scarry scam link passed virus total check.
Someone sent me a malicious link this morning. I ran it through VirusTotal before clicking. 0 out of 95 security vendors flagged it. Every single one came back clean. The link was not clean.
It was a fake Microsoft Teams URL designed to download a trojan on your machine. This matters because most people in crypto treat VirusTotal as the final word. If it passes, they click. That assumption is now being weaponized. Attackers are building malware that specifically evades automated scanning, knowing that is the check most of us run.
The domain was teams.ms-meets.co. Not microsoft.com. Close enough to scan past at normal reading speed, clean enough to pass every security tool available to the public. The rest of the setup was standard: Telegram outreach, vague pitch about synergies, a real Calendly booking to build trust, then the payload link sent right at call time when you are expecting to click something.
VirusTotal passing is no longer a green light. Check the actual domain. Real Teams links come from teams.microsoft.com only. Anything else, regardless of what the scanners say, treat it as hostile. This is being run against people in Web3. Founders, operators, investors. Be careful out there.


Quite terrifying

hyperliquid's 4-of-5 multisig controls $4b in user deposits with zero timelock. uniswap has 48 hours. aave has variable delays. makerdao has 48 hours. hyperliquid has zero. five anonymous signers can upgrade bridge contracts and drain everything instantly with no review period. closed-source node client means validators can't even verify what they're running. assign a 5% annual probability to multisig compromise and 90% loss severity and you're looking at negative expected value on idle capital. the product is elite. the UX is best in class. the revenue is $600m annualized. but treat it as a trading venue not a vault. trade there, withdraw profits to self-custody, never let capital sit idle on a platform where the entire security model is "trust five people you've never met"
155
Catch me in another amazing spaces by @GammaPrime_Fi live now! – at Medford, MA

Energy, Risk, and Markets: What Changes Now?
⏰We’re breaking it down on April 1st at 5 PM CEST with our guests:
Paul Lalovich @paullal8
Alex Damsker @AlexDamsker
Harrison Frye @FryeCryptoGuy
Amanda Goodall @amanda_goodall
Bring your questions and join the conversation 👉teapawt.net/i/spaces/1RKjpzMkRAoJw…

66
Deciding if I should head to ETHcc for just the week.
Already have some meetings lines up.
Looking for more insight – at Medford, MA

46
Available all week to discuss M&A, OTC and Secondary deals in the space. Looking to meet buyers, sellers and industry insiders @Acquire_Fi – at Manhattan, NY

Advised IDEX on its sale to Katana as principal at Acquire.Fi.
They are now Katana Perps. Native on-chain perps integrated into the Katana App, backed by @GSR_io, @SeliniCapital , and @Auros_global at launch. @katanaperps @katana
We sourced and ran the full process. Good team, right home.
cryptopolitan.com/katana-acq…
perps.katana.network – at Mango, FL

3
94
Scam Alert!!!
New phishing vector targeting crypto conference organizers and speakers.
The scam:
-Impersonates conference organizers (this one fake ETHCC)
-Uses sites.google.com to build fake booking pages
-Google domain = instant trust and credibility
-Asks you to "schedule a call" via fake booking link
-Likely harvests calendar access, email, or deploys malware
Red flags:
-Real booking link is a subdomain (calendly.com/name, cal.com/name)
sites.google.com is just a webpage builder, not a booking tool
-No legitimate conference uses Google Sites for speaker coordination
-Unprofessional Telegram outreach
The Google brand creates false trust. They're weaponizing it.
Stay sharp.


122
Going live in 40 minutes! Joining @GammaPrime_Fi on their spaces! – at Medford, MA
Shifting Capital Flows: How Geopolitics is Reshaping Global Investment
Join for our expert insights today at 5 PM CET (11 AM EST)
Our special guests:
@paullal8 - agiledynamics.co
@izakaminska - @theblindsp0t
@FryeCryptoGuy - @Acquire_Fi
@constkogan - @holisticapital
@michaelfkong - @SonicLabs
👉teapawt.net/i/spaces/1AxRnaokALjxl…

1
61
Excited to be a part of the @SimplicityWeb3 Accelerator this coming April! See you all there! #Merger #Acquisition #Crypto #web3 #blockchain #secondaries #otc @Acquire_Fi

Our lecturers are almost finalised. We tried our hardest to find the most impactful and knowledgeable people across all startup topics, and are looking forward to joining every lecture to learn the nitty gritty specifics ourselves.
If you haven't been accepted, don't worry - all lectures will be published on our YouTube channel: youtube.com/@Simplicity_Grou….
🆘 Applications close 28 Feb. Apply here: forms.gle/i2cnnujuKVJ8aEAy9

1
3
133
Harrison CryptoGuy Frye retweeted

Our lecturers are almost finalised. We tried our hardest to find the most impactful and knowledgeable people across all startup topics, and are looking forward to joining every lecture to learn the nitty gritty specifics ourselves.
If you haven't been accepted, don't worry - all lectures will be published on our YouTube channel: youtube.com/@Simplicity_Grou….
🆘 Applications close 28 Feb. Apply here: forms.gle/i2cnnujuKVJ8aEAy9
Excited to be joining Simplicity Group's accelerator program as a guest speaker for Week 5 on Fundraising.
I'll be covering acquisitions and OTC deals - how to position your project for a successful exit and what buyers are actually looking for in 2025.
Looking forward to sharing what we're seeing across 350+ mandates at @Acquire_Fi with the founders in the cohort.
Thanks to the Simplicity team for having me.
This quoted post is unavailable.
58
SCAM ALERT #2 - ETHDenver
Another sophisticated attack targeting conference attendees.
The Setup:
-Fake "TECHNO NIGHT" party posted on Luma for Feb 18
-Real venue (Club Vinyl) but not actually booked
-Timed perfectly for first night when late-night options were limited
-Professional branding, targeted at degens
The Scam:
-Accepted all registrations
-Sent email requiring NFT mint for entry (Is also on the event flier)
-Fake Moongate site: moonsgates.xyz (real is moongate.id) @Moongate
-AI-generated static HTML, near-perfect spoof
-When you "mint," you sign a transaction that drains your wallet
The Result:
-Dozens of confused attendees outside a closed venue on the cold Denver street
-Empty wallets
-No party vibes
This is the second major scam reported this week at ETHDenver
Protection Basics:
-Never sign transactions for event access - If you do, use a burner wallet
-Verify URLs character by character
-Never click Zoom/meeting links from unverified sources
-Use a burner wallet for any minting
-If it requires a signature to RSVP, it's a scam
These attacks are getting absurdly good. AI makes it trivial to create convincing spoofs in minutes.
The scammers target conference attendees who are mobile, distracted, intoxicated, etc. They know the schedule. They know when people are looking for plans.
Stay paranoid.


SCAM ALERT!!!!
By far the best phishing attempt I've seen targeting ETHDenver attendees.
Here's the playbook:
Setup:
-Fake "Shorooq Closed-Door Dinner Network" on Luma
-Professional branding, AI-powered screening process
-Registration form harvesting contact and company details
The Hook:
-TG DM asking for Calendly to schedule "screening interview"
-Booked via unmanned Shorooq email ([email protected])
-Premium verified TG account (+1 717-973-0455, @ShorooqCapital)
-Asked specific, pointed interview question (AI-generated)
-Sent fake Streamyard link: streamyard.ink (not .com)
-Near-perfect HTML replica, likely built in 60 seconds with AI
Red Flags:
-Domain was .ink not .com
-Deleted chat immediately when confronted
What they wanted: Executable file download to steal wallets, accounts, credentials, etc
The sophistication is insane. Premium TG, AI screening questions, pixel-perfect spoof site, perfect timing.
If you registered:
Don't click any links
Change passwords if you did
Alert your team
The bar for phishing just went up 10x. These are getting harder to catch even for pros.
Stay sharp.
@ShorooqPartners


We always post this externally to anyone trying to use zoom or other call links :
Security Notice Regarding Video Calls
Due to a recent uptick in scam activity and impersonation attempts related to Zoom and similar platforms, any Acquire.Fi team member will only attend calls via Google Meet (Hangouts), or directly on Telegram/Whatsapp.
If you're ever unsure about a call link or request, feel free to double-check directly with our team via email or Telegram.
Thanks for understanding — keeping everyone protected is our priority.
— Acquire.Fi Team
1
1
179