MFTV & Bitcoin Rails | coauthor BIP 360 | Head of @MARAFoundation_ @MARA
Joined February 2010
- Tweets11.9K
- Following2.5K
- Followers15.9K
- Likes25.8K


Pinned Tweet
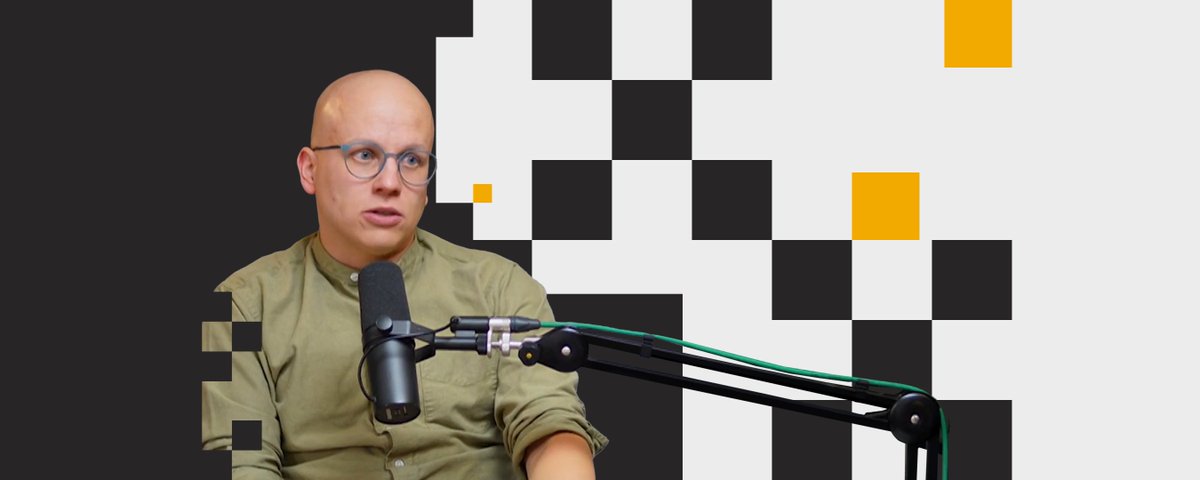
I finally got the chance to interview @Trezor CTO @tsusanka on the PQ transition.
One of the more interesting and underrated facets of Bitcoin’s post-quantum discussion is the outsized role wallets will play in ensuring a safe transition… especially if we implement a stateful scheme like SHRINCS, which is looking more and more likely as discussions evolve.
It’s pretty obvious to me that @tsusanka and @P3b7_ will be some of the most critical MVPs of the PQ transition.

Trezor CTO on Post-Quantum Bitcoin’s “Stateful Signature Problem” | TOMÁŠ SUŠÁNKA
🔗 YouTube: youtube.com/watch?v=sBNhbMqT…
🌿 Spotify: open.spotify.com/episode/7xG…
As Bitcoin researchers get closer to consensus on hash-based post-quantum signature schemes like SHRINCS, hardware wallet manufacturers are weighing architectural decisions to protect users from the pitfalls of stateful signatures.
In this episode of MFTV, Trezor CTO @tsusanka unpacks the efficiency and security tradeoffs of SHRINCS, a stateful scheme in which reusing signing state can have serious security consequences. Preventing that reuse will become a critical responsibility for wallet developers if SHRINCS is adopted by the network, which is looking more likely as pressure mounts for Bitcoin to make a move.
@tsusanka shares the specific architectural choices Trezor is considering to support safe handling of SHRINCS and reduce the potentially catastrophic “footgun” risks associated with this new scheme. He also unpacks Trezor’s internal approach to quantum-prepping its hardware wallets, explaining why the company released a post-quantum device late last year — well before a Bitcoin network upgrade was in view.
TIMESTAMPS:
🎙️ 00:00 Intro
⚛️ 05:38 When quantum computing truly entered the chat
🏗️ 07:08 The three layers of Trezor hardware
🏭 12:10 Embedding post-quantum keys at the manufacturing level
🏷️ 15:13 The “quantum-ready” marketing debate
⚖️ 19:47 Stateful vs. stateless signatures
🧮 26:55 Hash-based vs. lattice-based cryptography
⏳ 39:53 Operational friction for merchants
🔍 50:32 The open-source vs. closed-source hardware debate
🤖 52:52 Handling AI-generated bug bounty reports
🤝 01:04:12 Accepting compromises for a post-quantum standard


Isabel Foxen Duke⚡️ retweeted

I guess it's really happening at this point, with the second block found with @StratumV2 by @MARA: mempool.space/block/00000000…

Most people assume that AI represents a bigger threat for open-source software than closed-source software because it’s public for anyone to see.
But, as Trezor CTO @tsusanka raised to me, what happens when closed-source code is hacked or leaked… and exposed to the AI wolves with less review?
Trezor CTO on Post-Quantum Bitcoin’s “Stateful Signature Problem” | TOMÁŠ SUŠÁNKA
🔗 YouTube: youtube.com/watch?v=sBNhbMqT…
🌿 Spotify: open.spotify.com/episode/7xG…
As Bitcoin researchers get closer to consensus on hash-based post-quantum signature schemes like SHRINCS, hardware wallet manufacturers are weighing architectural decisions to protect users from the pitfalls of stateful signatures.
In this episode of MFTV, Trezor CTO @tsusanka unpacks the efficiency and security tradeoffs of SHRINCS, a stateful scheme in which reusing signing state can have serious security consequences. Preventing that reuse will become a critical responsibility for wallet developers if SHRINCS is adopted by the network, which is looking more likely as pressure mounts for Bitcoin to make a move.
@tsusanka shares the specific architectural choices Trezor is considering to support safe handling of SHRINCS and reduce the potentially catastrophic “footgun” risks associated with this new scheme. He also unpacks Trezor’s internal approach to quantum-prepping its hardware wallets, explaining why the company released a post-quantum device late last year — well before a Bitcoin network upgrade was in view.
TIMESTAMPS:
🎙️ 00:00 Intro
⚛️ 05:38 When quantum computing truly entered the chat
🏗️ 07:08 The three layers of Trezor hardware
🏭 12:10 Embedding post-quantum keys at the manufacturing level
🏷️ 15:13 The “quantum-ready” marketing debate
⚖️ 19:47 Stateful vs. stateless signatures
🧮 26:55 Hash-based vs. lattice-based cryptography
⏳ 39:53 Operational friction for merchants
🔍 50:32 The open-source vs. closed-source hardware debate
🤖 52:52 Handling AI-generated bug bounty reports
🤝 01:04:12 Accepting compromises for a post-quantum standard
Very strong argument for open source code
In the age of AI… assuming its truly open
Source and not just “source available.” In other words, as long as there’s an incentive for the OW code to be reviewed
Cc @stutxo
151
Isabel Foxen Duke⚡️ retweeted
Most people assume that AI represents a bigger threat for open-source software than closed-source software because it’s public for anyone to see.
But, as Trezor CTO @tsusanka raised to me, what happens when closed-source code is hacked or leaked… and exposed to the AI wolves with less review?
Trezor CTO on Post-Quantum Bitcoin’s “Stateful Signature Problem” | TOMÁŠ SUŠÁNKA
🔗 YouTube: youtube.com/watch?v=sBNhbMqT…
🌿 Spotify: open.spotify.com/episode/7xG…
As Bitcoin researchers get closer to consensus on hash-based post-quantum signature schemes like SHRINCS, hardware wallet manufacturers are weighing architectural decisions to protect users from the pitfalls of stateful signatures.
In this episode of MFTV, Trezor CTO @tsusanka unpacks the efficiency and security tradeoffs of SHRINCS, a stateful scheme in which reusing signing state can have serious security consequences. Preventing that reuse will become a critical responsibility for wallet developers if SHRINCS is adopted by the network, which is looking more likely as pressure mounts for Bitcoin to make a move.
@tsusanka shares the specific architectural choices Trezor is considering to support safe handling of SHRINCS and reduce the potentially catastrophic “footgun” risks associated with this new scheme. He also unpacks Trezor’s internal approach to quantum-prepping its hardware wallets, explaining why the company released a post-quantum device late last year — well before a Bitcoin network upgrade was in view.
TIMESTAMPS:
🎙️ 00:00 Intro
⚛️ 05:38 When quantum computing truly entered the chat
🏗️ 07:08 The three layers of Trezor hardware
🏭 12:10 Embedding post-quantum keys at the manufacturing level
🏷️ 15:13 The “quantum-ready” marketing debate
⚖️ 19:47 Stateful vs. stateless signatures
🧮 26:55 Hash-based vs. lattice-based cryptography
⏳ 39:53 Operational friction for merchants
🔍 50:32 The open-source vs. closed-source hardware debate
🤖 52:52 Handling AI-generated bug bounty reports
🤝 01:04:12 Accepting compromises for a post-quantum standard
Isabel Foxen Duke⚡️ retweeted
AI is finding more bugs... but a huge number of AI-generated bug reports are also just "slop," creating extra work for engineers sorting the wheat from the chaff. To handle the volume, @Trezor CTO @tsusanka says the team now has a dedicated engineer on "triage" duty who also relies on AI to sift through the onslaught of new reports.
Trezor CTO on Post-Quantum Bitcoin’s “Stateful Signature Problem” | TOMÁŠ SUŠÁNKA
🔗 YouTube: youtube.com/watch?v=sBNhbMqT…
🌿 Spotify: open.spotify.com/episode/7xG…
As Bitcoin researchers get closer to consensus on hash-based post-quantum signature schemes like SHRINCS, hardware wallet manufacturers are weighing architectural decisions to protect users from the pitfalls of stateful signatures.
In this episode of MFTV, Trezor CTO @tsusanka unpacks the efficiency and security tradeoffs of SHRINCS, a stateful scheme in which reusing signing state can have serious security consequences. Preventing that reuse will become a critical responsibility for wallet developers if SHRINCS is adopted by the network, which is looking more likely as pressure mounts for Bitcoin to make a move.
@tsusanka shares the specific architectural choices Trezor is considering to support safe handling of SHRINCS and reduce the potentially catastrophic “footgun” risks associated with this new scheme. He also unpacks Trezor’s internal approach to quantum-prepping its hardware wallets, explaining why the company released a post-quantum device late last year — well before a Bitcoin network upgrade was in view.
TIMESTAMPS:
🎙️ 00:00 Intro
⚛️ 05:38 When quantum computing truly entered the chat
🏗️ 07:08 The three layers of Trezor hardware
🏭 12:10 Embedding post-quantum keys at the manufacturing level
🏷️ 15:13 The “quantum-ready” marketing debate
⚖️ 19:47 Stateful vs. stateless signatures
🧮 26:55 Hash-based vs. lattice-based cryptography
⏳ 39:53 Operational friction for merchants
🔍 50:32 The open-source vs. closed-source hardware debate
🤖 52:52 Handling AI-generated bug bounty reports
🤝 01:04:12 Accepting compromises for a post-quantum standard
Hey @robin_linus — could post-quantum signatures be the psyop we need to reignite the block size debate?
For clarity, @Trezor CTO @tsusanka thinks we should maybe hold off on this 😜
Trezor CTO on Post-Quantum Bitcoin’s “Stateful Signature Problem” | TOMÁŠ SUŠÁNKA
🔗 YouTube: youtube.com/watch?v=sBNhbMqT…
🌿 Spotify: open.spotify.com/episode/7xG…
As Bitcoin researchers get closer to consensus on hash-based post-quantum signature schemes like SHRINCS, hardware wallet manufacturers are weighing architectural decisions to protect users from the pitfalls of stateful signatures.
In this episode of MFTV, Trezor CTO @tsusanka unpacks the efficiency and security tradeoffs of SHRINCS, a stateful scheme in which reusing signing state can have serious security consequences. Preventing that reuse will become a critical responsibility for wallet developers if SHRINCS is adopted by the network, which is looking more likely as pressure mounts for Bitcoin to make a move.
@tsusanka shares the specific architectural choices Trezor is considering to support safe handling of SHRINCS and reduce the potentially catastrophic “footgun” risks associated with this new scheme. He also unpacks Trezor’s internal approach to quantum-prepping its hardware wallets, explaining why the company released a post-quantum device late last year — well before a Bitcoin network upgrade was in view.
TIMESTAMPS:
🎙️ 00:00 Intro
⚛️ 05:38 When quantum computing truly entered the chat
🏗️ 07:08 The three layers of Trezor hardware
🏭 12:10 Embedding post-quantum keys at the manufacturing level
🏷️ 15:13 The “quantum-ready” marketing debate
⚖️ 19:47 Stateful vs. stateless signatures
🧮 26:55 Hash-based vs. lattice-based cryptography
⏳ 39:53 Operational friction for merchants
🔍 50:32 The open-source vs. closed-source hardware debate
🤖 52:52 Handling AI-generated bug bounty reports
🤝 01:04:12 Accepting compromises for a post-quantum standard
Isabel Foxen Duke⚡️ retweeted
It took a lot of patience to get here, but it feels good to watch @StratumV2 adoption snowball.
Thanks to everyone who’s contributed to SV2 over the years!
Isabel Foxen Duke⚡️ retweeted
"We can have both hash-based signatures and lattice-based signatures, and I think that's what we should have eventually," says @Trezor CTO @tsusanka
With regard to the hash-vs-lattice-based debate for post-quantum Bitcoin signatures, Sušánka shares why he imagines a world with both options enshrined into Bitcoin at some point. That said, he understands why starting with a more conservative cryptographic assumption may make sense as a first step, despite efficiency and implementation-risk tradeoffs.
He additionally explains why he chose two different PQ signature types for different operations in the Safe 7 — Trezor's "quantum ready" hardware signing device.
Trezor CTO on Post-Quantum Bitcoin’s “Stateful Signature Problem” | TOMÁŠ SUŠÁNKA
🔗 YouTube: youtube.com/watch?v=sBNhbMqT…
🌿 Spotify: open.spotify.com/episode/7xG…
As Bitcoin researchers get closer to consensus on hash-based post-quantum signature schemes like SHRINCS, hardware wallet manufacturers are weighing architectural decisions to protect users from the pitfalls of stateful signatures.
In this episode of MFTV, Trezor CTO @tsusanka unpacks the efficiency and security tradeoffs of SHRINCS, a stateful scheme in which reusing signing state can have serious security consequences. Preventing that reuse will become a critical responsibility for wallet developers if SHRINCS is adopted by the network, which is looking more likely as pressure mounts for Bitcoin to make a move.
@tsusanka shares the specific architectural choices Trezor is considering to support safe handling of SHRINCS and reduce the potentially catastrophic “footgun” risks associated with this new scheme. He also unpacks Trezor’s internal approach to quantum-prepping its hardware wallets, explaining why the company released a post-quantum device late last year — well before a Bitcoin network upgrade was in view.
TIMESTAMPS:
🎙️ 00:00 Intro
⚛️ 05:38 When quantum computing truly entered the chat
🏗️ 07:08 The three layers of Trezor hardware
🏭 12:10 Embedding post-quantum keys at the manufacturing level
🏷️ 15:13 The “quantum-ready” marketing debate
⚖️ 19:47 Stateful vs. stateless signatures
🧮 26:55 Hash-based vs. lattice-based cryptography
⏳ 39:53 Operational friction for merchants
🔍 50:32 The open-source vs. closed-source hardware debate
🤖 52:52 Handling AI-generated bug bounty reports
🤝 01:04:12 Accepting compromises for a post-quantum standard
Isabel Foxen Duke⚡️ retweeted

Michael Saylor gives his thoughts on MSCI:
"MSCI is out on their own with this one. I don't know why, but again, not my decision."
When @Trezor launched their "quantum-ready" hardware wallet last year, some were confused about the product choice when Bitcoin may be years from a post-quantum upgrade. CTO @tsusanka shares their reasoning for releasing an end-to-end PQ HW device sooner rather than later, citing potentially long migration timelines as an industry concern.
Trezor CTO on Post-Quantum Bitcoin’s “Stateful Signature Problem” | TOMÁŠ SUŠÁNKA
🔗 YouTube: youtube.com/watch?v=sBNhbMqT…
🌿 Spotify: open.spotify.com/episode/7xG…
As Bitcoin researchers get closer to consensus on hash-based post-quantum signature schemes like SHRINCS, hardware wallet manufacturers are weighing architectural decisions to protect users from the pitfalls of stateful signatures.
In this episode of MFTV, Trezor CTO @tsusanka unpacks the efficiency and security tradeoffs of SHRINCS, a stateful scheme in which reusing signing state can have serious security consequences. Preventing that reuse will become a critical responsibility for wallet developers if SHRINCS is adopted by the network, which is looking more likely as pressure mounts for Bitcoin to make a move.
@tsusanka shares the specific architectural choices Trezor is considering to support safe handling of SHRINCS and reduce the potentially catastrophic “footgun” risks associated with this new scheme. He also unpacks Trezor’s internal approach to quantum-prepping its hardware wallets, explaining why the company released a post-quantum device late last year — well before a Bitcoin network upgrade was in view.
TIMESTAMPS:
🎙️ 00:00 Intro
⚛️ 05:38 When quantum computing truly entered the chat
🏗️ 07:08 The three layers of Trezor hardware
🏭 12:10 Embedding post-quantum keys at the manufacturing level
🏷️ 15:13 The “quantum-ready” marketing debate
⚖️ 19:47 Stateful vs. stateless signatures
🧮 26:55 Hash-based vs. lattice-based cryptography
⏳ 39:53 Operational friction for merchants
🔍 50:32 The open-source vs. closed-source hardware debate
🤖 52:52 Handling AI-generated bug bounty reports
🤝 01:04:12 Accepting compromises for a post-quantum standard
Isabel Foxen Duke⚡️ retweeted
While Sušánka recognizes that SHRINCS may be the conservative cryptographic choice because it relies on the same cryptographic assumptions as SHA-256, he is “kind of torn on the topic because maintaining the state is a burden.”
“For example, you can have two Trezors with the same recovery seed. How do you share the state between those two? You really don’t,” he added.

Trezor CTO on Post-Quantum Bitcoin’s “Stateful Signature Problem” | TOMÁŠ SUŠÁNKA
🔗 YouTube: youtube.com/watch?v=sBNhbMqT…
🌿 Spotify: open.spotify.com/episode/7xG…
As Bitcoin researchers get closer to consensus on hash-based post-quantum signature schemes like SHRINCS, hardware wallet manufacturers are weighing architectural decisions to protect users from the pitfalls of stateful signatures.
In this episode of MFTV, Trezor CTO @tsusanka unpacks the efficiency and security tradeoffs of SHRINCS, a stateful scheme in which reusing signing state can have serious security consequences. Preventing that reuse will become a critical responsibility for wallet developers if SHRINCS is adopted by the network, which is looking more likely as pressure mounts for Bitcoin to make a move.
@tsusanka shares the specific architectural choices Trezor is considering to support safe handling of SHRINCS and reduce the potentially catastrophic “footgun” risks associated with this new scheme. He also unpacks Trezor’s internal approach to quantum-prepping its hardware wallets, explaining why the company released a post-quantum device late last year — well before a Bitcoin network upgrade was in view.
TIMESTAMPS:
🎙️ 00:00 Intro
⚛️ 05:38 When quantum computing truly entered the chat
🏗️ 07:08 The three layers of Trezor hardware
🏭 12:10 Embedding post-quantum keys at the manufacturing level
🏷️ 15:13 The “quantum-ready” marketing debate
⚖️ 19:47 Stateful vs. stateless signatures
🧮 26:55 Hash-based vs. lattice-based cryptography
⏳ 39:53 Operational friction for merchants
🔍 50:32 The open-source vs. closed-source hardware debate
🤖 52:52 Handling AI-generated bug bounty reports
🤝 01:04:12 Accepting compromises for a post-quantum standard
Isabel Foxen Duke⚡️ retweeted
Bitcoin’s leading candidate for a post-quantum signature scheme, SCHRINCS, features stateful signatures that make transactions efficient — but introduce potentially catastrophic security vulnerabilities when misused.
“It’s our job to make it in a secure way,” argues @Trezor CTO @tsusanka, in reference to the built-in safeguards being considered for safer implementation of the scheme by hardware wallets.
More on this in the coming weeks from SHRINCS co-authors @blksresearch
Trezor CTO on Post-Quantum Bitcoin’s “Stateful Signature Problem” | TOMÁŠ SUŠÁNKA
🔗 YouTube: youtube.com/watch?v=sBNhbMqT…
🌿 Spotify: open.spotify.com/episode/7xG…
As Bitcoin researchers get closer to consensus on hash-based post-quantum signature schemes like SHRINCS, hardware wallet manufacturers are weighing architectural decisions to protect users from the pitfalls of stateful signatures.
In this episode of MFTV, Trezor CTO @tsusanka unpacks the efficiency and security tradeoffs of SHRINCS, a stateful scheme in which reusing signing state can have serious security consequences. Preventing that reuse will become a critical responsibility for wallet developers if SHRINCS is adopted by the network, which is looking more likely as pressure mounts for Bitcoin to make a move.
@tsusanka shares the specific architectural choices Trezor is considering to support safe handling of SHRINCS and reduce the potentially catastrophic “footgun” risks associated with this new scheme. He also unpacks Trezor’s internal approach to quantum-prepping its hardware wallets, explaining why the company released a post-quantum device late last year — well before a Bitcoin network upgrade was in view.
TIMESTAMPS:
🎙️ 00:00 Intro
⚛️ 05:38 When quantum computing truly entered the chat
🏗️ 07:08 The three layers of Trezor hardware
🏭 12:10 Embedding post-quantum keys at the manufacturing level
🏷️ 15:13 The “quantum-ready” marketing debate
⚖️ 19:47 Stateful vs. stateless signatures
🧮 26:55 Hash-based vs. lattice-based cryptography
⏳ 39:53 Operational friction for merchants
🔍 50:32 The open-source vs. closed-source hardware debate
🤖 52:52 Handling AI-generated bug bounty reports
🤝 01:04:12 Accepting compromises for a post-quantum standard
Isabel Foxen Duke⚡️ retweeted

Looking forward to a future where all PRs in libsecp256k1 come with formal proof correctness.
github.com/bitcoin-core/secp…

Isabel Foxen Duke⚡️ retweeted
Trezor CTO Tomáš Sušánka explains the trade-offs of Bitcoin’s leading post-quantum signature scheme.