

Official account of MalwareMustDie, NPO & public account @unixfreaxjp Info: https://teapawt.net/t.co/131r5UW4bF Blog: https://teapawt.net/t.co/lUnpKnXOqV
Joined September 2018
- Tweets717
- Following144
- Followers5.8K
- Likes328





Pinned Tweet
For followers & IR folks. Updated fakedns python tool with bugfix (for py 2.7) and upgraded to v2 for py 3.11+ compatibilities. Please use it with tests beforehand.
This updates inspired by code originally made by Francisco Santos & I still use it for +/- 20years (since Sat, 15 Apr 2006/thanks) - @unixfreaxjp
PS: feel free to improve.
py 3.11+:github.com/unixfreaxjp/malwa…
py 2.7:github.com/unixfreaxjp/malwa…
#malwaremustdie friends

#Blog: #MMD-071-2026 #KinsingBot a "bad-bad"-designed Linux botnet a while ago.. until recent.
blog.malwaremustdie.org/2026…
(I posted this to answer requests on new analysis #education materials. I rendered by chapters accordingly. Thanks for sticking with #malwaremustdie! Enjoy! - @unixfreaxjp, Nov 2026)


BLOG: MMD-0070-2026 - Once upon a time, Linux/Hajime hexstring-pushed a tiny ARM ELF fileless downloader: blog.malwaremustdie.org/2026…
#malwaremustdie (#research & #education purpose)
A lot of improvements in Iaito (radare2)
Now it is as sharp as my katana irl :)
Thank you @radareorg @trufae <3
#MalwareMustDie!

Okay, listen up. THIS (see prev thread) #malware campaign is on-going, even now. Adversaries are in control of these .INFO domains:
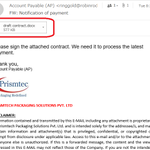
crystalogletree[.]info, coraliereinger[.]info and kevinsaad[.]info, Which they are spreading infection campaign relayed from various IP MTA located in this subnet 160[.]250.128.0/23 at AS150895/EZ TECHNOLOGY CO LTD, I attached. email they used for the infection.
Chains infection:
docx -> rtf -> xml obj #cve-2017-118822 load shellcode to decrypt & load another shellcode to execute malicious script in rtf (there are license.vbs/.js/Client.vbs) that downloads python312x86()zip contains evil Protected(py) to be persistence installed & executed, or execute a DLL binary of "license(.)ini" to be injected to into process.
That evil python is lastly served at sendspace(.)com/pro/dl/5qcr3i
So all of scripts used & binary will be heavily obfuscated. They tried hard to evade all checks and aiming unpatched #EQEDIT on older #msoffice app.
The above #IOC and #CTI info should be their #TTP so use information above to #block ur network in anyway you can.
Just saying, in a glimpse, it seems like adaptation of previously known as #hancitor docx campaign added w/ AI steroid. No, this isn't emotet, and no this is not Heodo/Geodo but could be the copycat.
#MalwareMustDie!!


Well, the adventure continues.. w/same bad-actors (pivoted attackers spambot: 160[.]250.128.165/VN) who's very eager to do more #malware CTF with me.
But.. the endgame is now different...an AI generated hash-obfuscated DLL loader..
See the pics of details & links (it has my hint to crack the hash), below is chain of infections:
docx: virustotal.com/gui/file/467f…
rtf: virustotal.com/gui/file/4289…
DLL loader: virustotal.com/gui/file/1a11…
#MalwareMustDie!


Okay.. this #malware actor's efforts continues. New #email malvertisement w/domain robinrodriguez[.]info via spambot at 161[.]248.238.122 at same AS150895/EZ TECHNOLOGY in #Vietnam, w/same payload "Protected .py" saved in #sendspace camouflaged in a zipped python windows pkg. The evil docx is now using new obfusctated JS loader to exec encoded powershell downloader, triggered by same cve #EQUEDIT exploit. It aims signature evasion, with same infection #backdoor motivation.
See attached pictures for better understanding. Block that sendspace url & final #stager hashes.
docx: virustotal.com/gui/file/fc04…
js: virustotal.com/gui/file/4062…
#MalwareMustDie!


Okay, listen up. THIS (see prev thread) #malware campaign is on-going, even now. Adversaries are in control of these .INFO domains:
crystalogletree[.]info, coraliereinger[.]info and kevinsaad[.]info, Which they are spreading infection campaign relayed from various IP MTA located in this subnet 160[.]250.128.0/23 at AS150895/EZ TECHNOLOGY CO LTD, I attached. email they used for the infection.
Chains infection:
docx -> rtf -> xml obj #cve-2017-118822 load shellcode to decrypt & load another shellcode to execute malicious script in rtf (there are license.vbs/.js/Client.vbs) that downloads python312x86()zip contains evil Protected(py) to be persistence installed & executed, or execute a DLL binary of "license(.)ini" to be injected to into process.
That evil python is lastly served at sendspace(.)com/pro/dl/5qcr3i
So all of scripts used & binary will be heavily obfuscated. They tried hard to evade all checks and aiming unpatched #EQEDIT on older #msoffice app.
The above #IOC and #CTI info should be their #TTP so use information above to #block ur network in anyway you can.
Just saying, in a glimpse, it seems like adaptation of previously known as #hancitor docx campaign added w/ AI steroid. No, this isn't emotet, and no this is not Heodo/Geodo but could be the copycat.
#MalwareMustDie!!
Thank you @freebsd & @cperciva for the great news. I've been waiting for this. Will test in on my Vortex86DX3 & Raspberry PiZero2W box before production.
Memo: time for #pkbase switching, fixes: userland package (libc stuff), old OpenZFS bug, more info at #freebsd announce: freebsd.org/releases/14.4R/a… & notes: freebsd.org/releases/14.4R/r…
Update/upgrade, red this 1st: docs.freebsd.org/en/books/ha…

2
851
Well, the adventure continues.. w/same bad-actors (pivoted attackers spambot: 160[.]250.128.165/VN) who's very eager to do more #malware CTF with me.
But.. the endgame is now different...an AI generated hash-obfuscated DLL loader..
See the pics of details & links (it has my hint to crack the hash), below is chain of infections:
docx: virustotal.com/gui/file/467f…
rtf: virustotal.com/gui/file/4289…
DLL loader: virustotal.com/gui/file/1a11…
#MalwareMustDie!
(smile) Someone at 160[.]250.128.122 spammed me w/docx email attachment..(downloader), it downloaded Protected.py (a persistent installer),then runs classic shed api shellcode with reversed shell injected to SndVol..(snipped part sc)..
to bad..no reg+SndVol in #BSD

So, how license.ini stager DLL got executed? See docx's exploit XML's (Equation.3 /3072bytes). It has embedded encrypted #shellcode loader, it execs license.ini to memory after EQU bug exploited by buffer overflow.
See pic for more. This is that loader: virustotal.com/gui/file/c37b…
Stay safe! Check ur updates/patch #malwaremustdie

1
311
(smile) Someone at 160[.]250.128.122 spammed me w/docx email attachment..(downloader), it downloaded Protected.py (a persistent installer),then runs classic shed api shellcode with reversed shell injected to SndVol..(snipped part sc)..
to bad..no reg+SndVol in #BSD
the whole #malware infection chain:
virustotal.com/gui/file/16da…
virustotal.com/gui/file/0d5d…
virustotal.com/gui/file/0d06…
virustotal.com/gui/file/7857…
to these bad actors, just make sure to exclude me from your spamlist ;-)

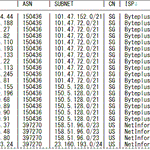
There are a lot of spear phishing originated fr infra at:
AS150436 Byteplus Pte. Ltd.
AS397270 Netinformatik
101[.]47.73.0/24
101[.]47.74.0/24
101[.]47.75.0/24
101[.]47.76.0/24
101[.]47.77.0/24
101[.]47.78.0/24
150[.]5.128.0/24
150[.]5.129.0/24
150[.]5.130.0/24
158[.]51.96.0/24