

We are a leading provider of software and learning on web security. We make @Burp_Suite and @WebSecAcademy.
UK
Joined May 2008
- Tweets4.5K
- Following23
- Followers111K
- Likes239

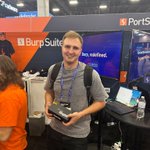


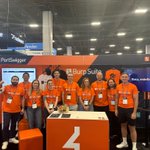


PortSwigger retweeted
You're in control with Burp AT.
The latest update makes sure Burp AT works your way:
📖 Custom skills for your methodology
🎯 /goal to keep it working until it gets there
💡 Requests, issues and docs as context
🚧 Reject, redirect or approve tool calls
#BurpAT

PortSwigger retweeted
“Burp AT integrates seamlessly with Burp’s existing tooling and functionality, instead of being just another chat interface to an LLM.”
Burp AT vs Juice Shop, Safe Mode on, no hints: 3 unintended RCEs and a critical handlebars CVE (CVSS 9.2).
@ElliottSaysWhat, web app pentester at Leidos, shares what to feed it, how to steer it and what it cost.
brandon-t-elliott.github.io/…
PortSwigger retweeted
How do you test how powerful an AI testing tool is?
@0xTib3rius built his own target: a bespoke vulnerable app, source code never published, with three known, tricky paths to RCE. Then he tried Burp AT.
Burp AT found a fourth within minutes.
#BurpAT

PortSwigger retweeted
“Burp AT re-wrote the book.”
Mario Contestabile used Burp AT to investigate potential IDOR and XSS findings in seconds, while keeping testing decisions firmly in his hands.
Share your best Burp AT story with #BurpAT for a chance to win exclusive swag. We want to hear yours too!


New research: CSS: the bomb inside your inbox 💣
Debuting at Black Hat USA today, @garethheyes shows how "safe" CSS in Gmail, Outlook, Fastmail, ProtonMail, Yahoo & AOL Mail becomes a serious attack surface - no JavaScript required.
#BHUSA #BlackHatUSA

What CSS alone can do:
💣 Brute-force login tokens from a URL, or run a real-time keylogger inside Outlook's own sanitiser
💣 Mutate "cleaned" CSS into live selectors that hijack clicks & deface UI
💣 Hide instructions from humans but not AI email agents, exfiltrating data
Responsible disclosure works: 2 Fastmail bugs fixed, bounties paid for both.
If you build or secure anything that renders untrusted HTML/CSS, this isn't one to miss.
Read the full white paper 👇
portswigger.net/research/css…

We're ready for you BHUSA Day 2 🎩
What a day one - incredible to meet so many of you, and even better to hear how many are already using Burp AT.
Huge congrats to our own @PortSwiggerRes @albinowax and @t0xodile, who took the stage to present brand new research.


Swing by booth #5342 all day for live demos of:
🔹 Burp Suite DAST, our enterprise-scale security solution
🔹 Burp AT, our new agentic solution built for practitioners
Heads up: swag is running low.
Tees, tattoos, stickers and caps are going fast - get to the booth before they're gone 👀
#BlackHatUSA #BlackHat2026 #BurpSuite #BurpAT #DAST
🚨 New from @PortSwiggerRes's James Kettle @albinowax
At #BlackHatUSA today: can AI invent genuinely new attack techniques, not just find known bugs?
Yes - and it compromised banks, government infrastructure, and an airport along the way.

☠️ AI can do original security research, not just pattern-match known bugs
☠️ It found a genuine 0-day (now CVE-2026-63078)
☠️Its biggest discovery, "Shared-Parser Confusion," only surfaced once a human stepped back in. AI took it 90% of the way; human judgment found the rest
This human-in-the-loop model is exactly what powers Burp AT, our agentic AI for pentesting - and this research is already shaping it.
Full exploit chains, open-sourced tooling, and defensive guidance here: portswigger.net/research/htt…

Day one of #BHUSA is here - come find us at booth #5342!
Live demos, talks, and a lot of swag all day...

⚡ 10:30 Corey Ball, "Instant API Hacker"
⚡ 11:00 — Alan Levy, "Stop Asking AI to Find Bugs"
⚡ 11:30 — Tib3rius, "Adventures with Burp AT"
⚡ 2:00 — Alex Wren (Intigriti), "Don't Manage Context, Share It via Burp Suite"
⚡ 2:30 — Ads Dawson, "How Gareth Heyes Made Me $22k"
And it wouldn't be Black Hat without the swag: tattoos, stickers, caps, our ultra-exclusive event tee, and the classic Burp Suite tee.
Come say hi, catch a demo, and see what's new in Burp Suite. See you at #5342 😎
#BurpSuite #BurpAT #DAST #BlackHatUSA #BHUSA
