

Secure your agentic development
New York, NY
Joined January 2019
- Tweets420
- Following463
- Followers7.3K
- Likes232




Pinned Tweet
We sat down with Adam Jordan (@XYLAMIC), Distinguished Engineer & Head of Secure, Sustainable Software at Shell, to talk about how Shell…
🤖 Enables autonomy to deliver secure software
💪 Defines strong security controls and automation
📈 Measures and articulates #AppSec success
Watch the full interview with @idanplotnik 👇
apiiro.com/resource/adam-jor…
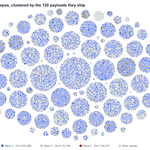
🚨 Shai-Hulud is still stealing.
Apiiro Research found worm files in 110 public @github repos, committed by trusted CI bots. Opening an infected repo in @claudeai or VS Code can trigger the stealer.
The coding agent is the new perimeter.
Read 👇
apiiro.com/blog/shai-hulud-l…

🚨 PHP2Shell: Find affected apps. Prioritize risk. Generate dynamic patch. AutoFix with context.
@Apiiro Guardian Agent connects to your WAF via MCP/CLI to generate dynamic patches with context from your Software Graph while fixes roll out.
Read 👉 apiiro.com/blog/php2shell-ph…

🎣 AI builds phishing kits. @huggingface hosts them. And we call it 𝗛𝘂𝗴𝗴𝗶𝗻𝗴𝗣𝗵𝗶𝘀𝗵.
We analyzed 182,093 DeepSite projects and found:
🔴 57 explicit phishing requests
📤 18 pages wired to send creds out
🚫 0 refusals across those requests
Read👇
apiiro.com/blog/huggingphish…

Apiiro retweeted

The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
🚨 𝗠𝗮𝗹𝘄𝗮𝗿𝗲 hiding in a photo. Inside an npm package.
Apiiro uncovered 𝗗𝗮𝗿𝗸𝗿𝗼𝗼𝗺: 19 dotenv look-alikes concealing PowerShell commands in a JPEG. 📸 distributed through fake @github exploit repos.
🔍 Full research 👇
apiiro.com/blog/darkroom-npm…

🚨 Waiting for more details on the @opencode breach.
One thing is becoming crystal clear: 𝗖𝗼𝗱𝗶𝗻𝗴 𝗮𝗴𝗲𝗻𝘁𝘀 𝗮𝗿𝗲 𝘁𝗵𝗲 𝗻𝗲𝘄 𝗽𝗲𝗿𝗶𝗺𝗲𝘁𝗲𝗿.
👇

We had a security breach last night related to a large scale distillation attack that impacted 1.4% of OpenCode Console users
We have notified them all this morning via email. If you did not get an email you were not impacted, it was a subset of users who had external providers linked
The incident is ongoing so we cannot share more details at this point but we are working with Anthropic, OpenAI, and Google to remediate
Developers are no longer writing code. AI agents are.
🔗 The @AnthropicAI Claude Compliance API is now integrated into the Apiiro Software Graph.
See which agent acted, what it installed, what code it generated and what it executed, in real time.
apiiro.com/demo
Apiiro joins the @chainguard_dev Athena coalition 🛡️
AI finds zero-days faster than teams can patch. The bottleneck is fixing without breaking code.
Guardian Agent turns a shared finding into a tested Autofix.
⚡ Free for open source maintainers
tinyurl.com/ytvrn8jh
🚨 One pastebin edit. A 1,000-Repo Malware Network.
We uncovered CheatSheet: 1,000+ malicious @GitHub & @gitlab repos posing as game cheats to deliver password and crypto stealers.
🔗 Read the full research: apiiro.com/blog/cheatsheet-f…

🏆 Apiiro is a 𝗟𝗲𝗮𝗱𝗲𝗿 in the first-ever 2026 @Gartner_inc Magic Quadrant™ for Software Supply Chain Security.
Coding agents are the new perimeter.
🛡️ Guardian Agent: Prevent. AutoFix. Protect. Across all coding agents.
🔗 apiiro.com/blog/apiiro-named…
Apiiro Security Research uncovered 𝗖𝗩𝗘-𝟮𝟬𝟮𝟲-𝟴𝟮𝟰𝟱𝟲, a critical vulnerability (𝗖𝗩𝗦𝗦 𝟭𝟬.𝟬) in argocd-mcp, the MCP server connecting AI coding agents to @argoproj
🚨 Exposed HTTP servers could enable unauthorized deployments. Read 👇
apiiro.com/blog/cve-2026-824…


Full report 👇
apiiro.com/blog/never-delete…

💎 Introducing SHINE, Apiiro's new integrations program! 💎
SHINE is a direct reflection of our goal to 𝐬𝐞𝐚𝐦𝐥𝐞𝐬𝐬𝐥𝐲 connect across our customers’ stack, providing a 𝐡𝐨𝐥𝐢𝐬𝐭𝐢𝐜 and 𝐢𝐧𝐭𝐞𝐫𝐜𝐨𝐧𝐧𝐞𝐜𝐭𝐞𝐝 view across every facet of their applications, software supply chains, risks, and changes over time. SHINE also reflects our vendor-𝐧𝐞𝐮𝐭𝐫𝐚𝐥 commitment to integrate with any and all security tools and processes and to 𝐞𝐧𝐫𝐢𝐜𝐡 findings with our deep code-to-runtime context.
We’re thrilled to unveil SHINE with our anchor partners—@Mend_io, @Checkmarx, @jfrog, and @Bugcrowd— and several dozens of integrations.
Read the full announcement on our blog: apiiro.com/blog/introducing-…
New regulations are upping the pressure on AppSec teams. 🗜️
🤿 Dive into our @CyberSecDive article to learn how #ASPM can lighten the load for AppSec teams and stay ahead of the risk and compliance curve. apii.ro/4beCZBA
Our new prioritization funnel makes it clear just how powerful Apiiro’s context is, enriching application security findings with key risk factors such as:
💥 High business impact
🌎 Deployed or internet-facing
📞 Used in code (our answer to reachability)
⚒ In applicative vs. test code
🤬 Has a high EPSS score or known exploit in CISA KEV
By understanding how likely a security finding is to be a real risk and its potential impact on your business, you can zero in on what matters most.
apiiro.com/blog/contextual-a…
Curious to see how a unified AppSec approach removes friction for devs and fills the gaps left behind by vulnerability-focused and siloed security tools? This @SANSInstitute webcast does just that while offering a first look at Apiiro’s #ASPM platform.
🎬 Watch the on-demand recording of this in-depth conversation between @idanplotnik, Co-Founder and CEO at @ApiiroSecurity, and SANS Certified Instructor Matt Bromiley to get a look at how Apiiro’s deep ASPM platform helps you:
🔍 Get complete and continuous application and software supply chain visibility
🔢 Prioritize security findings across your tools and Apiiro’s in-built solutions based on risk with deep code analysis and runtime context
📊 Accelerate the remediation of application risks and prevent risks earlier in the dev lifecycle
apiiro.com/resource/sans-web…
We teamed up with @SANSInstitute , a trusted advisor in the security space for over 35 years, to give the market a First Look at application security posture management (#ASPM)!
The report, authored by SANS Certified Instructor Matt Bromiley, covers current AppSec challenges and the need for ASPM and provides an in-depth look at Apiiro’s platform and its differentiators.
“Apiiro’s ASPM is a completely open platform but also includes native security capabilities that help provide fast time to value to bolster existing efforts or fill security coverage gaps, including secrets security, API security testing, sensitive data exposure prevention, and SCM and CI/CD pipeline security.”
Get your copy to see how Apiiro provides a unified platform for measuring and reducing application risk 👇
apiiro.com/resource/sans-rep…
Learn how Apiiro has enabled @cloudera to…
📦 Deeply understand their application security posture and consolidate their AppSec tools
⚒️ Reduce their AppSec backlog and save time fixing risks with deep code-to-cloud context
🧑💻 Proactively automate security feedback to empower developers to see the issues before they are released
Read the full case study: apiiro.com/resource/cloudera…