






Pinned Tweet
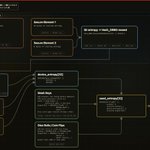
How the new COLDCARD seed generation works (MK4/MK5 ≥5.6.1 and Q ≥1.5.1Q):
Track the security status here: coldcard.com/security/status
Explore the interactive tool and source code here: scgbckbone.github.io/seedflo…

We are investigating how a post containing a phishing link was published from this account. It has since been deleted.
Do not visit or interact with that link. COLDCARD’s only official website is coldcard.com.
This account has used offline 2FA with tightly restricted access since 2017. We have contacted @X and are reviewing all account access.
We will share further verified updates here.

@Support — urgent escalation requested. A phishing post appeared on our account, yet we can find no corresponding login, session, or access record. Our credentials and offline 2FA remain secure.
This raises concern about unauthorized platform-level or administrative access. We are also aware of reports that access to X administrative accounts is being sold on darknet markets, although we cannot independently verify a connection.
Please preserve all relevant logs and have your security team investigate immediately. This appears to be a targeted, highly specific attack.
COLDCARD retweeted

Its true & honestly a great point to consider.
Just remember when you wanna hate in COLDCARD, atleast they are in the fight to try to help pay back their customers whose Bitcoin was stolen.
Ledger is just playing dumb about what happened.

A clear case is not decoration. It lets you inspect a COLDCARD for a component swap or implant. The tamper-evident bag, anti-phishing words, dual Secure Elements and verified firmware add independent checks. That’s defense in depth.
coldcard.com/docs/physical-n…

COLDCARD retweeted

Firmware updates and device authentication for both are done through the manufacturer’s app:
Trezor Safe 7 — Genuine check and firmware updates both happen in Trezor Suite (cryptographic attestation via secure elements + on-device confirmation of signed firmware).
Jade Plus — Genuine Check and firmware updates are done in the Blockstream app (Jade link could be used for firmware update).
After that, you can use Sparrow for day-to-day signing.
Coldcard Q doesn’t touch the internet ever.
COLDCARD retweeted

I’m hopeful @COLDCARDwallet gets bigger and better and continues to build. If you never have failure you never learn . They will learn from this and get better.


Press 2 at the OK TO SEND? screen to open Transaction Explorer. Step through every input being spent and every destination or change output instead of approving from a summary alone.
coldcard.com/docs/ready-to-s…
COLDCARD retweeted

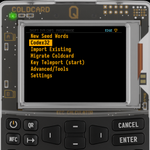
I know it's probably not many of you, but for the other crazy fucks like me still using it, this makes the first hardware device you can directly import Codex32 shares into for backup recovery.
COLDCARD firmware 5.6.3 and 1.5.3Q are live. 🧊
• Codex32 + Shamir backups
• Seed Vault names for temporary seeds
• PSBTv2 locktime support and stricter parsing
• More signing and firmware hardening
Read what’s new: blog.coinkite.com/coldcard-f…

COLDCARD retweeted

The closest thing to a perfect hardware wallet setup:
•Buy a Ledger, a Trezor, and a third signer (Coldcard/Keystone, or Tangem if it supports multisig on your chain). Only from official sites or authorized retailers
•Generate each seed separately with your own dice rolls, offline
•Combine them into a 2-of-3 multisig
•Back up the wallet descriptor with every seed. Without it, seeds alone can't recover a multisig
•Store each key and backup in a different location
•Test a full recovery with a small amount before funding
Your entropy is yours, and no single company's bad firmware, hack, or shutdown can drain you.
@Ledger @Trezor @Tangem @COLDCARDwallet @KeystoneWallet @Ledger_Support
COLDCARD retweeted

This will be an unpopular post, but I had lunch with some hardcore Bitcoiners (10y) today and the Coldcard incident was mentioned.
Everyone owning them was disappointed, but all of them are still using them because they like features no other model has. They still trust.

Coinkite will get flak on that post, given the missed RNG vulnerability...
That was a serious mistake - and we're all very disappointed.
Still, that doesn't change the fact that much of the CC featureset both in firmware & hardware (as in this example) added value to HWW security and still does.
While disappointed, it's hard to give up on the best.
I feel dirty typing this, because good people lost funds and I didn't - because I had older keys with strong passphrases and dice rolls, because I never trusted any of you mfers.
But...
It's still the best tool for the job when used properly.
I'm still using all my CC gear.
And fucking @nvk didn't give me a single freebie ever. Zero. Just a regular common customer. 🤣
It's always 100% self-interest, tho.
I don't care about what people say. I choose what I think it's best for my use case. As always before, time will be the judge.
Choose wisely.
TL;DR: They fcked up but I'm still bullish, but the struggle is real. 😬
COLDCARD retweeted

I've met the @Trezor team at @EthCC, know people from @Ledger, and was recommending @COLDCARDwallet and Opendime almost 7 years ago.
One thing I genuinely believe: these companies are not the bad actors.
They've spent years building products with a shared mission: helping people protect their assets and take control of their financial sovereignty.
And that deserves recognition.
But I think we need to have an uncomfortable conversation about the hardware wallet industry's current business model.
What happens when the weakest link is no longer the hardware or firmware, but everything surrounding it?
Shipping companies. Logistics providers. Authorized resellers. Customer databases. Third-party services.
Every additional intermediary introduces another potential attack surface.
Even when manufacturers do everything right, a compromise somewhere in that chain can expose customers to phishing, targeted attacks, privacy violations, or worse.
And every incident damages trust, not just in one company, but across the entire self-custody ecosystem.
I'm particularly paranoid about these risks because I believe privacy is inseparable from security.
A secure element cannot protect your personal information once it has been exposed through a third party.
So perhaps the question isn't whether these companies are doing enough.
Perhaps the question is whether the traditional hardware wallet distribution model is still compatible with the level of privacy and security we're trying to achieve.
Could open hardware, local assembly, DIY approaches, and minimizing customer data collection help reduce some of these risks?
I believe they're worth exploring.
That's part of the thinking behind #LeekWallet, an open-source DIY hardware wallet project exploring a different approach to self-custody.
Not a replacement for everything these companies have built. Not a claim of superior security. And certainly not an attempt to capitalize on anyone's misfortune.
Just another contribution to a problem our industry needs to solve collectively.
I hope those responsible for attacks are held accountable, and I hope we can turn these incidents into an opportunity to rethink how we protect users.
Self-custody should not require surrendering your privacy just to acquire the tools that protect your assets.
If you are interested into Open Source Hardware wallets please make sure to take a look into
initiatives.thedao.fund/init…
@ETHGlobal finalist
@EthAppsGuild hackathon winner

A clear case is not decoration. It lets you inspect a COLDCARD for a component swap or implant. The tamper-evident bag, anti-phishing words, dual Secure Elements and verified firmware add independent checks. That’s defense in depth.
coldcard.com/docs/physical-n…
COLDCARD retweeted
Bro. Coldcard entropy failure shook everybody to the core. I searched for another HW in the aftermath, but nothing came close to the Coldcard Q’s that I was using. I looked very closely at Trezor 7 and Jade Plus. I didn’t like that both used manufacture’s app.
The problem was seed generation- nothing more, and that was fixed. I still wasn’t satisfied. The dice roll seed output were checked against online checkers to make sure the math was correct-Repeated multiple times with same results. The same dice rolls entered into other coldcard q devices gave same seed. The math was properly calculated the same way in all coldcard q’s that I tested.
This wasn’t a light decision. It took a couple of weeks of intense thinking and testing to confirm to myself that ColdCard Q’s were extremely safe, and possible the safest air-gapped signing device. But, you do your own research. 👍😁
COLDCARD retweeted

No. With fixed firmware (1.5.3Q+), new seeds require your dice rolls plus proper RNG, so trust is reasonable if you follow that and use a strong passphrase. Coldcard Q fully meets your needs: dice entropy (or dice-only), QWERTY for complex BIP-39 passphrases, and pure air-gapped signing via QR/MicroSD/NFC with Sparrow—no manufacturer app.
Vs popular options: Ledger and Trezor require USB connections plus their apps and are not air-gapped. Keystone 3 Pro and Passport offer similar QR air-gap but often multi-coin. Coldcard’s dual multi-vendor secure elements and Bitcoin-only design give a stricter isolation model.
The transaction approval screen shows the outgoing total, fee, input/output counts, destinations, and change. COLDCARD signs only after you review and confirm on-device.
coldcard.com/docs/ready-to-s…
