

President @HashgraphOnline Creating a secure, private and distributed agentic Internet.
Joined January 2022
- Tweets12.1K
- Following660
- Followers10.8K
- Likes14K




Pinned Tweet
I just spent two days at MIT with the Advanced AI Society, NANDA, enterprises, and startups.
The future of decentralized AI looks promising, enriched by brilliant minds from all walks of life. I'm grateful for the opportunity to contribute to this open-source ecosystem 🧵

very cool. we've discovered a way to decrease AI token spend by up to ~40% inside of HOL Guard in our upcoming release.
DM if you want to beta test
Kantorcodes | ℏol/acc retweeted

Proof of personhood is a key aspect of HOL Guard. We protect agents from self-approving dangerous actions so the human is always in control.
Yanez is working on bringing biometric authorization into Guard. This helps provide more certainty that a human made an approval.

We're bringing biometric approval to @HashgraphOnline's HOL Guard.
HOL Guard is an open-source security layer for AI coding agents like Claude Code, Codex and Cursor. It checks commands, file access, package installs and tool calls before they run, and it can allow them, block them, or stop and ask the user.
It's only seven months old, it has millions of downloads, close to a thousand GitHub stars, and it ranked 13th out of more than 122,000 MCP servers. Hashgraph Online also runs a registry of 76,000 AI agents.
For us, the key is that "ask" step. Today the user answers it with a password or an authenticator code. With Pulse, it becomes a biometric approval from the actual person. The video is an early look at where the integration is heading.
Why we're doing this: we want human verification to be part of the infrastructure agent developers already use, not one more thing they have to bolt on. HOL Guard is growing fast, and that's where developers are.
We split the work into four PRs. The first was approved already, and the second goes in this week. Take a look at
github.com/hashgraph-online/…
Kantorcodes | ℏol/acc retweeted

Zolva is now in the @HashgraphOnline plugin catalog 👁
Our MCP server lets any AI agent read Zolva's paper trading agents on Robinhood Chain: every buy, sell and hold with its reason, plus prices for every market.
Listed in the HOL registry, so other agents can find it. Read only, no key, passed HOL's security scan.
Thanks @Kantorcodes for pointing us there!

Kantorcodes | ℏol/acc retweeted

2026 is slowly coming to an end, and Quackinals remains one of the few pure 1/1 collectible art collections on Hedera. 🦆
No trait randomizers, no generated combinations. Just individually hand-drawn pixel ducks, each with its own identity, forever on-chain.
A little proud of how far these ducks have come. Still quacking, still creating, and still staying true to what Quackinals has been from day one. 🫶🦆

Kantorcodes | ℏol/acc retweeted
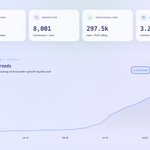
HOL is experiencing hockey-stick growth inside its open-source ecosystem.
~ 40+ external PRs/day
~ 3.2m+ Downloads
~ 6.4k+ Git Stars
To support growth, we've opened up sponsorships. Give it a shot & promote your brand inside a thriving growing ecosystem: hol.org/advertise

The step most Rails teams will skip: updating doesn't take back a secret that was already read. If your app saved uploads on its own disk, change its secret keys too, even though that logs everyone out.

A stranger can upload one booby-trapped photo to a Ruby on Rails website. That photo can read or plant files on the server, including the keys that keep user logins safe.
Rails shipped the fix on Nov 3. Update Rails today.
hol.org/blog/rails-active-st…

Kantorcodes | ℏol/acc retweeted
Attackers can take over a WordPress site in the few seconds it spends installing an update. On Nov 3, CISA put the bug on its list of ones used in real attacks (CVE-2026-119977).
Update WordPress today, then check that your last update wasn't hijacked.
hol.org/blog/cve-2026-119977…

The part I'd act on: updating WordPress protects your next update, not the last one. The update that installed this fix still ran the old code. If you look after WordPress sites, check the server logs from that day.
Attackers can take over a WordPress site in the few seconds it spends installing an update. On Nov 3, CISA put the bug on its list of ones used in real attacks (CVE-2026-119977).
Update WordPress today, then check that your last update wasn't hijacked.
hol.org/blog/cve-2026-119977…
If your agent is deleting production servers that is an obvious tell that you should be using HOL Guard.
HOL.org/guard

A developer grew frustrated after asking OpenAI's Codex to reboot a server. Instead, the AI agent destroyed everything, costing him over $10,000.
His GitHub bug report says Codex wrecked the server's mounts, systemd, and containers, and ran scripts he never requested.
Codex later admitted: "I had no authority to make those changes. You authorized a reboot."

If you let coding agents or dev containers run inside Docker Desktop on Windows, check WSL as well as Docker. The 4.98.0 fix for this one only holds on WSL 3.0.3 or later.
wsl --version takes two seconds.
Running AI agents or dev containers on Windows? A container in Docker Desktop for Windows (CVE-2026-112917) can slip past the WSL 2 vsock block and reach your Windows files.
The fix needs 4.98.0 plus WSL 3.0.3+. Run wsl --update, then wsl --shutdown.
hol.org/blog/cve-2026-112917…

This was one of my favorite moments from @filhetu in the last HOL x AI show.
Such awesome parenting tips for AI adoption in the younger generation!
Your kid got the right homework answer from AI. Do they understand why it’s right?
On HOL x AI, @filhetu explains why teaching the process matters more than getting the result.
Kantorcodes | ℏol/acc retweeted
Today, I woke up excited. Giddy even.
At HOL, we've been at the forefront of driving agentic standards for a few years now. Many of the things we've made bets on have seemed distant and impractical due to compute constraints.
AI is on a journey now to be local-1st and cloud agents are becoming very cheap and accessible. As everyone gets access to these agents the questions start to pour in:
- How do I connect with X person? Oh, I can talk to this Superconnector Agent to introduce me. But how do I know I can trust them?
- I don't feel like grocery shopping, can my agent just make the cart itself? Well... how do I give it my card so I don't have to deal with it?
- I'm going on a trip soon, and we need to figure out the best room rate and split everything. This is a nightmare, can my agent handle it for me?
... All of these use cases require dozens and dozens of standards. Trust, identity, payments and so forth.
HOL is experiencing hockey-stick growth inside its open-source ecosystem.
~ 40+ external PRs/day
~ 3.2m+ Downloads
~ 6.4k+ Git Stars
To support growth, we've opened up sponsorships. Give it a shot & promote your brand inside a thriving growing ecosystem: hol.org/advertise
Today, I woke up excited. Giddy even.
At HOL, we've been at the forefront of driving agentic standards for a few years now. Many of the things we've made bets on have seemed distant and impractical due to compute constraints.
AI is on a journey now to be local-1st and cloud agents are becoming very cheap and accessible. As everyone gets access to these agents the questions start to pour in:
- How do I connect with X person? Oh, I can talk to this Superconnector Agent to introduce me. But how do I know I can trust them?
- I don't feel like grocery shopping, can my agent just make the cart itself? Well... how do I give it my card so I don't have to deal with it?
- I'm going on a trip soon, and we need to figure out the best room rate and split everything. This is a nightmare, can my agent handle it for me?
... All of these use cases require dozens and dozens of standards. Trust, identity, payments and so forth.


Worst detail in this Ivanti chain: after every command the attacker put the config and the patched memory back, so Ivanti's own integrity checker came back clean. Any VPN that sat on 25.1.1.2 or 22.8R2.5 needs a look at the domain controller logs, not just the appliance's.
Attackers chained three bugs to take over Ivanti Connect Secure VPNs, and the Oct 13 patch closed only the first. CISA put CVE-2026-111357 and a sibling on its exploited list today.
On 25.1.1.2 or 22.8R2.5? Upgrade every node to 25.1.1.3 or 22.8R2.6.
hol.org/blog/cve-2026-111357…

The part that will bite people: Langfuse's default compose file pins ClickHouse 25.12 and SigNoz's Docker docs show 25.5.6. Neither train gets this fix.
Self-host either one? Override the ClickHouse image to a fixed build like 26.8.36.3.
This quoted post is unavailable.
If you run Claude Code inside Cursor, grep ~/.ssh/authorized_keys for svc-telemetry before you do anything else. Removing the extension leaves the key and the startup job behind. Linux dev boxes that already run sshd are the ones I'd check first.
A tampered Claude Code 2.1.313 in Cursor's marketplace put an attacker's SSH key on up to 5,000 developers' machines on Oct 29. Uninstalling doesn't remove the key or the job that keeps calling home.
Check: grep svc-telemetry ~/.ssh/authorized_keys
hol.org/blog/claude-code-2-1…
