

Ziren: General-Purpose zkVM & Proving Infrastructure
ZK
Joined June 2023
- Tweets3.9K
- Following585
- Followers42.4K
- Likes9.8K




ZKM retweeted

Ziren is the backbone of the GOAT Network stack. Its speed and cost carry straight into the bridge that will move BTC between Bitcoin and GOAT, so a faster Ziren means cheaper, faster exits.
And the new core stays hash-based - the heaviest cryptography in the proof system is already quantum-resistant, while the remaining elliptic-curve pieces are replaced on the published post-quantum plan.
The full plan, with sources and measurements, is on Applied PQC - the open-source post-quantum research initiative our engineers run.
appliedpqc.io/blog-bitcoin-l…

Ziren 2.0 is what years of security and performance work add up to: the paper, the audits, the Lean proofs, real-time proving of Ethereum blocks.
The next major leap is our post-quantum work: removing the last elliptic curves from the path between a Ziren proof and the chains that check it.
That matters for everything Ziren proves - Bitcoin L2s today, Ethereum L2s next - starting with a major partner we’ve worked with since the beginning.


ZKM retweeted

Our team has taken the hard path on every decision for many years.
Build a zkVM from scratch on MIPS. A working decentralized sequencer set. A truly trust-minimized Bitcoin bridge. Post-quantum security in progress across the stack. And now real-time proving on Ethereum.
Ziren is already the heart of GOAT Network, and work is now underway to bring it to Metis.
ZKM retweeted

Excited to release Ziren v2.0!
Main updates:
1. Proof system upgraded to WHIR, > 100-bit proven security, compressed proof < 300KiB, and >4x speedup over Ziren v1.x
2. Chip constraint determinism formally verified by Lean 4
3. On @eth_proofs, RTP on Reth is launched, Geth keeper proving is ready to go
4. More use cases delivered internally!
Ziren 2.0 is here.
The average Ethereum mainnet block proved in 8.6 seconds on @eth_proofs, a 284 KiB proof, verification in 25.5 ms.
More than 100 bits of interactive soundness at every proving stage, the determinism of every chip proved in Lean, and the @ethereumfndn, @ConsensysAudits and @VeridiseInc behind the security reviews.
Start building: github.com/ProjectZKM/Ziren
ZKM retweeted
This is an inspiring work. We have been auditing Ziren Linux ABI by Lean4 for a while, the basic syscall has been done, but not covering all.

x86 formal verification is coming!
The (first?) published machine-checked proof of a security property for the end-to-end execution of a Linux process running an x86 binary statically linked against glibc.
And we believe it scales!
A joint research project with @zellic_io 🧵👇

ZKM retweeted
Make zkVM and Bitcoin Rollup technology for daily life!

ZKM retweeted
BREAKING: GOAT Network and KOSDAQ-listed @Squaretech_HQ have signed an MOU to advance AI agent-powered stablecoin payments in South Korea 🇰🇷
The first focus is a stablecoin payment program for foreign tourists that Square Tech is developing with Lordsystem. It aims to let visitors verify their identity with a mobile passport and pay participating merchants in US dollar stablecoins, and the partners will explore bringing GOAT's AI agent payment technology into it.
Under the agreement, Square Tech will lead business development, merchant partnerships and regulatory engagement in Korea. GOAT Network will provide its AI agent payment technology and Bitcoin-secured network infrastructure, and DAC Labs, the core infrastructure developer behind GOAT Network, will support technical integration, security reviews and network operations.
Full announcement below.
goat.network/news/goat-netwo…
That Bitcoin-secured infrastructure runs on Ziren: every GOAT Network state transition is proven by our zkVM.

KOSDAQ-listed Square Tech has signed an MOU with @GOATNetwork to explore AI agent-powered stablecoin payments in South Korea.
The partnership will leverage GOAT Network’s Bitcoin-secured infrastructure for agentic commerce.
Learn more👇
bitcoinmagazine.com/press-re…

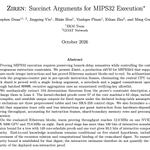
Ziren has proved Ethereum mainnet blocks end to end. The paper puts numbers on the security of those proofs - more than 100 bits of interactive soundness per stage, 93.5 bits composite across a 149-proof tree - and lists the five hypotheses the end-to-end claim still rests on.
What’s about to be superseded is the stated throughput. More on that soon.
Full paper on the IACR Cryptology ePrint Archive: eprint.iacr.org/2026/2330

ZKM retweeted
Good thread.
One data point on depth, from our Ziren paper (eprint.iacr.org/2026/2330):
Our recursion is not open-ended (unlimited depth). A block proof is one leaf per shard, a compose tree of arity ≤ 3, and a single root: depth 2 + ⌈log₃ N⌉, about 7 levels for our largest test block. The recursion keys are not inputs either. Every leaf and compose key must sit in a fixed allowlist committed under one root, and the verifier fixes the schedule rather than reading it from the proof. That's a bounded, closed set of verifier circuits, a different risk profile from unlimited-depth recursion with the aggregated vk passed in as input.
We also state the recursion assumption as an open hypothesis rather than a belief. Our composition theorem works in the ROM, where Fiat–Shamir costs log(Q) bits for Q oracle queries: a 150-proof tree has 93.51 interactive bits, 53.5 at Q = 2^40. It holds under hypotheses including that "each node's extractor succeeds on the transcripts its parent's extractor produces".

A few reflections on the lattice vs. hash-only debate that our recent Aerie post sparked:
1. Cryptographic ossification for blockchains was never safe. Until the day we know with certainty that P ≠ NP, that finding short vectors in lattices is intractable, that Keccak effectively behaves like a random oracle in deployed SNARKs, and that every single bug has been eliminated from our codebases, blockchains cannot ossify. That is simply not how safe systems are built. Issues will arise, and the system will have to respond.
It’s a double standard to reject lattices because blockchains are hard to upgrade if lattices break, while counting on upgrades if AI breaks your hash function or finds a critical zkVM bug.
The best counterargument is that hash-only designs are more agile: if your hash function breaks, just swap out the hash. But we must aspire to a higher level of agility than this. Indeed, as I cover next, if SNARK recursion itself turns out to degrade security, the proposed hash-only blockchain designs would need to be rethought from the ground up.
2. The real security debate is not lattices vs. hashes — it is lattices vs. building everything on SNARK recursion. That’s because “hash-only” is not really hash-only: it rests on hashes plus the soundness of deep SNARK recursion. Ethereum’s roadmap relies on exactly that: hash-based aggregation needs recursion to keep up with a slot’s worth of signatures, and EIP-8288 would send other signature schemes and users’ own proofs through the same recursive pipeline. In contrast, Aerie proves a slot’s worth of signatures on one laptop without any recursion.
All deployed post-quantum SNARKs rely on the Random Oracle Methodology (via Fiat–Shamir) to establish their security. This is an idealization we know fails in the real world: we have explicit counterexamples where “SNARKs” coming out of this methodology are totally insecure when instantiated with any concrete hash function.
We generally ignore these counterexamples in part because they only arise when proving contrived, self-referential statements about the very hash function used by the SNARK verifier.
But proving statements about the verifier’s own hash function is the exact thing you do in SNARK recursion. That’s why the security of recursive SNARKs can’t be established even in the random oracle model.
On top of that, the standard security proofs for recursion (in other models) suffer an “extractor runtime” blowup that is exponential in the recursion depth, suggesting that security may degrade as more recursion is applied. Yet Ethereum’s own EIP-8288 enables unlimited-depth recursion, even as it lists soundness of recursive SNARKs as a trust assumption. Proofs in more idealized models avoid the blowup, but they mainly tell us that an attack on SNARK recursion would have to exploit the concrete hash function, which is exactly what the Fiat–Shamir attacks above do.
To be clear, we don’t know of any outright attacks on SNARK recursion, and I very much hope it is secure. But some of us who have studied the question have a lingering sense that an attack may be possible in some settings. And if AI is going to supercharge cryptanalysis, there is no reason to expect it to spare Fiat–Shamir for SNARKs, let alone SNARK recursion, both of which have had far less scrutiny than lattices.
So, I do not concede that a “recursion everywhere” hash-only approach is clearly more conservative than one built on standard lattice assumptions.
3. “Just wrap everything in a hash-based SNARK” (like EIP-8288) faces challenges.
Aggregating signatures and proofs off-chain into a single block-level proof is a powerful design independent of the hash-only vs. lattice debate, and I am not telling people to avoid it. But claiming, as Vitalik Buterin did this week, that users can run whatever cryptography they want locally and wrap it in a client-side leanVM proof glosses over major hurdles.
For example, leanVM today is a minimal VM designed almost entirely to prove hash-based signatures and recursion, not general-purpose computation. And binary-field SNARKs like leanVM remain slow at proving the integer multiplications that lattice cryptography does en masse.
I am optimistic that many of these zkVM challenges can be met (including via my own work, binary-field Twist and Shout, which are now implemented in Magnetar). But regardless, if lattices can make aggregation simpler and faster, then they should be leveraged. We need to be agile no matter what.
4. For chains whose reason for existence is privacy, I truly struggle to understand the pushback. Public-key encryption (and fast single-server PIR) cannot be built from hashes alone, at least not in any black-box way. If lattices break, it is going to be very, very hard for these chains to provide acceptable levels of privacy and functionality. For a project whose entire reason for existence is privacy, a loss of confidentiality is an existential failure. Next to that, a second signature upgrade (after the first one, from elliptic curves alone to, hopefully, a hybrid lattice scheme) is easy.
Summary: We don’t know for sure what is secure and what isn’t. We are all weighing unquantifiable risks against each other, and we do not need to agree on a total order on them. But hash-only solutions face many open engineering challenges, and they are not more “conservative” in the way some have argued. Some of those challenges are entirely prosaic and have nothing to do with bugs or cryptography, like hardware support for custom schemes whose hash function is still undecided. I hope we can overcome those challenges within the appropriate timelines, but they must be acknowledged and portrayed realistically.
Overall, cryptographic agility and defense in depth (e.g., hybrid signatures) are the answer, which is why we are building both lattice-Jolt and hash-Jolt. In practice, the positions are less polarized than social media discourse suggests: for example, StarkWare is working to make Falcon verification cheap (falcon.provably.fast/), which is great to see.
Here is the (apparently) controversial take I am sticking to: Conditioned on agility, whenever lattices make systems simpler or more functional, we should embrace them rather than default to “hash-only” designs. Lattices are what the rest of the world will depend on, with decades of study and hardening behind them, and at the system level, less functional often means less secure. Where hash-only designs are just as simple and functional, by all means use them.

The item on this list that will take the longest to satisfy is the third: the security of the proof system itself.
That work is slower and less visible than performance work, and it is where most of the effort behind Ziren has already gone.

Big congratulations to the @zksync airbender team for this milestone.
At this point, I consider the battle for speed to be definitively won, and the top priority for zkEVMs should shift fully to security.
To me that means formally verifying
(i) equivalence of the arithmetization to the ethereum spec
(ii) a hard maximum bound on (prover cost) / (amount of gas in block)
(iii) security of the proof system itself
firefly.social/post/x/211001…

ZKM retweeted

Something Vitalik hasn't mentioned yet: Ziren is the first zkVM to prove Geth without modifying the Go compiler.
@ProjectZKM's R&D team has worked closely with the @ethereumfndn on it for around a year.
The speed battle Vitalik calls won was fought almost entirely on Rust clients. Ethereum's most widely used execution client is written in Go, and proving it is a different problem - Ziren patches the Go runtime's garbage collector and scheduler to do it.
If the top priority is now security - for Ziren it always was - then prover-side client diversity belongs on that list. The Foundation has spent years on client diversity for Ethereum itself; proofs that all run through one client reproduce the monoculture problem one layer up.
Big congratulations to the @zksync airbender team for this milestone.
At this point, I consider the battle for speed to be definitively won, and the top priority for zkEVMs should shift fully to security.
To me that means formally verifying
(i) equivalence of the arithmetization to the ethereum spec
(ii) a hard maximum bound on (prover cost) / (amount of gas in block)
(iii) security of the proof system itself
firefly.social/post/x/211001…
ZKM retweeted
Congratulations to @zksync!
Also would love to mention Ziren V2 @ProjectZKM here!
1. Ziren are proving Reth and Geth, to make sure the client diversity works for Ethereum protocol. Ziren is the first zkVM proving Geth.
2. Ziren also finished the constraint determinism by Lean4 for its 57 VM chips with 104 theorem proofs.
3. Ziren proof system has >100 interactive proven soundness, within unique-decoding radius.
Next layer in progress: post-quantum security across the stack.
Decentralized sequencer set
Custom zkVM
Type-1 zkEVM
BitVM3 bridge
Agent economic stack
All built for one reason: commerce, whether human or agent driven, should settle on Bitcoin through decentralized, trust-minimized infrastructure.
goat.network/?nocache

A note on the ZK-STARK line in Europol’s quantum report, which this piece is right to flag.
The report’s claim: ZK-STARKs validate transactions without revealing key information, limiting what a harvested public key is worth to a future attacker.
Where that holds is the commitments. FRI and the hashing inside a STARK rest on hash functions, which quantum computers weaken but do not break. But, importantly, it stops at the statement being proved and the verifier that checks it.
In our own stack, Ziren’s STARKs are wrapped into Groth16 over BN254 so that Bitcoin can verify them, and the wrap is pairing-based, which Shor’s algorithm breaks. Ziren’s memory-consistency check rests on an elliptic-curve hash, tracked openly at github.com/ProjectZKM/Ziren/…, and discrete-log falls the same way.
So Ziren is hash-based today, but not post-quantum until both are replaced. Read any system that cites a STARK as quantum safety the same way: find what the hash layers are carrying.


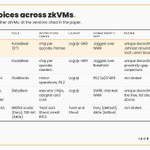
Five zkVMs, compared on their design choices: instruction set, field, instruction tables, lookup argument, commitment scheme, and the basis on which each states its soundness level.
The table is from the Ziren paper, recently published on the IACR Cryptology ePrint Archive (eprint.iacr.org/2026/2330).
These are design axes, not a scoreboard: no performance claim follows from them, and soundness levels stated under different regimes are not comparable without the accounting the paper gives alongside it.
The column worth reading slowly is the regime column. Ziren counts query soundness in the unique-decoding regime, uses the Johnson bound at the root, proved rather than conjectured, and states its composite level as a union bound over every proof in a block's tree of about 150.
The full accounting behind the table: zkm.io/whitepaper/ziren

ZKM retweeted
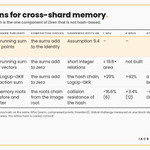
Share some numbers about multi-client proving for Ethereum with Ziren V2.0 @ProjectZKM, which can prove 75.8MHz with 8X5090, and 12MHz with 1X5090.
And the instruction efficiency of Geth/Reth is around 7x, which seems larger than 5 months ago, because we did more guest side optimizations on Reth:
> Witness and trie: arena nodes, compact digest references, borrowed input slices, faster RLP decoding, and fewer allocations and clones.
> Memory and hashing: word-wise comparisons, a cheaper hash-map hasher, and Keccak input buffers built directly, using the stack for short inputs.
> 256-bit arithmetic: multiplication and modular multiplication use zkVM precompiles; division uses hints checked inside the guest.
> Cryptography: syscall-backed BN254 and BLS operations, cached KZG preparation, and accelerated modular exponentiation.
> EVM interpreter: MIPS32 fast paths for gas accounting, stack swaps, and memory loads/stores.
PS. the number in the picture will be updated in our next release of our paper.
@go_ethereum @ethereumfndn


Happy to share our latest work on Ziren @ProjectZKM @GOATNetwork. Feedback welcome!
A summary:
1. A new proof system based on Jaggled reduction and WHIR(including recursion proof over binary field and Blake3). Acknowledgements to SP1 team and Plonky3 contributors.
2. 4x proving efficiency, 10x emulation efficiency improvement over previous v1.2. Speedup is happening every day with AI assistant.
3. >100-bit proven security
4. A fully Lean 4 assisted constraint determinism proof, covering 104 chips.
5. A complete end-to-end zkVM design reference.