

HackerOne All Time Top 10 | Cybersecurity | https://teapawt.net/t.co/Ai76qek7Ag |🧑💻
Chandigarh, India
Joined August 2020
- Tweets237
- Following125
- Followers2.3K
- Likes376


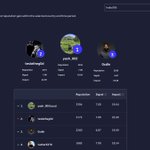


Crossed 50K reputation points and reaching all time 7th rank on @Hacker0x01
Glad to be a part of this great community
#BugBounty

17
181
4,219

2nd in India and 8th in the world in 2025
@Hacker0x01
Happy New Year 🙌
#bugbounty


Gear up, Indian Hackers! Exclusive LHE in Chandigarh (Virtual: Nov 15-22) & (In-Person: Nov 23). RSVP now for bigger bounties, networking, food, and awesome swags from @Hacker0x01 and program team!
Don't miss out.
h1.community/events/details/…
#BugBounty #InfoSec

2025 Q3 🎥
Ranked 1st in India and 7th globally, gaining 3394 reps, submitting 214 reports in Q3 on @Hacker0x01
Again ranked 1st(5th consecutive time) in iOS app asset in the world & 3rd in Web apps asset.
Ranked 3rd in BAC bug type.
Current Reps/Rank: 20822/63
#BugBounty


Turns out I crossed 20k reps on @Hacker0x01 and I wasn’t even aware of it until just now.
Thanks to last 90 days reps and last 2 years consistency
#BugBounty


7
110
6,850
When a program team from @Hacker0x01 personally email you for appreciating the findings.
These kinds of email always lets us to keep going.

2025 Q2 🎥
Ranked 2nd in India and 11th globally in the @Hacker0x01 2025 Q2 Leaderboard.
Report Submitted: >240
Reps Gained: >3000
Ranked 1st in iOS app asset, 4th in web apps and 4th in BAC issues globally.
All-time Reps/Rank: 17438/80
#BugBounty #CyberSecurity #hackerone


Yash Sharma retweeted

HackerOne Clubs across Asia-Pacific are adding fresh energy. Welcome to these new Brand Ambassadors!
🇮🇩 @zeeagils & 🇮🇩 root_geek280 (Indonesia—new club!)
🇮🇳 @hetroublehacker & 🇮🇳 @05__Yash (India North)
🇮🇳 @0xcharan (India South)
🇮🇳 @ThisIsDK999 & snifyak (India East)
🇧🇩 @0x0asif (Bangladesh)
From Bangalore to Bandung, they’ll nurture talent, run CTFs, and keep the region #cyberstrong. 💪
Check out the program: bit.ly/3lMs6lO
#AppSec #EthicalHacking #H1Club

April 15th, 2021 —> First ever bounty received on @Hacker0x01
April 23rd, 2025 —> Reached all-time top 100 hackers on @Hacker0x01
Glad to be a part of cybersecurity 🫡
#bugbounty #cybersecurity #hackerone


Presented with the Most Valuable Hacker award in @zomato 1st ever Live Hacking Event in collab with @tusharSharma_0 😒
Such higher rewards with extra bonuses makes any LHE attractive👏
Hard to figure out @letsblinkit delivery time is faster or the team’s triaging🤔
#BugBounty


2025 Q1 @Hacker0x01 Leaderboard
Ranked 2nd in India and 14th in the world, gaining over 2300 points in a single quarter
Ranked 1st in the world in discovering iOS mobile app vulnerabilities
Achievement are one thing and getting a $25K duplicate balances it all😶🌫️
#bugbounty


Yash Sharma retweeted

Finished in the Top 10 of the Q1 India Leaderboard on @Hacker0x01! Really hard with a full-time job 😅😥
Best quarter in terms of bounties earned on @Hacker0x01
Reported some quality bugs. Some of them, coming in collaboration with @05__Yash
#hackerone #bugbounty


Crossed 14K reputation on @Hacker0x01
Soon to be in all-time top 100🤞
Competition.. NOT easy. To move even 1 rank up, hundreds of points needs to be achieved when nearing top 100.

2024 Recap 🎥
Ranked 1st in India on @Hacker0x01 Leaderboard and 14th in the world.
Submitted over 800 reports, gaining over 8500 reps in 2024
Also, ranked 1st in the world for discovering vulnerabilities in iOS app asset in 2024
#bugbounty #cybersecurity #ios


Here is my 2024 journey on @Hacker0x01: 798 vulnerabilities reported, including 259 high-severity reports and 82 critical findings!
The most productive month was June, with 130 new submissions🫨
Here's to more discoveries in 2025, hopefully 🚀
#HackerOne #InfoSec #BugBounty

Hey Bounty Hunter
Here are the steps to configure your iOS device with the Burp Suite proxy.
1. Change your burp settings to below.
Go to Proxy > Proxy Settings > Select running proxy > Change it to "All Interfaces".
2. Copy the IP address(arrowed one).
3. Later in the proxy itself, click on Regenerate Certificate.
4. Go to your iOS device > Settings > WiFi > Touch the "I" icon beside your connected WiFi.
5. Scroll down and click on Configure proxy > Set it to Manual.
6. Input the IP that was copied and the port that is connected to the proxy in Burp.
7. Go to Safari browser in iOS same device and input in the URL: "HTTP://burp"'.
8. Download the certificate.
9. Go to settings again and there will be an option to install the certificate Near Wifi/Bluetooth option. Install the certificate.
10. After installing, in the settings itself, search for certificate > select Trusted Certificates > Certificate Trust Settings.
11. Enable the PortSwigger CA certificate.
You are all set. All the apps traffic you open in your iOS device will be proxied in Burp Suite.
The screenshot belongs to the 1st and the 3rd steps respectively.
I hope to see some more bounty hunters in the iOS assets ranking after this post🤞😉
PS: I don't know how to link my previous post with this, could really use the help.
#BugBounty #ios #cybersecuritytips #bounty


2024 Q3 @Hacker0x01 Leaderboard
Ranked 1st in India and 13th in the world in the 3rd quarter.
Along with this, ranked 1st in iOS and 6th in web application assets in the world.
#bugbounty is amazing!!!
P.S. - Didn’t forgot about iOS proxy with Burpsuite post.
#ios #websites #CyberSecurity #hacker


Crossed 10000 reputation points on @Hacker0x01, gaining 8013 reps in last 365 days.
Also reached all time top 170 hackers on @Hacker0x01
Next target - Reach all time top 100 on @Hacker0x01 without disturbing my personal life and as chill as possible like before.
#bugbounty #cybersecurity #achievement

