

Security Researcher
Joined September 2013
- Tweets2.8K
- Following808
- Followers425
- Likes4.9K



Pinned Tweet
This is my latest profile as an SR at @code4rena . I'm posting it here as appreciation for C4, which has become a place for SRs to develop and compete at teh same time.


Feeling blessed and grateful 🙏
Submitted 5 bug bounty reports: 1 Critical, 2 High, and 2 Medium. All findings were confirmed and fixed by the project team.
Thank you to the team for taking security seriously and recognizing my work. Proud to help make the ecosystem safer!

0xDemøn retweeted

OpenZeppelin is now officially a part of S&P Global.
The acquisition we announced in September is finalized. OpenZeppelin’s decade of securing and building the infrastructure onchain finance runs on now meets @SPGlobal's more than a century of helping markets understand risk. Together, we can help institutions and builders move onchain with greater confidence.
To our clients and to all the users of OpenZeppelin open source tools:
• OpenZeppelin Contracts and all our open source applications and tools remain open source, free and publicly maintained on GitHub.
• Security audits, secure development work and ecosystem programs continue with the same team, brand, quality and customer experience, now backed by S&P Global’s research capacity, market data and institutional reach.
For the last decade, OpenZeppelin has set the security standard for onchain finance. Now we take it to the scale of global finance.
Read the full announcement: press.spglobal.com/2026-10-2…


0xDemøn retweeted

Full write-up & technical breakdown is live on Medium.
Diving deep into the CosmWasm / IBC v2 bugs, git fix correlations, and the administrative handling:
medium.com/@hdny679/triaged-…


The engineers behind @cosmos CosmWasm wasmd are clearly capable of telling real bugs from spam.
I reported 3 vulnerabilities through @Hacker0x01, and the Cosmos team validated and officially triaged all of them.
They had the capability to handle this properly. Instead, there was no follow-up, no technical discussion, and zero professional handling. it turned into a free security audit handled in bad faith: using retroactive rules to slap a spam label on valid findings right before quietly pushing the exact same patches, then locking every single report.
Code and commit trails don't lie, @cosmoslabs_io labels do.
I broke down the technical root causes, logic flaws, commit trails, and evidence in the write up: github.com/7tecra7/cosmos-sp…


0xDemøn retweeted
The engineers behind @cosmos CosmWasm wasmd are clearly capable of telling real bugs from spam.
I reported 3 vulnerabilities through @Hacker0x01, and the Cosmos team validated and officially triaged all of them.
They had the capability to handle this properly. Instead, there was no follow-up, no technical discussion, and zero professional handling. it turned into a free security audit handled in bad faith: using retroactive rules to slap a spam label on valid findings right before quietly pushing the exact same patches, then locking every single report.
Code and commit trails don't lie, @cosmoslabs_io labels do.
I broke down the technical root causes, logic flaws, commit trails, and evidence in the write up: github.com/7tecra7/cosmos-sp…
0xDemøn retweeted

Update: Immunefi upheld the duplicate closure.
Their own fix-bypass policy says a bug that wasn't effectively fixed should be reported.
That's exactly what I did. The PoC in my report still works after the attempted fix.
Yet their mediation response didn't even mention the fix-bypass policy.
So what's the point of having it?
Why would any whitehat spend time checking whether a fix actually works if the answer is still "duplicate, no reward"?
I thought Immunefi was supposed to keep this fair.
Instead, they're keeping their clients happy.


Projects trying to rug whitehats seem to be the norm lately.
I recently found a High severity bug. The project closed it as a duplicate of an earlier report. Which is technically true since both have the same root cause.
The funny part is they already tried to fix it.
And failed.
My PoC demonstrates that their fix can be bypassed and the bug is still exploitable.
@immunefi even has an explicit fix-bypass policy for cases like this:
immunefisupport.zendesk.com/…
But I guess it's easier to close the report than fix the bug and pay the whitehat.

0xDemøn retweeted
I decided to give Immunefi Studio Review a shot before submitting a High severity finding.
The submission for this particular program costs $75 so I decided to pay $20 for a Studio review first to sanity-check the report.
Immunefi Studio came back with "Ready" - "meets standard escalation criteria with no blocking technical flaws".
To be fair, it suggested a couple of improvements to the PoC which I applied to the report before submitting.
So I paid the $75 and submitted.
15 minutes later, my favorite guy Andrew closed it as a duplicate of a report submitted 9 days earlier.
So that's $20 for Studio Review + $75 submission fee = $95 to have one Immunefi bot tell me "send it" and another Immunefi bot tell me "duplicate report".
That's the part I'm struggling with.
Immunefi Studio is explicitly advertised as checking duplicate risk too.
If a duplicate has already been sitting in your system for 9 days and the Review bot can't catch it, but the triage bot catches it almost immediately after submission, then what exactly is the value proposition here?
@immunefi / @MitchellAmador - I genuinely think this is useful feedback if you're still iterating on Immunefi Studio.
But from the whitehat side, this flow feels pretty broken.
Especially when it costs $95 to get to this outcome.

0xDemøn retweeted
Small @immunefi ask:
When a report is closed as "Duplicate of invalid", show why the original was rejected as invalid.
Right now we only see the original report, NOT the closure reason.
It feels like basic courtesy when I paid 75 USDC to submit.

0xDemøn retweeted

.@DarioAmodei and @sama!
it is high time you put some money into KYC, or whatever trust/verification system you want, and give legitimate security researchers access to your best models.
1. we’ve helped secure both of your companies multiple times against issues that could have had serious consequences. i wouldn’t be surprised if we can keep doing that, and i also wouldn’t assume every capable attacker is reporting what they find.
2. there is now a KVM escape that, if researchers hadn’t found it first, could have been exactly the kind of thing your models eventually find in another hugging face style incident.
you know, the list will keep growing, this is not the end.
it rationally makes sense to get as many trusted researchers and companies as possible red teaming your companies, your models, and the infrastructure they depend on.

Fixed now.

I experienced the same thing or even worse.
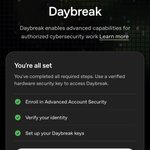
Until now I still have access to daybreak blue and I also got an email to re-verify but instead as shown in the image below for the current situation.
I have also already set, 1 yubikey and 2 other security.
cc @thsottiaux @sama


I experienced the same thing or even worse.
Until now I still have access to daybreak blue and I also got an email to re-verify but instead as shown in the image below for the current situation.
I have also already set, 1 yubikey and 2 other security.
cc @thsottiaux @sama

According to latest email from Open AI, Existing Daybreak users are being forced to do Re-KYC? and no matter what we do its being failed with Persona hence unable to setup Daybreak
Can anyone from @OpenAI help?


0xDemøn retweeted

Security researchers are the backbone of onchain security today and across the broader internet. Because of them, we are surviving the AI security apocalypse.
And that has been forgotten.
Too many companies went from valuing SRs one day to abandoning them the next. They weren’t even thrown a life raft to follow along.
At Immunefi, we see things differently.
SRs were the core of security before, they remain the core of security today, and they will be the core of security tomorrow.
We need to figure out, as an industry and as a community, how we’re going to adapt to these changes; how to bring all security researchers with us, along with the recognition and support they deserve for keeping us safe thus far.
SR Summer was our way of showing a little recognition, and with Immunefi Studio, we will continue to put as much power in the hands of SRs as possible.
Thanks to all those who took part, and congratulations to the winners!
0xDemøn retweeted
They closed a Triaged Critical as Spam.
Cosmos wasmd / IBC v2. 1 Critical, 2 High.
24 Apr changelogs list the fixes.
4 May the reports are locked as an “unrelated audit.”
teapawt.net/0wlxzy/status/20969381…
@cosmoslabs_io


What happens when 1 Critical and 2 High vulnerabilities are reported to a major Web3 ecosystem?
The reports are moved to Triaged, closed as “Spam,” later matched to public fixes, then locked when disclosure is requested.
A documented @Hacker0x01 timeline. Technical write-up next. 🧵
#BugBounty #Infosec #cybersecurity @cosmoslabs_io @interchain_io
0xDemøn retweeted

And here I am, having reported vulnerabilities throughout my career that could have resulted in a total of several billions (yes, with a B, > $2B) being *stolen*, while my total earnings are around $2M.
So what's the lesson the industry is teaching researchers?
That next time we should steal the funds first, then negotiate a "responsible disclosure," return 80–90%, and walk away with 10–20%?
Obviously, no. But it's insane that the incentives can make that rhetorical question even possible.
The bounty world is broken.
Blackhats exploit a protocol and get treated like kings in negotiations. Meanwhile, whitehats disclose the exact same kind of vulnerability privately, prevent any damage from happening, and then spend months arguing with projects that try to downgrade the finding and pay the bare minimum.
I'm fighting several cases like this right now. Millions of dollars protected, vulnerabilities responsibly disclosed, and yet projects still don't want to pay the amounts they themselves advertised.
We should be making responsible disclosure the overwhelmingly obvious choice.
Instead, the current state of Web3 is doing its absolute best to discourage whitehats while creating increasingly attractive incentives for blackhats and "grayhats".
Those incentives are backwards, and eventually the ecosystem pays the price.


0xDemøn retweeted
What happens when 1 Critical and 2 High vulnerabilities are reported to a major Web3 ecosystem?
The reports are moved to Triaged, closed as “Spam,” later matched to public fixes, then locked when disclosure is requested.
A documented @Hacker0x01 timeline. Technical write-up next. 🧵
#BugBounty #Infosec #cybersecurity @cosmoslabs_io @interchain_io
0xDemøn retweeted

Blockstream’s Liquid Network (@Liquid_BTC) reportedly hacked by whitehats for 4k bitcoins.
8db751a650ae2f12006b7e8c69a75e4df360e8afd6b9e05ae0b9fa6458a7b140
Hacker message: "we are whitehats. contact us on chain"
c103de95817b43f2df635ec6f35ff126ca26a7c6d20570c4b01866b2b3e69a19