

Bug Bounty Hunter. Until death, all defeat is psychological.
India
Joined June 2024
- Tweets107
- Following98
- Followers310
- Likes94


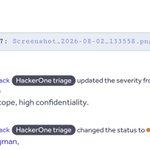


If ghosting is an art, then Hackerone remediation team is Picasso. 🎨 @Hacker0x01
#bugbounty #hackerone
2
232

TheHatedOne retweeted

Next hacker summer camp giveaway!
3 seats to our “The Bug Hunters Methodology” course!
Like and share to be entered!
arcanum-sec.com/training/the…

TheHatedOne retweeted
Giveaway time!
Up for grabs is 3 free tickets to our “Attacking AI” live course!
Repost and like to enter!
arcanum-sec.com/training/att…


Reported an issue 30 min ago, got triaged on @Hacker0x01 . Then re-read the scope & realized, asset is in-scope but not eligible for bounty 😭
Recon > hype.
Tip: Check scope eligibility before you celebrate.
#bugbounty #bugbountytip


Made a huge mistake today. Reported an issue on H1, then self-closed it as "intended behavior." After more digging, turned out it WAS a real security bug, So I re-reported it. New report got marked Informative because of my own earlier comment. Wht should I do next?
#bugbountytip


4
32
4,025
TheHatedOne retweeted

ًWrite-up is now available you can read it here medium.com/@youssefmohamedsa… Follow Me to Stay updated with more Findings


How I Discovered 23,000+ Leaked Records Through Google Dorking by mrx_w_ medium.com/p/how-i-discovere…
Always try google dorking while hunting
Credits : @MrxXb12 nice finding and congrats for the bounty brother🤍
TheHatedOne retweeted

Just published my first bug bounty write-up 🎉
How I Hacked a Live Chatbot and Earned My First $$$$ (4-Digit) Bounty.
Hope you find it helpful 👇
Link: medium.com/p/how-i-hacked-a-…
#bugbounty #cybersecurity #appsec
No Username. No Password. Just a Header — A $3,000 Authentication Bypass by ALR medium.com/p/no-username-no-…
Credits : @00xalr nice finding brother🥳
Always take a shot. Now they gave me a bounty of $150 and total $250 bounty.
#TogetherWeHitHarder #bugbounty


1
87
3,717
TheHatedOne retweeted

A simple OTP bypass resulted in a €2,000 bounty.
1. Request some OTP codes.
2. Test one of them randomly.
3. If accepted, try to bypass the OTP request limit.
How the exploit works: enter victim's email, request 99999 OTP codes, then submit any random code like 77777 and log in.

TheHatedOne retweeted

$2000 for a web cache deception bug. As always I share my methodology 👇
Identifying a deception bug is always easy but exploiting it can be hard due to SameSite restrictions on victims cookie
I bypassed this to steal victim JWT. Read about it here:
🔗 medium.com/@tinopreter/crack…

TheHatedOne retweeted

Found a cool bug at Meta.
From misconfigured Grafana instance to R/W access on 507 private Meta repositories.
Wrote up the full chain here:
sectricity.com/blog/misconfi…
$157k bounty awarded by @metabugbounty

TheHatedOne retweeted
ًWrite-up is now available
you can read it here
medium.com/@youssefmohamedsa…
Follow Me to Stay updated with more Findings


