
智能合约安全研究员 | Web3 Security Researcher 合约审计 / 漏洞研究 / 风险评估 目前正在寻找全职岗位🤝欢迎联系
Joined October 2022
- Tweets1.1K
- Following253
- Followers1.3K
- Likes912





Pinned Tweet
While bug hunting for the @TruYields project on #Immunefi, I discovered some vulnerabilities that fell outside the defined scope. 🤨
Nevertheless, acting in accordance with my responsibilities as a security researcher👨💻, I sent an email 📧 to report the issue.
I am pleased that they verified the findings and ultimately acknowledged my submission.😌
The project team deserves praise for the importance they place on security. Finally, 🫡I would like to thank them for recognizing my work.


A successful defense against governance risks took place at @AmpleforthOrg ; 🧐 every DAO should pay attention to this type of risk.
中文版本👇:mp.weixin.qq.com/s/dzX25Ox81…

#Etherfi Attack Analysis
"Traditional analysis, handwritten articles" 🥹 don't miss out!
Here’s a quick tip regarding ERC-7702 accounts.
It all started while I was analyzing an attack transaction: app.blocksec.com/phalcon/exp…
I noticed that the ERC-7702 account performed a `delegatecall` to the CoinbaseSmartWallet contract (at address `0x0001`), yet I couldn't find any link between the ERC-7702 account and the CoinbaseSmartWallet on the account's Etherscan page, despite searching thoroughly.
After some analysis, I clarified the underlying logic. When an ERC-7702 account delegates to a logic contract, it utilizes only the contract's code, not its storage; Its storage is located at the address of account 7702. Since Etherscan does not resolve the storage of account 7702, the relevant information cannot be read on the web page. If it is necessary to read it, it can only be done through RPC.

I analyzed the #Balancer attack incident and implemented a #fuzz testing script as a hands-on exercise. While this might not be the optimal approach for detecting the vulnerability, I have documented my thought process throughout the exercise. I learned a great deal from this case study; the implementation may not be perfect, but the experience itself was rewarding.
中文版本:mp.weixin.qq.com/s/J_PHSTepe…

Web3 领域可能正经历一场礼乐崩坏
最近 @Liquid_BTC 项目被攻击了,损失了 4000 个 BTC。但是和一般的黑客攻击不一样,这次的攻击者选择了先获取资金,再保留 15% 作为漏洞赏金的方式。
为什么会出现这种情况?其实侧面是反映了白帽黑客对于项目方的信任缺失。这不是空穴来风,可以从近期各类项目方的种种事迹看出来(包括但不限于😟)
1. 漏洞平台上,项目方的赏金奖励大幅下调。且在漏洞评定上,尽可能的推脱,把漏洞判定在范围外。
2. 漏洞平台提交漏洞,需要支付一笔提交费用。且漏洞重复或其他情况合理情况,这笔费用一概不退回。
3. 赏金标记着用 ETH 支付,但是当 ETH 价格上涨以后,改为用 ETH 价格最低点时等值的 USDC 折算。
4. 直接通过项目方邮箱提交的漏洞,大概率是石沉大海,没有回复。即使被认可了,也有可能只是支付与漏洞风险不对等的少量赏金。
以上种种,结合目前 Web3 领域的下行行情,可以看出,当前在整体下行收益下降的情况下,各大项目方都选择了缩紧安全方面的支出。结合招聘行情来看,许多招聘岗位目前都是面向社区运营和 BD,这些能够维持客户,造成现金流的岗位。
其实也很好理解,当项目的收入下降不及预期时,第一时间的操作往往降本增效。又何尝有余力把资金投入到项目安全的建设中去。此时就进入到了一个两难的局面,重视安全是慢性死亡,忽视安全是讳疾忌医。毕竟项目朝不保夕,甚至不知道资金亏空和黑客攻击哪一个先到来。
我们唯一能做的就是看紧点手中的资金,在进行投资时要做好仓位控制和风险评估,尽量选择在安全方面持续投入的/有赔付实力的项目。毕竟每个人的钱都来自不易,尽量不要让他暴露在风险之中。各位币圈朋友们要远离风险,投好项目,做好人,得好报。(李大霄.jpg)
如果忽视风险,等到真正发生安全事故后,那就晚啦!(溥仪.jpg)


Because #Sherlock's Tare contest had no unacceptable report, the reward was distributed according to ranking.😂 I ranked 212th among the participants and received a huge sum of $0.78.


The @Tare_io Audit Contest is complete!
No valid Medium or High severity issues were identified.
With no valid findings to reward, the fixed $27,000 USDC prize pool was distributed based on SR leaderboard points.
Top 3:
🥇 @iam0x52 — $4,670
🥈 bicktivism — $2,535
🥉 @maigadohcrypto — $1,071
Congrats to the researchers who participated.
Full results below 👇

The root cause of this attack is that the #balancer used a “round half up” rounding method, rather than rounding in a way that is favorable to the protocol.
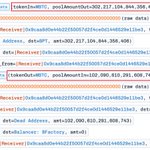
The attacker used flash-loan funds to manipulate the WBTC balance in the pool down to a remaining 7 wei, then repeatedly extracted BPT tokens by exploiting the rounding defect.
[pic.1]
- BPT.joinswapPoolAmountOut(): deposit 1 wei WBTC, receive 0.302217104844356406 BPT
- BPT.exitswapPoolAmountIn(): deposit 0.102090610291608743 BPT, receive 1 wei WBTC
[pic.2-3]
The rounding issue appears in the calcSingleOutGivenPoolIn and calcSingleInGivenPoolOut functions, which compute token amounts using bmul and bdiv.
[pic.4]
For example, in calcSingleInGivenPoolOut:
newTokenBalance = bmul(1.21428571e18, 7) = (8.49999997 + 0.5) rounded = 8.
If rounding favorable to the protocol had been used, 8.49999997 should become 9, and the user would have needed to provide 2 wei WBTC instead of 1 wei WBTC.


We are aware of a bug found in legacy Balancer v1 contracts that allows draining LP funds. These pools are deprecated and non-pausable. Users are encouraged to withdraw proportionally via legacy.balancer.fi. Other Balancer products are not affected.
Are auditors supposed to double as ETH call options now?
One more thing: the project team used an ETH price of $1201 for the payout, which is roughly half of the current price.


在最近经历过找工作这段时间之后,也慢慢觉得有时候很多事情并不取决于你。
很多公司目前就是不招人,你问了,也是不招人。或者说招人,但只招行业精英/明星从业者。
但我只是个普通人,我没办法让老板专门为我破例招聘,也没办法成为大明星。
我能做的,只有在求职失败后,选择是做一个内耗的普通人,还是坦然面对的普通人。

东大人太相信个人努力了,完全忽视了世界的荒诞本质。
觉得人生很容易就毁掉是正确的,因为你试图用个人努力去完美规避世界的随机性惩罚,这必然要求你一步不能错。
同样的,觉得人生很容易翻身也是正确的,因为你个人的缺陷很难阻止幸运的发生。
一个人一辈子努力学习工作健身不抽烟不喝酒,但是一个醉酒的司机可以彻底毁掉他的生活甚至生命,让他所有的努力都失去意义。请问你打算怎么防?
同样一个人吃喝嫖赌无恶不作惫懒迟钝的人,也可以借助某次天赐良机一下翻身备受艳羡。
这时候天道酬勤又在哪里? 和荒诞世界带来的随机性比起来,个人的努力或者放纵都是如此微不足道。
你能做的其实是尽量脱离循规蹈矩的范式,范式在规避风险的时候也会规避掉机遇。
人应该做的是尽可能开放自己的边界,尽可能多的去尝试和体验,允许并欢迎所有可能性的发生。
这不一定能让你获得世俗的成功,但是能试出你个人在这个世界里的上限。
🥹Wouldn't you like to click and take a look at this handwritten article?
中文版本:mp.weixin.qq.com/s/b3WrVFNUy…
