

Be a champion in everything that you do. https://xitter.cf/t.co/yvw5hq7Rtc
Joined October 2021
- Tweets46.5K
- Following519
- Followers129K
- Likes86.8K





Pinned Tweet
Washington defends America from the outside in. Agencies, surveillance, endless spending. It has the threat model backwards. Security starts at home. Strong families. A real economy. Free, healthy citizens. My new book:
11 RULES FOR NATIONAL SECURITY.
Coming soon.

Good morning. ☕️ ☀️ MAC OS and Apple IOS will be releasing operating system updates at 1 pm ET today (27.2). Included is a security patch for a kernel jailbreak exploit. Monitor who sends you text messages, emails, floods your X posts with messages, or calls you today before the update is released to identify bad actors / hackers.
Good news.

The Trump administration moves to treat millions of mentally ill veterans with psychedelics politi.co/4idkGBF


I expect that the other state AG’s will follow suit.

A New Mexico judge ordered Meta to pay $25 billion for deceiving users about its data privacy practices. The judge ruled Meta had committed 43 million violations of New Mexico’s consumer protection laws. Each violation carried a penalty of up to $5,000. trib.al/IfLVLfP

Andrew G. Huff retweeted

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Andrew G. Huff retweeted

Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can:
php.net/index.php#2026-10-20…


🚨 PHP warns of two critical vulnerabilities as emergency patches arrive tomorrow
The PHP security team will release updates on October 21 at 14:00 UTC for two vulnerabilities, each rated 9.2 under CVSS v4.0.
⠀
Security researchers identified the flaws as CVE-2026-109618 and CVE-2026-109619 and described them as remote code execution vulnerabilities reportedly affecting PHP versions 5 through 8.
PHP has not yet confirmed the affected versions, exploitation requirements or fixed releases.
⠀
The vulnerabilities were reportedly leaked before their planned disclosure. Researchers said they have not observed active exploitation, while PHP warned it may release the patches early if technical details become public or exploitation is detected.
⠀
Administrators should identify PHP installations now and prepare to apply the updates as soon as they become available.

Biology is a national security blind spot. We need scientists who can bridge biology and classified intelligence. Count the workforce. Sponsor clearances. Build the pipeline before the next crisis.
My latest article in ClearanceJobs. (news.clearancejobs.com)

Washington demanded honor and discipline in war. I believe he would have despised the cruelty described here. If accurate, this is disgraceful. I served in combat. Killing an enemy gives you no right to torment his widow. No uniform, flag, or cause excuses that dishonor.
This Post is from a suspended account. Learn more
The discourse is steering away from the fact that the proper forensic epidemiological study has not been conducted. Funny, how some people went from “we will never know” to now pointing at a laboratory, US, origin. Stop the nonsense. Conduct the forensic investigation.

1/ NEW: In 2019, NIH lab chief Vincent Munster proposed to his postdoctoal student the idea of inserting a furin cleavage site into SARS-like spikes “to enhance infectivity,” newly obtained records show.
His lab also sought and obtained unpublished SARS-related sequences for the same research project that year.
Along with the rejected DEFUSE proposal, this is the second documented instance of scientists proposing to engineer a furin site into a wild bat coronavirus spike to boost infectivity in the two years before the COVID pandemic emerged.
Story: usrtk.org/covid-19-origins/b…

Andrew G. Huff retweeted

WWII Marine Raider Shares the Brutal Reality of Surviving Iwo Jima
“Fired the first round, crossed my chest, crossed my lungs. It came out on my left side... A big hole on my left side ... took all the muscle out of my left arm.”
“One doctor said, ‘Well, we're going to have to take it off.’ ... That woke me up. ... He started grabbing for the saw. ... About that time, I woke up real good."
-Frank Wright
Andrew G. Huff retweeted
Every federal employee's smart card is about to get a second set of keys. @NIST ‘s working drafts for post-quantum PIV take a dual-stack approach, classical keys kept and ML-DSA and ML-KEM credentials added, which is the right design. What the drafts do not yet contain are the decisions, and the calendar does not wait: a PIV card can be valid for six years, and NIST's own transition plan expects today's public-key algorithms to be disallowed after 2035. A classical-only card issued in 2030 outlives the algorithms that make it work, so the parameters and interfaces need to be final by about 2027.
My twelve comments answer the open questions NIST marked in the drafts: ML-DSA-65 and ML-KEM-768 as the baseline with the category 5 sets permitted; dates in the tables; precedence and key-separation rules for the dual stack; seed storage so twenty retired keys fit on the card; mandatory extended-length APDUs and a defined signing input; card authentication at the door with timing requirements; a post-quantum secure-messaging suite now rather than later, because PIN entry over contactless rides on ECDH today; PKI and validation in the same revision; an identifier registry built for the next transition; and no new freely readable objects that make a cardholder easier to track.
Drafts: pages.nist.gov/piv-standards


Andrew G. Huff retweeted
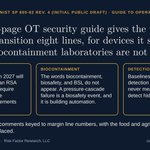
NIST's rewrite of SP 800-82, the operational technology security guide, is a real improvement: restructured around CSF 2.0, new sections for building automation, food and agriculture, rail, maritime, and water, and an architecture chapter that endorses analog backups and out-of-band management. I filed twelve comments, in the letter and in NIST's template.
Two gaps stood out.
1. The post-quantum transition gets eight lines in a 320-page guide, with no date, no algorithm, and no acquisition rule, for devices the draft itself says have life cycles measured in decades. A controller bought against this guide in 2027 will still be verifying firmware with an RSA signature in 2040; the root of trust is the one element a patch cannot migrate, and @NIST already has the signing schemes (LMS and XMSS under SP 800-208, ML-DSA under FIPS 204) that procurements should require now.
2. And biocontainment laboratories are absent entirely: the words biocontainment, biosafety, and BSL do not appear, yet a BSL-3 pressure cascade is building automation whose failure is a biosafety event.
Also in the letter: the food and agriculture section's best sentence (ventilation shutoffs on circuits independent of the monitoring systems) promoted to a design principle, disease-control OT added, the radio layer answered rather than named, detection measured like surveillance (case definitions, denominators, false-positive rates, medians instead of means), consequence-first risk analysis, and zero trust kept out of every safety path.
Draft: csrc.nist.gov/pubs/sp/800/82…
#OTsecurity #ICS #criticalinfrastructure #NIST #postquantum #biosecurity #foodsecurity #biodefense


Andrew G. Huff retweeted
My Analysis & Perspective on Ebola: no US cases, and CDC assesses the likelihood of spread here as very low. Uganda’s exported chain closed in July. The DRC curve has been flat since June, not accelerating. Large and unresolved, but not a US emergency. Follow it closely. Don’t panic.
