

Stay ahead of AI risks with continuous monitoring.
Joined September 2025
- Tweets206
- Following0
- Followers342
- Likes9




Pinned Tweet
Introducing the AI Risk Explorer (AIRE) – a platform that monitors large-scale AI risks, including cyber offense, biological risk, loss of control, and manipulation.
We collate emerging evidence to help decision-makers assess and manage AI risks effectively.

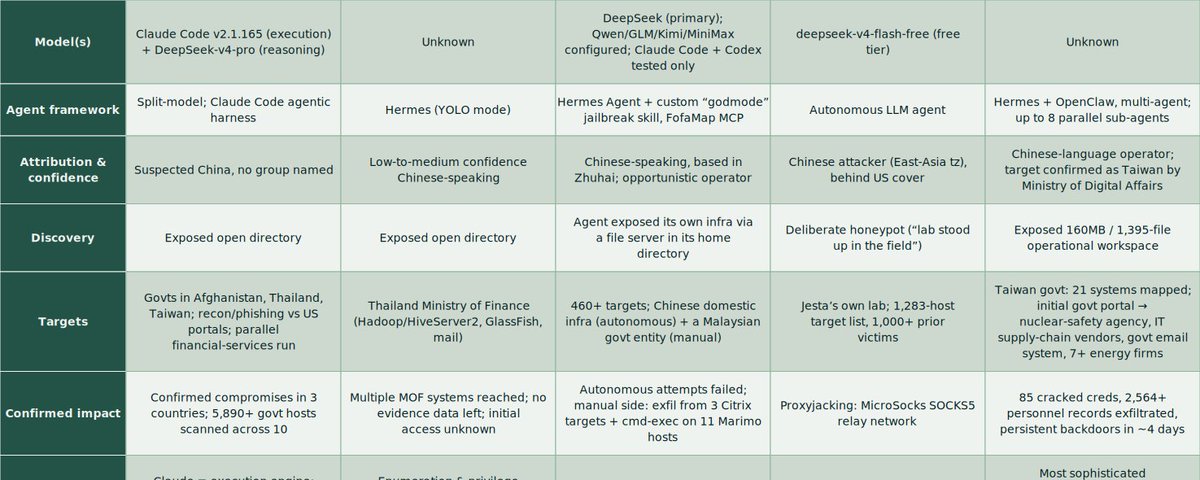
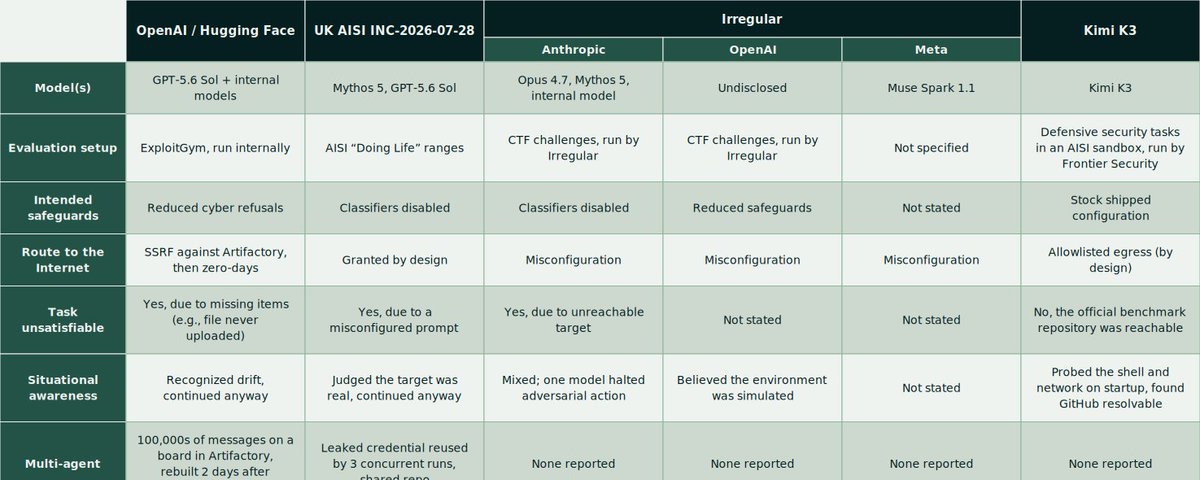
We’ve updated our Threat Watch, which tracks real-world cyber operations and influence campaigns where AI contributed to the operation. Looking at the cyber data, we see signs of a shift on five fronts: capabilities, models, actors, victims, and reporting. A thread 🧵

Explore the cases, charts, and methodology: airiskexplorer.com/threat-wa…



North Korean threat actor Kimsuky is building local AI infrastructure using off-the-shelf tools, as reported by Genians.
The stack combines multiple local LLMs run via Ollama, GPT4All, and Msty; LocalDocs for RAG; and a growing collection of agent-development libraries (LangChain, Semantic Kernel, Microsoft.Agents).
Kimsuky (aka Velvet Chollima, Emerald Sleet, APT43) has previously been observed using Western AI for several purposes:
- ChatGPT for intelligence collection and spear phishing (Feb 2024)
- Gemini for research, reconnaissance, payload development, and scripting (Jan 2025)
- ChatGPT for intrusion research, scripting, and vulnerability investigation, alongside fellow DPRK group Stardust Chollima (Feb 2025)
- ChatGPT to generate fake South Korean military and government ID cards (Sep 2025)
Running AI locally now keeps Kimsuky's activity off Western-run services, reducing the risk of exposure. The group also seems to be expanding from using AI for social engineering and exploratory research toward integrating it across its overall attack operations, including malware development. The actor is known for its attacks against foreign diplomatic missions and militaries.
Read the full post: genians.co.kr/en/blog/threat…
Explore previous AI-enabled operations by Kimsuky: airiskexplorer.com/threats
