

Blockchain Intelligence at your fingertips. Crypto Tracing / AML Screening / Incident Response
Joined October 2020
- Tweets2.2K
- Following624
- Followers8.2K
- Likes4.4K



3/ The report breaks this down by target, network and attack type. Download the full report:
blog.amlbot.com/crypto-crime…

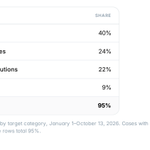
2/ But it’s not only exchanges that get hacked. Individual users were the target in 40% of hacks and exploits.

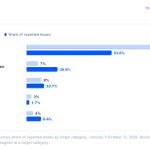
1/ According to AMLBot’s 2026 report, exchanges were just 7% of cases from January to mid-October, but carried almost a fifth of reported losses.

Update: @tether has frozen ~$2.2M linked to the @CoinDCX exploit
Both parked addresses from our last post moved one hop before the freeze: TQPyFb2HodpR9WYRidAye1V2NzJXKNHS1V ($720K) → TETvPCoHdB6KorVS3PL1jxf4hh78B7KZKG ($401K) + TGj6jwiBxgdrBByGJSaDs9SFT2BJVCrpqs ($319K) TMHURkhvUHSNdLmGeD2akjZC2YExGDQYD5 ($665K) → TErumSEPUCZif1kdh3Ja2wNiyynNwM6n8a ($665K)
All three are now frozen. ~$800K more is frozen across 5 other addresses


Wallets on TRON linked to @CoinDCX were drained of ~$16M USDT on Oct 21. ~40 deposit addresses, one of them holding $15.8M, were swept to
TAg6SZ1HhgVVjUaKY1paQoFBUS2JFrg5bT
Tracing shows the funds were deposited to @okx (~$5.5M), @binance (~$2.8M) and @Gate (~$1.4M). A large share went through unidentified services
~$2.4M is still parked across fresh addresses, including TQPyFb2HodpR9WYRidAye1V2NzJXKNHS1V (720K) and TMHURkhvUHSNdLmGeD2akjZC2YExGDQYD5 (664K). None are frozen by @tether yet
We are actively monitoring this case

We tracked this case as well. About $2.8M of the swept USDT was deposited to Binance. xitter.cf/AMLBotHQ/status/211328…
Wallets on TRON linked to @CoinDCX were drained of ~$16M USDT on Oct 21. ~40 deposit addresses, one of them holding $15.8M, were swept to
TAg6SZ1HhgVVjUaKY1paQoFBUS2JFrg5bT
Tracing shows the funds were deposited to @okx (~$5.5M), @binance (~$2.8M) and @Gate (~$1.4M). A large share went through unidentified services
~$2.4M is still parked across fresh addresses, including TQPyFb2HodpR9WYRidAye1V2NzJXKNHS1V (720K) and TMHURkhvUHSNdLmGeD2akjZC2YExGDQYD5 (664K). None are frozen by @tether yet
We are actively monitoring this case
We are sorry for your loss. We looked into the case too. ~$2.4M is still parked across fresh addresses. xitter.cf/AMLBotHQ/status/211328…
Wallets on TRON linked to @CoinDCX were drained of ~$16M USDT on Oct 21. ~40 deposit addresses, one of them holding $15.8M, were swept to
TAg6SZ1HhgVVjUaKY1paQoFBUS2JFrg5bT
Tracing shows the funds were deposited to @okx (~$5.5M), @binance (~$2.8M) and @Gate (~$1.4M). A large share went through unidentified services
~$2.4M is still parked across fresh addresses, including TQPyFb2HodpR9WYRidAye1V2NzJXKNHS1V (720K) and TMHURkhvUHSNdLmGeD2akjZC2YExGDQYD5 (664K). None are frozen by @tether yet
We are actively monitoring this case
We tracked this case as well. About $5.5M of the stolen USDT was deposited to OKX. xitter.cf/AMLBotHQ/status/211328…
Wallets on TRON linked to @CoinDCX were drained of ~$16M USDT on Oct 21. ~40 deposit addresses, one of them holding $15.8M, were swept to
TAg6SZ1HhgVVjUaKY1paQoFBUS2JFrg5bT
Tracing shows the funds were deposited to @okx (~$5.5M), @binance (~$2.8M) and @Gate (~$1.4M). A large share went through unidentified services
~$2.4M is still parked across fresh addresses, including TQPyFb2HodpR9WYRidAye1V2NzJXKNHS1V (720K) and TMHURkhvUHSNdLmGeD2akjZC2YExGDQYD5 (664K). None are frozen by @tether yet
We are actively monitoring this case
AMLBot Plan Update ⚡️
We've made our plans better for you: there are now two, with more features, and each one is built around what you need.
🔹 Personal (formerly Lite) is for checking wallets yourself. Same risk assessment as Business, plus a detailed breakdown of each address you check.
🔹 Business (formerly PRO+) is for VASPs and crypto companies. Our most powerful plan, now with Travel Rule.
See what's in each plan: blog.amlbot.com/amlbot-plans…


Both FXMR and XMR1 on Hyperliquid are heavily used by money launderers. We have covered this before as well
xitter.cf/AMLBotHQ/status/210241…
Seems like the @Fetch_ai / @ASI_Alliance exploiter has started laundering the stolen funds
100 ETH was swapped to ~266K USDC, bridged via Circle CCTP to Arbitrum and deposited into Hyperliquid, then converted into "FXMR" which is likely a Monero variant
The other 100 ETH was sent to @Chainflip, where the broker rejected the deposit. The attacker was refunded and pivoted to @THORChain, swapped into ~3.28 BTC and began peeling it through a chain of Bitcoin addresses
The remaining ~433 ETH are still parked at the main address 0x2dcc1085fDCf418B421E45e86e4e54637cc21dfE

3/ It’s a victim-side view of crypto crime, built from investigations as well as public cases.
Download the full report:
blog.amlbot.com/crypto-crime…
2/ The findings show two sides of the threat: scams, phishing and wallet compromise made up 72% of cases from January to September. In Q3, hacks were 19% of cases but accounted for 40% of reported losses.

1/ Many crypto crime reports focus on publicly known incidents. AMLBot's 2026 report draws on 250+ investigations, including cases reported directly by victims to its team.
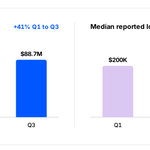
Private data that's not shown in public cases reveals that claimed losses rose 41% from Q1 to Q3, while the median claim fell 49%.

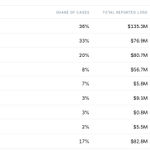
Ethereum (36%) and TRON (33%), the two main networks for USDT transfers, dominate case counts. Ethereum cases carried the largest total: $135.3M.
Bitcoin cases are fewer but bigger: involved in 20% of cases, with the highest median loss of the four most-involved networks, $364K.

Reported losses climbed every quarter: $62.9M in Q1, $75.9M in Q2 and $88.7M in Q3, up 41% in two quarters.
The typical case moved the other way. The median loss rose from $200K in Q1 to $223K in Q2, then fell 49% to $113K in Q3.
The pattern points to a handful of very large cases, not bigger everyday losses.

Europe remains the center of gravity: 40% of cases from January to September and 35% of reported losses.
Losses tell a different story. Asia was 10% of cases but 30% of losses, and the Middle East 9% of cases but 20% of losses. Four cases above $15M each were recorded in the Middle East, Asia and Europe.
These shares show where incidents were recorded, not where offenders operate.

Individual users were the target in 77% of cases and carried 51.6% of reported losses.
Exchanges were only 7% of cases but nearly a fifth of reported losses (18.8%). For them, the threat is hacks: 81% of exchange cases were hacks and exploits.
Hacks are not only an institutional problem, though. Individual users were the target in 40% of them.
