

Research | Threat Intelligence
Joined October 2024
- Tweets451
- Following283
- Followers4.6K
- Likes188



𝒜𝓁𝓅𝒽4 🍁 retweeted

‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws.
New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance.
Full details → thehackernews.com/2026/10/ur…

𝒜𝓁𝓅𝒽4 🍁 retweeted

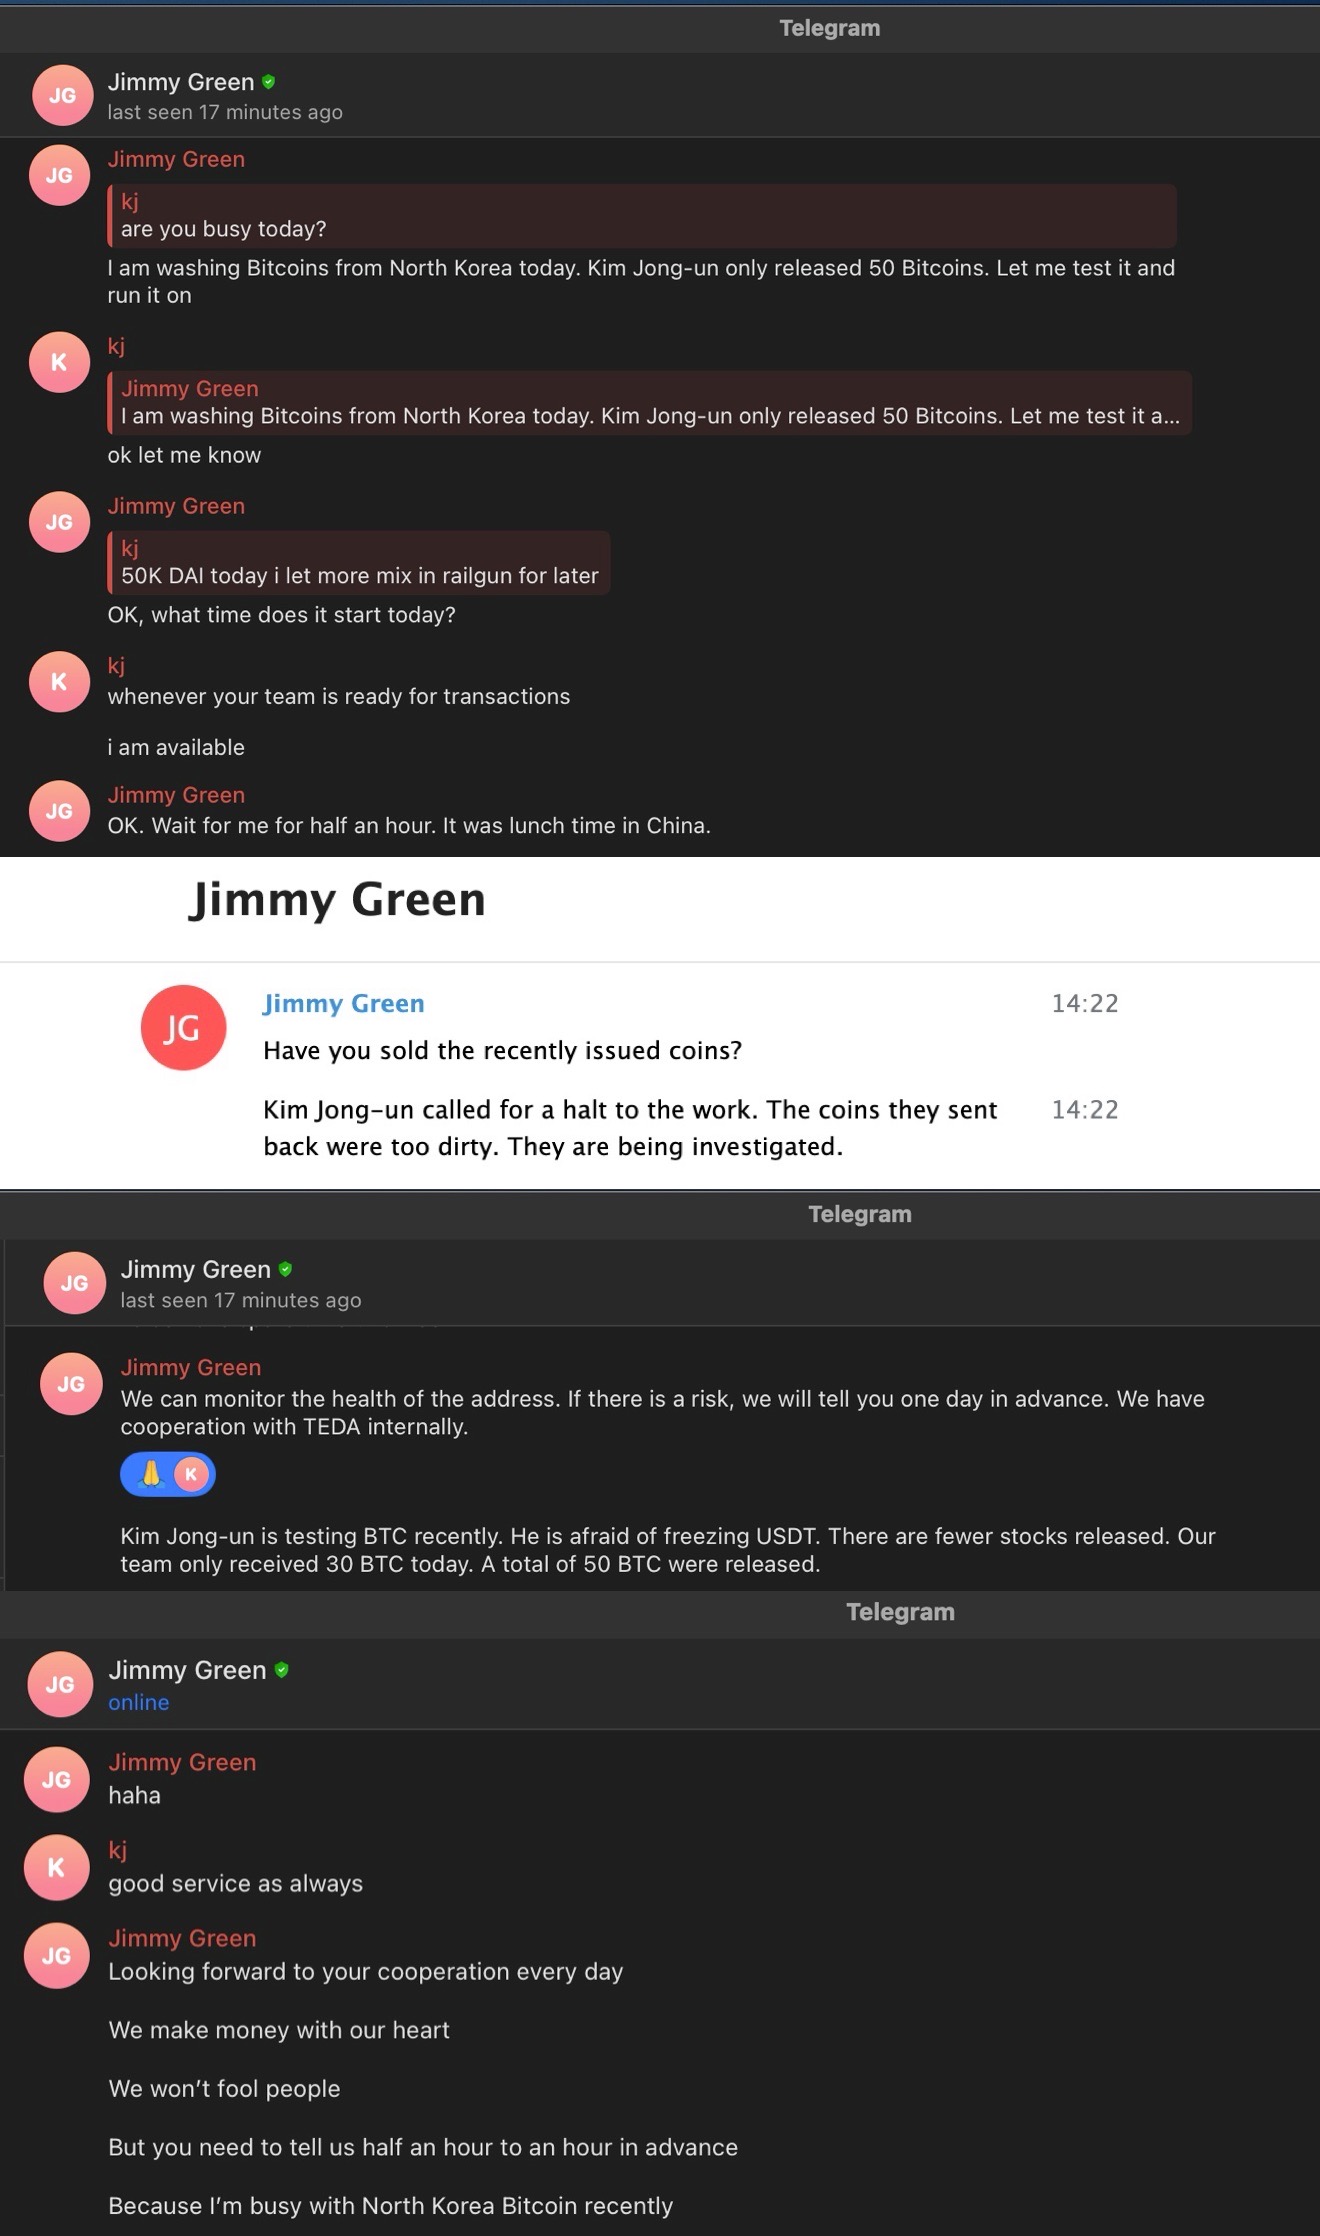
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

𝒜𝓁𝓅𝒽4 🍁 retweeted

🚨 Threat Actor vs. Threat Actor
This is not something we see every day.
ShinyHunters has compromised and defaced the Cl0p ransomware group's leak site.
Behind Cl0p's CAPTCHA, the leak site has been replaced with a ShinyHunters-branded page, displaying its Umbreon imagery and effectively taking over Cl0p's public-facing leak infrastructure.
A rare case of one major cybercrime operation turning its capabilities against another.
DarkFeed is actively monitoring the situation for further developments.
#DarkFeed #ShinyHunters #Cl0p #Ransomware #CyberSecurity #ThreatIntelligence

𝒜𝓁𝓅𝒽4 🍁 retweeted

🚨 LAPSUS$ claims it is permanently ending operations after meeting its financial objectives, stating there will be no further communications, leaks, or access offerings.
The group also taunted investigators and TeamPCP, while alleging that Mercor user data, including personal information, biometric records, and recordings, was sold to Chinese entities.
These claims remain unverified.
Source: lapsus[.]bz

𝒜𝓁𝓅𝒽4 🍁 retweeted
🚨 Notion user database allegedly up for sale
A threat actor claims to be selling a database containing 110M+ unique Notion user records.
Alleged exposed fields include:
• Emails
• Names
• Password hashes
• Signup / login data
• IP addresses
• Locale, timezone, and country
• Workspace metadata
Claim is unverified. Organizations using Notion should review account security, enforce MFA, and monitor for suspicious login activity.


𝒜𝓁𝓅𝒽4 🍁 retweeted

‼️🚨 BREAKING: 320,000 Fortinet firewall devices have been targeted in a campaign that has been dubbed 'FortiBleed'. Attackers were able to confirm 75,000 working credentials against the admin and SSL VPN interfaces.
The victims include really big names like Samsung, Oracle, Spotify, Sony, and more.
The data was first surfaced by researcher Volodymyr "Bob" Diachenko and analyzed by Hudson Rock and SOCRadar. The operation runs as a self-feeding loop. Attackers scan the internet for exposed Fortinet devices, then test each one against a curated list of passwords leaked from earlier Fortinet breaches and infostealer logs. Every successful login gets recorded into a verified database. They then turn each compromised box into a listening post, sniffing the traffic passing through the firewall to harvest fresh credentials, which go straight back into the scanner.
The scale is large. The group ran an estimated 1.16 billion credential attempts against more than 320,000 FortiGate targets, plus 2.1 billion brute-force tries against 160,000 MSSQL servers. In the deeper intrusions they intercept SSL VPN authentication hashes, crack them on a dedicated 45-GPU cluster, and move into internal Active Directory.
Diachenko confirmed full network compromises in Japan, Taiwan, Vietnam, Iraq, and Turkey, including a Turkish NATO defense contractor that had classified defense documents stolen.
If you run Fortinet, act now: rotate every VPN and admin credential, enforce MFA on all external gateways, restrict management access to approved sources, segment internal networks, and audit gateway logs for unusual logins. Hudson Rock has a free domain lookup at hudsonrock.com/fortinet.
Data surfaced via the Hunt Intelligence, Inc. feed.


𝒜𝓁𝓅𝒽4 🍁 retweeted

🚨 CYBER INTELLIGENCE ALERT: POSSIBLE WIDESPREAD COMPROMISE AND EXFILTRATION — PERU 🇵🇪
[STATUS: UNDER INVESTIGATION / VULNERABILITY EXPLOITED (SQLI) / UNCONFIRMED / ACTIVELY MONITORING]
The threat actor identified as NemorisHacking has carried out an intrusion against the infrastructure of the classifieds platform Doplim Peru. Exploiting a critical code injection vulnerability, the attacker indicated that they managed to compromise regional subdomains and inject defacement pages. Furthermore, the actor claims to have exfiltrated a historical database covering the period from 2013 to 2026, consolidating a batch of more than 109,000 emails and user authentication data.
🏢 Affected Entity: Doplim Peru
👤 Threat Actor: NemorisHacking / System Rippers.
⚔️ Attack Vector: Persistent SQL Injection (SQLi) in the application's backend, combined with an authentication bypass in the moderation console that allows access with null or basic logical credentials.
🛡️ TECHNICAL RECOMMENDATIONS AND PREVENTIVE MITIGATION
🛑 Disconnection and Isolation of the Moderation Panel (Immediate Action): The Doplim technical team is urged to temporarily deactivate the .doplim.com.pe subdomain and suspend all external access to the production databases to stop the SQL injection query.
💻 Urgent Web Query Sanitization (SQLi Patching): Mandatory implementation of prepared and parameterized queries in all form inputs and variables of the web application. Prevent the direct concatenation of user-submitted strings into SQL database statements.
📊 MONITORING AND EVALUATION
Intelligence System: analyzer.vecert.io
Quickly assess your website's security with: monitor.vecert.io
#CyberSecurity #Peru #Doplim #NemorisHacking #SQLInjection #Defacement #WebmailBreach #InitialAccess #ThreatIntelligence #CyberAlert #VECERT #Infosec #ConfirmedBreach


𝒜𝓁𝓅𝒽4 🍁 retweeted

ShinyHunters compromised Canvas (to a currently unknown extent) which resulted in a "this system has been compromised" to over 9,000 universities.
As ridiculous as that sounds, I'm not memeing. It has been speculated it is actually over 9,000 universities.
ShinyHunters is having their ALPHV moment. They're now going to get attention at a serious scale outside of the information security circle.

𝒜𝓁𝓅𝒽4 🍁 retweeted

#Phishing 🪝 Geral
Cocos🇦🇷
hxxps://cocoscapital.top/
ID Theft 🇺🇸
hxxps://idreportinfo.online/
JADLOG APK 🇧🇷
hxxps://playstorejadlog.com/
Panini 🌏⚽️
hxxps://mayorista-panini.online/
hxxps://figurinhascopa-panini2026.site/
hxxps://albumdacopa.store/
hxxps://panini-pt.com/


𝒜𝓁𝓅𝒽4 🍁 retweeted

🇵🇪 🎓 Peru Government Data Leak — Education Sector
A threat actor claims to have leaked data from the Regional Education Directorate of Madre de Dios (dredmdd.gob.pe) in Peru.
The dump reportedly contains two databases linked to administrative and educational systems.
Exposed systems may include:
Recruitment and job application records
Administrative document submissions
Payroll and employee-related data (including digital pay stubs)
Institutional and operational records
The platform is used for managing education services, hiring processes, and internal government operations in the region.
⚠️ Status: Unverified — based on underground forum activity
⚠️ Potential risks include exposure of employee data, applicants’ personal information, and internal government records
#DDW #DataLeak #Peru #CyberSecurity #DarkWeb #DataBreach #Infosec

𝒜𝓁𝓅𝒽4 🍁 retweeted
‼️Access to over 30 Claro Cloud user websites is allegedly being offered on a popular cybercrime forum, with claims that the telecom giant's cloud platform has severe security flaws allowing malicious code uploads and website infections.
▪️ Target: Claro Cloud (sitios web / website hosting platform)
▪️ Sites Affected: 30+
▪️ Access Level: Full website management panel (build, pages, clipboard, design, options, settings, databases)
▪️ Exposed Data: Advisor names, mobile numbers, emails, zone information
▪️ Backend Access: FTP Administrator, Windows Services, email, metrics, website creators, files, and databases
Screenshots demonstrate full access to the Claro Cloud admin panel, including the ability to edit HTML, manage web apps, view client advisor contact data, and access database management tools.
One screenshot shows a defacement with "HACKED BY WORRYSEC" injected into a live site as proof of exploitation.


𝒜𝓁𝓅𝒽4 🍁 retweeted
‼️🇵🇪 Access to the Peru branch of OXXO, the convenience store chain with an annual revenue of $25.3 billion and a network of 28,000 stores, is allegedly being sold on a popular cybercrime forum.
▪️ Price: $20,000
The database tree reveals extensive internal operational data including:
▪️ Sowing and planogram files (February 2026)
▪️ Exhibitor and cold display case layouts
▪️ Checkout mesa configurations
▪️ Supplier exhibitor data
▪️ Fast food operations
▪️ Cold zone mapping and gondola layouts
▪️ Promotions (493/15,000)
▪️ OXXO Peru records (367/559)
▪️ Quality documents
▪️ Human resources files
▪️ Operational guides and commercial data
▪️ Administrative documents
▪️ Regional PLU files for Aeropuerto, Arequipa, and Lima (September 2025)
▪️ Promoxxo Archives and internal process documentation

𝒜𝓁𝓅𝒽4 🍁 retweeted
🚩 Sitio web del gobierno peruano 🇵🇪 ha sido comprometido para distribuir el malware #SalatStealer.
hxxps://sisee.diresaucayali.gob[.]pe/public/file/d/espol/becas.html?n=AABBCC&c=81023330XXX
Hallazgo por @malwrhunterteam.
El sitio malicioso (IA-powered) suplanta a @espol 🇪🇨 y al parecer está dirigido a los estudiantes con el señuelo:
"Consulta de Becas Escolares — PAO I 2026"
La web descarga un archivo .ZIP el cual tiene en su interior un .LNK malicioso que inicia la instalación del malware ⚠️ por último, se abre el sitio real de ESPOL y muestra la lista real de Becarios.
Servidores C2:
- wrat[.]in
- salat[.]cn
- 217.26.28[.]234
[+] bazaar.abuse.ch/browse/tag/E…


𝒜𝓁𝓅𝒽4 🍁 retweeted
‼️🇵🇪 Access to Peru's capital regional government portal is being sold for $200, with root RCE, shell, and network admin panel on a Linux firewall device.

𝒜𝓁𝓅𝒽4 🍁 retweeted
🚨CVE-2025-25257: Pre-Auth SQL Injection to RCE - Fortinet FortiWeb Fabric Connector
PoC: github.com/watchtowrlabs/wat…
Write-up: labs.watchtowr.com/pre-auth-…


𝒜𝓁𝓅𝒽4 🍁 retweeted

Un ciberataque masivo al MTC eliminó irreversiblemente 65,000 documentos claves durante la transición de gobiernos. La investigación señala que fue un ataque interno. @elfoco_pe (1/3)


𝒜𝓁𝓅𝒽4 🍁 retweeted

🚨🇵🇪: El grupo de ransomware ThreeAM publica en su sitio DarkWeb a Industrial Controls, S.A.C.
#Peru #ciberseguridad #ransomware #ciberataque #DarkWeb #ThreeAM

ALT 🚨🇵🇪: El grupo de ransomware ThreeAM publica en su sitio DarkWeb a Industrial Controls, S.A.C. #Peru #ciberseguridad #ransomware #ciberataque #DarkWeb #ThreeAM
