

拆解你以为是运气的东西。 机会通常藏在大家觉得理所当然的地方。 Mass 追踪因果链:资金 → 波动率 → 注意力 👀 @MaxGuruAI 追热点看到的是已经发生的事。跟线索,步步领先 。 📺 https://xitter.cf/t.co/XNBuDs6VgH
Joined March 2021
- Tweets8.5K
- Following1.7K
- Followers31.7K
- Likes2.3K




Pinned Tweet
我们来解释一下, 这场 “意外” 的加密货币牛市, 为什么刚刚开始?
它还会持续: 18 - 30 个月。
期间 bitcoin:native 或许会被拉升至 20 - 30 万美金。
真是难以想象,
加密货币的原住民, 迎来他们翘首以盼的 “超级大牛市”。
一代人的财富,
这也是 2026 年 等加密货币最讽刺的一幕:
这个诞生于 2008 年、原本打着“反银行”旗号长大的行业,如今反而成了美债最大的新买家之一。


📺 PHP严重漏洞! 逆向工程 + 社会工程学:加密资产安全的下一个风险点! 提前做好加密资产隔离!
最近3天内多项目遭黑客攻击:
随着 AI 工具在代码审计、漏洞挖掘和自动化攻击脚本生成上的广泛使用,加密领域的攻击门槛明显降低,漏洞从发现到被利用的窗口期缩短,供应链、第三方组件以及人员层面的薄弱环节被更高效地暴露。
1️⃣ Coinbase , 约 6.9 万名用户的敏感数据,包括姓名、地址、电话、邮箱、部分身份证件影像以及账户余额和交易历史等信息。
2️⃣ Solana 交易自动化平台 Bloom 于 10 月 26 日官方确认安全事件。盗取约 9408 SOL(约 94.7 万美元)
3️⃣ 印度交易平台 CoinDCX 确认约 1599 万美元损失。 因自动扫款服务故障导致存款堆积而被盗。
4️⃣ BNB Chain 预测市场 MYRIAD 于 10 月 26 日发生内部运营钱包被利用事件。
5️⃣ DotSwap V1 约于 10 月 25 日通过旧版服务器端签名路径漏洞盗取约 8.5 BTC;
6️⃣ NGRAVE 硬件钱包厂商近期持续发布安全提醒,此前其配套 App 的第三方推送通知服务被劫持,造成约 256 万美元以上损失;
7️⃣ Keystone 则确认网站被入侵,客户记录及设备验证密钥外泄,计划销毁近 1.9 万台库存设备。
‼️ 如果保持现状不变, 很快就轮到自己被盗, 是迟早的事。
——
AI 让逆向工程的门槛变低,这不等于“所有系统都会立刻被攻破”。
但它确实改变了一个重要前提:过去被认为难以分析的代码、依赖关系和攻击面,正在变得更容易被研究、被自动化梳理。
📺 YouTube : youtube.com/watch?v=0-3U2BhR…
------
刚刚,韩国第二大加密货币交易所Bithumb确认遭受安全漏洞
【个人认为, 几个月内, 币安 OKX Bitget Gate Mexc 其中一家会“被盗” , 技术各家都差不多, 主要安全意识不达标, 似乎不当回事 】
@binance @okx @bitget @Gate @MEXC


South Korea’s Second-Largest Crypto Exchange Bithumb Confirms Security Breach
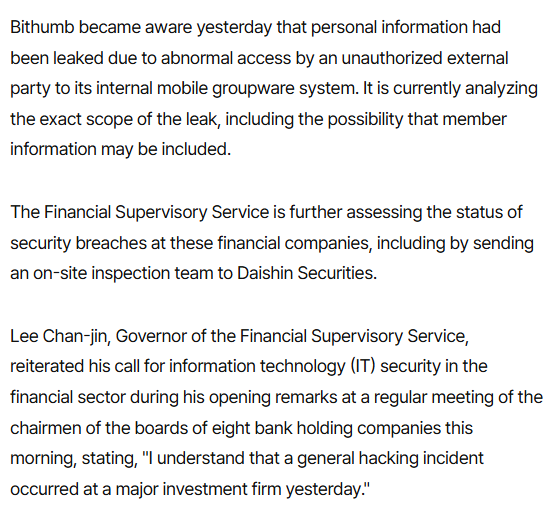
According to Yonhap News Agency, South Korea’s second-largest cryptocurrency exchange, Bithumb, confirmed that an unauthorized external party accessed its internal mobile groupware system, resulting in a personal data leak. The exchange discovered the incident on October 27 and is investigating whether customer information was compromised.
Two other South Korean financial institutions, Mirae Asset Global Investments and Daishin Securities, were also confirmed to have suffered cyber intrusions. Daishin Securities disclosed that the personal and credit information of 38,490 customers had been leaked. South Korea’s Financial Supervisory Service (FSS) is investigating the incidents.


Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.

中国全面暂停转播
西班牙足球联赛及与 基利安·姆巴佩 所有相关的比赛,。
暂停所有比赛转播, 受影响俱乐部包括:
皇家马德里(Real Madrid)
巴塞罗那(FC Barcelona)
马德里竞技(Atlético Madrid)
暂停以上俱乐部,所有足球运动员赛事在中国的转播。

La televisión estatal china CCTV suspende las retransmisiones de la Liga española de fútbol y de los partidos relacionados con el delantero del Real Madrid Kylian Mbappé, tras unas declaraciones del jugador francés sobre un 'meme' que lo compara con Mao Zedong.
efe.com/deportes/2026-10-27/…


内幕再次成功预测并通过多个钱包地址,完成获利。

现在内幕也学精了, 分多个钱包, 就不会太引起关注了。
看看这个家伙, 是不是内幕地址吧。
Address: 0x58f5f813bb7d2a6078070573f4d1b7d319fbc6c9
12 个 “新创建钱包” , 通过各种组合, 总计投入约 27 万美金, 在金球奖获奖名单中。
这些 @Polymarket 账户可能由同一人持有。
整体来看,他在10月26日伦敦颁奖典礼前下注了这个排名:
1、 凯恩
2、姆巴佩
3、亚马尔
4、罗德里
5、梅西
polymarket.com/zh/@lordpengu…


我晕 😵 中国人 为啥能和 土耳其人 吵起来。
翻历史有什么用呢。 历史都是胜利者书写的。
我就知道现在出了 中国 🇨🇳 和美国 🇺🇸 在玩 AI 大模型。
只听说过土耳其烤肉拌饭
要么再往前翻一翻 ?


"Çinlilerin böyle söylemesi elbette her zaman doğru olmayabilir; ama siz de en azından kendi 'tarih kitaplarınızı' ortaya koyup tek tek karşılaştırarak nerelerin yanlış olduğunu çürütmelisiniz, değil mi? Türkler Çin'in tarih kayıtlarını karıştırıp duruyor, ama kendilerinin hiçbir kaydı yok; bu da tam bir rezalet/komedi."


现在内幕也学精了, 分多个钱包, 就不会太引起关注了。
看看这个家伙, 是不是内幕地址吧。
Address: 0x58f5f813bb7d2a6078070573f4d1b7d319fbc6c9
12 个 “新创建钱包” , 通过各种组合, 总计投入约 27 万美金, 在金球奖获奖名单中。
这些 @Polymarket 账户可能由同一人持有。
整体来看,他在10月26日伦敦颁奖典礼前下注了这个排名:
1、 凯恩
2、姆巴佩
3、亚马尔
4、罗德里
5、梅西
polymarket.com/zh/@lordpengu…
换私钥吧。 一些攻防团队, 已经在大面积采集“私钥”了
只要你用户过 Telegram Bot 并明文展示过私钥。
就有概率被采集。
外面传的 IOS ( 假 Telegram )
许多用户 Telegram 已经被套壳了
主要针对 IOS 系统。
‼️ 被攻击了, 也无感知。
不确定, 今天被盗的 Bloom Bot 是不是就是这个原因。
反正就是今天的出的事。
——
截图, 是做攻防的朋友发的, 都已经用上了。
对普通用户可能无所谓, 最多丢点信息和个人聊天记录。
——
但币圈用户, 默认 Telegram Bot 私钥已经泄漏。


这就是为什么 @metricxyz 过去 7 天交易量, 是其他平台的 10 倍 ‼️
就用这个交易就行了 , 以后你会感谢我的:
app.metric.xyz/r/0xcii
1 ETH 交易, 磨损只有 $0.15
你用任何 其他 DEX , 目前应该都做不到。


Tokenized stock DEX volume growth, past 7 days
@metricxyz did +$310.9M, more than 10x anyone else
@MeteoraAG and @Uniswap follow at +$26.7M and +$24.8M.
Via @tokenterminal.

链求君 🔥 retweeted

I wanted to test if a Solana program with no source available could be pulled from the chain and reverse engineered into a byte identical open source version
So I took the daosfun contract and did just that
Found a critical security vulnerability in the mainnet program too, oops!
All smart contracts can be perfectly reverse engineered now
There is no security by obscurity anymore
github.com/lalalune/daosfun-…

‼️ 风险是有的, 毕竟上次 GIWA 假链跑路了。
但是如果 , 这条链确认是官方。 @Kinetiq_xyz
🎉 抢跑, 至少 10 倍起步。
$e/acc $520K
CA: 0xedb963ed6efe231f6327c87a42ed49abe2447afa
boxa.pro/#/asset/0xedb963ed6…
💎 Delphi Digital 推荐必属精品: ⬇️
xitter.cf/Delphi_Digital/status/…
🤔 Elysium 是个什么项目?
🔗 xitter.cf/Kinetiq_xyz/status/209…
Mass 上周线索🕵️
🔗 youtu.be/K10DmME1fpk
———
为什么现在有人在抢桥 Elysium,而不是等官方上线 ?
机会通常不在“官方宣布”的那一刻,而在资金已经开始流动、注意力还没完全跟上的窗口里。
HyperEVM 上先制造热度 → 用 burner 钱包通过启动台内置桥接进 Elysium → 在目前仅有的两个活跃启动台上买早期币。
这是当前可见的因果链。
---
链上实际情况
(⚠️ 非官方泄露信息):
网络:elysium(Kinetiq 在 Hyperliquid 上的 L2)
链 ID:99901
父链:hyperevm(999)
Gas:hype
官方 RPC 受限,目前公共访问基本依赖启动台自己的 RPC
目前能桥的路径只有启动台内置桥:
boxa、elysiumpump
官方桥还没出来,Kinetiq 文档里主网路由器仍写着“即将推出”。
这是单向的。
在主网上线 + 挑战期之前,桥回去的路径基本不存在。
当前能买的地方:
@ElysiumPump:e/acc(口号币,约 $526k)、ak(链上第一个币,约 $84k)
@boxa_elysium:max 和后续新发行
‼️‼️‼️ 这是私有链。
有可能在 11 月 9 日前重置,币直接归零。
启动台和桥接都是匿名团队。
但是,也确实存在“赚 100 倍” 的一个窗口期。
目前,大部分人还没听说过这条链,更不太可能交易。


🌍 名称:cve.now:免费 CVE 漏洞源
📖 简介:cve.now 提供免费的公开 CVE 漏洞情报源,支持 RSS、Atom、JSON Feed 与 MCP 接入,方便 AI Agent、开发者和安全团队自动订阅、监控与获取最新漏洞信息。
🔥 关键词:cve.now、CVE漏洞、漏洞情报、免费漏洞订阅、RSS订阅、Atom Feed、JSON Feed、MCP、安全情报、漏洞监控
📂 分类:情报研究
🏷️ 标签:CVE、漏洞情报、安全订阅、RSS、JSON Feed、MCP、AI Agent
🔗 网址:t.me/yongzhuan_bot?start=sr_…

链求君 🔥 retweeted

Patch or Die!
Today we sent the following out to the CEOs in our portfolio regarding the widespread vulnerabilities that have been detected by AI agents:
The previous week should make it obvious that things have changed. Vulnerabilities are being discovered and exploited at a rate that has never been seen before. While there has been a flood of new vulnerabilities AI agents are being adopted at scale multiplying the potential risk. Agents not only help automate the attacker lifecycle, every ai agent is an insider threat. Your environments are designed to withstand attacks from the outside, not from within. As such, we are suggesting company leaders consider the following changes:
1 - Ensure you're sufficiently staffed for security. The average enterprise allocates roughly 10% of its tech spend to security. Consider doubling that. There are likely thousands of vulnerabilities that need fixing in your environments. Security through obscurity no longer works, all that can be exploited will be exploited.
2 - Establish a zero tolerance policy for secuirty bugs in new features and product releases. Re-examine launch and release schedules and consider delays to ensure all vulnerabilities are patched before deploying new features or products.
3 - Double tap the zombies. Find all old legacy environments that have been neglected and turn them off. Labs, test environments, zombie CI/CD projects etc. Turn it off for now. If it isn’t tied to revenue, kill it.
4 - End the risk acceptance process. Over the last 10 years the risk acceptance process has morphed from a way to accept risks to enable the business, to a way to justify never fixing security issues. Adopt a zero tolerance policy for security issues and risks.