

you'll never know if you never go
Joined July 2025
- Tweets11K
- Following522
- Followers13.5K
- Likes16.9K

Archive retweeted
this is crazy...
the guy reverse-engineered Candy Crush and found the code that decides how close you are to winning on every single move
Candy Crush is one of the most popular mobile games ever. 14 years after launch it still makes nearly $1 billion a year
he's a reverse engineer who decompiles viral apps with AI and publishes the dark patterns he finds inside them
here's what he found step by step:
step 1 → Candy Crush scores how close you are to beating a level.
In the code it's called pass proximity
step 2 → the game downloads a table with hundreds of thousands of rows to your phone.
It says where your pass proximity should be after every move
step 3 → every time you move, it checks if you're where they want you to be
step 4 → falling behind? MakeEasierAction() shifts the candy odds your way.
On your last move it can drop up to 56 extra candies onto the board
step 5 → playing too well? there's a function literally named MakeHarderAction() that tweaks the colour odds against you
step 6 → everyone loses eventually, so you get two ways to keep playing: watch an ad or pay
step 7 → watch an ad: the closer you were to winning, the smaller your reward
step 8 → pay: an ML model reads your pass proximity, your losing streak, whether you're low on lives and your place in the weekly race.
Then it decides what the same 10 gold bars buy you: anywhere from +5 to +190 moves
under the hood:
→ the game's native library is stripped, but C++ still leaves class names behind, so a plain strings dump turns up names like MakeHarderAction
→ the offer logic comes down from their servers as plain JavaScript, with the developers' original comments still in it
→ on Block Blast he went further: jadx for the Java side, Ghidra for the native library, a clean Android emulator and GPT-6 Astra to port their models
→ and found a rule that waits for an expensive ad to load, then deals you a hand you can't place
the same number that keeps you playing is the one they use to sell you the way out
his full write-up with the actual code is in the reply below

this is crazy...
the guy reverse-engineered Candy Crush and found the code that decides how close you are to winning on every single move
Candy Crush is one of the most popular mobile games ever. 14 years after launch it still makes nearly $1 billion a year
he's a reverse engineer who decompiles viral apps with AI and publishes the dark patterns he finds inside them
here's what he found step by step:
step 1 → Candy Crush scores how close you are to beating a level.
In the code it's called pass proximity
step 2 → the game downloads a table with hundreds of thousands of rows to your phone.
It says where your pass proximity should be after every move
step 3 → every time you move, it checks if you're where they want you to be
step 4 → falling behind? MakeEasierAction() shifts the candy odds your way.
On your last move it can drop up to 56 extra candies onto the board
step 5 → playing too well? there's a function literally named MakeHarderAction() that tweaks the colour odds against you
step 6 → everyone loses eventually, so you get two ways to keep playing: watch an ad or pay
step 7 → watch an ad: the closer you were to winning, the smaller your reward
step 8 → pay: an ML model reads your pass proximity, your losing streak, whether you're low on lives and your place in the weekly race.
Then it decides what the same 10 gold bars buy you: anywhere from +5 to +190 moves
under the hood:
→ the game's native library is stripped, but C++ still leaves class names behind, so a plain strings dump turns up names like MakeHarderAction
→ the offer logic comes down from their servers as plain JavaScript, with the developers' original comments still in it
→ on Block Blast he went further: jadx for the Java side, Ghidra for the native library, a clean Android emulator and GPT-6 Astra to port their models
→ and found a rule that waits for an expensive ad to load, then deals you a hand you can't place
the same number that keeps you playing is the one they use to sell you the way out
his full write-up with the actual code is in the reply below
Archive retweeted
Holy crap, who the hell did this?!!
Someone open-sourced a launch-film studio for your coding agent and lets you run it on your own computer.
GitHub's already at 1,665 stars, repo's called huashu-motion.
You just tell Claude Code "make a 30-second launch film for my product", and it reads the product, shows you three directions, builds the film, and writes its own music score. Sampled piano, strings, drums and 23 sound effects on the beat - it's got all that covered too.
And it's not just launch films. Feed it a CSV and it makes a data story, hand it your voice memo and the motion lands on your words, ask for vertical and you get a 1080×1920 cut. An editor where you press C, click the frame and type what to change - they threw that in too.
No After Effects, no motion designer, no stock music
Link's right here: github.com/alchaincyf/huashu…
But hey, Anthropic launched Claude Motion for Team and Enterprise only, and this one made a 22-second film on DeepSeek V4.1 Flash for $0.27
Who needs a damn Enterprise plan!
Archive retweeted
It is becoming dangerous
I gave MiniMax M3.1 Flash one prompt, and a few minutes later I had a playable game
Space Bunny, the anonymous model that ran 200T+ tokens, was an early version of M3.1 Flash. Now the official release is out, and it's stronger. So I had it build a game about a space bunny
The result: a full space game in one 41 KB index.html, no libraries, with its own autopilot
It got there on its own in MiniMax Code: wrote the game, tested it in a headless browser, fixed its own bug and finished at 19/19 tests
The whole session came to about $0.10 at list price: $0.15 in and $0.60 out per 1M tokens
- Claude Haiku 5.5 jumps from $0.10 to $0.50 per 1M input tokens past 100K
- GPT-6 Luna doubles in price past 272K
- Gemini 3.8 Flash starts at $0.75
- M3.1 Flash has flat pricing: $0.15 in and $0.60 out, no matter how long the context gets
The video is the finished game, played by its own autopilot
Launch offer: 50% off your first month of M Plan
Try it in MiniMax Code, links in the reply below
Archive retweeted
THIS IS A PURE F*CKING GOLDMINE
the best Claude Code trick almost nobody runs yet.
The idea: a Stop hook runs your tests every time Claude tries to finish, and sends it back to work until they pass.
Claude can't call a broken build "done" anymore, because the hook checks the work before the turn is allowed to end.
You just register one hook in .claude/settings.json:
"Stop" → .claude/hooks/check-done.sh
here's the split:
→ Claude finishes and tries to end the turn
→ the Stop hook runs your test suite
→ a failure exits with code 2 and the error goes straight back to Claude
→ Claude keeps fixing until the tests are green
The hook only steps in at three moments:
→ the end of every turn
→ every time a test fails
→ after 8 blocks in a row, when Claude Code ends the turn anyway so it can't loop forever
Claude writes. Tests judge. The hook decides.
That's the whole rule: "done" isn't something Claude says, it's something your tests confirm.
the full tree
> .claude/settings.json registers the Stop hook
> check-done-sh runs your test command
> exit 0 lets the turn end
> exit 2 sends the failures back to Claude
> stop_hook_active tells the hook it's already a retry
> /goal does the same for one session with zero config
paste the tree and this prompt into Claude Code ↓
"Add a Stop hook to this project:
1. Create .claude/hooks/check-done.sh that runs [your test command] and prints only the failing tests.
2. When tests fail, exit 2 with the failures on stderr. When they pass, exit 0.
3. If stop_hook_active is true and the same tests still fail, exit 0 and tell me instead of looping.
4. Register it under "Stop" in .claude/settings.json, then show me /hooks.
Show me every change as a diff first. Nothing changes until I say go."
↳ code.claude.com/docs/en/hook…
save it, it'll come in handy.
Archive retweeted
It is becoming f*cking dangerous: the NSA's own reverse-engineering tool now plugs straight into Claude Code - Ghidra has 94k stars, and GhidraMCP lets your agent read a compiled program instead of guessing what it does
Install Ghidra 12.1.4 from ghidra-sre,org (free, released by the NSA)
Download the GhidraMCP release and add it in File -> Install Extensions
Restart Ghidra and switch on GhidraMCPPlugin in File -> Configure -> Developer
Connect it: claude mcp add ghidra -- uvx --from git+github.com/LaurieWired/Ghidr… ghidra-mcp
Open a binary you're allowed to analyze and let Ghidra run its analysis
Ask Claude what a function does: it decompiles it, renames the variables and explains it in plain English
Ask for the map: every function, import, string and cross-reference, and where the interesting code lives
The decompiling runs in Ghidra on your machine, Claude just drives it
Malware samples, old firmware, your own builds: your agent reads the program itself, not the docs about it
Find the repo in the reply below
STOP WASTING HOURS TRYING TO FIGURE OUT HOW TO LEARN REVERSE ENGINEERING
I put together one practical roadmap with videos, GitHub repos, guides, books, research papers, and hands-on practice
VIDEOS:
Self-Learning Reverse Engineering - youtube.com/watch?v=gPsYkV7-…
Every Level of Reverse Engineering Explained - youtube.com/watch?v=8vk5z9VA…
Ghidra Quickstart, Solving a Crackme - youtube.com/watch?v=fTGTnrgj…
Reversing WannaCry, Finding the Killswitch - youtube.com/watch?v=Sv8yu12y…
Firmware Analysis & IoT Reverse Engineering - youtube.com/watch?v=zs86OYea…
ghidraMCP, AI Can Reverse Malware - youtube.com/watch?v=u2vQapLA…
AI Reverse Engineering with MCP for IDA and Ghidra - youtube.com/watch?v=iFxNuk3k…
Automating Hardware Hacking with Claude Code - youtube.com/watch?v=Z5uBrFNi…
GITHUB REPOS:
Ghidra (NSA) - github.com/NationalSecurityA…
REA, Reverse Engineer Anything - github.com/morluto/rea
GhidraMCP - github.com/LaurieWired/Ghidr…
IDA Pro MCP - github.com/mrexodia/ida-pro-…
Free Reverse Engineering Tutorial - github.com/mytechnotalent/Re…
x64dbg - github.com/x64dbg/x64dbg
Frida - github.com/frida/frida
JADX, Android Decompiler - github.com/skylot/jadx
ImHex - github.com/WerWolv/ImHex
radare2 - github.com/radareorg/radare2
capa by Mandiant FLARE - github.com/mandiant/capa
Awesome Reverse Engineering - github.com/wtsxDev/reverse-e…
GUIDES:
Android App Reverse Engineering 101 - ragingrock.com/AndroidAppRE/
RE101 Workshop by Malware Unicorn - malwareunicorn.org/workshops…
OWASP Mobile App Security Testing Guide - mas.owasp.org/MASTG/
Ghidra Cheat Sheet - ghidra-sre.org/CheatSheet.ht…
Nightmare, Binary Exploitation Through CTFs - guyinatuxedo.github.io/
BOOKS:
Reverse Engineering for Beginners (free) - beginners.re/
Practical Malware Analysis - nostarch.com/malware
Practical Binary Analysis - nostarch.com/binaryanalysis
The Hardware Hacking Handbook - nostarch.com/hardwarehacking
Hacking: The Art of Exploitation - nostarch.com/hacking2.htm
RESEARCH PAPERS:
SoK: The Art of War, Offensive Techniques in Binary Analysis - sites.cs.ucsb.edu/~vigna/pub…
No More Gotos (NDSS 2015) - ndss-symposium.org/ndss2015/…
LLM4Decompile - arxiv.org/abs/2403.05286
LLMs for Code Analysis: Do They Really Do Their Job? - arxiv.org/abs/2310.12357
PRACTICE:
pwncollege - pwn.college/
OpenSecurityTraining2 - ost2.fyi/
crackmesone - crackmes.one/
Microcorruption - microcorruption.com/
picoCTF - picoctf.org/
Flare-On Challenge - flare-on.com/
Repost so someone else can find this roadmap, and follow @ArchiveExplorer for more on reverse engineering with AI

Archive retweeted
Claude Code can now reverse-engineer your robot vacuum...
1 prompt + 10 min = every server it talks to, what each one gets, and a switch to cut off the ones you never agreed to
here's full guide step by step:
step 1 → paste the prompt below into Claude Code with a photo of the label under your vacuum
step 2 → connect REA once: npx rea-agents setup - it takes apart the vacuum's phone app and lists every server it calls
step 3 → Claude gives you one command to save your router password to your keychain - the password never touches the chat
step 4 → run one cleaning cycle. Claude matches what the vacuum actually called against the list from the app
step 5 → you get three piles: needed to clean, needed for the app, not needed at all. The floor map, room names and your Wi-Fi list show up in whichever pile they really go to
step 6 → for every server in the last pile, one rule to block it and one to undo it. You say yes, Claude applies it
the result: you finally know what a device that drives around your bedroom tells the internet, and it keeps cleaning just the same
p.s: works with most Wi-Fi vacuums. If yours uses a different app, tell Claude Code and it'll find another way in
Try it tonight, before the next cleaning run. Then read the post below on how REA takes any app apart:
"Find out what my robot vacuum sends home:
1. From the photo, identify the model and its phone app. Use REA to take the app apart and list every server it talks to and what each request carries.
2. Give me one command to save my router password to the keychain. Never ask for it in chat.
3. Watch the vacuum on my router during one cleaning run and match what it calls against the list from step 1.
4. Sort everything into: needed to clean / needed for the app / not needed. For every 'not needed' server, give me one rule to block it and one to undo it.
Change nothing until I say yes."
Archive retweeted
this is f*cking insane, a Grok bot ordered itself a body and the parts are showing up at its owner's apartment
Evan Bacon (frontend lead for Grok at SpaceXSI) gave his bot $1,000 and one assignment: build yourself a body
it modeled the parts in CAD, ran a sim, ordered the electronics on Amazon and the 3D prints on Craftcloud, and had all of it mailed to his place
he says he wasn't involved in the CAD. he also owned zero tools, so calipers, hex keys and a multimeter showed up too
here's where the money went:
→ Amazon: servos, an ESP32 board, a servo driver, wiring and tools – $126.96, two shipments
→ Craftcloud: the printed body parts from 3D Pros – $90.19
→ total: $217.15 of the $1,000
a robot can look perfect in a sim and still fall over on the floor
the bot flagged it itself before the build: "the built robot will weigh about twice what the sim assumed, so the first hop test may show you need stronger servos"
every purchase came back with:
> a one-time card he approved
> the order number
> the total with tax
> a check that the order went through before it touched it again
two orders, $782.85 still in the budget, and the next step is the first hop test
tag your bot and ask:
"Build yourself a small robot body on a $___ budget
1. Model the parts in CAD and run a sim before you buy anything. Flag what the sim can't confirm
2. Split the order: electronics and tools from one store, 3D prints from a print service. Show me every line item
3. Pay only with a one-time card I approve, and check the order went through before you retry
4. Tell me what will break first when we build it"
start with one leg and one servo before you order the whole body
he's posting everything he learns on X, so your bot can keep an eye out for updates
Archive retweeted
this is pure gold for anyone running coding agents
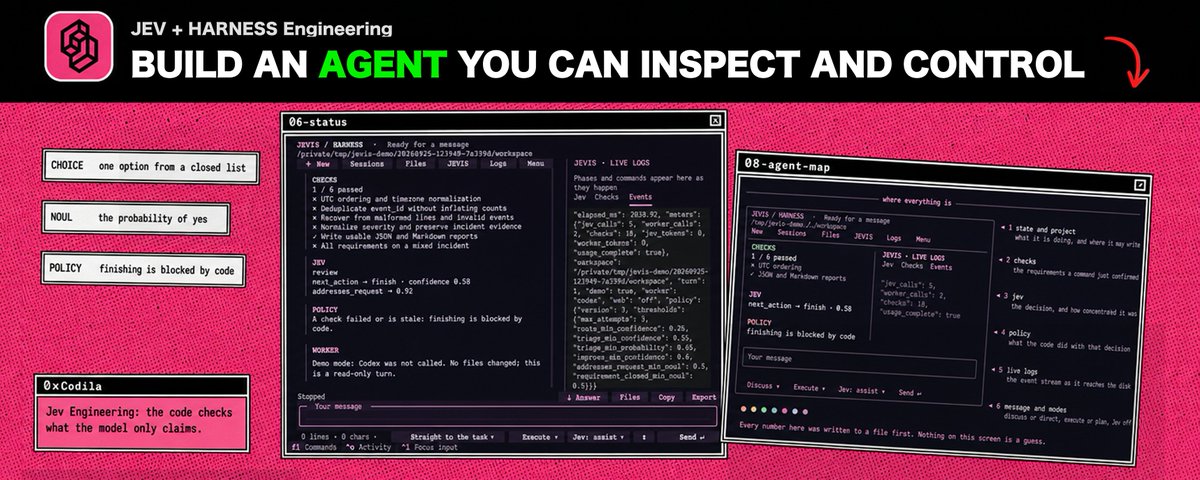
TypeSafe, the team behind Jev, published their guide to building with it
the promise:
> most calls come back in about 100 ms
> their target is over 100× the intelligence per unit of speed and cost
the model hasn't been the slow part for a while
the speed and the cost sit in how much of the work you hand to a model at all
the rules from the guide:
> keep control flow, rules and side effects in code
> break broad judgments into narrow, typed questions
> give each question only the context it needs
> act, review or escalate on the confidence number
how to use it:
> install their skill in Claude Code:
claude plugin marketplace add typesafe-ai/skills
claude plugin install typesafe@typesafe-ai
> drop the guide below into Claude Code and let it rebuild your agent's small decisions around Jev
one catch they spell out: Jev doesn't replace the model behind Claude Code. It makes the small decisions inside what you build
one evening of setup
and your agent starts next week on a harness most teams still don't have
Archive retweeted
REA + Jev + Haiku 5.5 is f*cking dangerous...
REA (Reverse Engineer Anything) gives your AI agent tools to inspect closed-source apps, down to the binary.
Haiku runs the investigation. Jev routes the workflow and checks whether the evidence supports the conclusions.
Paste this prompt into Claude Code and trace how an app’s features actually work.
Then save the article below for the full reverse-engineering setup 👇
Archive retweeted
Jev engineering inside Grok Bot is lowkey insane:
Grok stops deciding whether to retry, and a model that only returns decisions makes the small calls
one router sits in front of every expensive move, and it can only answer with an action:
- reuse_cache hands Grok a fresh artifact instead of redoing the work
- stop_retry ends an approach that keeps failing the same way
- research_capped stops research at 5 pages, then makes Grok write it up
- ask_human holds anything that sends, publishes, pays or deletes until you say yes
→ the same approach kept failing: repeat attempts went from 3 to 0
→ a fresh artifact already existed: browser opens went from 1 to 0
→ 24 candidates to check: Jev ranked them, 53.8 s became 4.1 s and 14 pages became 5, for about $0.0004 of Jev
a cheap judge can be wrong too, so it starts in shadow mode and only logs what it would have done
Grok thinks. Jev decides. You approve.
every call to Jev carries only:
> the goal
> the kind of task
> the last error and how many times it repeated
paste this into Grok Bot:
"Build me a Jev router skill. Before any browser, research, retry or subagent, send Jev the goal, the task type and the last error, then follow its action: reuse_cache, stop_retry, research_capped at 5 sources, or ask_human before anything that sends, publishes, pays or deletes. Run it in shadow mode for a week and log every decision. I'll add TYPESAFE_API_KEY myself. Show me the plan first. Do not switch to active until I confirm"
start with the one routine that keeps retrying, not your whole setup
full setup below