

Full time Bug Bounty Hunter on Google
Android
Joined May 2018
- Tweets39
- Following257
- Followers184
- Likes1.9K

Atom retweeted

While we wait for the #PHP2Shell patches, we pulled some numbers from Profundis.
PHP shows up in 347,425 of 6.08M HTTP(S) records over 24h (5.7%). That isn't a count of vulnerable servers.
CVE-2026-109618 / CVE-2026-109619
Fixes: 14:00 UTC.
🤖 Made with AI

Atom retweeted

🚨 BREAKING: A Broadcom Wi-Fi bug lets anyone in range run code on routers without the password.
Quentin Kaiser showed it on Proximus, Orange Belgium and VOO routers and estimates ~1.5M in Belgium are exposed, none patched.
The bug dates to 2010. Broadcom won't assign a CVE.


I found Two Critical vulnerabilities on Google
Always feels good to receive emails from them
#bugbounty #cybersecurity #infosec #hacking

8
196
6,689
Atom retweeted
We investigated a spam campaign running on throwaway domains, and found the company behind it with our new Pivot tool.
Its WHOIS was privacy-protected, but the company name was left in the organization field, on 208 domains.
blog.profundis.io/blog/from-…


Atom retweeted
Our AI-powered Favicon Matcher just got a major upgrade!
Search is now ~90× faster (near-instant results) and it considers more candidates, so matches are sharper than ever 😎
Find visually similar favicons across billions of indexed sites 👇
profundis.io/tools/favicon-m…
#Bugbounty #recon #osint #ai
1/2
9 minutes, 400€
One of the simplest bugs I ever found
I almost skipped this target
This time I did the opposite of what I usually do
I hunted where nobody looks
I jumped into @profundisio (my favorite asset discovery engine) and used its Pivot tool

Atom retweeted

I earned $10,000 for my submission on @bugcrowd bugcrowd.com/h/elsicarius #ItTakesACrowd #BugBounty
Bug: Weak JWT sign key + mass assignment in the JWT -> read arbitrary customer sensitive/PII data
Fully found by Claude using @profundisio MCP

Atom retweeted
Still using a single hash to reverse search your target favicons?
We did some intensive research on a recon technique nobody thought about: visual similarity search across 50M+ favicons.
Full write-up 👇
blog.profundis.io/blog/favic…
#osint #cybersecurity #recon

Super événement ! Ravi d’avoir pu partager mes connaissances lors d'un talk.
Des échanges enrichissants, hâte de revoir les autres interventions en rediffusion.
Merci à l’ESN'HACK pour l’organisation !

🎥 Les rediffusions du dernier Ambrosia sont enfin dispo !
Retrouvez les talks de @Creased_, @GnousRick, @Atom_User_, @_Worty, @kevin_mizu, Onirix et Iziram sur notre PeerTube : peertube.esnhack.fr 🎬

Atom retweeted

Hello ! 🧙🏼♂️
On se retrouve demain (Mardi 22) à 21h as usual ! ⏰
Topic 1 : Optimize your BSCP 🤔 FT. @Atom_User_
Topic 2 : Lalubuntu Ground Work & 24.04 migration 🤯
rdv @ twitch.tv/thelaluka

(1/2)
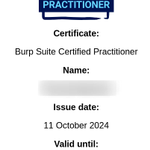
Mission accomplie !
Après plusieurs mois de travail intense, je suis officiellement Burp Suite Certified Practitioner (BSCP) !
📢 J'ai rédigé un article sur mon blog afin de vous partager les stratégies qui m'ont permis d'obtenir la BSCP
Merci à @PortSwigger
⬇️

(2/2)
📢 Retex pour la communauté :
at0m.space
Vous voulez en savoir plus ?
Rejoignez-moi en live le 21 octobre 21h avec @TheLaluka !
On parlera méthodo, hacking et conseils pour réussir la BSCP.
👉 teapawt.net/TheLaluka/status/18482…
#blog #BSCP #cybersecurite


Hello ! 🧙🏼♂️
On se retrouve demain (Mardi 22) à 21h as usual ! ⏰
Topic 1 : Optimize your BSCP 🤔 FT. @Atom_User_
Topic 2 : Lalubuntu Ground Work & 24.04 migration 🤯
rdv @ twitch.tv/thelaluka
1
5
561

