

BLOKWORX defends managed service providers and their clients from cybercrime and financial loss. We defend. We protect. You grow.
Reno, NV
Joined January 2012
- Tweets3.9K
- Following24
- Followers146
- Likes49




It’s RED Friday. 🇺🇸❤️
R.E.D. stands for Remember Everyone Deployed, and today we wear red for the service members who can’t be home with the people they love. To those standing watch around the world, and to the families holding it down back home: we see you, we’re proud of you, and we won’t forget you.
Wear your red today and share this to remind someone why it matters.
#REDFriday #RememberEveryoneDeployed #MilitaryFamily #BLOKWORX #MSP #MSSP

25
Remember Log4Shell? There is a new one, and they are calling it Java4Shell.
It is a critical flaw in Java itself (CVE-2026-114938, CVSS 9.2). An attacker can send malformed data and run code on the server, no login required. Researchers have already proven it works against default installs of Confluence, Jira, Jenkins, and Kafka.
The reach is the problem. The bug lives in a core Java function that thousands of applications use, so the exposure goes far beyond those four names.
Oracle released the fix in its November update. If you or your clients run anything built on Java, patch this one today, not at the next maintenance window.
#MSP #Cybersecurity #Java4Shell

1
1
108
Quick question for the MSP owners out there.
If you could cut one tool from your stack tomorrow with zero consequences, which one goes first?
Not the one with the worst renewal price. The one nobody on your team would miss.
Every environment we step into has at least one. The agents pile up, the conflicts multiply, and somehow nothing gets more secure.
Drop it in the comments. No vendor shaming required. Category is fine.
#MSP #ToolSprawl

7
Zoom, CNN, IKEA, HSBC. None of their websites needed to be hacked. All of them delivered malicious code to visitors anyway.
Attackers injected malicious JavaScript into Optimizely, an A/B testing platform used across major websites. The attack reached 178 organizations, delivering code designed to steal payment information and target iPhones with exploit kits.
The malicious code came through a trusted third-party script, served from a legitimate domain with a valid certificate.
Every third-party script on your site is someone else's security posture running in your visitors' browsers.
Do you know what yours are loading right now?
cybersecuritynews.com/optimi…
#MSP #Cybersecurity #SupplyChainAttack

1
42
The FBI just put a name on something we have been watching for months.
Over the weekend the Bureau warned that attackers are using ARTEX, an AI-powered penetration testing framework, to automate cyberattacks against organizations worldwide. A tool built to help defenders find weaknesses is now running those same playbooks at machine speed, for the other side.
This is the shift that matters for MSPs. Reconnaissance, exploitation, and lateral movement that used to take a skilled operator days now runs in minutes without one. The attacker does not get tired, does not log off at 5, and does not need to be good. The tool is good for them.
Machine-speed attacks do not wait for business hours. Your detection and response cannot either.
#MSP #Cybersecurity #AIThreats
BleepingComputer on the FBI warning: bleepingcomputer.com/news/se…

1
22
It is Friday, and we wear red.
R.E.D. stands for Remember Everyone Deployed. For the service members who are away from home, and for the families holding things down until they return.
From all of us at BLOKWORX, we see you. We remember you. Come home safe.
#REDFriday #RememberEveryoneDeployed

Attackers are going after MSP tools again.
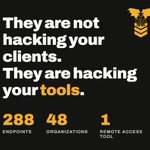
Active ScreenConnect attacks have planted rogue clients on 288 endpoints across 48 organizations. A day earlier, N-able pulled N-central offline after 33 flaws were found.
Your remote access and RMM stack hold the keys to every client you manage. If a rogue agent showed up today, who would notice?
The BLOKWORX SOC watches partner environments for exactly that. [email protected]
#MSP #Cybersecurity

13
Today is Veterans Day.
Every Friday we wear red at BLOKWORX for the ones still deployed. Today is for everyone who served. Thank you for the years you gave, the places you went, and the things you carried back.
If you have a veteran on your team, make sure they hear it today.
#VeteransDay
5
Today is Patch Tuesday. For attackers, it is research day.
Every fix Microsoft ships gets reverse engineered within hours, and the gap between patch and exploit keeps shrinking. Just last week, attackers were hammering a new OpenSSH flaw within hours of disclosure.
A patch only protects the machines that get it, and most environments take days or weeks to get there. The window in between is exactly when someone needs to be watching.
Patch fast. Have the BLOKWORX SOC watching while you do. [email protected]
#MSP #PatchTuesday

44
An active campaign is using stolen Microsoft Entra application secrets to log in to MSP environments as trusted apps, then pivoting into downstream clients. 27 organizations hit so far. No malware, no phishing, no Microsoft flaw. Just valid credentials nobody was watching.
User MFA does nothing here, because nothing signs in as a user. App identities need eyes on them too.
BLOKWORX ITDR watches Microsoft 365 identity activity for exactly this. blokworx.com/worx-bundle/
#MSP #ITDR

2
94
An active campaign is using stolen Microsoft Entra application secrets to log in to MSP environments as trusted apps, then pivoting into downstream clients. 27 organizations hit so far. No malware, no phishing, no Microsoft flaw. Just valid credentials nobody was watching.
User MFA does nothing here, because nothing signs in as a user. App identities need eyes on them too.
BLOKWORX ITDR watches Microsoft 365 identity activity for exactly this. blokworx.com/worx-bundle/
#MSP #ITDR

31
Every MSP should ask their security vendor one question: what happens after the alert?
Some vendors will say the alert goes to your queue. That means you bought a tool. Your team still has to investigate it, respond to it, and wake up for it at 2am.
A real security partner answers differently. Trained analysts see the alert, investigate it, and handle it before it ever lands on your team.
Ask the question. The answer tells you who is actually doing the work. BLOKWORX partners already know ours. [email protected]
#MSP #MSSP

12
Hackers spoiled tons of food across Europe this week without touching a single register. They took over supermarket refrigeration controls in at least six countries and flipped freezers into defrost mode overnight.
Most of that gear was vendor managed and sitting on networks nobody watched. Your clients have equipment just like it.
If you cannot see it, you cannot defend it. BLOKWORX gives partners visibility into the networks their clients actually run. [email protected]
#MSP #Cybersecurity

34
Colonial Pipeline hit on Mother’s Day weekend. JBS on Memorial Day. The FBI and CISA have warned for years that major ransomware deployments cluster around holidays, when staffing is thin and response is slow. Attackers check the calendar before they check your defenses.
The holiday stretch starts this month. Before PTO requests start stacking up, answer one question: who is watching your client environments at 2 AM on Thanksgiving?
If the honest answer is “whoever answers the phone,” that is a coverage gap, not a plan. Our SOC does not take holidays: blokworx.com
#MSP #Ransomware #SOC

11
Count the human users in a typical M365 tenant. Now multiply by 25.
That is how many non-human identities sit alongside them: service accounts, OAuth grants, API tokens. No MFA. Permissions that pile up. Almost nobody reviewing any of it.
Attackers have noticed. Most MSPs have not.
We broke down the 25-to-1 problem and where to start looking: blokworx.com/the-25-to-1-pro…
#MSP #IdentitySecurity #CyberSecurity

13
The scariest things this Halloween are not wearing costumes. 🎃
Ghosts are not real. Phishing emails are. Vampires do not drain your resources. Unmonitored endpoints do. Zombies are fiction. Dormant accounts with active credentials are not.
The monsters that should keep MSPs up at night do not knock on the door once a year. They probe networks every night, holidays included.
Our SOC does not take Halloween off. While the kids are out trick-or-treating, we are watching the endpoints, hunting the threats, and keeping the candy, I mean data, where it belongs.
Happy Halloween from the BLOKWORX team. Stay safe out there, in every sense. 👻
#Halloween #Cybersecurity #MSP #BLOKWORX #SOC

12
R.E.D. Friday. Remember Everyone Deployed.
Every Friday, the BLOKWORX team wears red for the men and women serving far from home. They stand watch so the rest of us do not have to.
To every service member deployed around the world: we see you, we thank you, and we will not forget you.
Wear red today. Remember Everyone Deployed. 🇺🇸
#REDFriday #RememberEveryoneDeployed #BLOKWORX #SupportOurTroops

7
Nearly half of MSP clients already treat their MSP as the CISO. They just do not call it that.
Sophos surveyed 800 MSPs this spring. 84% expect demand for CISO-style services to grow over the next year. Clients are not asking for another tool. They are asking who is accountable when something gets through.
That is a different job than reselling licenses. Someone has to read the signals, own the response, and show up for the review.
If you are the CISO now, make sure something is watching at 2 a.m. The BLOKWORX SOC is 100% US-based and on watch 24/7/365.
blokworx.com/worx-bundle/
#MSP #vCISO

11
Three end-of-support dates land this month, and all three are sitting in client environments.
Windows 10 consumer ESU ended October 13. Exchange Server 2016 and 2019 receive their final security update this month, and Microsoft says there will be no further extension. Windows 11 24H2 Home and Pro got their last update in October as well.
After this month, every one of those systems is a known target that cannot be patched. Attackers keep lists.
Pull the inventory this week. Anything on it needs a dated plan, not a note to revisit in Q1.
#MSP #EndOfSupport

25
Cybersecurity Awareness Month has four days left. The holidays do not.
Short staff, year-end deadlines, and inboxes full of shipping notices and gift card requests. Attackers plan for that season too.
Are you REDI? Score your MSP in about five minutes, before Q4 gets loud.
blokworx.com/redi/
#MSP #CybersecurityAwarenessMonth

9