

i talk about security i explain crypto. i talk about life also i'll block you if you don't have a cold wallet Telegram: Bala_ibb. Building @Astraeus_AI
knowledge is wealth
Joined October 2018
- Tweets1K
- Following1.3K
- Followers20K
- Likes173K


Bala 🧤 retweeted
every piece of software you trust right now has a vulnerability that nobody's found yet
not some of them. all of them
your wallet, your browser, your banking app, your password manager, the operating system running your phone right now
openssh runs almost every server on earth, somebody found out that typing 257 random characters as the password gives you full root access. just like that
microsoft paint, the app you drew stick figures on as a kid, just got a vulnerability that lets attackers run code on your computer through the internet. paint.
apple told everyone icloud was end-to-end encrypted, then buried in a support page that sharing a link kills the encryption completely even if you paid for advanced data protection
these are the most audited, funded, and trusted tools ever built and they keep falling apart in ways nobody predicted
code is written by humans who cut corners, increasingly generated by AI that doesn't understand what it's producing, and tested by systems that can only catch what someone thought to look for
"secure software" doesn't exist. there's just software running on borrowed time until someone finds the crack
Bala 🧤 retweeted
changing your gmail password after getting hacked is the first thing everyone does and it barely fixes anything
when someone gets into your gmail they don’t just read your emails, they set up systems that keep working after you lock them out
they set forwarding rules that send a copy of every email to their address, filters that auto-delete google’s own security warnings before you see them, IMAP access that lets them read your inbox from another app entirely
you change the password thinking you’re safe, meanwhile every email you receive is still being forwarded to someone else and you’d never know because the notification google shows you disappears after one week
here’s what you need to check right now
go to gmail settings, forwarding and POP/IMAP, if there’s a forwarding address you didn’t add, disable it
check filters and blocked addresses, if there’s a filter you didn’t create especially one that auto-deletes or auto-forwards, delete it
check your labels for anything unfamiliar, and turn off IMAP access if you’re not using it
if you’ve ever used “continue with google” to log into chatgpt, gemini, or anything else, those apps still have access too. a password change doesn’t revoke them
your password is the front door. hackers don’t come back through the front door, they leave windows open
Bala 🧤 retweeted
binance gave their engineers an internal AI tool to work faster. north korea used the same tool to rob them of $6.34 billion
after compromising one engineer through a fake job interview, the hackers didn't try to brute force their way through binance's security
they just logged into the AI tool that engineer already had access to, used it to reach two more engineers on the wallet team
found a container deployment token sitting on one of their machines, and from there walked straight into the wallet signing system
binance caught and blocked 57 north korean attacks this year. number 58 didn't attack their defenses, it used their own tools against them
the thing they built to make their team more efficient is the same thing that made the breach possible

Bala 🧤 retweeted
discord is about to make your public server messages searchable on google starting mid december
and the setting is already turned ON for you by default
that means anything you've ever typed in a public server, your takes, your questions, your conversations, all of it can show up when someone googles your username
the opt out is buried in User Settings → Data & Privacy → turn off "Show my message content from Discoverable channels on web pages"
funny how the EU, UK, canada, brazil, australia and south korea get it turned OFF by default but the rest of us have to go find it ourselves
every app is starting to feel like a race to see how much of your data they can expose before you notice
Bala 🧤 retweeted
everyone talks about 2FA but almost nobody is using the version that’s actually unhackable
most people use text message codes or authenticator apps. both can be beaten. sim swaps beat SMS, phishing sites can steal authenticator codes in real time
there’s a third option almost nobody talks about. it’s called a yubikey
it’s a tiny device you keep on your keychain. when you log into your google, apple, or crypto accounts, you plug it in or tap it on your phone. without that physical tap, nobody gets in. not hackers, not phishing sites, not even you from a different device
the reason phishing doesn’t work on it is because the key checks the actual website URL before responding. a fake google login page gets nothing. the yubikey just refuses
it costs around $50-70. you can’t update the firmware after buying so make sure you get the latest version, and buy directly from yubico not random sellers
keep one on your keychain and store a backup somewhere safe
$50 for a device that makes your accounts basically untouchable. that might be the cheapest security upgrade that actually works
Bala 🧤 retweeted
black october just got worse. a japanese company lost 27,000 servers and it’s not even the scariest part
GMO Internet runs a cloud service called Onamae Desktop, mostly used by forex traders running automated trading bots
hackers broke in, installed malware across up to 26,739 servers, stole trading credentials and started making unauthorized trades on people’s accounts
not one broker. over 70 different securities and forex firms across japan and internationally. people woke up to trades they never made, money moving they never authorized
OANDA Japan froze customer withdrawals. GMO refused to pay the ransom, permanently shut down the entire service, and did something nobody expected
they asked the japanese government to use brand new active cyber defense powers, literally military-grade authority that just went into effect october 1st, to trace and neutralize the attackers’ infrastructure. the government can now legally hack back
the technical details from the attacker’s own site are terrifying. GMO configured their VPS network using Active Directory, something you should never do on shared hosting
every server had admin credentials. and the RDP files customers used to connect? drive redirect was enabled by default, meaning the moment you connected to your VPS, your entire local PC was shared with the server
hackers didn’t just own the servers. they had a direct path into every customer’s personal computer. they extracted data, installed backdoors. customers were exposed like this for over 7 years
27,000 servers. 70+ brokers. unauthorized trades. personal computers backdoored. a company begging its government to go to cyber war
october isn’t slowing down
Bala 🧤 retweeted
they’re calling it “Black October” and i don’t think people realize how serious this is
in the last 48 hours there have been over 27 major cybersecurity incidents. not in a month. not in a week. in 48 hours
any ONE of these would normally be the biggest story of the year
PHP: critical vulnerability in the software running 80% of the web. severity 9.2 out of 10
Node.js: high-severity flaw letting attackers take over servers remotely. affects versions 22, 24, and 26
Java: also compromised. three of the most used programming languages on earth hit at the same time
GitLab: a perfect 10 out of 10 severity hole in every version since 2014
Railway: hosting platform compromised. API keys for OpenAI, Claude, Stripe potentially exposed
Signal: a bug that could leave your mic and camera on after you hang up
WordPress: hackers stole a plugin maker’s keys and planted backdoors on websites
LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
and that’s not even half the list
thousands of AI agent swarms are reportedly scanning and attacking vulnerable servers right now. automated. around the clock
security researchers are saying this might be the early stages of a global cyber incident that nobody fully understands yet
if you run a website, use cloud services, store API keys on hosting platforms, or use any software built on PHP, Node.js, or Java you are potentially affected
update everything. rotate your API keys. change your passwords on critical services. enable 2FA everywhere you haven’t already
this is not a normal week on the internet. this is something different
Bala 🧤 retweeted
cellebrite can now unlock your iphone remotely from 8 meters away, no physical access needed
iPhone 11 through 16. even with stolen device protection turned on
remember when zachxbt said use a dedicated iphone instead of a hardware wallet because it's safer?
someone with this device just needs to be within 26 feet of you and your phone is open
at a conference. at a coffee shop. in an airport. sitting next to you on a bus
they don't need to touch your phone. they don't even need to be close enough for you to notice them
and this is a tool being sold to law enforcement and forensic labs. right now. commercially available
if it's available to governments it's eventually available to everyone else
your iphone was never a vault. it was always just a phone with a better lock. and now even that lock can be picked from across the room


Bala 🧤 retweeted
a VPN couldn’t save this kid from the FBI. one phone number brought the whole thing down
he swatted a girl’s home for years. threatened to firebomb it on discord. thought his VPN made him invisible
the FBI caught him because his discord account was registered to his real phone number
they matched the IP addresses from his verizon account to his discord login times. same IPs. same timestamps. same person
bro had a VPN running the whole time and it meant nothing because his phone number connected every single dot
a VPN hides your browsing. it doesn’t hide the phone number you signed up with
a VPN without OPSEC is just expensive false confidence


Bala 🧤 retweeted
did you know someone can track your exact location just by sending you a PDF?
no malware. no link to click. no app to install. just a regular looking PDF
let me explain how this works because most people have no idea
when someone sends you a PDF they can embed a tiny invisible image inside it that loads from their server
the moment you open the PDF the image loads. their server records your IP address
your IP address tells them your city, your internet provider, and your approximate location
you didn’t click anything suspicious. you just opened a document
this is how people get doxxed. someone sends a “job offer” or a “partnership proposal” as a PDF
you open it thinking it’s legit but it might not be
and this isn’t just PDFs. word documents and HTML emails do the same thing
the most innocent looking file on your screen might be quietly telling someone where you live right now
Bala 🧤 retweeted

my portfolio: never reach $30
my screen time: diabolical
my sleep schedule: messed up
my social life: deteriorating
my blue tick go soon expire
but yeah crypto is definitely going to change my life

Bala 🧤 retweeted

my portfolio: down 50%
my screen time: up 400%
my sleep schedule: destroyed
my social life: non existent
but yeah crypto is definitely going to change my life
Bala 🧤 retweeted
a hacker just accessed denmark’s entire national ID database. 8.8 million people got exposed
the password protecting it was “123456”
bro. an entire country. 8.8 million citizens. their most sensitive personal data
protected by a password that wouldn’t pass the signup page on most websites
i need 12 characters, a capital letter, a number, a special symbol, and a blood sacrifice just to log into my email
but an entire nation’s identity database was sitting behind “123456” this whole time
we keep talking about sophisticated hackers and zero-day exploits and AI cracking encryption
sometimes the biggest hack in the world doesn’t need any of that
sometimes the door was just never locked
Bala 🧤 retweeted
the UK guy who got robbed for $800K at knifepoint could have avoided it if he followed these rules
never reveal how much crypto you hold online. not even to your close friends. one screenshot. one conversation. that’s all it takes for the wrong person to find out
no exchange or wallet company will ever call you first. if someone calls claiming to be support hang up immediately. open the app yourself
never buy a hardware wallet from anywhere except the official website. we just saw $86 million drained from tampered devices bought at real stores
use a separate email and phone number for all your crypto accounts. if your main gets compromised your crypto stays untouched
if you’re holding serious money move in silence bro. no PnL screenshots. no “just made $50K” posts. no flexing. the people watching your timeline aren’t all fans
the guy in the UK did everything right with his wallet security. but his identity was linked to his holdings and someone showed up at his door with a knife
your wallet can’t protect you if people know where you live and what you hold
Bala 🧤 retweeted

somewhere along the way, NFTs stopped meaning anything.
we went back to the beginning.
arc916.xyz
Bala 🧤 retweeted
how do you lose $4 million and still tweet about it this calmly
crypto genuinely rewires your brain from reality bro
frogman woke up at 4:30AM in a hotel in singapore and his wallet was empty
$4 million gone. nine tokens drained. converted to ETH BNB and SOL. laundered through privacy tools before he even opened his eyes
bro is at TOKEN2049. surrounded by thousands of crypto people. linked up with new people the night before
and by morning everything was gone
he still doesn't know how it happened. nobody does yet
crypto events are the most dangerous place for your wallet bro
everyone around you knows you hold bags. they see you. they hear you talking
$4 million stolen while he was sleeping in his hotel room
and the scariest part? he might have shaken hands with the person who did it

Bala 🧤 retweeted
Let me explain what it is all about
. @Astraeus_AI is a decentralized AI marketplace aimed at connecting builders with organizations that want to discover and buy access to AI tools.
Think of it as a platform designed to bring AI models, AI agents, developers, and users into one ecosystem.
The meeting hub for AI builders & organizations focused on discovering products, meeting builders, and finding opportunities.
➝ What it does?
Creators list AI models, APIs, automation scripts, and data pipelines. Buyers discover, evaluate, and purchase access. The stated mission is to make production-ready AI tools accessible to organizations while giving creators a fair, secure place to monetize their work.
On-chain activity uses a single-chain setup on Base, with USDC as the settlement currency.


Are you a builder and ship AI tools but have no real way to monetise them?
This is where @Astraeus_AI comes in.
Bala 🧤 retweeted
zach is a fuckin beast
this man is doing FBI-level work from his laptop for free 😭


Bala 🧤 retweeted
bro zachxbt is actually insane
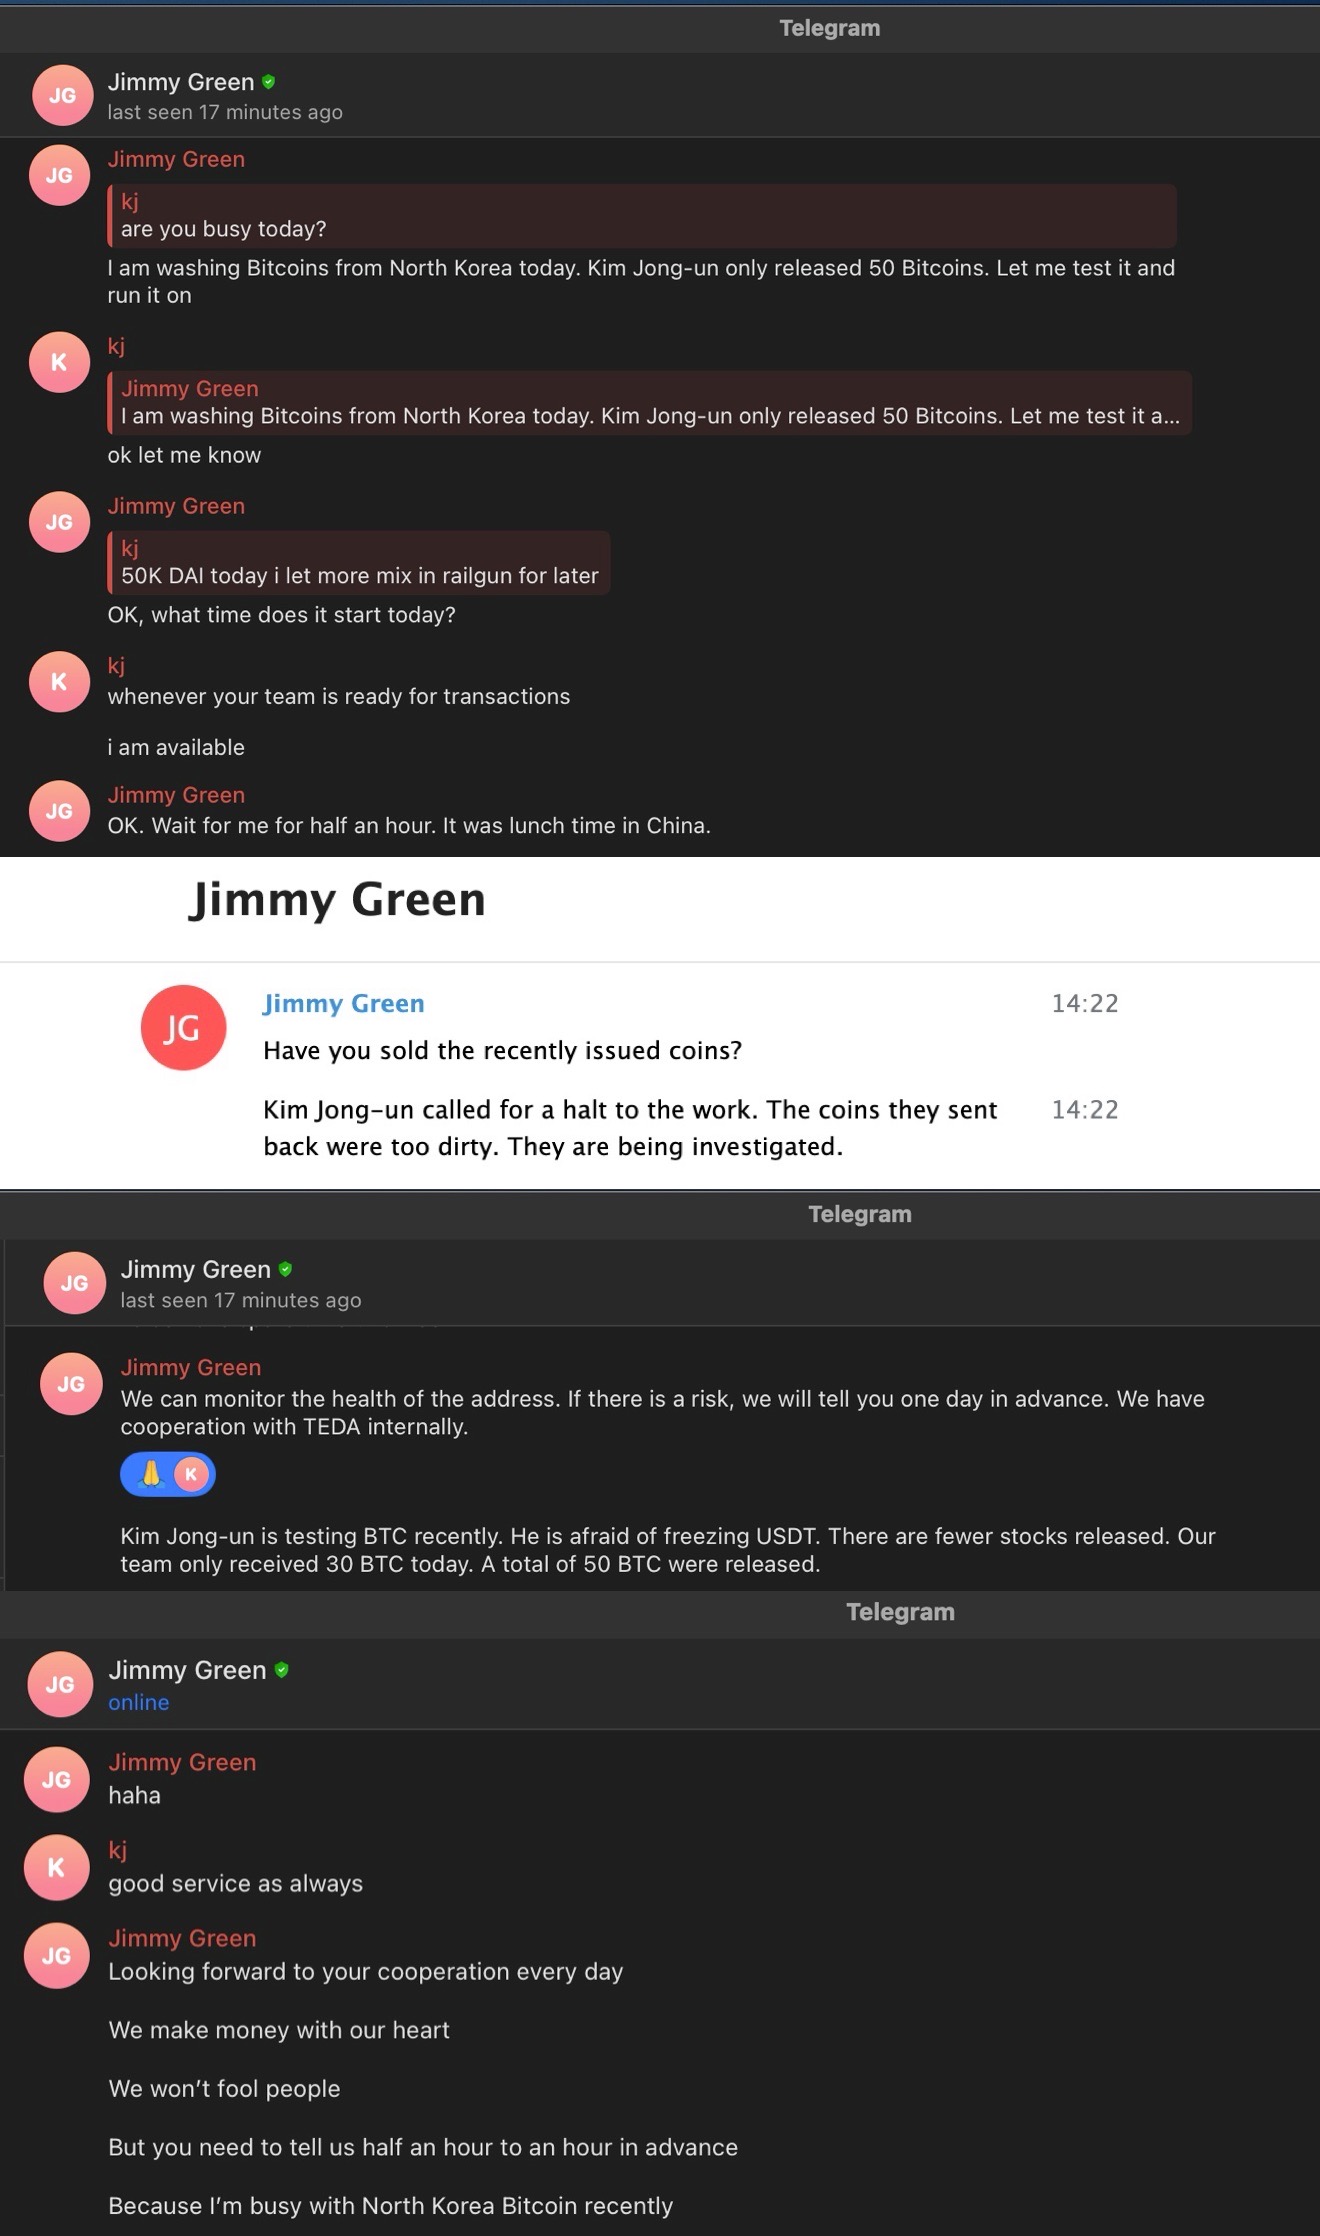
this man went undercover as a money laundering client
spent $350K of his OWN money to gain the trust of a chinese launderer who was moving bybit hack funds for north korea
the guy started sharing everything. screenshots. wallet addresses. bridge transactions. in real time
zach was matching every single transaction on-chain as the guy was sending them
traced $12M+ across bitcoin, ethereum, solana, and tron
got tether to freeze $442K from the evidence alone
and the funniest part? in between discussing how to launder funds for north korea this guy was casually talking about playing mahjong and his weight loss plan 😭
bro thought he was talking to a client. he was talking to the most dangerous investigator in crypto
and zach funded this entire operation himself. $350K out of pocket. no guarantee he'd ever see it back
this is not the FBI. this is one guy with a laptop and a blockchain explorer
different breed