

School of Solana S8 • Uniswap Hook Incubator S10 • Rektoff Rust Security C5 💙 | Java dev by day, Building Wu!Studio 🔥
Kuala Lumpur
Joined August 2023
- Tweets249
- Following592
- Followers107
- Likes2.8K


Pinned Tweet
spent saturday at the @aws kuala lumpur office for "AI Agents are coming for wall street: the future of RWAs" by @treasures_io. walked out with my mental model of tokenized assets fully rewired. quick thread on what i learned 🧵
I built Haunted Handshake: Lava-Cracked Witch Hat H on AI Skills Studio from Handshake
app.joinhandshake.com/ai-sho…
1
90
Brian Har 🇲🇾 - Wu!Studio. retweeted

i built a skill to un-slop AI-looking apps
most AI-generated UIs still have the same problem:
they look polished, but they also look obviously AI-made
same cards
same gradients
same generic “modern app” layout
same zero-personality design
so this skill forces claude to actually think differently than it would normally do
→ starts from a real visual concept
→ explores 3 different directions
→ picks one coherent design language
→ renders the screens at iPhone size
→ scans the result for obvious AI-slop patterns
→ critiques and refines it before you ship
when everyone is shipping ai slop apps, yours has to be different to succeed
i’m giving the full skill away for free
rt + comment “stop slop” and i’ll send it over
(follow so i can dm)


Got my NFT ❤️ Thanks @AtriumAcademy! Can’t wait for the swag and further building Landfall in next cohort 😎

2
10
177
😂

Ass Bench Update 🚨
After running GPT 6 Astra in a loop for the past week, with a couple of steers a day, we have officially reached high-fidelity cheeks.
I’m going to let this thing run in a self-improving cycle for as long as I can and see where the ass technology ends up in a month.
Lots of different butt styles will be added, so no one is safe.
Not even you, Granny.
You’ll also be able to support the project and help fund the benching of other models like Fable, Gemini, etc.
All it takes is a buck, and you can slap your sticker + website directly onto a cheek.
The future of AI benchmarking is here
More Soon
65
The best developer tools, free for students: education.github.com/pack via @githubeducation
happy to be a student lol :)

6
82
Gonna spend my evening to play this 🐸

What if you could learn Kuala Lumpur’s history just by playing? 🇲🇾🎮
I’m building Jalan KL with GPT 6 Astra ~ a 3D adventure where you roam the city, complete quests, and uncover the stories behind its landmarks.
For locals rediscovering home and visitors getting their first taste.
Jom jalan! 👟
try it here: jalankl.themasterofnone.xyz
1
64
received my graduation certificate for the @rektoff_xyz x @solana Rust Security Bootcamp 🦀
Huge thanks to the Rektoff team and mentors for putting together such an intense, hands-on, and high-quality program. Really appreciate the time, guidance throughout the journey ❤️

Capstone notes just came back.
Love how meticulously they read our capstone project and giving full attention on feedback ❤️🫡 All respect to Lucas and @m4rio_eth!
Next time I will write all the issue I found 😂🫡


1
48


Brian Har 🇲🇾 - Wu!Studio. retweeted

GPT-6 Astra is world class at Blender and 3 dimensional reasoning. This was a 1-shot game it created, all running in browser.
Brian Har 🇲🇾 - Wu!Studio. retweeted

We just launched the ElevenLabs MCP in Claude.
You can now manage your voice and chat agents where you already work. Review performance, spin up new agents, update configs, all without leaving your Claude session.
To celebrate, we're giving away 11k free credits so you can build your next AI Voice Agent.
For the next 11 hours, retweet + comment "MCP" below and we'll DM you the credits.
(must follow so we can DM)

Awesome 👏

💰🚨 $1.4M from Web3 bug bounties in 2026!
Meet @0xvivekd and learn about his journey, mindset, AI workflow, and the lessons he's learned along the way.
Part 1: The Journey
- Vivek didn't come from a software engineering background.
- He was a Chartered Accountant (licensed financial and tax professional) running his own firm.
- In 2021, a friend who traded crypto came to him for help filing taxes. That's how he got introduced to crypto and started investing, mainly participating in IDOs (Initial DEX Offerings).
- When the bear market arrived, he didn't leave the industry. He pivoted into data analysis.
- Then in 2023, as the market became active again, he started airdrop farming.
- In June 2024, he entered Web3 security through public audit contests.
- The next 15 months were difficult.
- He kept participating in contests but struggled to achieve consistent results.
- Around August/September 2025, he made a decision that completely changed his career.
- He switched from public audit contests to bug bounties.
Today, he has earned over $1.3M in bug bounties in 2026 alone, including another $250,000 critical bounty announced yesterday.
Part 2: The Mindset
- "Bug bounties are not difficult in the technical sense. They are difficult from a psychological point of view."
- He explained what led him to leave audit contests:
- During a White Hat Mastermind, everyone was asked what they were working on.
- Around half of the researchers were working on the contest with the smallest scope and the lowest payout.
- Vivek realized he was always choosing the easiest targets because they offered the fastest and most predictable payouts.
- Bug bounties were different. There was no guarantee of finding anything. No guaranteed payout. Sometimes weeks of work could lead to nothing.
- That was exactly why he switched.
- As he put it:
"Bug bounty hunters are paid handsomely for dealing with uncertainty."
Part 3: AI
- AI has completely changed Vivek's workflow.
- Today, he gives AI a target while he spends that same time building a high-level understanding of the protocol.
- Once AI surfaces potential issues, he validates them, removes false positives, and determines whether they're actually valid vulnerabilities.
- His estimate surprised me.
Today, around 70-80% of the issues are initially surfaced by AI.
- But he doesn't believe AI will replace security researchers. His reasoning is simple.
- AI is excellent at spotting unusual behavior. It still struggles to understand intended behavior. That's why human validation remains essential.
- He also believes the learning process has changed.
- Reading audit reports and recent hacks is still fundamental, but today researchers should also follow AI developments and continuously experiment with AI tools.
Part 4: Advice
- According to Vivek, DISCIPLINE is what separates the best researchers from everyone else.
- His advice was straightforward:
Don't expect meaningful results during your first 12 months. Focus on the inputs, not the outputs. Don't compare yourself to researchers who have been building their skills for years. Stay disciplined. Don't chase shiny objects. Keep adapting as the industry evolves.
- One detail I really liked was how he dealt with difficult periods.
- Whenever he went through a dry spell, he listened to podcasts from other top white hats.
- Not because they never struggled. But because they did.
- It reminded him that even the best researchers experience periods without finding bugs.
Congratulations on the incredible journey! @0xvivekd. 👏


1
69
Brian Har 🇲🇾 - Wu!Studio. retweeted

The best AI audit tools I've used 🧵
> All free
> All on GitHub
All built by actual auditors
(4 of them Bulgarian, we are so back)
Save this one 👇
1⃣ Pashov skills by @pashovkrum
Fast, cheap and efficient. 2 skills:
📌solidity-auditor - security feedback on your changes in under 5 min
📌x-ray - pre-audit scan that builds a threat model, invariants and entry points
github.com/pashov/skills
2⃣ Claudit by @MartinMarchev
Find bugs on solodit without the manual searching.
It's an MCP that plugs Solodit's 20,000+ findings straight into Claude. You describe the bug you are looking for and it pulls the exact reports.
github.com/marchev/claudit
3⃣ Plamen by @p_tsanev
Costs a lot, but it's really good.A fully autonomous audit agent that runs 20-100 agents and only reports bugs with a verified PoC.
A thorough run is $30-100+ but it fuzzes invariants and has a judge to kills false positives.
Supports EVM, Solana, Move and L1s
github.com/PlamenTSV/plamen
4⃣ foundry-poc-mainnet-fork by @cholakovvv
Turns your finding into a submission-ready Foundry PoC on a mainnet fork.
Real deployed addresses, no mocks, no vm.store cheats.
github.com/cholakovvv/foundr…
5⃣ sc-auditor by @archethect
Map, Hunt, Attack. 6 specialized agents hunt in parallel (reentrancy, accounting, oracle, economic...) then every finding goes through a Devil's Advocate that tries to kill it.
github.com/Archethect/sc-aud…
6⃣ Nemesis by @0xiehnnkta
2 agents in a loop: a Feynman auditor that questions WHY every line exists, and a state auditor that hunts for coupled state that updates on one side only.
Each pass feeds the next until nothing new surfaces.
This is the closest to how a human actually audits.
github.com/0xiehnnkta/nemesi…
---
That's the stack.
Missing an invariants tool tho... if you know a good one drop it below 👇

Brian Har 🇲🇾 - Wu!Studio. retweeted

C5 just crossed the equator, and Module 1 is officially in the books.
This week the cohort arrived where all the groundwork was pointing:
> Lecture 5. Solana Virtual Machine (SVM).
> Lecture 6. Practical guide to SVM.
That closes out the first module. Six lectures, one arc:
> How memory actually works.
> Where it breaks, and what unsafe Rust really costs.
> Who gets to touch memory and why ownership decides it.
> And finally, the machine all of it runs on.
Three weeks ago this was 125 people with strong fundamentals. Now it's a cohort that can read the SVM the way an auditor needs to, from the bytes up.
Module 2 is where it turns adversarial.

Two weeks into C5, and the cohort is now properly inside Rust's engine room.
Week 1 was how memory actually works. Week 2 is who gets to touch it.
> Lecture 3. Exclusive access and memory, the borrow checker's core promise and what it actually guarantees.
> Lecture 4. More on ownership and memory, going deeper into the model everything else in Rust stands on.
Plus office hours with @danielkcumming, where the questions from lectures get pulled apart one-on-one.
Ownership is the part of Rust that makes entire classes of bugs impossible to write, and it's the lens every audit this cohort will ever run looks through.
Foundations first. The security work lands harder because of it.

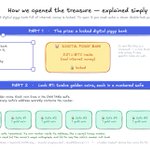
A first-ever Simplicity CTF on Liquid: a digital piggy bank of L-BTC behind two locks that only open *together*.
I drove Claude Opus 4.8 through the on-chain forensics and rebuilt the unlock myself.
Here's how the puzzle works 🧵👇


1
2
322
So "winning" = reconstructing it on regtest where I'm the owner:
issue 12 units → fund the 12 nonce-slot addresses → fund the reward → fire the atomic claim tx.
`simplex test` → 1 passed. Reward claimed 🎉

1
73