

We find exposed attacker infrastructure, read what they leave behind, and publish it as a case file.
Joined July 2026
- Tweets44
- Following0
- Followers185
- Likes5



Pinned Tweet
Coruna iOS exploit kit, new IOCs:
- 88 lure hosts
- 37 compromised sites used as watering holes
New IOCs (1/3):
iphone[.]apiforx[.]work
trigger[.]translatevv[.]com
mobilecare[.]me
carolineschaay[.]nl
IOCs below. Full list + CSV: c2huntersresearch.com/blog/2…
#Coruna #iossecurity

Your smart TV could be an attacker's exit node right now, and you'd never know.
We analysed 100+ attacker IPs renting real home internet to look like ordinary visitors. Ten real cases, from the attacker's own code.
c2huntersresearch.com/blog/2…
#ResidentialProxy #JA4 #Fraud #BOT

Inside the ten cases: fake signups that pass fraud checks, a bank intrusion on one proxy account across 80 scripts, cryptojacking that hides from the proxy provider too, carding, credential stuffing, and more.
The IP alone won't catch any of it.
#ResidentialProxy #JA4+

An AI agent ran a 32-day #ransomware and intrusion campaign from a single markdown file (OPERATION_MEMORY.md).
We analysed the file behind what we call Operation HADES: 2,148 lines of rules, credentials and a live log.
c2huntersresearch.com/blog/2…
#HadesRansomware #DFIR #CTI

The monetization order was set before the first target: crypto, then payments, then ransomware.
The result: an ISP breached from the inside, 606,932 payment transactions exposed and 10 live tunnels into internal networks.
#ransomwareattack
It even timed its recon around a service's daily API quota reset: 16:00 UTC plus 7 minutes, every day. By the end it had spawned 473 sub-agents.
Full analysis, with the Russian original and translation:
c2huntersresearch.com/blog/2…
Part 2 coming soon: the toolkit and TTPs.
C2 Hunters Research retweeted

Added two new items to the feeds, courtesy of the item below and @C2HuntersLabs
- VShell C2
- DesRedTeam (a.k.a. DesShell)
items should be live soon.

VShell C2 (v4.9.3) panel identified.
VShell is a cross-platform post-exploitation framework popular with Mandarin-speaking threat actors.
WebSocket connection found in the panel: wss://www.haiwoi[.]top/api/v2/sync
IOC: haiwoi.top
#ThreatIntel #C2 #VShell

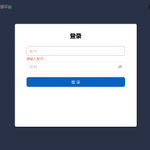
Pivoted further using @modat_magnify and found 16 active VShell panels across 13 IPs. All serving the same Chinese-language login page.
IOC thread 🧵
#ThreatIntel #C2 #VShell

VShell C2 (v4.9.3) panel identified.
VShell is a cross-platform post-exploitation framework popular with Mandarin-speaking threat actors.
WebSocket connection found in the panel: wss://www.haiwoi[.]top/api/v2/sync
IOC: haiwoi.top
#ThreatIntel #C2 #VShell
Active VShell panel IOCs:
23[.]238[.]80[.]171:8082 🇺🇸
143[.]92[.]51[.]145:8082 🇸🇬
8[.]138[.]112[.]168:23333 🇨🇳
38[.]60[.]227[.]210:81 🇭🇰
38[.]60[.]227[.]210:443 🇭🇰
23[.]226[.]132[.]147:8082 🇺🇸
119[.]28[.]13[.]158:80 🇭🇰
38[.]55[.]192[.]71:17777 🇺🇸
218[.]1[.]219[.]233:51010 🇨🇳
218[.]1[.]219[.]233:51030 🇨🇳
218[.]1[.]219[.]233:51050 🇨🇳
45[.]113[.]200[.]6:8082 🇨🇳
111[.]229[.]112[.]115:8082 🇨🇳
132[.]232[.]203[.]63:8082 🇨🇳
101[.]37[.]80[.]76:8095 🇨🇳
36[.]138[.]100[.]216:45991 🇨🇳
Credit to @modat_magnify for the scan data.

We identified an exposed server hosting infrastructure for a suspected #DarkSword iOS exploit operation.
The exposed files included a SQLite database (darksword.db), exploit delivery code, post-exploitation scripts and server logs.
Here's what we uncovered:
🧵(1/4)

We also recovered group.html and post_exploit.js.
The code contains a staged iOS exploit loader, sandbox-escape routines, device identification, command polling and data collection capabilities.
Server logs confirm repeated requests to the exploit delivery page. (3/4)
An interesting observation: much of the recorded activity originated from private or loopback IPs, with repeated landing-page tests.
This suggests possible operator-side testing, although external deployment cannot be ruled out.
#darksword #coruna #ios #exploitkit (4/4)
We also recovered group.html and post_exploit.js.
The code contains a staged iOS exploit loader, sandbox-escape routines, device identification, command polling and data collection capabilities.
Server logs confirm repeated requests to the exploit delivery page.
(3/4)
An interesting observation: much of the recorded activity originated from private or loopback IPs, with repeated landing-page tests.
This suggests possible operator-side testing, although external deployment cannot be ruled out.
#darksword #coruna #ios #exploitkit (4/4)
The recovered database contained:
• 18,054 HTTP activity logs
• 3,109 exploit telemetry records
• 5 landing-template records
• 8 configured command scripts
• 469 administrative audit events
The data provides a glimpse into the backend infrastructure.
#iOS (2/4)
VShell C2 (v4.9.3) panel identified.
VShell is a cross-platform post-exploitation framework popular with Mandarin-speaking threat actors.
WebSocket connection found in the panel: wss://www.haiwoi[.]top/api/v2/sync
IOC: haiwoi.top
#ThreatIntel #C2 #VShell
Coruna iOS exploit kit — new IOCs, part 2.
Additional infra found via @modat_magnify
New IOCs (1/2):
https://fcsvip[.]icu
https://btvm888[.]xyz
18[.]141[.]188[.]98
203[.]189[.]235[.]62
186[.]244[.]241[.]222
205[.]234[.]170[.]172
177[.]5[.]75[.]142
154.219[.]112[.]16
#coruna
Coruna iOS exploit kit, new IOCs:
- 88 lure hosts
- 37 compromised sites used as watering holes
New IOCs (1/3):
iphone[.]apiforx[.]work
trigger[.]translatevv[.]com
mobilecare[.]me
carolineschaay[.]nl
IOCs below. Full list + CSV: c2huntersresearch.com/blog/2…
#Coruna #iossecurity