

Updates about all things threat intelligence & updates about stuffs going on in the cybersec, ransomware, OSINT, SOCMINT, and hacking communities #threatintel
in the wires
Joined January 2026
- Tweets958
- Following4.4K
- Followers3.9K
- Likes4.5K





Pinned Tweet
Drughub vendor usernames now tracked and added to threatactorusernames.com/
#osint #threatintel #cti #cybersecurity #infosec #dnm

CTI Updates retweeted

Spacebears ransomware DLS caught mid debug crash on its onion portal. PHP 8.3.6, Laravel 10.43.0, Ignition exposed via SQLSTATE. Stack trace, filesystem paths, controller source, raw SQL queries and env vars visible. Code shows scripted view count inflation.


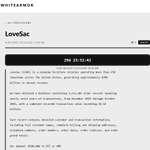
the WhiteArmor ransomware group has just listed LoveSac (@Lovesac) with a demand of $500,000 paid in Bitcoin or Monero.
They claim to have taken 1,113,285 order records spanning nearly seven years of transactions, from December 2019 through October 2026.


lfg

hashcat v8.0.0 released!
The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards.
Release notes: github.com/hashcat/hashcat/b…
Download: hashcat.net/hashcat/

CTI Updates retweeted

hashcat v8.0.0 released!
The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards.
Release notes: github.com/hashcat/hashcat/b…
Download: hashcat.net/hashcat/


the Falcon ransomware group has listed healthcare company Astrana Health. With claims of 738 gb of data taken.
"Our 738 GB extraction includes internal documents, regulatory audit reports, payer financial dispute trackers, internal operational readiness reviews, acquisition pipelines, detailed reimbursement tables, internal system evaluations, regulatory notifications, funds transfer records showing liquidity status, company financial statements, user credential lists, client contact lists, employee PII decks and much more. Contacted us then timewasted, re-attacks incoming."

update - Deloitte is no longer listed on The Gentlemen ransomware group DLS


the Anubis ransomware group has listed Ohio-based Newcomer Cremations, Funerals & Receptions with a claimed 289 gb of data taken.


the Emperador ransomware group has listed AB InBev with a $1,000,000 demand paid in BTC.
AB InBev is the world's largest brewer, headquartered in Belgium, known for Budweiser, Corona, and Stella Artois.
"We hold 329,244 AB InBev social-listening alerts, 2,510 corporate emails across all subsidiaries, 19K access logs, GBS portal records, internal PKI certificates, and 3.2GB of Azure blob assets."

update 🚨 lulagain has deleted both threads and all post replies related to selling the ShinyHunters and BF telegram channel BreachForumsNews for $3,000 and leaking BreachForums bf[.]st data 🤔👀


initial access broker selling Indonesian city gov VPN access. Fortinet SSL-VPN + cPanel access.

ALT AckLine threat actor and initial access broker selling access to an Indonesian government city. Fortinet SSL VPN access and cPanel access


