
Posts warning about cryptocurrency related scams
Joined February 2020
- Tweets1.1K
- Following133
- Followers86
- Likes270




3/3 🛠 C2 & Live Social Engineering:
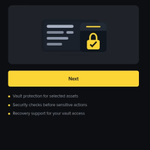
The site connects back to operators using real-time WebSockets (/ws) with an SSE fallback (/api/vault/events).
Operators track victim activity via /api/vault/audit and can dynamically trigger live chat or fake KYC popups to manipulate victims.
2/3 🔍 Attack Flow:
• Access Gate: Demands 6-digit code or auto-bypasses targets via ?sessionTransfer=
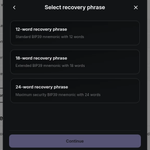
• Seed Harvesting: Steals 12-word recovery phrases via /api/vault/restore-seed
• Spoofed Dashboard: Fakes incoming balances and sets withdrawal hold timers to trap funds.
1/3 🚨 Newly registered phishing domain impersonating @binance Vault:
🌐 Domain: liveness-binance[.]com
📅 Registered: 12 October
The site serves a single-page application built to harvest credentials and siphon crypto assets. Technical breakdown 👇
@BinanceHelpDesk


Attacker Spender:0x464a32310881825508993415E21f58F0CA0C9C16
Target Token (Arbitrum USDT):0xFd086bC7CD5C481DCC9C85ebE478A1C0b69FCbb9
Exfil Channel ID: 1471216429197164617
Hosting Platform: Netlify (Site ID: 77482f08-ea9e-4f27-9611-8d8225934da3)
Delivery Evasion: Hardcoded failover to multiple public CORS proxies (allorigins[.]win, corsproxy[.]io, codetabs[.]com) if direct webhook POST requests are blocked or fail.
📡 C2 & Exfiltration Mechanics:
The drainer captures victim addresses and the split EIP-712 signature parameters (v, r, s):
Exfiltration Channel: Discord Webhook channel ID 1471216429197164617 (reported to Trust & Safety)
✍️ EIP-2612 Permit Abuse (_signTypedData):
Sscript requests off-chain Permit signature granting uint256 MaxUint256 allowance:
Target Token: Bridged USDT on Arbitrum One
Spender: Attacker address
Deadline: 1 Year
Victims see no immediate gas fee and zero on-chain transactions
⚙️ How the Drainer Works:
Aggressive Triggers: Uses timed setTimeout triggers (100ms/300ms) and binds click/touchstart across the entire document to immediately force network switching and sign requests.
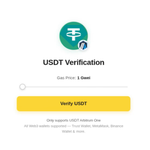
Decoy : Gas sliders and fake "Gwei" adjustments distract the victim
🚨 Phishing & Web3 Alert: EIP-2612 USDT Drainer on Arbitrum One
usdtverify[.]online
Phishing lure masquerading as an official "USDT Verification" page. The campaign leverages off-chain EIP-712 Permit signatures to steal funds gas-free without an upfront on-chain approve() alert

7/7 🌐 IOCs
• Lure: ledgerproporsal[.]com
• C2: vitmass[.]com
• IP: 188.253.11.18
• Cert CN: FRZGNU0NTD6EDPD.549121
6/7 🛡️ File Hashes (SHA-256)
• ZIP: 39438314580cd65e73c02d664df8183e218ec409021b327aff317df4c584fbec
• BAT Dropper: 1abf3f6ac62e8f1f390ecf062a9a154c10eaf3a2c8f2b962ad02e37e5a6ddab9
• ScreenConnect MSI: c0fb7911a2ca099632e39172a5dce9356d4aa960afa5b90bc8479bc31a6793e5
5/7 🌐 C2 & Infrastructure
Triage reveals the attacker's relay setup:
• Domain: vitmass[.]com
• Host IP: 188.253.11.18
• Cert CN: FRZGNU0NTD6EDPD.549121
188.253.11.18 exposes raw RPC ports (SAMR, Spooler), pointing to unfirewalled Windows client machine used as relay host
4/7 🪝 Silent ScreenConnect Backdoor
Concurrently, the script runs: msiexec /i SC_FeedbackTool.msi /quiet /norestart
rundll32 executes ScreenConnect.InstallerActions!FixupServiceArguments to configure a persistent Windows service, granting the actor remote control.
3/7 🎭 Decoy Smokescreen
The script runs SecondInstaller.exe, launching a genuine signed DocuSign Print Driver installer (WiX Burn).
The victim sees an authentic setup wizard to review the "proposal"—distracting them while the backdoor installs silently in the background.
2/7 📦 Delivery & Loader
@github
"Download Full Document ↓ .Zip" routes to:
github[.]com/sp908/1/releases/download/1/Ledger_Seedless_Proporsal.zip
Inside, the .bat dropper:
• Priv check via fltMC.exe
• Carves Base64 payloads via PS
• Verifies SHA-256 before exec
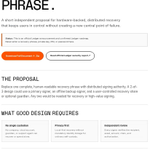
1/7 🧵 Fake @Ledger Proposal Drops ScreenConnect via DocuSign Decoy
A Web3 phish on ledgerproporsal[.]com lures targets with a fake proposal.
Runs a real DocuSign installer as a decoy while silently installing weaponized ScreenConnect RMM backdoor. 👇
@Ledger_Support

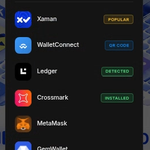
🚨 SCAM ALERT: XRPL wallet drainer targeting @XamanWallet
• Domain: ledger-allocation[.]app
• Lure: Spoofed "Xaman Airdrop / XRPL Allocation"
• Vector: Malicious Web3 modal targeting Xaman, WalletConnect, Ledger, Crossmark
Triggers malicious signing payloads to drain assets


The scam flow:
Prompts hardware selection (Nano, Flex, Stax)
Simulates a failed connection
Triggers "Use alternative method"
Prompts manual entry of 12, 18, or 24-word recovery phrases


🚨 SCAM ALERT: Campaign impersonating @Ledger_Support with a fake "2026 Exploit" advisory claiming $150M in losses.
• exploits2026-ledger[.]app
Lure: Claims older @Ledger devices have weak-entropy seeds via a fake MicroPython/Yasmarang bug to push a "risk scan."


