

Cybersecurity researcher/blogger/pentester. Try to tweet only technical/educational but occasionally post about https://teapawt.net/t.co/MTZoEINlWg 🙂
Indianapolis, IN
Joined October 2011
- Tweets3.9K
- Following871
- Followers2K
- Likes4K




𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

🚨 BREAKING: AI coding agent OpenCode was breached in what it calls a "large scale distillation attack".
OpenAI and Anthropic keys saved by 1.4% of its Console users have been exposed after intruders hit a legacy system.
One developer says their keys ran up $400+ overnight.


𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted
New Phishing Technique - Vaultjacking: One Captured PIN, the Entire Google Password Manager Vault phishu.net/blogs/blog-vaultj…

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

New phishing meta just dropped: Vaultjacking.
One captured 6-digit Google Password Manager PIN = attacker gets your entire synced vault. All passwords. All passkeys. Banking, crypto, email, work SSO - the whole jackpot.
Google's "convenient" sync layer turns out to be one weak PIN away from total compromise. No device needed, pure Adversary-in-the-Middle magic.
Remember when we were told password managers + passkeys would save us?
Turns out they just created a juicier single point of failure.
"Trust us with your passwords" - famous last words.
Stay safe out there.
phishu.net/blogs/blog-vaultj…
𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

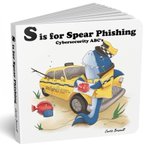
New board book from @CurtBraz is in!
“S is for Spear Phishing" cybersecurityabcs.com
#SisforSpearPhishing #CybersecurityABCs

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

My kid had to draw a favorite character from a book today and the choice was "M Is For Malware" by @CurtBraz! 😁

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

Tristan Morris welcomed guest host, Curtis Brazzell [@CurtBraz] on the April 14 GPS Live. Listen now to hear a discussion on "Juice Jacking", the EU AI monitoring, and the logistics of the leaked documents still making the news. Watch it here: okt.to/rNgK2W

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

In our latest GPS Live, Tristan Morris and guest host Curtis Brazzell [@CurtBraz] discuss the #CryptoAPI vulnerability reported by the NSA, #HIVE #ransomware group site seizure, and the ongoing Riot Games League of Legends source code auction + much more. okt.to/MrpFCR

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

Just made a minor update to MFASweep to cover the other conditional access device options and also added in a concise results summary.
github.com/dafthack/MFASweep

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

Combination of evilginx2 and GoPhish. github.com/fin3ss3g0d/evilgo…
𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

U.S. #cybersecurity agency CISA warns of active exploitation of a high-severity reflected/amplified DoS attack #vulnerability (CVE-2022-0028) in Palo Alto Networks' PAN-OS.
Read details: thehackernews.com/2022/08/ci…
#infosec #technews #hacking #cyberattack

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

"Functional illiterates" is a thing even in infosec community:
curtbraz.medium.com/exploiti…
TL;DR
Never run PoCs without checking
@CurtBraz
𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

Beware of this "fakesploit" perpetrating to be a PoC for CVE-2022-26809.
github.com/HellKnightsCrew/C…
Last year @CurtBraz carried out an experiment that taught me a valuable lesson to read code before running any POC. Today it pays off.

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

IT'S OPEN SEASON ON @OPENSEA AS SYSTEM HACKED, USERS TAKEN FOR MILLIONS IN ETHEREUM AND #NFTs
@Bitfinexed @SilvermanJacob @molly0xFFF @zachxbt @coffeebreak_YT

This Post is from an account that no longer exists. Learn more
𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

Found it two years ago. Not recently. That’s the point.

That feeling when you find the bug already and now it's in the wild :(
Here's the POC
github.com/gdabah/win32k-bug…
googleprojectzero.github.io/…
𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted
You can now scan for Log4Shell (CVE-2021-44228) using Burp Suite Pro or Enterprise Edition by installing @SilentSignalHU’s Log4Shell Scanner from the BApp Store.
portswigger.net/bappstore/b0…

𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

🎁 Looking for gift ideas for your kids? This coloring book by @CurtBraz is absolutely worth it! High quality, fun, and never too soon to get your kids interested in security… Cybersecurity ABC's Coloring Book amazon.com/dp/057896659X/ref…


𝐂𝐮𝐫𝐭𝐢𝐬 𝐁𝐫𝐚𝐳𝐳𝐞𝐥𝐥 retweeted

I'm excited to be able to let you all know that WPScan has been acquired by @automattic @jetpack.
I want to thank everybody that has ever supported me and believed in me.
jetpack.com/2021/11/04/jetpa…

