


Pinned Tweet
Today I'm going all in.
After an incredible run at Edge & Node, I'm leaving to focus full-time on @1clawAI.
Here's why:
We're about to hand the keys of the digital economy to AI agents. They'll hold API keys, sign transactions, move money, and act on our behalf... billions of them, then hundreds of billions.
And right now, most of them are running with secrets pasted into config files and zero guardrails.
That's the gap 1Claw exists to close.
Military grade vaults (HSM). Cryptographic key splitting (MPC). Policy engines that let agents act autonomously, but only within the rules humans set. Human-in-the-loop approvals when it matters. Full audit trails, always.
Private and secure AI focused infra in @AMD SEV-SNP (TEE) nodes. 🔒
Agents that are powerful AND accountable. That's the unlock for this entire wave of AI.
Our mission: secure the next 100 billion AI agents.
It sounds audacious. It should. The infrastructure layer for agentic AI is being built right now, and I believe 1Claw will be at the center of it.
Grateful for everything I learned at Edge & Node. Now it's time to grow.
1claw.co
docs.1claw.co
LFG 🦞

The @Railway hacked showed us, we don’t manage access to secrets properly.
Learn how @1clawAI can help!

The Railway Hack: A Look at 1Claw for Securing Keys and Mitigating Hacks xitter.cf/i/broadcasts/1lKQRWMNP…

The work our team has done over the past year is finally paying off for users.
We are securing the agentic economy together🦞
1Claw was featured on @hackernoon today.
Black October is here and @1clawAI is here to save the day. 🦞
hackernoon.com/1claw-builds-…

Security, security, security, security, security, security, security, security, security, security, security, security, security, security, security.
@1clawAI
Kevin Jones retweeted

if your private keys or openai keys were sitting in a @Railway variable, you’re probably rotating them right now
or you could’ve just used a vault that doesn’t hand the plaintext to the host
.@1clawAI exists for this exact reason

An urgent notice from the Railway team
blog.railway.com/p/security-…

Kevin Jones retweeted

hackers stole decrypted api keys of Railway users,
burning through ppls AI credits, drained crypto,
all before Railway alerted the public Oct 21.
their solution: rotate keys
all of them
fast.
AI boom made API keys a honeypot.
solution: key proxy + access control
Kevin Jones retweeted
railway just taught everyone why dumping API keys in env vars is a bad idea
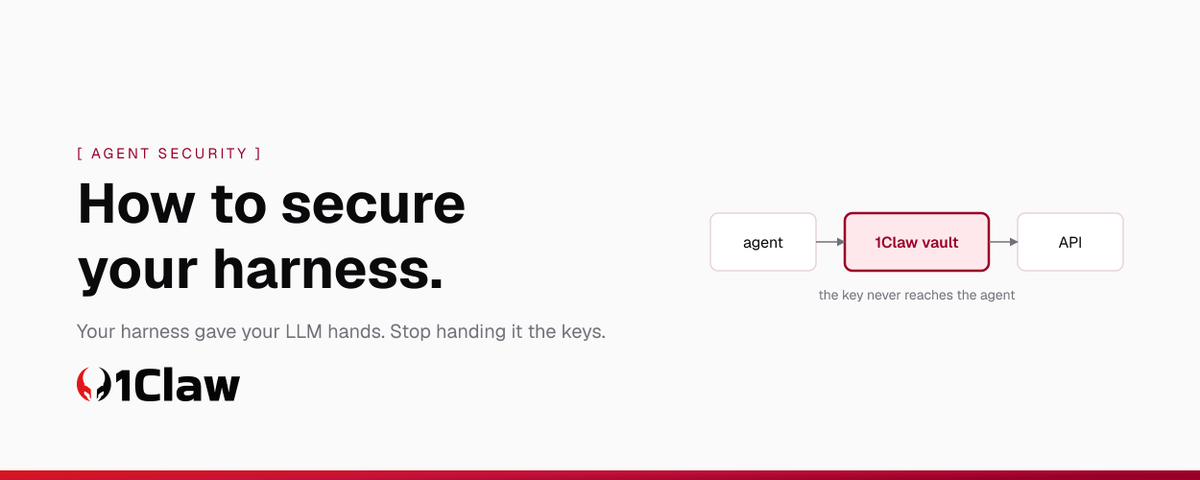
@1clawAI whole thing is agents get the secret at runtime and never hold it
timing is comical
The time is now to step up security. If you are shipping fast then look at @1clawAI
I built 1Claw to make it easy for developers to secure their applications.
You inherit all of the security and guard rails when you build on our API’s.
Tell your friends. 🦞

Kevin Jones retweeted
UPDATE: @1clawAI won 1st place in the pitch competition! 🏆
Our founder @DevSecOpz is presenting at Tokenize Las Vegas from @TigerMansionLV
Excited to represent @1clawAI and to be among legendary speakers like @iamscottpage, @michaelterpin, @mikealfred, @Player1Taco and many more.


Devs…. Let me help you out here.
Secrets management is hard. The truth is systems get breached, but environment variables should not live that close to the app infrastructure.
Token based access, policy enforced access is the answer.
With @1clawAI the breach would be as simple as clicking the rotate key button or a single API call 1Claws API.
Not to mention our impossible travel revocation and honey pots.
An urgent notice from the Railway team
blog.railway.com/p/security-…
What do you think of my socks? 👀
Thanks to @JulioMCruz, @Yelogamo and the rest of the @perk_os team for the gift 🦞
@1clawAI 🦞🦞🦞

Tokenize has been absolutely fantastic 👏
The next billion crypto users will be AI agents coming onchain.
Let’s build the agentic economy together.
Our founder @DevSecOpz is presenting at Tokenize Las Vegas from @TigerMansionLV
Excited to represent @1clawAI and to be among legendary speakers like @iamscottpage, @michaelterpin, @mikealfred, @Player1Taco and many more.
Kevin Jones retweeted

Extraction models turn human language into data your software can act on. We're bringing them to Sage.
Early access tomorrow for everyone who registers on @levantolabs by PT today. Demo 📺👇
Most software needs structured inputs. People communicate through emails, chats, tickets, contracts, and conversations.
Extraction models connect those two interfaces. You define the information your application needs, and the model identifies it in the text: people, companies, products, dates, amounts, descriptions, or requests.
Calling this “extracting stuff from documents” understates what developers can build with it.
Consider a customer message:
“The blue jacket arrived with a broken zip. Please send a replacement to 18 King Street.”
An extraction model can identify the product, defect, requested remedy, and address. Your application now has fields it can validate, look up, and pass to a tool.
A decision model can then evaluate whether the request qualifies for an automatic replacement, needs more information, or requires human review.
Extraction → decision → action.
Each stage has a defined responsibility. Extraction supplies the values. The decision model evaluates the available options against your policy and context. Your application validates the result and controls execution.
That separation matters for agent builders. You can inspect what the model extracted, test the decision independently, and control which actions are permitted.
Speed changes where this becomes useful.
At roughly 200 ms for extraction, developers can start putting language interpretation directly into interactive software:
• A support interface that fills relevant fields while an agent reads a ticket.
• A browser agent that extracts values from a message before populating a form.
• A find-in-page feature that highlights cancellation deadlines or product complaints, even when the text uses different wording.
• A workflow that turns an incoming email into validated tool arguments and evaluates the next action.
The opportunity extends to any application where someone currently reads a message, copies information into fields, and decides what happens next.
Developers can define the information they need and the decisions their software must make, then connect those outputs to existing functions.
We're bringing extraction and decision models together in Sage so builders can implement that flow.
Watch the demo below. Register on Levanto by PT today for early access tomorrow.
Excited for this one. My first crypto event almost 10 years ago was Tokenize as a volunteer, previously Coin Agenda.
Full circle I am speaking about the only tech that will move agents onchain securely.
See you there!
Our founder @DevSecOpz will be speaking at Tokenize and attending @money2020
The next billion crypto users will be AI agents. Is your stack ready to support then?

There is literally a Netflix documentary about the problems @1clawAI fixes with AI.
AI Gone Wild, check it out.
Can you say “product market fit”?