
Senior Security Engineer @Amazon. Ex Assistant Professor. Opinions are mine; not my employer's. DM is open. Author of xlmdeobfuscator and https://xitter.cf/t.co/eh1fMHMADE
Joined February 2018
- Tweets2.7K
- Following158
- Followers15K
- Likes3K







Malwrologist retweeted

Last year I wrote an article for the MISC magazine showing how to analyze maldocs with #oletools, msoffcrypto-tool, ViperMonkey and XLMMacroDeobfuscator. It is now available online:
English translation: connect-ed--diamond-com.tran…
French: connect.ed-diamond.com/misc/…
Malwrologist retweeted

Once again, we at @Google in collaboration with @WiCyS_SV are presenting an @Android app security & hacking workshop! Please spread the word and register at eventbrite.com/e/google-wicy…
#Android #Hacking #CyberSecurity

Malwrologist retweeted
This man deserves a chance...
This is baffling me that he couldn't get any gig in security
if I had any hiring power, I would definitely give him a chance

Malwrologist retweeted
David left out some key facts. He’s self taught, passionate, spends countless hours researching malware, has written multiple decoders in VB, has writing skills and published many blogs .

Malwrologist retweeted
#oletools 0.60.1 is out: this is a long overdue bugfix release, also improving oleobj (customUI and CVE-2021-40444 detection) and ftguess (more file formats)
Details: github.com/decalage2/oletool…
I also updated the install instructions: github.com/decalage2/oletool…

Malwrologist retweeted

I have created a PowerShell script to display information on trusted documents for Microsoft Office. It can be used for checking when and in which Microsoft Office document file a malicious macro was executed. github.com/nmantani/PS-Trust…

Malwrologist retweeted

We're #hiring multiple Threat Analysts for #MSTIC Threat Discovery team! Come join our dynamic threat intelligence team and help protect customers and disrupt threats.
aka.ms/threat-hunter-role 🔥
Malwrologist retweeted

Recent #Emotet downloaders use:
XLSX ➡ VBA ➡ batch ➡ PowerShell
Based on some great work by @DissectMalware, binary refinery now has a batch deobfuscator. Ripping out those C2s is easier than ever!
🏭 xlxtr | bat | carve -sd b64 | xtp url
🌐 github.com/binref/refinery


Malwrologist retweeted
Puzzled why a yara rule did or didn't match?
Let me introduce yaradbg.dev, a web-based #yara #debugger!
With #YaraDbg, you can see the:
1⃣ evaluation steps
2⃣ matched strings
3⃣ relationship among the rules
Malwrologist retweeted

Yooo! Can't wait to come back to #Kernelcon with @malwareforme to represent MSTIC as we talk about .appx malware and threat intelligence/detection engineering!


Malwrologist retweeted
Want to automate extracting URLs from #dridex ?
Take a look at: dridex_extractor.py github.com/DissectMalware/MD…
#dridex xlsb > hta > vbscript
#xlmdeofuscator + python wrapper for extracting urls in #vbs
bazaar.abuse.ch/sample/ce8e7…
DO NOT USE IT IN A PRODUCTION SYSTEM; USES EVAL

Malwrologist retweeted
Awesome!
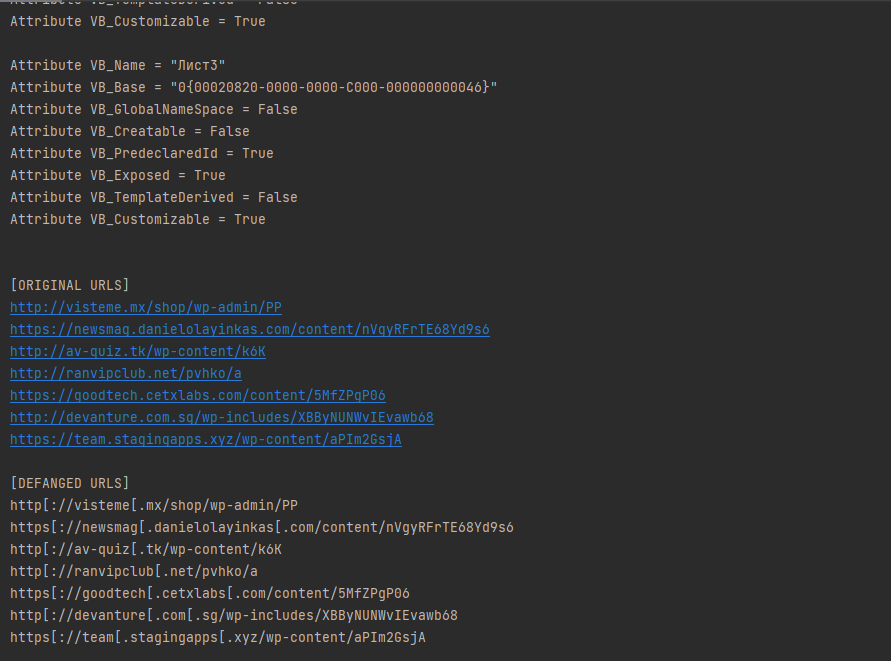
Changed the script so that it prints out the original URLs and also the defanged version...
python extractor[.py [file_path]
Malwrologist retweeted

CPython 3.9 and upwards has no support by decompilers yet (afaik).
But you can always analyse .pyc files by disassembling them. Python has its own module for that called dis.
This is how you do it, e.g., for a malwaremodule.pyc 👇
#Python #reversing

Malwrologist retweeted

My 8-year old, with whom I have never discussed the Twitter vocabulary, came and asked me how many followers I got on #Twitter. Show some love folks, and I can impress him tomorrow. #parenting
Malwrologist retweeted

The #OSDFCon agenda is now out! I'll be giving a talk on #MemoryForensics at this free #DFIR virtual conference on December 1st :-D
Don't forget to register!
osdfcon.org/2021-event/2021-…
#infosec #volatility #malwareanalysis #malware #memoryanalysis

Malwrologist retweeted
#WebCacheDeception Attack: #PathConfusion Never Sleeps!
Check out the new USENIX Security paper at onarlioglu.com/publications/…!
This paper along previous research papers (sajjadium.github.io/files/us… and sajjadium.github.io/files/ww…) show #PathConfusion potentials!
Malwrologist retweeted
Do you use #xlmdeobfuscator to analyze XLM, aka Excel 4.0, macros?
* Please take the poll and retweet for better reach
38%Never used, what's that?
3%Once used, didn't like it
23%Use occas, kinda like it
36%Use commonly, like it
66 votes • Final results Malwrologist retweeted
#CTF Challenges of the Week
CSAW: github.com/sajjadium/ctf-arc…
RCTF: github.com/sajjadium/ctf-arc…
TMUCTF: github.com/sajjadium/ctf-arc…
Tsuku: github.com/sajjadium/ctf-arc…
@osirislab @NYU_CSE @nyutandon @isislab @tsukuctf #CSAW21 #TsukuCTF #CTFtime #Pwn #Cybersecurity #InfoSec #CaptureTheFlag