The official account of the U.S. Department of War Office of the Chief Information Officer. Linking, replying/following does not = endorsement.

Pentagon, Arlington, VA
Joined September 2016
Transforming and securing the @DeptofWar digital ecosystem is an active, ongoing mission that requires continuous innovation. Today, @DoWCIODavies officially opened nominations for the 26th Annual CIO Awards to spotlight those who drive cybersecurity and empower our warfighters with data supremacy and decision dominance on the battlefields of today and tomorrow. Leaders are encouraged to nominate champion performers by October 30, 2026, 12:00 pm EST. Nominate here: dowcio.war.gov/About/Awards/ Read more at: dowcio.war.gov/In-the-News/A…
2
7
20
1,759
"It's just charging my phone." That single plug can compromise an entire @DeptofWar mission network. Threat actors weaponize everyday accessories via firmware exploits and payloads the second they touch a port. Keep your Government Furnished Equipment (GFE) locked down: - Never charge personal phones, watches, or devices via GFE USB ports. - Zero personal flash media or thumb drives—ever. - No unapproved personal Bluetooth or wireless accessories. - If it requires a driver download, it doesn't plug in. Cyber defense starts at the port. Be Brilliant at the Basics!
2
23
4
56
1,635
LTG Paul Stanton, @DoW_DISA Director and DCDC Commander, highlights a critical threat we all face every day Social Engineering. SI is making these attacks more sophisticated and harder to spot. Verify before you share and Be Brilliant at the Basics.
Our Director, @USArmy Gen. Paul T. Stanton explains how to spot social engineering and protect your data. Building this awareness is key to being #BrilliantAtTheBasics. For this week’s @DoW_CIO #CyberSecurityAwarenessMonth campaign we're urging you to stay vigilant & be secure.
1
6
17
804
Clear calendars, casual clothes, and incredible conversations. Last Friday, the @DeptofWar CIO Enterprise Technology Excellence (ETE) team gathered for an All-Hands focused entirely on connection, introducing new teammates, sharing unknown facts about one another, and collecting honest ideas on how we can make our everyday work experience even better. Proud to work alongside such an amazing, dedicated group!
7
1
21
690
Protecting @DeptofWar warfighters and ensuring they can accomplish the mission demands resilient and rehearsed operational technology (OT) incident response capabilities across the DIB. OT response is fundamentally different because these incidents directly impact physical infrastructure. Prepare – Contain & Mitigate – Recover – Integrate Lessons Brilliant at the Basics highlights two valuable resources to bolster partner readiness: - @DC3Forensics's DIB Vulnerability Disclosure Program: For mitigating public-facing software vulnerabilities. - @CISAgov ICS310 Training: For building OT threat-detection capabilities. Links: DIB-VDP: dc3.mil/Missions/Vulnerabili… CISA ICS310: cisa.gov/resources-tools/tra…
1
5
1
23
914
Calling all USPACOM/DoW cyber personnel: Ready to help shape the future of cyber at the @DeptofWar? If you're in the USPACOM area, join DoW CIO Cyber Workforce leadership at the Hilton Hawaiian Village on Oct. 26 from 10:30 am – Noon. This is a great opportunity to connect directly with DoW CIO Cyber Workforce leadership, share your vision, and discover upcoming pathways for career growth and skill development in our community. For more information, go to: events.afcea.org/TIP26/Publi… Bring your ideas and energy—we can’t wait to connect!
12
24
917
In 2026, smartwatches, optical smart glasses, and fitness trackers have become second nature. They optimize our health, streamline notifications, and log our daily habits with incredible precision. However, every sensor tracking your pulse or step count opens a digital door. This Cybersecurity Awareness Month, it’s time to take a closer look at the physical and cyber-attack surfaces strapped directly to our wrists and faces. Be Brilliant at the Basics and make it a priority to secure your wearables.
4
12
32
1,060
@DoW_CIO retweeted
🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗 go.dhs.gov/5Hi
61
735
63
2,235
270,081
@DoW_CIO retweeted
We recommend Cisco users disable the Smart Install (SMI) auto-loading feature on all NSS and DIB network devices to mitigate exploitation by remote attackers. Have you taken this action? Read more: media.defense.gov/2019/Jul/1… #CybersecurityAwarenessMonth
45
749
84
2,902
161,565
@DoW_CIO retweeted
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
1,303
10,847
2,834
70,332
12,446,168
If you’re a Defense Industrial Base partner looking for practical, no cost or low-cost cybersecurity resources, you don’t have to look far. In our latest Brilliant at the Basics Cybersecurity Awareness Month reel @DeptofWar CISO Aaron Bishop shares how our IT and OT Top 10 lists can help your organization strengthen resilience, manage cyber risk, and protect critical systems. Watch the reel and explore the whole collection. dowcio.war.gov/BrilliantBasi…
1
11
26
827
The portal for the 26th Annual CIO Awards closes October 30, 2026, at 12:00 PM EST. Across @DeptofWar teams are hardening networks, pushing mission software to the edge, and out-innovating adversaries in real time. Component Commands, Services, Departments and Agencies, and inter-governmental defense partners – don’t miss this chance to ensure your highest-performing cyber and IT personnel receive the recognition they earned. Details and submission portal: dowcio.war.gov/About-DoW-CIO…
4
12
698
Be Secure. Cybersecurity does not stop at the screen. Physical security helps protect personnel, facilities, our technology ecosystem, and data from actions that can create serious risk. A misplaced badge, unlocked workstation, unattended device, or unsecured document can create an opening for unauthorized access. You should always secure devices, badges, and sensitive materials before stepping away from your workstation or leaving a facility. Do not prop doors open or allow others to follow you into controlled spaces without using their own authorized credential. Whether you are a warfighter, member of the @DeptofWar workforce, or Defense Industrial Base, strong physical security is a key part of being Brilliant at the Basics.
11
25
791
DoW CIO commends the collaborative effort of @NSACyber, @NIST, and @CISAgov in delivering practical guidance for managing the risks associated with super intelligence control incidents. We are in an unprecedented period of technological advancement, and these practices offer a strong opportunity to strengthen resilience, improve incident readiness, and better protect the systems that support national security. We encourage all network defenders and those safeguarding National Security Systems across the @DeptofWar and Defense Industrial Base to read the report. media.defense.gov/2026/Oct/1… xitter.cf/NSACyber/status/211251…
NSA joined @NIST and @CISACyber in releasing guidelines for managing SI control incidents. Organizations utilizing SI are encouraged to adopt these practices. Read the joint report: media.defense.gov/2026/Oct/1…
2
15
1
36
1,608
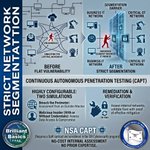
A flat network is a vulnerable network. Logically separating business IT networks from critical operational technology (OT) systems helps limit lateral movement and contain a potential intrusion before it disrupts core operations. Eligible small DIB businesses can also explore @NSACyber's Continuous Autonomous Penetration Testing (CAPT), an AI-powered capability that enables internal-network penetration testing at no cost and without prior expertise. NSA’s CAPT is designed to help eligible small businesses assess internal networks and validate remediation. Learn more at nsa.gov/About/Cybersecurity-…
1
9
31
1,042
This week’s @DeptofWar Brilliant at the Basics Cybersecurity Awareness Month campaign theme is Be Secure. In our latest reel, Deputy CIO for Operations Christine Condon shares a simple, yet important tip regarding government-furnished equipment. Watch the whole reel to learn more.
6
1
15
1,018
Don't fall for Harry The Hamster's tricks. Social engineering is one of the most effective tools used by our adversaries. AI has increased the sophistication of the attacks and the data available to the attackers. Every member of the @DeptofWar team must be constantly vigilant to counter these tactics. Indicators of a social engineering attempt include: •Unsolicited requests for personal or financial information. •A sense of urgency or pressure to act quickly. •Suspicious email addresses or unusual grammar. •Promises that seem too good to be true. Verify before you trust to be Brilliant at the Basics!
5
19
873
Congratulations to Farah Pathan, the DoW CIO’s program analysis and IT asset management lead, on receiving the Leading for IMPACT Women in Leadership Award! The award recognizes women whose leadership, mentorship, and mission focus make a meaningful difference across the federal community. Farah’s recognition reflects the expertise and commitment she brings to the @DeptofWar CIO team every day. We’re proud to have her on our team.
3
5
14
791
Insider threats are among our most complex and hard to recognize risks because they are deliberately designed to avoid detection. During Cybersecurity Awareness Month, and every month, all @DeptofWar personnel and industry partners must be vigilant every day. Spotting the subtle indicators of recruitment or network exploitation protects our Information and Operational Technology. Know the signs: changes in behavior, unexplained affluence, accessing information not needed for their job, and more. If you See Something, Say Something. Be Brilliant at the Basics!
12
1
35
1,068
Today, Honorable Kirsten Davies also welcomes Mr. Kenneth Nienhuser to his new role as the Deputy Chief of Staff. He assumes this position after serving as the lead for the office’s industry outreach, coordinating executive-level engagement processes, strategic communications, and decision-support materials. A Marine Corps veteran, Mr. Nienhuser brings a wealth of experience supporting senior @DeptofWar leaders to the position.
1
5
18
1,009
Today, I am signing The Vice President’s Pledge to Protect Americans from Fraud to reaffirm a shared commitment to protect Americans from fraud. Cyber fraud threatens individuals, families, and organizations alike. The @DeptofWar OCIO remains focused on strengthening cybersecurity to protect the ecosystem that powers our warfighters. During Cybersecurity Awareness Month, the @DoW_CIO’s Brilliant at the Basics campaign reinforces practical habits that can reduce fraud risk—from protecting credentials and verifying requests to recognizing suspicious messages. I encourage everyone to stay vigilant and apply these simple safeguards to help protect personal information, the Department, and the mission.
1
2
1
7
532