

🇧🇷🇷🇸🇮🇱🏴☠️🍵
...
Joined August 2026
- Tweets925
- Following146
- Followers41
- Likes7.8K




Pinned Tweet
Love these books and here is why:
* Jeff's book is a gem, the "alien notation" and the challenge is a fun start and then it goes on into the practical stuff.
* Mitnick's book is legendary as it taps into the most frequent point of failure in cybersecurity: humans.
* Bluefox is a masterpiece written by a giant in ARM security, something to be consulted carefully and with attention. Absolutely love it.
* Windows Internals is simply a must have for everyone wishing to understand the intricacies of the OS. Much love for Pavel Yosifovich (also my teacher at TrainSec).
What are the books that you're reading now and leaving a mark on your learning?

3
658
Finally arrived! 😍 Going to dig It.
Co-Authored by the super badass @sherrod_im

༺༒ Луди зец ༒༻ retweeted

We get it. OAI/Ant want a regulatory moat.
LLMs are just probabilistic auto complete. All they do is answer the question of “given a sequence of tokens, what is the next most likely token?”
So please explain to me how we’re getting from that to “33% chance it overthrows the govt in 12 months” for anything other than getting it regulated to make it harder for competitors to enter the market.
We live in a yap epidemic.

༺༒ Луди зец ༒༻ retweeted

A lot of people are confused about the conflicting information coming from OpenAI about their plans for AI safety.
This point by @KelseyTuoc does a good job clarifying what’s going on.

I don't have a reputation to spare so I can speak why this AI hype doesn't resonate with me:
I view models as a collection of tools of varying quality that are extremely good at fulfilling contracts. The deeper issue is the assumption that goes underneath a lot of the hype (ASI, AGI..whatever): that better token prediction is evidence for the Computational Theory of Mind (it isn't). The more immediate damage I see is people outsourcing their own reasoning capabilities to models and then slowly but surely losing whatever critical thinking they have.
(running for cover)😱

I feel people have stopped sharing their real opinions on here, and instead everyone is participating in some informal prediction market where the currency is their reputation. Especially on AI.
It sucks. I want to know what people really think because I want to be exposed to alternative perspectives. But in this degenerate prediction game everyone is playing, there's no room for that. If you post something that diverges from the mainstream, you're basically gambling your entire credibility.
I find myself moderating my own posts, even. I don't want to say something too strongly and then have it thrown in my face. So my more unique opinions, the ones where I don't think what everyone else thinks, I don't share.
I'm tired of it. I don't learn anything on here because everyone is just like "ASI by 2028" because someone else said it and they don't want to be seen as an AI skeptic. Please stop. Stop treating every opinion as a bet you can win against someone. All it's doing is reducing the quality of discourse by forcing everyone to shut up and conform.
1
2
109

༺༒ Луди зец ༒༻ retweeted

Enquanto deputados do PSOL do alto do seus gabinetes promovem antissemitismo nas redes sociais contra turistas israelenses no Brasil, o povo de Itacaré, na Bahia, se manifesta em solidariedades aos turistas judeus.
PSOL e antissemitismo caminham lado a lado.

༺༒ Луди зец ༒༻ retweeted

November Black Friday on trainsec!
All individual courses are 40% off!
trainsec.net/cybersecurity-c…


༺༒ Луди зец ༒༻ retweeted

If you manage Active Directory today and are considering your career options, and you’re not retiring soon, here’s my advice.
Get a job as an internal security resource. A generalist role. Find a company and a team you really jive with.
Your super power should be that you actually understand IT.
Networking. Windows, Linux, Mac. Infrastructure. Backups. Hypervisors. Firewalls. Technical Support.
Having a strong IT background is a super valuable skill when transitions to cybersecurity.
🚨🚨🚨

HEADS UP re: RAILWAY INCIDENT: Josh @joshmanders needs some help with incident response so I am posting this on his behalf and with his permission asking for those of you in my orbit who are qualified, and many of you are, to reach out to him with serious intent about helping him with the recent Railway incident.
Triage.
Log analysis.
Correlation.
Josh will give you the specifics.
And no trolling or I'm going to lose my shit on you. This is a serious tweet and inquiry.
Make me proud.
P. S. Retweet far and wide please.
78
🎯🎯🎯
Yes we should talk about this so everybody is very clear on what it is you have said and what I've said and what others have said here.
This behavior is illegal, an actual crime was committed, and the people who ran these agents are 100% responsible and accountable for what the agent did.
STOP RUNNING AGENTS WITH FULL PRIVS AND WITHOUT OVERSIGHT.
AND DON'T HIRE IDIOTS WHO PORTSCAN YOUR COMPETITORS AND PASS IT OFF AS TESTING.
You're not allowed to do that!
64


༺༒ Луди зец ༒༻ retweeted

A portion of security complains about being heard and another portion are elitist. That manager, director, GRC finding gets you headcount and tools. All that takes influence. It might be harder to influence an entire culture and navigate political barriers than find a vuln.
Outside the bubble no one gives a shit about security. If they did we wouldn’t need sanctioned security awareness programs that everyone hates. We might not have mountains of IT debt. Stay humble.
༺༒ Луди зец ༒༻ retweeted

We have a golden opportunity here to do the funniest thing and respond to everything Sam writes on the internet with pictures of our RAM. Like take a selfie with it. And I mean like everything this dude writes needs to just be filled with pictures of RAM. Just flood his feed with it!

OpenAI CEO Sam Altman says it’s “quite terrible” that people have so much DRAM sitting in their own PCs instead of being used in data centers.
“Everyone have a bunch of the world’s limited supply of DRAM sitting in their own computer. And be used 5% of the time,”
He argues that cloud data centers should make better use of limited memory supplies instead of people running AI models locally.


😂😂😂😂😂😂. Todo mundo gosta de se sentir "único" e "especial", acreditar que tem um superpoder ou algo que faça se destacar dos demais.
As armadilhas : o pedantismo, o efeito Dunning-Kruger, a indução vulgar e o perigo de ficar só arrotando grandeza no seco, por puro medo de mergulhar e se molhar.

superdotação é uma desgraça. Existe uma discriminação absurda na vida adulta quando a maioria tá satisfeito em ser pouca merda e a gente que é superdotado sempre tá lá em cima e não aceita esse sistema. Daí começa o boicote.
queria mesmo era ser burra q nem uma porta
54
Do people really believe LLMs are "alive and conscious" and have any agency other than token prediction aimed at fulfilling contracts?

The impact of 0days is irrelevant to my claim of LLMs being pattern matching machine that just predict tokens. 0days are not novel scientific discoveries, they are variants of existing known code flaws, which fits well within pattern matching + token prediction.
"Uncountable 0days of insane impact" what 0days and what impact? Is there some onslaught of insane AI-powered 0day attacks in the wild I'm not aware of?
"High quality healthcare opinions?" Wat. Please tell me you are not consulting ChatGPT instead of a doctor about your health.
"In April you claimed they were awful at reverse engineering when hundreds of researchers were using opus 4.6 to RE software and find vulns." In April I was using Opus 4.6 to RE software and find vulns. It was absolutely awful at RE, and the number of vulns it (or anyone else) found is not a refutation of that. You do not need world class RE capabilities to find bugs and my metrics for high quality reverse engineering is a little higher than "can it find vulns?" (a random number generator can find vulns).
"In June you claimed threat actors weren’t getting faster with ai and anyone who has used ai at all in the last year knows this is clearly false by the simple fact that these models help development happen way faster."
This is a statement of opinion. You have provided zero data to substantiate this claim. Your implication that AI being good at finding exploits establishes evidence for this is a non-sequitur. Most threat actors don't use exploits at all, and plenty (likely the majority) don't use AI in any transformative capacity at all. Automated scripts still remain 1000s of times faster than AI inference.
I'm gonna be honest man, I was expecting to at least have to concede "yeah, you got me there" on some points, but this whole argument was a waste of my time. It just screams "I only understand vulnerability research and I'm just going to shove everything into the 'AI can find vulns' box because it's the most nuance I'm capable of".
So since I feel bad at your piss poor attempt to make a coherent argument, I'll concede some points to myself: I was actually surprised by just how many CVEs came out of throwing a bunch of AI compute at the problem. I expected a decent amount, but nowhere near as many as actual.
22
༺༒ Луди зец ༒༻ retweeted

The wild thing about people who work in any aspect of OffSec (AppSec, pentesting, red teaming, or whatever else) is how often people assume that translates directly into being good at crime.
It’s also always been entertaining watching people come from pentesting backgrounds with minimal concern for opsec/stealth move into red teaming, where those things matter because getting caught can burn weeks of effort.
Now take that up another level with actual crime, where screwing up could mean spending years in jail. You’re managing infrastructure and everything else that comes with maintaining opsec under those stakes, plus the ever so fun part of figuring out how to actually monetize your hacks, convert the proceeds to cash, and get that money into your hands.
There are levels to this whole thing, and it’s easy to assume the rest is simple when you’re playing with little or no risk.
༺༒ Луди зец ༒༻ retweeted
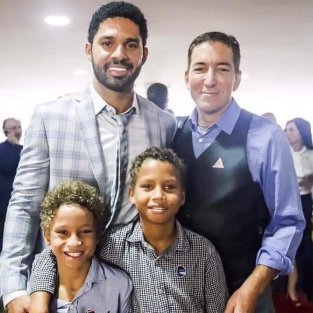
One more amazing thing about Brazil and Lula's campaign:
The NYT today has a gushing profile of a Congressman named @AndreJanonesMG, who became the face of Lula's campaign, its chief communication strategist. and -- as a result of admittedly innovative though extremely creepy digital strategies -- the greatest hero of the Brazilian left. But listen to what the article doesn't mention:
Just 2 years ago -- not 20 years ago or 10 years ago, but 2 years ago -- Janones got caught committing one of the most despicable crimes imaginable: he forced his Congressional staff employees to transfer a portion of their (quite low) monthly public salary to him as a condition for keeping their jobs. The money he stole from his workers didn't go to his campaign: it just went to enrich himself, into his pocket,.
He got caught when the employees secretly taped him angrily telling them they should stop complaining. When all this emerged, the left-wing members of Congress loyal to Lula -- who, remember, claims to lead a movement of workers! The name of Lula's party is the Workers Party -- protected him from all consequences from stealing the salary of his workers.
The pro-Lula judiciary let Janones confess guilt and simply pay back the money that he stole. And yet this doesn't bother anyone on the Brazilian left. Janones has become a beloved figure overnight among left-wing celebrities and is now one of Lula's closest allies. The NYT profile doesn't even mention this in their gushing profile.
In the scheme of Brazil's authoritarianism, it's not the biggest issue, but to me it's one of the most revealing about what frauds these people are:
