







EDIMO PEREIRA retweeted

FBI正式点名朝鲜:币安超60亿美元被盗,背后竟是一个活跃十多年的黑客网络!
美国FBI正式将币安超60亿美元资产被盗案归因于朝鲜黑客行动“TraderTraitor”。
美国特勤局、国税局刑事调查部门也参与追踪,发现黑客正将被盗资产主要兑换成ETH,接下来可能通过DeFi和即时兑换服务继续洗钱。
美国司法部此前曾将以下三起轰动全球的案件与朝鲜Lazarus黑客网络联系起来:
2014年:入侵索尼影业,造成大规模数据泄露。
2016年:从孟加拉国央行盗走8100万美元。
2017年:发动WannaCry勒索软件攻击,波及全球大量计算机系统。
FBI通缉名单上还有一个人,Park Jin Hyok(朴镇赫)。他被美国指控参与上述黑客犯罪网络,2018年遭起诉,能说韩语、英语、中文,最后已知所在地是朝鲜。
目前FBI已经公开数百个关联钱包地址,并要求DeFi、跨链节点及兑换服务商协助拦截。
60多亿美元被盗只是第一阶段,接下来围绕资金冻结、跨链转移和洗钱的攻防,可能比最初的攻击还复杂。
🤖 Made with AI


The FBI is releasing information advising the Democratic People's Republic of Korea (North Korea) was responsible for the theft of more than $6 billion USD in virtual assets from cryptocurrency exchange, Binance, on or about October 29, 2026. The FBI refers to this specific North Korean malicious cyber activity as "TraderTraitor."
The FBI, together with partners at the USSS and IRS-CI, has observed TraderTraitor actors converting stolen assets primarily into Ethereum (ETH). It is expected these assets will then be further laundered by converting them using DeFi and instant swap services as they prepare them for further laundering stages.
How You Can Help:
FBI, USSS, and IRS-CI are urging private sector entities including THORNode operators, RPC node operators, instant exchanges, DeFi services, blockchain analytics firms, and other virtual asset service providers to block transactions with or derived from addresses TraderTraitor actors are using to launder these stolen assets.
A list of addresses associated with this activity is available here: fbi.gov/investigate/cyber/al…

ALT FBI public service announcement with Department of Justice seal in the background on a gold gradient.
EDIMO PEREIRA retweeted

PCC é alvo de operação em Santa Catarina e no Paraná; assista #BastidoresCNN
EDIMO PEREIRA retweeted

这张脸,被美国 FBI 通缉了整整8年!背后牵出三起震惊世界的黑客攻击!
他叫朴镇赫(Park Jin Hyok),朝鲜籍程序员,出生年份可能是1981年或1984年,会朝鲜语、英语和中文。
美国司法部指控,他参与的朝鲜黑客组织“拉撒路集团”(Lazarus Group),涉嫌制造了三起轰动全球的网络攻击:
① 2014年:入侵索尼影业,窃取并泄露大量机密资料。据指是为了报复讽刺金正恩的电影《采访》。
② 2016年:攻击孟加拉国中央银行,成功盗走8100万美元。
③ 2017年:制造席卷全球的 WannaCry 勒索软件,感染数十万台电脑,英国医院系统也遭到严重冲击。
2018年,美国正式公布他的身份并发出通缉令。
2021年,美国司法部扩大起诉范围,指控他与另外两名朝鲜黑客参与全球金融网络犯罪,企图窃取、勒索超过13亿美元。
美国调查人员认为,这些黑客与朝鲜军事情报机构侦察总局有关,曾在中国等地开展活动。
截至2026年10月31日,朴镇赫仍在 FBI 通缉名单上,最后已知所在地是朝鲜。


FBI가 수배 중인 북한 해커 박진혁.
1981년 또는 1984년생으로 추정.
북한 국적에 한국어·영어·중국어를 구사하는 것으로 알려짐.
미국 법무부가 연루 혐의를 제기한 사건만 해도
① 2014년 소니픽처스 해킹
② 2016년 방글라데시 중앙은행 8,100만 달러 탈취
③ 2017년 전 세계를 마비시킨 워너크라이 랜섬웨어
북한 정찰총국과 연계된 조직에서 활동한 것으로 지목됐고, 2018년 미국에서 기소됨.
FBI가 실명과 얼굴까지 공개하고 수배 중인데 마지막으로 알려진 소재지가 북한이라 신병 확보도 쉽지 않다고 함.
※ 위 사건들은 미국 수사당국이 제기한 혐의이며, 박진혁 개인의 모든 범행이 확정된 것은 아님.


EDIMO PEREIRA retweeted
人在中国,身价千万美元!美国 FBI 公开悬赏通缉3名中国黑客,背后牵出中共国安、公安系统!
最高悬赏1000万美元,3人悬赏金额合计高达1400万美元!他们的姓名、照片和最后已知居住地,全部被 FBI 公之于众。
🔴 关天烽,1994年出生,最后已知居住四川
悬赏1000万美元!
被控参与攻击约8.1万台 Sophos 防火墙。他任职的四川无声信息技术有限公司,曾向中国公安部提供服务。
🔴 尹可成,1986年出生,最后已知居住上海
悬赏200万美元!
涉嫌入侵美国政府机构、科技企业及国防承包商,窃取敏感数据,并通过地下渠道出售。
🔴 周帅,1979年出生,最后已知居住上海
悬赏200万美元!
网名 Coldface,涉嫌与尹可成合作,向包括安洵在内的中国客户出售被盗数据。
这三人背后,究竟是谁?
美国司法部在2025年公布的起诉文件中明确指控:中国国安部、公安部利用民间黑客及网络安全公司,执行情报收集、商业间谍和针对海外异议人士的网络攻击。
其中,安洵公司的主要客户就包括中国国安部和公安部。
表面上是民间黑客,背后却牵出一整套与中共情报和公安系统有关的网络攻击产业链。
这也是美国调查人员提出的核心指控。三人的相关刑事责任仍有待司法程序认定。


这张脸,被美国 FBI 通缉了整整8年!背后牵出三起震惊世界的黑客攻击!
他叫朴镇赫(Park Jin Hyok),朝鲜籍程序员,出生年份可能是1981年或1984年,会朝鲜语、英语和中文。
美国司法部指控,他参与的朝鲜黑客组织“拉撒路集团”(Lazarus Group),涉嫌制造了三起轰动全球的网络攻击:
① 2014年:入侵索尼影业,窃取并泄露大量机密资料。据指是为了报复讽刺金正恩的电影《采访》。
② 2016年:攻击孟加拉国中央银行,成功盗走8100万美元。
③ 2017年:制造席卷全球的 WannaCry 勒索软件,感染数十万台电脑,英国医院系统也遭到严重冲击。
2018年,美国正式公布他的身份并发出通缉令。
2021年,美国司法部扩大起诉范围,指控他与另外两名朝鲜黑客参与全球金融网络犯罪,企图窃取、勒索超过13亿美元。
美国调查人员认为,这些黑客与朝鲜军事情报机构侦察总局有关,曾在中国等地开展活动。
截至2026年10月31日,朴镇赫仍在 FBI 通缉名单上,最后已知所在地是朝鲜。

EDIMO PEREIRA retweeted

Every machine on Earth that runs Python is about to become one computer.
Compute has borders. We just removed them.
Portal moves a running Python job between any two machines. Any cloud, any GPU, any CPU. Mid-run.
Everything before hit the wall, so we built a portal.


EDIMO PEREIRA retweeted

🚨 GLOBAL STOCK MARKETS COULD FACE A MASSIVE POLITICAL AND ECONOMIC SHOCK THIS WEEK.
The U.S. midterm elections, critical jobs data, major central bank decisions and earnings from some of the biggest AI companies are all coming in the next 5 days.
And this is happening while tech stocks are already crashing and hedge funds are aggressively cutting their exposure.
Here's what's coming:
Monday, Nov 2:
• ISM Manufacturing PMI: 54.7 expected.
• Apple earnings: $113.4B revenue expected.
• Palantir earnings.
Tuesday, Nov 3:
• U.S. midterm elections: Control of Congress at stake.
• Australia rate decision: Hike to 4.85% expected.
• JOLTS job openings.
• AMD, Arista, Astera Labs, Shopify and Eaton earnings.
Wednesday, Nov 4:
• ADP employment: Just 65K jobs expected.
• ISM Services PMI: 54.8 expected.
• Eurozone inflation: 3.9% expected.
• Qualcomm, Arm, AppLovin, Coherent, Uber and Datadog earnings.
Thursday, Nov 5:
• Bank of England rate decision.
• U.S. jobless claims and Challenger job cuts.
• Microchip, Lumentum, Cloudflare and Airbnb earnings.
Friday, Nov 6:
• U.S. October jobs report: 60K jobs expected after just 29K in September.
• Unemployment rate: 4.2% expected.
• Michigan consumer sentiment: 47.3 expected, near record lows.
But the biggest risk is how all these events could hit markets at once.
Markets are pricing roughly an 80% chance of another Fed rate hike in December.
A weak jobs report could raise fears about the U.S. economy, while stronger inflation data could make it harder for the Fed to ease policy.
Meanwhile, the midterm elections could reshape Washington's approach to AI, just as AMD, Arm, Qualcomm and other major chip companies report earnings.
Any disappointing guidance could put even more pressure on an already struggling AI trade.


EDIMO PEREIRA retweeted
Assista ao vídeo e descubra como o C-390 Millennium continua expandindo sua presença global. A primeira entrega do C-390 à Força Aérea do Uzbequistão é um importante marco nos esforços de modernização do país e torna o Uzbequistão o primeiro operador da aeronave na Ásia Central.
EDIMO PEREIRA retweeted

Writer Aaron Langmaid is urging Australia’s Defence Department to release its records on the 1966 Westall UFO incident, nearly six decades after more than 200 people reported seeing UFOs over Melbourne, Australia.
reddit.com/r/UFOs/comments/1…

EDIMO PEREIRA retweeted

8 years ago we set out to build a protocol that “was supra-national and could resist the coercions of nation-states to offer a decentralised trading venue”
I’ve left since long ago
But now we are about to find out.
God speed thornode operators. God speed. If the proctor goes offline then it is done for. Pack it up and leave.
EDIMO PEREIRA retweeted

JP (THORChain founder) stated this seems to be @THORChain’s ultimate test.
No PR spin. No compliance excuses.
The founder who stepped away years ago drew the red line: withstand the nation-state pressure test or admit the cypherpunk thesis was a marketing LARP and shut it down.
hold the line, it means a lot to many people.

8 years ago we set out to build a protocol that “was supra-national and could resist the coercions of nation-states to offer a decentralised trading venue”
I’ve left since long ago
But now we are about to find out.
God speed thornode operators. God speed. If the proctor goes offline then it is done for. Pack it up and leave.
EDIMO PEREIRA retweeted

扒了一下 FBI 通缉名单,发现一个很有意思的人:朴镇赫(Park Jin Hyok)。
这个朝鲜黑客,早在2018年就被美国司法部起诉,至今仍是 FBI 通缉对象。
他的背景相当不简单:
1981年或1984年出生,朝鲜国籍,会韩语、英语和中文。
2014年:涉嫌参与索尼影业(Sony Pictures)大规模网络攻击。
2016年:涉嫌参与孟加拉国央行8100万美元盗窃案。
2017年:涉嫌参与WannaCry勒索软件攻击,导致全球大量计算机系统瘫痪。
2018年:美国司法部正式起诉,指控其参与上述网络犯罪。
美国调查人员认为,他所在的黑客组织与朝鲜侦察总局(RGB)有关。
最有意思的是,美国不仅掌握了他的姓名、照片和部分活动信息,还公开通缉,但至今难以将其逮捕。
因为他最后已知的所在地,就是朝鲜。
从索尼影业,到央行SWIFT系统,再到全球勒索软件,朝鲜网络行动人员被美国指控涉及的攻击目标跨度非常大。


EDIMO PEREIRA retweeted
017. Three major cyberattacks, three completely different targets
teapawt.net/alphahunter000/status/…

扒了一下 FBI 通缉名单,发现一个很有意思的人:朴镇赫(Park Jin Hyok)。
这个朝鲜黑客,早在2018年就被美国司法部起诉,至今仍是 FBI 通缉对象。
他的背景相当不简单:
1981年或1984年出生,朝鲜国籍,会韩语、英语和中文。
2014年:涉嫌参与索尼影业(Sony Pictures)大规模网络攻击。
2016年:涉嫌参与孟加拉国央行8100万美元盗窃案。
2017年:涉嫌参与WannaCry勒索软件攻击,导致全球大量计算机系统瘫痪。
2018年:美国司法部正式起诉,指控其参与上述网络犯罪。
美国调查人员认为,他所在的黑客组织与朝鲜侦察总局(RGB)有关。
最有意思的是,美国不仅掌握了他的姓名、照片和部分活动信息,还公开通缉,但至今难以将其逮捕。
因为他最后已知的所在地,就是朝鲜。
从索尼影业,到央行SWIFT系统,再到全球勒索软件,朝鲜网络行动人员被美国指控涉及的攻击目标跨度非常大。
EDIMO PEREIRA retweeted

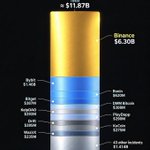
The FBI has confirmed North Korea was behind the $6.3 BILLION Binance hack. But the country's crypto heists go back years.
> On October 29, more than $6 BILLION in crypto was stolen from Binance.
> The FBI identified the operation as "TraderTraitor", a North Korean cyber operation.
> The stolen funds are now being converted primarily into ethereum:native with investigators expecting the hackers to move them through DeFi and instant-swap services.
> And if you think this came out of nowhere, North Korea has been targeting crypto platforms for years.
> In March 2022, hackers linked to Lazarus Group stole approximately $620 MILLION from the Ronin Network, one of the biggest crypto hacks at the time.
> A year later, in September 2023, the group struck again, stealing $41 MILLION from crypto betting platform Stake.com.
> One name that keeps coming up in investigations into North Korea's hacking operations is Park Jin Hyok.
> Park is a North Korean programmer on the FBI's Most Wanted list.
> The US government accused him of being part of Lazarus Group and participating in a hacking conspiracy involving major cyberattacks and cryptocurrency theft.
> Then came another massive target.
> In May 2024, North Korean hackers stole $308 MILLION from Japanese exchange DMM Bitcoin.
> And in February 2025, the FBI attributed the $1.5 BILLION Bybit hack to North Korea's TraderTraitor operation.
> Now, Binance has joined that list, with more than $6 BILLION stolen but about $3B were frozen with the help of industry partners.
From Ronin to Stake, DMM Bitcoin, Bybit and now Binance, North Korean hackers have stolen BILLIONS of dollars from the crypto industry.


EDIMO PEREIRA retweeted

A tecnologia muda o mundo. A pergunta que fica é o que ela muda em nós, e é sobre isso que este livro foi escrito.
A Era da Abundância é um livro sobre o nosso futuro, não sobre a tecnologia. E a edição brasileira tem um capítulo só sobre o Brasil.
EDIMO PEREIRA retweeted

I went through the on-chain data on the $6.3B Binance hack. What most people are posting is WRONG, and the smartest part of this attack is getting no coverage…
The main drain took 24 SECONDS. Not 20 minutes. About $2.7B left two Binance Ethereum wallets in under half a minute.
How they got in:
Binance says a DevOps engineer's laptop "may" have been compromised. They also say there is no evidence a private key leaked. Both can be true, and that's the interesting part.
An EIP-7702 delegation needs a valid signature from the wallet. If you control a service container that is already authorised to request signatures, you never need the key. You just ask the signing service to sign for you. Same shape as Bybit, where attackers hit a developer machine at Safe.
The transaction itself:
A type-4 tx carrying 50 separate EIP-7702 authorizations, all for the Binance 14 hot wallet, all pointing at the same attacker contract.
Only ONE landed. Nonce range 18,914,775 to 18,914,824.
They didn't know the wallet's exact nonce, so they sprayed a range and let one hit. Blockaid caught this.
The part nobody is talking about:
Within 3 minutes the attacker supplied 60M USDT to Aave as collateral and borrowed 19,762 wETH against it. About $45M.
Tether froze the address right after. Aave froze the markets 46 minutes later.
TOO LATE. They had already turned freezable stablecoins into ETH nobody can touch. Marc Zeller confirmed the position is overcollateralised so Aave isn't out anything.
Where it stands:
Frozen, per ZachXBT: over $2.83B. Roughly 1,767M USDT, 823M USDC, 40.5M RLUSD, 27.8M USD1, 29,934 WBETH.
Still with the attacker: 197,460 ETH, about $436M, plus $122M across 15+ tokens including LINK, AAVE, WBTC and ONDO. Another $19.5M on Arbitrum and $24M on Avalanche.
The wallet was funded with 0.1 ETH out of Tornado Cash. The delegation was removed and the wallet's code was empty again by 01:20 UTC.
The number that actually matters:
$6.3B stolen, about $3B frozen. That's a $3.3B hole.
SAFU took in $1B of Bitcoin earlier this year. It covers less than a third. At least $2.3B comes out of Binance's own corporate balance sheet.
Withdrawals went down at 22:15 UTC, almost two hours after the drain started.
Watch for the updated Proof of Reserves. That's the only document that tells you what Binance actually has left.
I will keep researching the subject, and I will keep you guys updated.
If you own ANY amount of crypto, make sure you're following me so you don't miss any important updates.
A lot of people will regret not following me…
EDIMO PEREIRA retweeted
The FBI named the unit behind the $6.3B Binance hack. TraderTraitor, not Lazarus.
North Korea has stolen roughly $6.75B in crypto since 2017. They nearly matched nine years of work in a few hours on Thursday.
And they're doing it with fewer attacks every year, not more. In 2025 they took 76% of all exchange theft value worldwide while running 74% fewer operations than the year before.
Same unit hit Bitget for $351.6M in September and Bybit for $1.5B last year. The two largest crypto hacks in history both belong to them.
The timing nobody flagged: the US Treasury sanctioned North Korea's fake remote IT worker network on October 28. Binance got drained on October 29.
The UN estimates those fake workers alone bring the regime $250M to $600M a year, separate from anything they steal.

I went through the on-chain data on the $6.3B Binance hack. What most people are posting is WRONG, and the smartest part of this attack is getting no coverage…
The main drain took 24 SECONDS. Not 20 minutes. About $2.7B left two Binance Ethereum wallets in under half a minute.
How they got in:
Binance says a DevOps engineer's laptop "may" have been compromised. They also say there is no evidence a private key leaked. Both can be true, and that's the interesting part.
An EIP-7702 delegation needs a valid signature from the wallet. If you control a service container that is already authorised to request signatures, you never need the key. You just ask the signing service to sign for you. Same shape as Bybit, where attackers hit a developer machine at Safe.
The transaction itself:
A type-4 tx carrying 50 separate EIP-7702 authorizations, all for the Binance 14 hot wallet, all pointing at the same attacker contract.
Only ONE landed. Nonce range 18,914,775 to 18,914,824.
They didn't know the wallet's exact nonce, so they sprayed a range and let one hit. Blockaid caught this.
The part nobody is talking about:
Within 3 minutes the attacker supplied 60M USDT to Aave as collateral and borrowed 19,762 wETH against it. About $45M.
Tether froze the address right after. Aave froze the markets 46 minutes later.
TOO LATE. They had already turned freezable stablecoins into ETH nobody can touch. Marc Zeller confirmed the position is overcollateralised so Aave isn't out anything.
Where it stands:
Frozen, per ZachXBT: over $2.83B. Roughly 1,767M USDT, 823M USDC, 40.5M RLUSD, 27.8M USD1, 29,934 WBETH.
Still with the attacker: 197,460 ETH, about $436M, plus $122M across 15+ tokens including LINK, AAVE, WBTC and ONDO. Another $19.5M on Arbitrum and $24M on Avalanche.
The wallet was funded with 0.1 ETH out of Tornado Cash. The delegation was removed and the wallet's code was empty again by 01:20 UTC.
The number that actually matters:
$6.3B stolen, about $3B frozen. That's a $3.3B hole.
SAFU took in $1B of Bitcoin earlier this year. It covers less than a third. At least $2.3B comes out of Binance's own corporate balance sheet.
Withdrawals went down at 22:15 UTC, almost two hours after the drain started.
Watch for the updated Proof of Reserves. That's the only document that tells you what Binance actually has left.
I will keep researching the subject, and I will keep you guys updated.
If you own ANY amount of crypto, make sure you're following me so you don't miss any important updates.
A lot of people will regret not following me…