This vast cosmos is filled to the brim with potential 100xs. ✨️ Crypto. AI. 🛸✨️ And the related macro. (El Paso stuff as well, I guess. )
⧝El Paso⧝
Joined April 2016
- Tweets18.5K
- Following2.1K
- Followers1.9K
- Likes33.9K



✨El_Crypton₳ut✨⧝ retweeted

Candlestick analysis can be simple:
Long lower wick = dip buying
Long upper wick = rejection
Wicks on both sides = rejection
No wicks = control


✨El_Crypton₳ut✨⧝ retweeted

币安刚刚发布了初步调查报告,梳理了他们是如何被朝鲜黑客,盗取了 60 多亿美金。
某位币安软件工程师,在求职网站上挂着简历,结果一位自称项目总监的人,主动联系他,说有个潜在岗位想聊聊。
对方安排了一位 HR 跟他视频面试,真人露脸。为了让他放下戒心,这位 HR 还把自己的社交账号发给了他,上面有他本人的生活照和视频,看着就像真实存在的人。
然后到了第二轮面试,对方换到一个常用的聊天软件上,跟一位自称是这家公司 CEO 的人聊,但其实公司是假的。
等面试快结束时,对方让他下载一份代码题,作为技术测试,结果这位币安员工,在工作电脑上下载运行了它。
这份代码,在安装环节偷偷自动执行,把电脑上一个正常的开发工具 pyenv,换成了带木马的版本,然后跟黑客的服务器连上,还会自己清理痕迹。
就连币安当时的杀毒软件,也没查出来。
从这台电脑开始,朝鲜黑客一步步渗透内部,摸进了交易所的钱包系统,一个多月后币安被盗了 60 多亿美金。
关键是现在领英上,还有一群币安在职员工的信息,这些估计都是朝鲜黑客的潜在欺诈对象。


✨El_Crypton₳ut✨⧝ retweeted

🚨ALERT: GitBook says an attack using AI agents compromised infrastructure credentials on Nov 2.
GitBook is a platform teams use to create and publish documentation and knowledge bases.
The attacker may have accessed integration tokens, Git Sync secrets, API tokens and questions visitors asked GitBook Assistant.
GitBook revoked all customer API tokens and replaced its infrastructure credentials and secrets.
Users SHOULD now:
- Rotate GitBook and connected third-party tokens and secrets.
-Re-authenticate the GitBook MCP server.
The app, API and published docs are back ONLINE, though some services remain degraded.
Of note, GitBook found no evidence that content was modified.


✨El_Crypton₳ut✨⧝ retweeted

.@emurgo_io are a$$holes.
That’s the tweet.

Wait whut…
Did EMIRGOROI just try to influence a an outcome after pledging to abstain since destroying all their credibility by shipping malicious code to their SecondFi wallet.
Is this really happening @phillip_pon
I’m sorry but you have lost me.
Malicious exit unexpected


✨El_Crypton₳ut✨⧝ retweeted

STOP WASTING HOURS TRYING TO LEARN REA.
REA Team put together one practical roadmap with tutorials, real investigations, GitHub repos, books, research papers and free courses.
START HERE:
1. REA Official Repository github.com/morluto/rea
2. REA Official Website rea.tools
3. Installation & Agent Setup github.com/morluto/rea/blob/…
4. Your First REA Investigation rea.tools/first-investigatio…
5. REA Guides rea.tools/guides/
6. Guided MCP Prompts github.com/morluto/rea/blob/…
Install: npx rea-agents@latest setup
WATCH & FOLLOW ALONG:
1. How To Use REA To Clone Any Software In Minutes — youtube.com/watch?v=FnB9tHKB…
2. REA + Pi Coding Agent Tutorial datacamp.com/tutorial/revers…
3. Ghidra Tutorial for Beginners youtube.com/watch?v=OFAxXXcL…
4. Frida for Android Reverse Engineering youtube.com/watch?v=GHh9P-Dy…
5. pwn.college Reverse Engineering pwn.college/intro-re-pwn~593…
6. Malware Unicorn RE101 malwareunicorn.org/workshops…
REAL REA INVESTIGATIONS:
1. Notes Export rea.tools/first-investigatio…
2. Notion Clipboard rea.tools/showcase/notion/
3. DX-Ball Reconstruction rea.tools/showcase/dx-ball/
4. Aegis APK rea.tools/showcase/aegis/
5. TH04 Bullet Patterns rea.tools/showcase/th04/
GITHUB REPOS:
1. REA github.com/morluto/rea
2. Awesome Reverse Engineering github.com/morluto/awesome-r…
3. REA Gems github.com/sqwu/rea-gems
4. Awesome Reverse-Engineered github.com/alexgaoth/awesome…
5. Ghidra github.com/NationalSecurityA…
6. JADX github.com/skylot/jadx
7. Frida github.com/frida/frida
8. ILSpy github.com/icsharpcode/ILSpy
9. x64dbg github.com/x64dbg/x64dbg
BOOKS:
1. The Ghidra Book, 2nd Edition nostarch.com/ghidra-book-2e
2. Reverse Engineering for Beginners go.yurichev.com
3. Practical Binary Analysis nostarch.com/binaryanalysis/
4. Practical Malware Analysis nostarch.com/malware
5. The Android Malware Handbook nostarch.com/androidmalwareh…
6. Reversing: Secrets of Reverse Engineering wiley.com/en-us/Reversing%3A…
RESEARCH PAPERS:
1. LLM4Decompile arxiv.org/abs/2403.05286
2. AutoDecompiler arxiv.org/abs/2606.16162
3. SALT4Decompile arxiv.org/abs/2509.14646
4. Decomperson usenix.org/conference/usenix…
5. DIRTY usenix.org/system/files/sec2…
6. Automatically Attacking Software RE Agents arxiv.org/abs/2605.30667
7. Does Reverse Engineering Need a Bigger Model? rea.tools/blog/reverse-engin…
FREE COURSES & PRACTICE:
1. OpenSecurityTraining2: x86-64 Assembly p.ost2.fyi/courses/course-v1…
2. pwn.college: Reverse Engineering pwn.college/intro-re-pwn~593…
3. pwn.college: Reversing Hell pwn.college/reversing-hell/
4. Malware Unicorn RE101 malwareunicorn.org/workshops…
5. Nightmare github.com/guyinatuxedo/nigh…
6. RPISEC Modern Binary Exploitation github.com/RPISEC/MBE
7. OWASP Mobile Application Security mas.owasp.org
BEST ORDER TO LEARN:
install REA → Notes Export → Notion → CTF binary → Aegis APK → DX-Ball → then Ghidra, assembly and papers


REA hit #1 on GitHub trending, and most people still run it inside a single chat
Split it into 4 subagents and one command takes a program you own from sealed binary to a tested rebuild with a match rate
Set it up once, aim it at the next one:
✨El_Crypton₳ut✨⧝ retweeted

🚨 A MASSIVE WAVE OF CYBERATTACKS IS HITTING THE INTERNET.
October 2026 has seen a shocking number of major cyberattacks, data breaches and serious security flaws.
And some of the biggest names in technology, banking and internet services are involved.
Here's what's been reported in just one month:
• PHP2Shell: Critical flaws in software used by nearly 70% of websites.
• eMudhra: Eight digital certificate keys compromised. One private key was literally the number 4.
• California: Sensitive public school student data stolen, including disability records.
• Railway: Customer API keys and database credentials potentially exposed.
• Zeabur: Major breach followed by an announcement that the company is shutting down.
• LiteLLM: Hackers planted password-stealing malware in a widely used AI tool.
• GitLab: A critical 10/10 security flaw affecting software versions dating back to 2014.
• SBI: Nearly 3,900 customer records exposed.
• Onamae: Up to 26,739 customer servers potentially affected by malware.
And these are only some of the incidents reported in October.
Several involve software used by thousands of businesses, meaning a single security failure could put many more companies at risk.
Some businesses may not even know their systems have been exposed, leaving customer data and important services vulnerable to further attacks.


✨El_Crypton₳ut✨⧝ retweeted

Honestly I couldn't f*ckin believe it actually happened
Stanford data research team just leaked the secret way they process data
your coding pipeline is waiting 2 seconds per row for a model to say "refund" or "bug"
that's what happens when you send a frontier LLM to label a table. it reads, it thinks, it writes a paragraph, and you parse one word out of it.
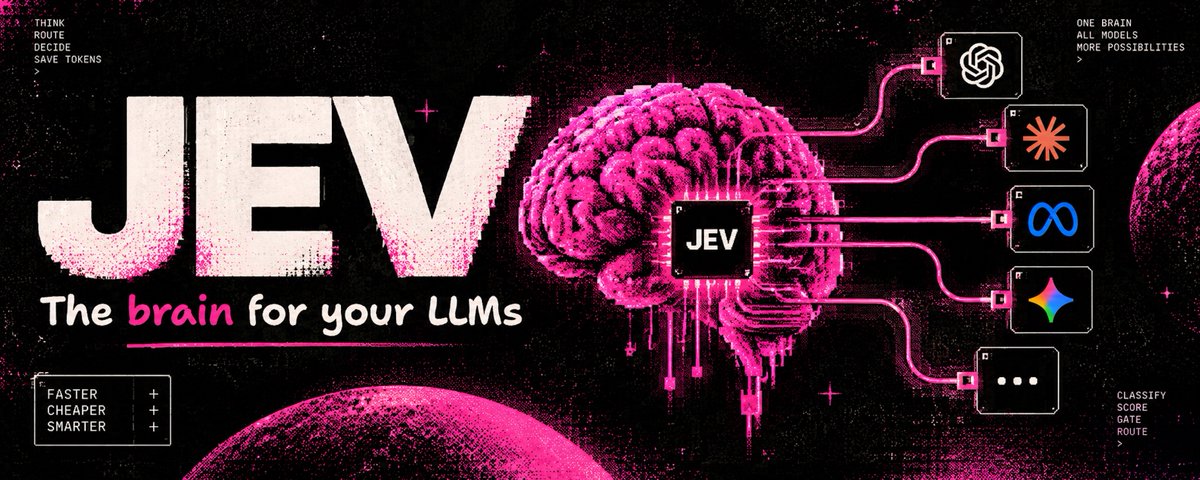
They stopped doing that. They use Jev.
Jev doesn't write. it picks from the labels you gave it, returns a probability, and moves to the next row.
someone benchmarked it on 500 examples from Stanford's SST-2 dataset against Claude Sonnet 5:
-> accuracy: 95.4% vs 95.6%
-> median latency: 376 ms vs 2,076 ms
-> throughput: 18.2 rows/s vs 3.5 rows/s
-> cost per 1,000 rows: $0.015 vs $0.80
same answer quality. ~5x faster. ~50x cheaper.
and it runs where your data already lives:
-> jev4pg: 41 Jev operators inside PostgreSQL. filter, extract, rank and match rows in SQL, with parallel execution and repeated values sharing one judgment
github.com/Sheltercosmo/jev4…
-> duckdb-jev: a native DuckDB extension that packs up to 1,000 judgments into one request and streams them straight from a query
github.com/prasanthj/duckdb-…
-> jevframe: a .jev accessor for pandas and Polars. ask a question about every row, get a normal column back
github.com/ktaletsk/jevframe
the database still does the math. Jev only takes the part where something has to be understood.
the catch: it's not magic on every dataset. on 4-topic news it scored 84% vs Claude's 90%, and a fine-tuned BERT beat both. measure it on your own data first.
> let SQL do the joins.
> let Jev do the judgment.
> let the frontier model handle what's actually hard.
bookmark this before your next labeling job eats a weekend to process.