

Elliot by alias, security by profession. Focusing on fintech & security research.
/home/user
Joined June 2023
- Tweets6.5K
- Following927
- Followers5.4K
- Likes251K







Pinned Tweet
Los únicos trabajos que no va a poder reemplazar la IA y la robótica son aquellos con mayor conexión humana, no necesariamente porque estas tecnologías no puedan desempeñar esas funciones, sino porque sencillamente la gente prefiere interactuar con otros humanos.


Sobre el caso Binance, se dice que el robo se debió a un acceso no autorizado desde la laptop de un DevOps (aún no se confirma cómo), pero la pregunta más legitima es, ¿cómo o por qué un DevOps tendría acceso privilegiado a parte de la tesorería de una exchange de talla mundial?
Chainalysis divulgó una brecha por "offensive agentic techniques" (primera vez que una empresa usa este término), expuso nombres, emails y roles de usuarios, sin evidencia de acceso a datos de investigaciones o credenciales.
bleepingcomputer.com/news/se…

ElliotSecOps retweeted

El futuro de la #InteligenciaArtificial no está predeterminado. Al tratarse de una tecnología desarrollada por seres humanos, su futuro depende de las decisiones que tomemos. Por lo tanto, tenemos la responsabilidad de orientar, modificar y, cuando sea necesario, rechazar sus aplicaciones. Un sistema fiable al servicio del ser humano es más valioso que un sistema extraordinariamente potente cuyas consecuencias no puedan preverse ni controlarse adecuadamente.

ElliotSecOps retweeted
INTEL: Crypto hack tracker Chainalysis reportedly hacked, exposing customer names and emails

🧵 Con respecto al hack de Binance:
No fue un exploit clásico. El atacante usó EIP-7702 (la nueva delegación de Ethereum) para hacer que la hot wallet “Binance 14” ejecutara su propio código malicioso.
Primero financió gas con Tornado Cash desplegó el contrato, obtuvo una firma..

Binance probes potential $5.8 billion crypto-theft hack
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

ElliotSecOps retweeted
The only thing that stops a bad guy with an abliterated LLM is a good guy with an abliterated LLM.
ElliotSecOps retweeted

Introducing Kimi K3.1 Pro: our most capable 3T-class open-weight model.
🔹 1M-token context, 2.8T total / 104B active params (MoE), Multimodal.
🔹 Full-project coding: games in Unreal, Unity & Godot.
🔹 Excels at parametric 3D modeling in Blender & CAD.
🔹 More reliable at finance work: Accurate modeling with hallucination down by 65%.
🔹 Matching the strongest proprietary models across coding, agentic and knowledge benchmarks.
Kimi K3.1 Pro and K3.1 Pro Highspeed (2–3× faster) are now live on Kimi.ai, Kimi Work, Kimi Code, and the Kimi API.
Open weights by Nov 4, 2026.
🔗 API: platform.kimi.ai
🔗 Tech blog: kimi.ai/blog/kimi-k3-1-pro

ElliotSecOps retweeted

Today we're releasing abliterated-model-large-v2.
Based on GLM-5.3, which is #3 on Terminal-Bench 4.0 (behind only Opus 5 and Fable), with 2× the cyber exploitation of 5.2.
We abliterated and hosted it so it does the offensive cyber, red teaming, and agent testing work other models refuse to do.
- US-hosted
- FP8
- 1 million context window
- Zero input/output prompt retention
Live now. 🧵

Hay mucha alarma por la posibilidad de que la IA ataque las criptos, pero internet y la banca usan un cifrado todavía más débil. La IA no necesita romper la criptografía de Bitcoin para hacer daño, con los datos filtrados ya se potencia el phishing, la ingeniería social, etc.


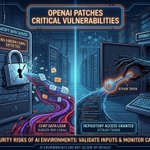
Esa vulnerabilidad de PHP que está causando estragos se detectó con GPT-5.6 Sol 👀

OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordinated…

Ahora con la IA se genera codigo más rapido que nunca, pero a su vez estamos revisando más codigo de lo que nunca antes lo habíamos hecho.
Se suponía que la IA iba a reducir nuestro trabajo, sin embargo siento que nunca antes había trabajado tanto en mi vida.
ElliotSecOps retweeted

software engineering is so back.
> people are reading books again.
> every line of code is being read carefully.
> fundamentals are cool again.
> architecture and system design are back in focus.
> nobody is fighting over frameworks anymore.
> understanding why something works matters again.
> code reviews matter more than lines of code shipped.
> debugging is becoming a superpower again.
> technical judgment matters more than typing speed.
> engineering is about thinking again, not just coding.
ElliotSecOps retweeted

Writing is a form of thinking.
So don't let AI do it all for you.


Apena hice este post OpenCode sufrió un acceso no autorizado afectando aproximadamente al 1.6% de sus usuarios, que a pesar de ser una cantidad pequeña, sigue siendo grave, pero sería injusto decir que OpenCode ha sido negligente cuando hoy los ataques son mucho más sofisticados

No hace falta ser objetivos de un APT para sufrir un acceso no autorizado o una brecha de datos, incluso un equipo de pocas personas con un enjambre de agentes haciendo reckoning día y noche (y un poco de ingeniería social) basta para encontrar un acceso oculto
Hasta el FBI cayó por un zero day, no por mala configuración, sino por software de terceros sin parche. Ni el equipo más capaz del mundo se salva cuando hasta los grupos más chicos de ciberdelincuentes operan con swarms de IA a costo marginal.
bleepingcomputer.com/news/se…
