







0x972Ops retweeted

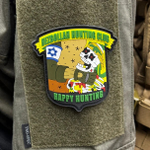
Choosing a new Hezbollah leader is a lot like choosing a new pope.
When one gets picked you'll see a giant plume of smoke in the sky.
0x972Ops retweeted

😂, but sad...

ALT Source: https://www.reddit.com/r/USMC/comments/1ak0mt7/when_you_let_the_data_nerds_near_the_ordnance/
0x972Ops retweeted

Sleight of Hand is out today. Written with @kristindelrosso and published through @ACGlobalChina, our report ties China's new vulnerability system to its offensive teams and explains how we got to Hot Zero Day Summer. 🧵
atlanticcouncil.org/in-depth…

0x972Ops retweeted

CVE-2023-40477: WinRAR Code Execution Vulnerability securityonline.info/cve-2023…

0x972Ops retweeted
"[I]dentity in this new era is rapidly becoming a super-human problem, according to RSA."
Great write-up from @helpnetsecurity detailing the #RSAIDIQ report and what it means for the future of #cybersecurity ⬇️
helpnetsecurity.com/2023/08/…


0x972Ops retweeted
Google's 2022 Year in Review of in-the-wild 0-days is out! 4 key takeaways:
🤖N-days function like 0-days on Android
⚡️0-clicks and new browser mitigations drive down browser 0-days
👯Over 40% of itw 0-days are variants
💥Bug collisions are high
#itw0days
security.googleblog.com/2023…

ALT Bar graph of the number of in-the-wild 0-days detected per year. Data comes from: https://docs.google.com/spreadsheets/d/1lkNJ0uQwbeC1ZTRrxdtuPLCIl7mlUreoKfSIgajnSyY/edit#gid=1662223764


0x972Ops retweeted
הבורסה שלנו בהשוואה לבורסות מובילות בעולם.
מבט על השבוע האחרון, החודש האחרון, מתיחלת השנה ושנה לאחור.
תסתכלו על השבוע האחרון, איזה פער בינינו לבין העולם.
תסתכלו על הנתונים מתחילת השנה.
הממשלה שורפת את הערך של הכסף שלנו ופוגעת לכולנו בעתיד.

0x972Ops retweeted

⚠️ Ivanti has released an update to address a vulnerability (CVE-2023-35078) in Ivanti Endpoint Manager Mobile (EPMM), formerly known as MobileIron Core. Patch ASAP. Read more at cisa.gov/news-events/alerts/…

0x972Ops retweeted

hookbot_source
This repository contains a few leaked files of HookBot. To ensure it is not used for malicious purposes, certain files have been modified and restricted from execution.
github.com/0xperator/hookbot…
#malware #cybersecurity #infosec #reverse

0x972Ops retweeted

APT41 hackers target Android users with WyrmSpy, DragonEgg spyware - @serghei
bleepingcomputer.com/news/se…

0x972Ops retweeted
Evading EDR, by Matt Hand, gives an inside look look at how Endpoint Detection & Response agents pinpoint adversary activity. Learn the ways each sensor component collects data, how to design an EDR, & how to evade one. Pre-order at 30% off w/ code GOTCHA: nostarch.com/evading-edr

0x972Ops retweeted
CISA shares free tools to help secure data in the cloud - @serghei
bleepingcomputer.com/news/se…

0x972Ops retweeted

Evil-WinRM - the ultimate WinRM shell for hacking/pentesting
hakin9.org/evil-winrm-the-ul…
#infosec #cybersecurity #redteam #pentest #pentesting #hacking #hackers #coding #opensource #Linux #windows
