

Hacktron is an autonomous vulnerability hunter for ambitious engineering teams. Built by world-class security researchers. Powered by one principle: PoC || GTFO
Latent Space
Joined April 2025
- Tweets250
- Following13
- Followers10.4K
- Likes251






Pinned Tweet
Introducing Hacktron Review: an AI security reviewer for your pull requests.
It understands your whole codebase, builds a threat model, takes your feedback, and catches exploitable vulnerabilities before they reach production.
Try for free: app.hacktron.ai
🚨 PHP2Shell: two critical PHP vulnerabilities are now patched.
PHP has fixed CVE-2026-109618 and CVE-2026-109619 (CVSS 9.2). Both can let an unauthenticated attacker run code on the server.
If you run PHP: update every runtime serving web traffic (check the version behind PHP-FPM or Apache, don’t rely on the CLI version alone), restart PHP workers, and review activity from at least 17 October onwards.
Full breakdown:
hacktron.ai/blog/php2shell?u…

Hacktron AI retweeted

i think people are confusing vulnerability disclosures with active exploitation, and thats causing a lot of unnecessary panic. most of these are researchers finding and fixing bugs before someone fucks things up.
oct 21:
php2shell: disclosure, reported in august
node.js: disclosure, patched, reported around august?
gitlab: disclosure, patched, reported a few months back
railway: security breach
litellm: supply-chain compromise
sbi: data exposure
emudhra: disclosure
oct 20:
plex2shell: disclosure + active exploitation
siteguard: actively exploited vulnerability
siemens: actively exploited vulnerability
oct 19:
- ovhcloud cli: supply-chain compromise
oct 17:
- opencode: security breach
We tried to hack our way into @Lovable's office to start a sales conversation.
We couldn’t break Lovable directly, so we went one layer down: @supabase.
Race condition → superuser → shell → root → the keys to other databases in the region.
$25K. Patched in a day.
The full write-up: hacktron.ai/blog/supapwn

Remote Code Execution in LibreOffice!
Update to the latest version, especially if you're using LibreOffice in web applications. We found few and reported!

A stranger writes a GitHub issue.
A developer clicks “Code with agent mode.”
Copilot reads the issue and does what the stranger said.
VS Code had patched this. We found a way around the patch.
Your agent can’t tell your instructions from an attacker’s.
The full breakdown: hacktron.ai/blog/rce-in-vsco…
An attacker uploads an image. How far can they get?
One library. Slack, OpenAI, Meta, GitHub Enterprise, and more.
Our HEIF Heist research traced attack paths through libheif, a library used to decode HEIC photos.
AI is making exploit development faster. Attackers don’t wait for your next security assessment.
Read the full research:
heif-heist.com/?utm_source=x…

Hacktron AI retweeted

I spoke with @LiveOverflow of Hacktron for a behind-the-scenes look at how they hacked OpenAI's infrastructure, what he's building with his cybersecurity education platform at @hextreeio and some very emotional personal news that he shared.
Building a Next.js replacement in a week is impressive.
Finding serious security flaws in it is a reminder of something else:
speed and security are two different problems.
Hacktron found 24 validated issues in vinext, including 4 critical ones. @Cloudflare patched them.
AI is making software faster to build.
Security still needs to be deliberately engineered.
Full breakdown → hacktron.ai/blog/hacking-clo…
No more AI. It's SI.
hacktron.si

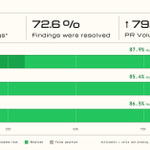
Review volume grew 79% MoM in September.
More volume usually means more noise. Not at Hacktron. 86.5% of evaluated findings were actionable.
Can't get this with an API wrapper and a .md skills file.

Hacktron AI retweeted

New YouTube video! We are looking at the dependency chain and how long it can take for security fixes to travel upstream.
This is why OpenAI was vulnerable to a 1-year-old vulnerability.

We found a flaw in Cluely.
it's built to be invisible. that's the selling point.
but think about it. an app nobody can see is also an app nobody can check.
it had your screen and your mic. one missing guard meant a single click could've handed both to a stranger. no warning, no prompt.
(found and patched back in 2025.)
AI apps are getting deeper access every month, and almost nobody reviews what they're shipping.
that's what we do. we check before it's watching you.
full breakdown here: hacktron.ai/blog/hacking-clu…
🎉 New Customer Story | Hacktron x Nopan
In payments, every pull request is a risk decision.
Nopan already combined peer review with automated testing, static analysis, and dependency scanning.
Hacktron adds context-aware review that surfaces complex, non-obvious risks in the relevant code without slowing delivery.
👇 Read the story: hacktron.ai/customer-stories…

