#jad (@J222ad) profile picture

OSINT

Joined September 2020
Photo by #jad (@J222ad)Photo by #jad (@J222ad)Photo by #jad (@J222ad)Photo by #jad (@J222ad)Photo by #jad (@J222ad)Photo by #jad (@J222ad)Photo by #jad (@J222ad)Photo by #jad (@J222ad)Photo by #jad (@J222ad)Photo by #jad (@J222ad)
The Inferno Drainer toolkit exploits smart account upgrades in metamask by initiating a deceptive transaction that bundles both the account upgrade itself and malicious actions (like draining funds). This is enabled solely by the lack of a trusted dapp whitelist.
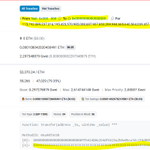
⚠️分析了下,这个 EIP-7702 的钓鱼利用确实有点创意,这个新钓鱼技巧来自熟悉的钓鱼团伙 Inferno Drainer。 我说的有点创意是指,这次并非通过钓鱼方式把用户的 EOA 地址切换为 7702 合约地址,也即 delegated address 并非钓鱼地址,而是几天前就存在的 MetaMask: EIP-7702 Delegator 0x63c0c19a282a1B52b07dD5a65b58948A07DAE32B,如图一。 钓鱼利用了 MetaMask: EIP-7702 Delegator 里的机制来完成批量授权钓鱼盗币操作。如图二,0xc6D289d55fE64227A09E3120855ccBa0d2E606DC 是受害者地址,发起了来自 MetaMask: EIP-7702 Delegator 的 execute 批量执行预定指令数据的操作。具体 tx 是: etherscan.io/tx/0x1ddc8cecbc… 图三是 MetaMask: EIP-7702 Delegator execute 里的具体逻辑,钓鱼团伙利用该机制完成受害者地址有关 token 的批量授权操作,如图四。 Game over...就这样。 在我们预测内,钓鱼团伙们跟上了...各位得提高警惕了,小心钱包里的资产被一窝端... cc @SlowMist_Team @MistTrack_io
5
5
1
33
15,904
teapawt.net/realScamSniffer/status… A signed permit granted an ERC1967Proxy smart account an unlimited AWETH allowance.Detection rules that rely solely on lists of known malicious contracts can miss this kind of activity.
Replying to @J222ad
This drainer owns no malicious contract.Every piece of the flow runs on legitimate used infrastructure (a Safe as its contract and the MetaMask Delegation Manager to split the funds). every signal detection tools rely on comes back clean, many standard detection rules don’t work.
1
1
2
168
The account used that allowance in the same UserOperation to split the funds between two addresses through direct transferFrom calls with the use of The Trust Wallet delegation. @blockaid_ @MetaMask @evilcos
3
98
🚨Kitless #drainer Drainers used to run on kits and their own contracts and wallets. Detection teams mapped them and turned that into IOCs for their rules and AI models. If that’s still how you detect drainers, wake up: the new generation of drainers is kitless.
1
1
8
225
This drainer owns no malicious contract.Every piece of the flow runs on legitimate used infrastructure (a Safe as its contract and the MetaMask Delegation Manager to split the funds). every signal detection tools rely on comes back clean, many standard detection rules don’t work.
1
1
3
209
If the MPC signing system could sign the EIP-7702 delegation without delay, why couldn’t it promptly sign the revocation? teapawt.net/binance/status/2117626…
20:20:59 : Malicious EIP--7702 delegation-23:01:59 :USDT rescue fails after Tether blacklists Binance 14 at 22:06:23--00:10:35 : Delegation revoked @binance may initially have suspected a key compromise, overlooking a malicious EIP-7702 authorization through its signing system
1
3
93
Binance may have overlooked the possibility of a malicious EIP-7702 authorization being signed without a PR leak. Separately, making Binance 14 the owner of Hot Wallet 34 created a shared point of failure.This practice is questionable. #BinanceHack
🤖 Made with AI
20:20:59 : Malicious EIP--7702 delegation-23:01:59 :USDT rescue fails after Tether blacklists Binance 14 at 22:06:23--00:10:35 : Delegation revoked @binance may initially have suspected a key compromise, overlooking a malicious EIP-7702 authorization through its signing system
1
10
258
20:20:59 : Malicious EIP--7702 delegation-23:01:59 :USDT rescue fails after Tether blacklists Binance 14 at 22:06:23--00:10:35 : Delegation revoked @binance may initially have suspected a key compromise, overlooking a malicious EIP-7702 authorization through its signing system
2
1
9
504
Replying to @zerion
@zerion How to contact the security team without going through Immunfi?
2
4
256
The threat actor uses sponsored search results to direct users to a fake @Rabby_io site that fully imitates the real extension’s experience, including installation, onboarding, and wallet import flows, in order to trick users into entering their seed phrase or private key .
2
9
443
#jad retweeted
tbh the @ambire wallet dev team deserves more credit than they get, they take care of their wallet codebase in such way that even automated security scanners mark them very safe, while plenty of other popular extensions fall below 90 score not only this time, I have seen multiple times that ambire often rank top in terms of security, UI, UX everything. Ambire wallet score : 97/100 link : crxplorer.com/extension/ehgj…
30
12
1
210
11,397
A gang of drainers deployed a malicious contract hiding behind the $ token symbol, tricking transaction simulators into showing fake balance gains in $ 🤣while quietly siphoning real ETH to their wallet.
2
2
10
673
One user, trying to protect the community, minted uint256.max to his own address convinced it would choke the contract and revert every future drain unaware that totalSupply() was purely cosmetic, every other wallet remained wide open, and the ETH kept flowing to the drainer.
4
268
you can build a browser extension that detects sponsored Google results and injects a Warning badge on them. Because let's be honest ,Google doesn't make it visually clear that these are ads. The 'Sponsored' label is tiny, easy to miss, and that's exactly how scammers thrive.
1
3
10
302
malicious app or overpriced tickets
1
1
5
163
Can someone help me establish contact with the @Blockaid security team? @idobn
1
7
326
Surface legitimacy is cheap to build and expensive to trust. Engineered to be reassuring, all of it exists to make you feel safe enough to stop asking questions before you reach the only place where the truth lives, which is the protocol level.
1
1
5
247
This applies equally to deceptive project marketing. A whitepaper full of revolutionary promises, a roadmap that never ships, a token with utility that exists only in the pitch deck, it is the same surface legitimacy, just applied earlier in the attack.
3
160
🔐💀 A lot of people are cryptographically signing the JavaScript code that was supposed to trigger the signature operation . Blind copying LLM responses without understanding what you're doing in crypto/auth= critical consequences waiting to happen.
3
9
442