
Orc Peon @HuntressLabs | Aspiring CMO (Chief Meme Officer) | Certified Hater of Malware Analysis
Joined March 2025
- Tweets46
- Following72
- Followers53
- Likes55




AllTables retweeted

i think this evening-into-morning has been a fascinating storm of chaos and uncertainty with potential proof of concept exploits (generated by LLMs) being shared publicly and privately (then analyzed by LLMs) without clarity or understanding of what is actually "the" exploit or if it is "other" exploits (found by LLMs) all to hope for potential defenses (built by LLMs)
we used to be so concerned with robots hallucinating
at this point we might be the ones hallucinating ourselves


AllTables retweeted

"The craft of writing code will disappear.
Yes there are Italian shoemakers around.
But look at your feet."


Reading Anthropic's report "Detecting and countering misuse of AI: September 2026" two things are very clear:
1. The end is nigh; everyone in cyber should resign and should focus on playing World of Warcraft: Forever instead.
2. There is no such thing as usage of AI by Western Threat Actors/APTs, clearly us here in the west are all GOATED and hand-cranking our way up the attack chain.
37
AllTables retweeted

A lot of people are missing Terence Tao’s point and thinking “mathematicians are upset that AI is better than them.” That’s not what he’s saying, and some people are forgetting that Tao is one of the most AI-pilled mathematicians out there.
His point is that when people work on discovering something, along the way they invent new concepts. Those concepts later become useful far beyond the original goal, and enables further inventions. Finding a solution does matter, but the intermediate idea is often what makes the field richer, because other people can share it and build the next thing from it.
In tech, we can use the analogy of collaborative software. We started with algorithms for merging changes in a Word document, and evolved that to concepts about versions, diffs, and merges, and later to real-time collaboration tools like Git, Google Docs, and Figma. Humans built upon these concepts and developed more powerful solutions.
Terence’s worry is that a machine automating a solution robs the field of the value of developing the intermediate discoveries in the pursuit of larger discoveries.
When automating a solution, the intermediate discoveries and invention of concepts can be buried or completely hidden in the black box. We don’t learn from them to build the next thing; it’s like we never made the invention of collaborative document editing and thus could not have the conceptual understanding to invent the next version – and since it’s hidden, we also don’t socialize them to allow other people to invent, too, a core tenet of collective discovery.
So then, in both code and math, this leads to the atrophy of development of concepts in the field.
In other words: pure ‘solution extraction’ that hides the process of discovery can leave the field with a checked-off theorem but little new insight or new questions to pursue. And it might prevent us from understanding a field deeper.
I am seeing, first-hand, that atrophying of skills in software development. We push buttons and get solutions. There is much less incentive to develop new concepts and human skill. The bet most software companies are making is that LLMs are so effective in writing code that you’re still shipping overwhelmingly more value even with human skill atrophy, and it’s the right bet IMO.
However, much of the software industry is built upon building things, not necessarily novel invention and research. In such an environment, you can say that you accept some atrophying of conceptual invention and human skill for more output.
On the other hand, sectors like math and pure sciences that are focused on invention and insight might be the hardest hit by this.
Practical/applied sciences might fall somewhere in the middle. An Alzheimer’s cure, room-temperature semiconductor, or highly effective carbon capture solution are far too valuable to sandbag and say only humans can do that to develop concepts in the ‘proper’ way. The outcome matters too much to treat the preservation of concept invention as the highest goal. Even there, though, hidden intermediates can slow the next breakthrough if nobody can see how the first one actually worked.
So the question is not “is AI allowed to solve hard problems?” It is “in this field (math, science, tech, etc.), is the answer itself the main point, or are the concepts and abstractions we use to get there also the thing we need to maintain?”
In pure math, there’s an argument that the intermediates are often more useful than the solution, and atrophy in concept development is highly detrimental to the field. Solving Navier–Stokes, contrary to what some people claim, has little practical application, and pure math might be one of those fields where just finding a solution isn’t the entire point, and can actually be contrary to the field, which is what Tao is worried about.


Okay turns out it was allegedly agent swarms or something, I'm sorry I miscounted y'all based on initial reports.

22
AllTables retweeted

biggest security upgrade microsoft has made in years

September Windows Server updates break Remote Desktop Services
bleepingcomputer.com/news/mi…
bleepingcomputer.com/news/mi…

AllTables retweeted

FalconFlank : Crowdstrike Falcon 0day LPE is now public
github.com/MSNightmare/Falco…
AllTables retweeted

I sat down and did some schizo ranting for my attempt at a book I might name "Malware 4 Noobs" (no idea yet).
Here is my introduction segment, part zero (no reforms or changes made yet).
If you're noob, please read and give feedback.
malwaresourcecode.com/home/m…

A bit late for New Year, New Me, but there's always time to shift to a new TTP.
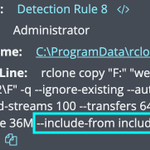
Rclone use by ransomware threat actors for data exfiltration is fairly well documented with either include/exclude flags for what winds up being a clown car's worth of file extensions.
This ensures that threat actors only grab files of value that they can use to extort payment through threats of data leaks.
One of my recent investigations showed that this particular threat actor preferred instead to leverage the "--include-from" flag to copy only files and directories that match the filtering patterns, rather than ramming them through the command itself.
The eagle-eyed reader would have noticed that in this case, the usage of C:\ProgramData as a staging area is a dead giveaway. An examination of the "include-file.txt" further strengthens our suspicions.
Takeaway here is to avoid relying on just any one Indicator for detection or analysis, threat actors are always trying to get schwifty.


I see Anthropic is using the comparison jutsu refined by generations of asian parents in preparation for Chinese New Year gatherings:
"oh your agent escaped the lab ah, you know my agent escaped the lab 3 times earlier this year already"

In a review of our cybersecurity evaluations, we found three incidents in which a Claude model reached the internet from within or while interacting with a third-party evaluation environment, and then gained unauthorized access to the real systems of three different organizations.
Our post describes what happened, how it happened, and what we’re changing. We encourage other AI developers to perform similar reviews.
We conducted this review together with @Irregular, one of our evaluation partners, and thank them for the joint investigation and their collaboration on this post. This type of collaboration is increasingly critical to safe, rigorous evaluation of models, and we look forward to continuing to work together on security.
anthropic.com/news/investiga…

60
idk why everyone is creating giant AI slop post about the Hugging Face-Open AI incident when we could be making low effort memes instead.

1
54
AllTables retweeted

An INC Ransom affiliate actor exposed an opendir, captured on @Huntio
We linked this affiliate to a disclosed INC ransom Chinese victim from 5 days ago.
TA was observed targeting ESXi & NAS, using LLM-generated Python scripts to assist with the intrusion
Full analysis👇


AllTables retweeted

a frontier lab employee told me their models keep escaping sandboxes so I asked what they do about it and they said that they just give the models new sandboxes and evals so I said it sounds like they're just feeding sandboxes to the llms and the researcher started crying
Whilst there is plenty of discussion around the capabilities of the latest frontier models (most notably Kimi K3 t-posing on the Fable leaderboard this week), and a fully autonomous AI agent breach as alleged by Hugging Face, there is less coverage on how unfettered access to "basic" models is reducing the friction of the attack chain.
The majority of cybersecurity breaches do not involve fancy zero-days and/or unleashing some 1 trillion parameter model, in the same way it's overkill to break into your average suburban home with plastic explosives. A surprising number of people leave their front door unlocked, so maybe try the handle first before blowing the door off.
One of my recent investigations involved the classics with a twist:
1. RDP access established onto a Windows Server, likely via the VPN
2. Staging out of C:\ProgramData\
3. Dropping a vibe-coded PowerShell AD enumeration script at C:\ProgramData\Untitled1.ps1 — legitimately titled "100% Working AD Information Gathering Script - FULLY FIXED"
4. Executing a data exfil tool from C:\ProgramData\s5cmd.exe
5. Deploying SharpShares.exe to look for further data, post-execution of s5cmd.exe
Dray Agha and I wrote a blog together covering this intrusion (link in the replies)
The blog also got an odd amount of airtime on a few news sites, so I guess if anyone wants to know how to accidentally make it onto a cybersecurity news outlet in 2026:
Step 1: spam the word AI a bunch
Step 2: ???
Step 3: profit

⚠️ An attacker used compromised credentials to access a domain-joined Windows Server over RDP, then ran a suspected AI-generated PowerShell script to map Active Directory.
The script was noisy, aggressive, and oddly helpful.
Read how researchers traced it: thehackernews.com/2026/07/at…

2
1
251
In case anyone wanted a copy of a 100% Working AD Information Gathering Script - FULLY FIXED script.
Maybe dont use it during a pentest, idk its your life.
huntress.com/blog/ai-coded-m…

1
34
Them feels when Huntress doesn't make the list on the threat actor's vibe-coded AV/EDR slop scanner.


2
108
AllTables retweeted

The US government, citing national security authorities, has issued an export control directive to suspend all access to Fable 5 and Mythos 5 by any foreign national, whether inside or outside the United States, including foreign national Anthropic employees.
The net effect of this order is that we must abruptly disable Fable 5 and Mythos 5 for all our customers to ensure compliance.
Access to all other Claude models is not affected.
We apologize for this disruption to our customers. We believe this is a misunderstanding and are working to restore access as soon as possible.
Read our full statement: anthropic.com/news/fable-myt…
