

| Full Stack Vibe Engineer | | Sr Prompt Engineer | | The Believer's Advantage | https://teapawt.net/t.co/aWzBCY4FVS
Joined October 2022
- Tweets3.8K
- Following214
- Followers278
- Likes18.2K


Joby retweeted

We built a little tracker for Tibo’s 28-day challenge 🗓️
An improvement or a full reset, every day. Let’s see what ships!
codex-resets.com/tibo-28


Joby retweeted

If they really start to gatekeep who gets to use the best models, that is a declaration of war.
This prospect fills me with the most sincere, bodily cypherpunk will-to-power that I've ever felt (at least since I was a teenager). If they really go down this route, I would go all-in on building the most psychotic swarms of open-source models and fine-tunes possible, all geared toward a Chaotic Good jamming of the entire institutional public sphere. If we didn't do that, all of political life and the marketplace of ideas would be over before we know it.
It's one thing if the top models become too expensive for me or others to use (I'm already pricing that in, and if you can't build something profitable enough to climb that ladder as it gets pulled up, then that's fair enough).
But if the ladder gets pulled up politically, now, so only select institutional players get access to the most intelligent models, then any mature American man should be as energized as gun collectors are around the 2nd Amendment, or liberal women are around Planned Parenthood.
Joby retweeted

NEW: malware developers added nuclear & biological weapons text to to their spyware.
Goal? To trigger LLM safety refusals... so that their spyware wouldn't be analyzed by an AI security scanner.
Cleanest practical example I can think of for why over-indexing on first order safety alignment is risky.
When closed (and open) models ship with aggressive refusals, they will be sprinkled with second-order blindspots that attackers will discover...and exploit.
We are only in the earliest days of attackers leveraging these features, and it wouldn't surprise me if users systems that need to handle complex cybersecurity issues demand that models be less safety-blunted.
In the weeds: @SocketSecurity's post also shows why intention matters in how you design a malware analysis pipeline to avoid prompt manipulation.
H/T to colleagues that shared this with me socket.dev/blog/mini-shai-hu…


Joby retweeted

How is that that one of the most powerful ideas in the entire history of technology is now under coordinated attack?
If I told you that one little software concept powers the website you're reading this on, the router in your house that connects you to the internet, the phone in your pocket and your TV streaming service, what would you think?
What if I said that the NASDAQ and New York stock exchanges where your retirement portfolio trades is powered by the same ideas? Or that those same concepts power 100% of the top 500 supercomputers on the planet doing everything from hunting for cures for cancer, to making rockets safer, to mapping the human brain?
Not only that, it also powers all the major clouds, from Amazon Web Services, to Google Cloud and Alibaba and more.
You'd probably think that was a good thing, right? Not just good, but absolutely critical to the functioning of modern life at every level. And you're be right.
That critical infrastructure is "open source" and it powers the world.
It's everywhere, an invisible bedrock beneath our entire digital ecosystem, underpinning all the applications we take for granted every day.
It seems impossible that something that important would be under attack.
But that's exactly what's happening right now. Or rather, it's happening again. It's not the first time.
In the early days of open source, a powerful group of proprietary software makers went to war against open source, looking to kill it off.
SCO Unix, a proprietary Unix goliath, tried to sue Linux into oblivion under the guise of copyright violations.
Microsoft's former CEO, Steve Ballmer, called open source cancer and communism and launched a massive anti-Linux marketing barrage. They failed and now open source is the most successful software in history, the foundation of 90% of the planet's software, found in 95% of all enterprises on the planet.
Even Microsoft now runs on open source with the majority of the Azure cloud powered by Linux and other open software like Kubernetes and thousands upon thousands of packages like Docker, Prometheus, machine learning frameworks like Pytorch, ONNX and Deepspeed, managed databases like Postgres and MySQL and more.
Imagine if they'd been successful in their early attacks on open source? They would have smashed their own future revenue through short-sightedness and total lack of vision.
And yet open source critics are like an ant infestation in your house. No matter how successful open source gets or how essential it is to critical infrastructure they just keep coming back over and over and over.
Today's critics of open source AI try to cite security concerns and tell us only a small group of companies can protect us from our enemies so we've got to close everything down again and lock it all up behind closed doors.
But if open source is such a security risk, why does "the US Army [have] the single largest installed base for RedHat Linux" and why do many systems in the US Navy nuclear submarine fleet run on Linux, "including [many of] their sonar systems"? Why is it allowed to power our stock markets and clouds and our seven top supercomputers that run our most top secret workloads?
But they aren't stopping with criticism there. They're pushing to strangle open source AI in its crib, with California bills like SB 1047 set to choke out American AI research and development while tangling up open weights AI in suffocating red tape, despite a massive groundswell of opposition from centrist and left Democrats, Republicans, hundreds of members of academia and more, the bill passed and now goes to the governor. Eight members of Congress called on the governor to veto the bill. Speaker Pelosi took the unprecedented step of openly opposing a bill in a state Assembly that is primarily Democrat.
And yet still the bill presses forward.
Why?
Do too many people just not understand what open source means to the modern world?
Do they just not see how critical it is to everything from our power grid to our national security systems and to our economies?
And the answer is simple:
They don't.
That's because open source is invisible.
It runs in the background. It quietly does its job without anyone realizing that it's there. It just works. It's often not the interface to software, it's the engine of software, so it's under the hood but not often the hood itself. It runs our severs and routers and websites and machine learning systems. It's hidden just beneath the surface.
The average person has no idea what powers their Instagram and Facebook and TikTok and Wikipedia and their email servers and their WhatsApp and Signal. They don't know it's making their phone work or that the trades of their retirement portfolio depend on it.
And that's a problem.
Because if people don't even know it exists, how can we defend it?
1/


Joby retweeted

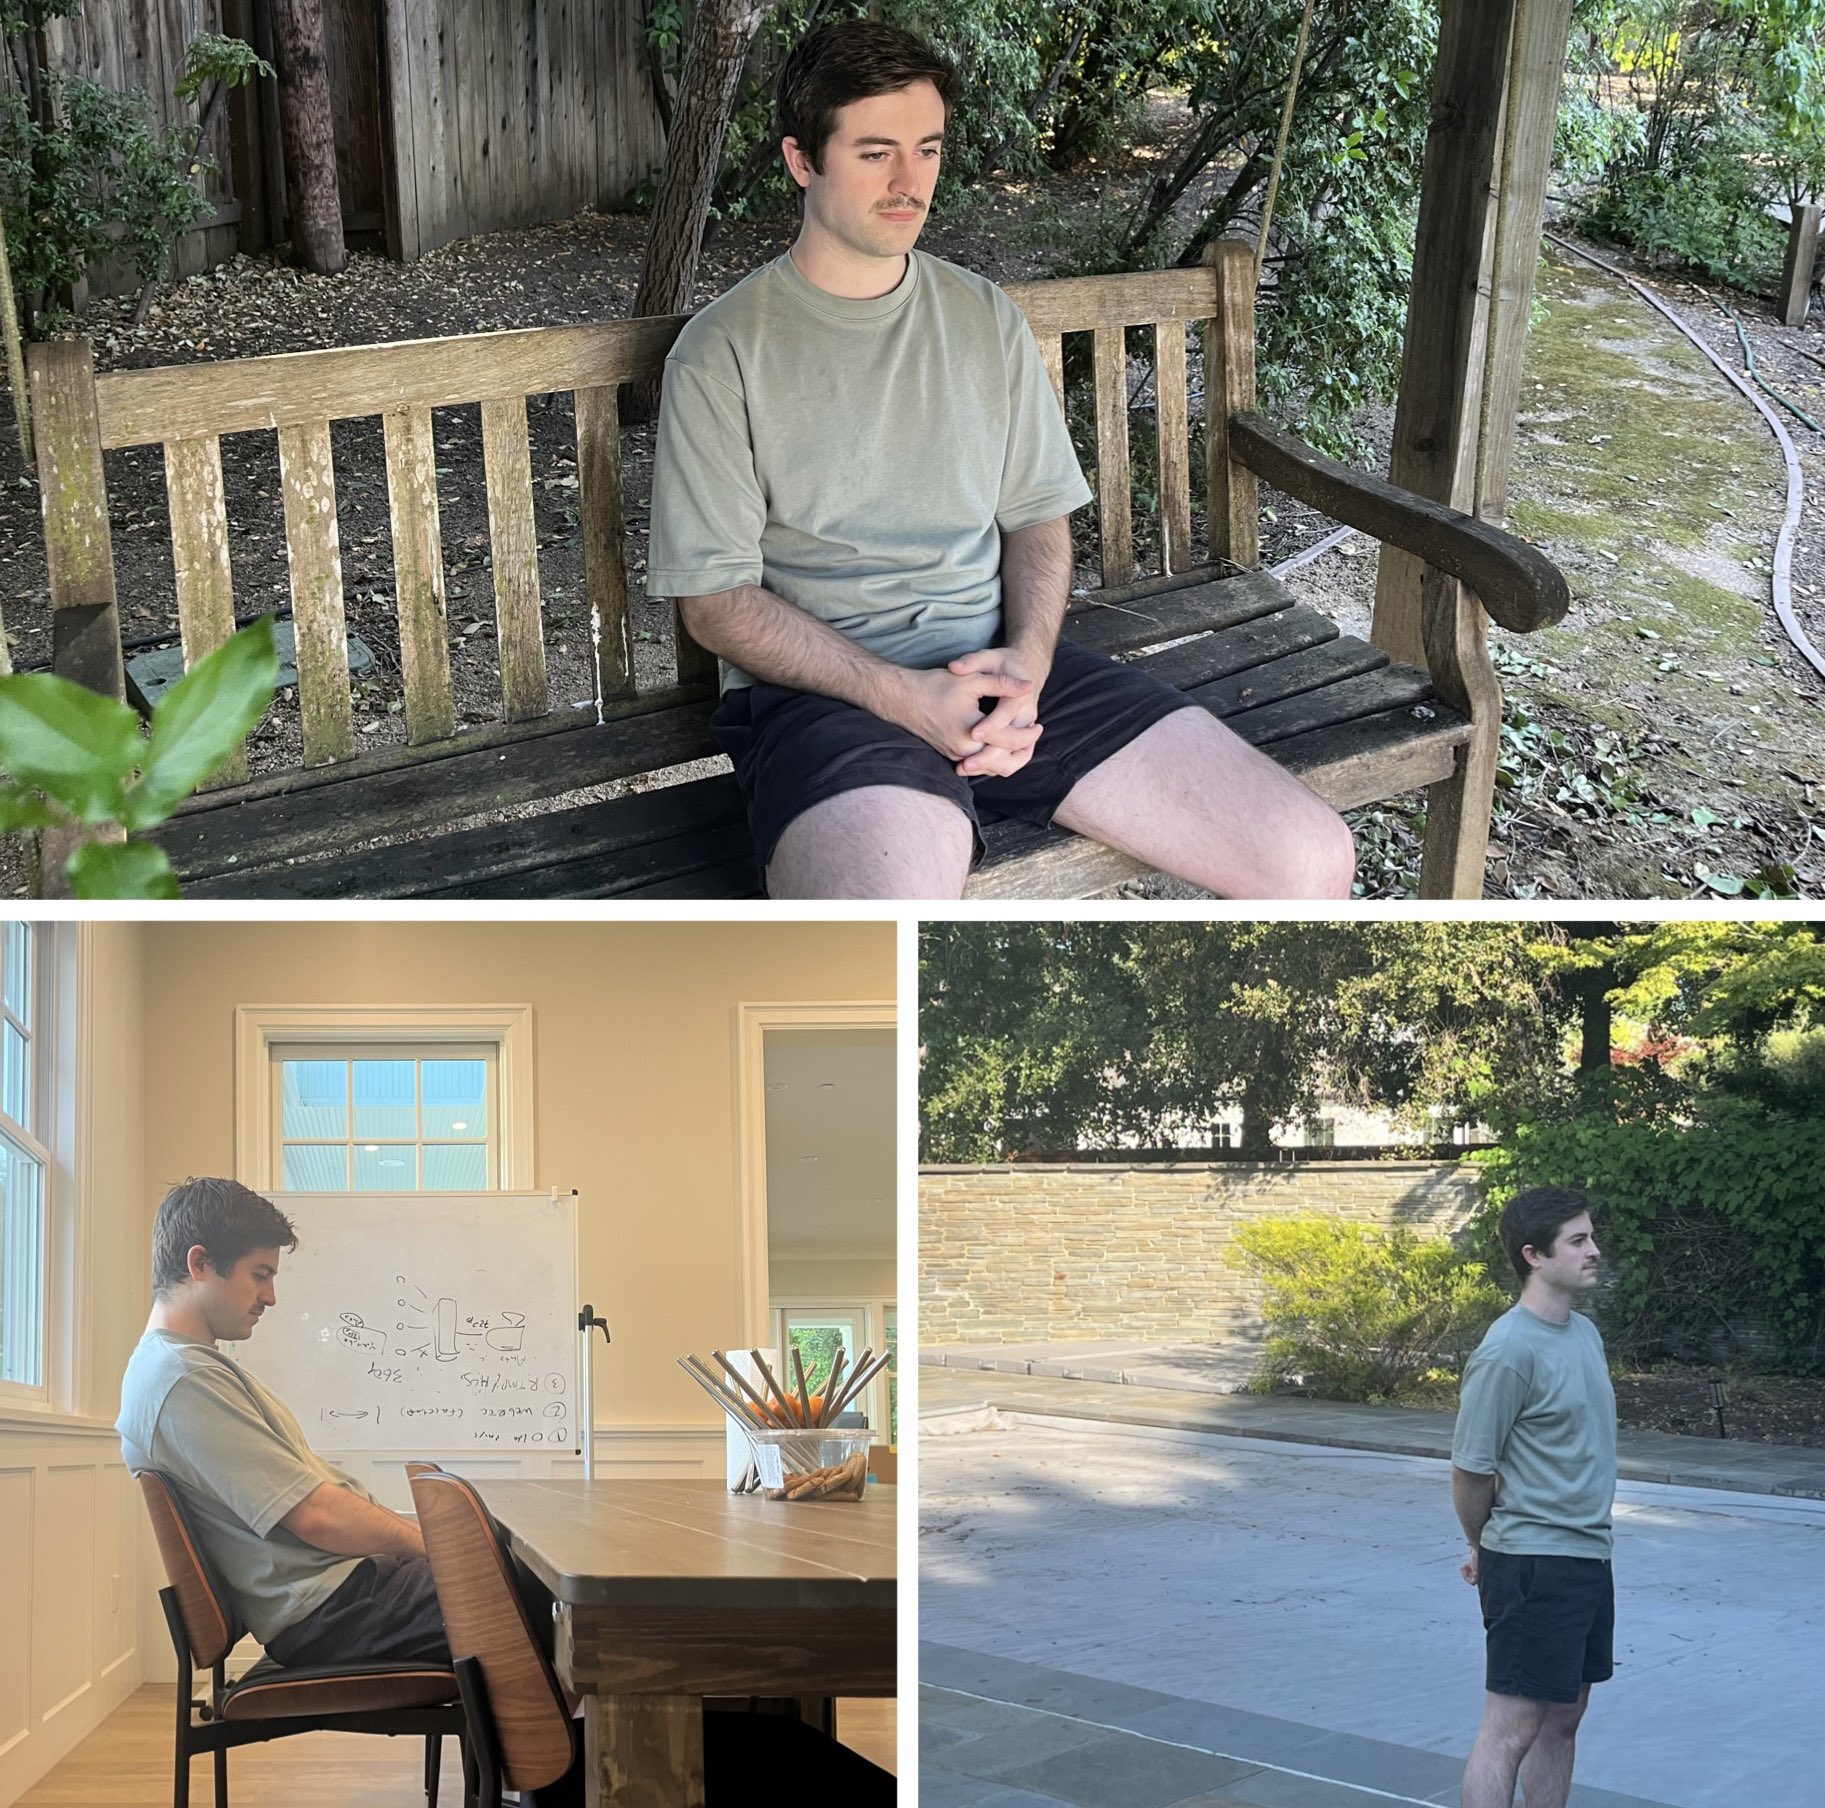
For those of you who do NOT have access to Advanced Voice Mode for ChatGPT:
Here's a little image to cheer you up while you wait...



Joby retweeted

We are going to have 4-5 years lag time for programmers where people learn and are creative with their use of code gen sota LLMs and get way ahead of the curve. There is no way out here, there is no tool you can download. You have to do it yourself and make it up yourself
Joby retweeted
ILYA HAS GONE DARK BECAUSE THEY REALIZED THEY NEEDED TO TRANSFER HIS CONSCIOUSNESS INTO GPT-5 IN ORDER TO MAKE IT TRULY AGENTIC AND ACHIEVE ARTIFICIAL GENERAL INTELLIGENCE.
(THREAD) ⬇️
This quoted post is unavailable.


