
Security @ Google | Ex-Qualcomm | CEH | SRT | Security Enthusiast | Github - https://teapawt.net/t.co/35EatPIhOV
Joined November 2012
- Tweets1.5K
- Following626
- Followers10.6K
- Likes2.9K



Pinned Tweet
A lot of you guys were requesting Gitbook for HowToHunt.
It took hell lot of work to arrange them 😓,
hope so you like it, and make some pull request, what's left.🙂
Here you go: 🔥
kathan19.gitbook.io/
#bugbountytips #bugbounty #BugBountyTips
they "fixed" an IDOR by randomizing the key (128‑bit). so I sent it as an integer — type juggling matched it anyway → key leaked → full unauth IDOR.
#bugbounty #bugbountytips #infosec

Kathan Patel retweeted

EXCLUSIVE: 200+ Government of India websites have been hacked!
From Google, they now redirect to vc66 [dot] net, a domain registered on Dec 21, 2024. Its an online money-making scam but links to malware—an attack called SERP hijacking.
Search [site:*.gov.in fast cash] to see.

Hey, community! 👋 Excited to attend @bsidesahmedabad If you see me around, don't hesitate to say hi. Looking forward to some great technical chats! 😄
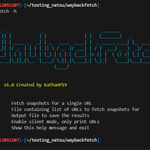
Updated WayBackFetch with a new feature that removes snapshot urls with duplicate content, leaving only urls with unique content. Thank you, Sensei @dwisiswant0 👍
If you haven't already checked the project here's the GitHub link : github.com/KathanP19/wayback…

Created a small tool to retrieve archived snapshots urls of web pages from the Internet Archive. Use it in your recon and let me know your feedback!! 😄
#bugbounty #bugbountytips #infosec

Httpx seems to be not reliable when checking urls suggest some tool which can do better job and also has filter based on web content or title.
#BugBounty
I found the solution using httpx itself, so the solution is that you need to find the sweet spot for threads. "-t 5" worked for me. It varies from target to target, so add this step to your recon checklist before running any tool for best results.
#bugbountytip 😅
Trying to find Origin IP check out this tool created by @mmrecon to find IP behind WAF:
github.com/mmarting/unwaf
#bugbountytips

HowToHunt is updated with some new resources and techniques check out: github.com/KathanP19/HowToHu…
- Reverse Engineer an API by @offensivedroid
- 2FA bypass method by @ome_mishra
- GraphQL Resource
.. and more
Sorry guys for late update lots of new things going in life. 😅


Kathan Patel retweeted
Lessons:
- Context is King. THINK!
- To break you must first understand: Know your target's technologies & the services they use.
- Learn to code.
Top:
teapawt.net/hacker_/status/1575466…

Kathan Patel retweeted

I've made over 100k on SSRF vulnerabilities.
They aren't always as simple as pointing it at localhost or AWS Metadata service.
Here are some tricks I've picked up over the past 5 years of web app testing:

Kathan Patel retweeted

The iOS Reloader is a weaponizing tool designed for jailbroken iOS devices. It facilitates the installation of a collection of essential tools on iOS devices for penetration testing purposes.
github.com/darklotuskdb/ios-…
#HR51KDB
#bugbountytip #bugbountytips #ios #vapt

Excited to kickstart my career as a Cyber Security Engineer at @Qualcomm! Joining the amazing #TeamQualcomm and ready to learn, grow, and make a difference in the world of technology. Grateful for the opportunity! 💪🔒✨ #New2Q #Qniversitygrad


Kathan Patel retweeted

AD FOR OSCP (Active Directory Guide)
abhishekgk.medium.com/ad-for…


Check out this awesome api my friend made to get subdomains of given domain, one more passive source to integrate in your tool 👍.
#bugbountytips
This Post is from an account that no longer exists. Learn more
