

RE and CTI. Feel free to take a gander at my past presentations: https://xitter.cf/t.co/iWUyecnxC6
Joined January 2011
- Tweets138
- Following22
- Followers1.3K
- Likes286




Some North Korean post infection malware. Nothing groundbreaking, I just always like to see the actual code when vendors gloss over it:
norfolkinfosec.com/north-kor…
I’ve included hashes where the files were on VT, if you want to grab them to look for yourself.


Some notes and testing on (what I think is) a #VIRTUALGATE sample, following Mandiant's ESXI report:
norfolkinfosec.com/some-note…
MD5 3c7316012cba3bbfa8a95d7277cda873
-Opens VMCI listener on 25736
-Listens
-Runs what it receives via cmd
Post shows RE + how to test it. Cool malware

ALT Overview

ALT Sockets -> Cmd.exe branch

ALT Sending data via VMCI tunnel
Kevin Perlow retweeted

.@MITREattack v9 is out!!! A big shout out 🙌 to @patrickwardle, @thomasareed, @its_a_feature_ , and @xorrior for helping us update changes to macOS🍎. There is more to come...but let's take a moment to appreciate my new favorite gif, which summarizes this release perfectly!

It has launched! ATT&CK v9 is now live with refactored data sources, ATT&CK for Containers, Google Workspace as a platform and more! Read about new data sources and the rest of the update at medium.com/mitre-attack/atta… or attack.mitre.org/resources/u… for new/changed groups/techniques/sw.
Also, my personal favorite talk from the conference was from @JamesPavur - A fantastic presentation on eavesdropping on satellite internet conversations.
youtu.be/d5Sbwlu6f8o
No technical satellite knowledge required (I barely know how they get up there)
They put our BlackHat videos up the other day! :)
It's a bit old now, but if you want to see how #Lazarus used ISO-8583 for the #FASTCash malware in past years, here's the URL: youtu.be/zGvQPtejX9w
Feedback is always welcome - presenting to a glowing orb was not the easiest.
Last #Lazarus #ZINC update: a source gave me the missing registry data (~2mb reg entry). Sorry for the spam... have to do this after hours.
Updated w/ brief analysis of Stage 2:
norfolkinfosec.com/dprk-targ…
Screengrab, process launching, recon etc.
That's it from me for a while :)


Part II: Looking at the #DPRK /#Lazarus/#ZINC .sys malware targeting security researchers, with a hunt hypothesis as the highlight:
norfolkinfosec.com/dprk-targ…
Note that I *don't* have the Stage 2 registry data. Would love to see it if someone has a copy!


Part II: Looking at the #DPRK /#Lazarus/#ZINC .sys malware targeting security researchers, with a hunt hypothesis as the highlight:
norfolkinfosec.com/dprk-targ…
Note that I *don't* have the Stage 2 registry data. Would love to see it if someone has a copy!
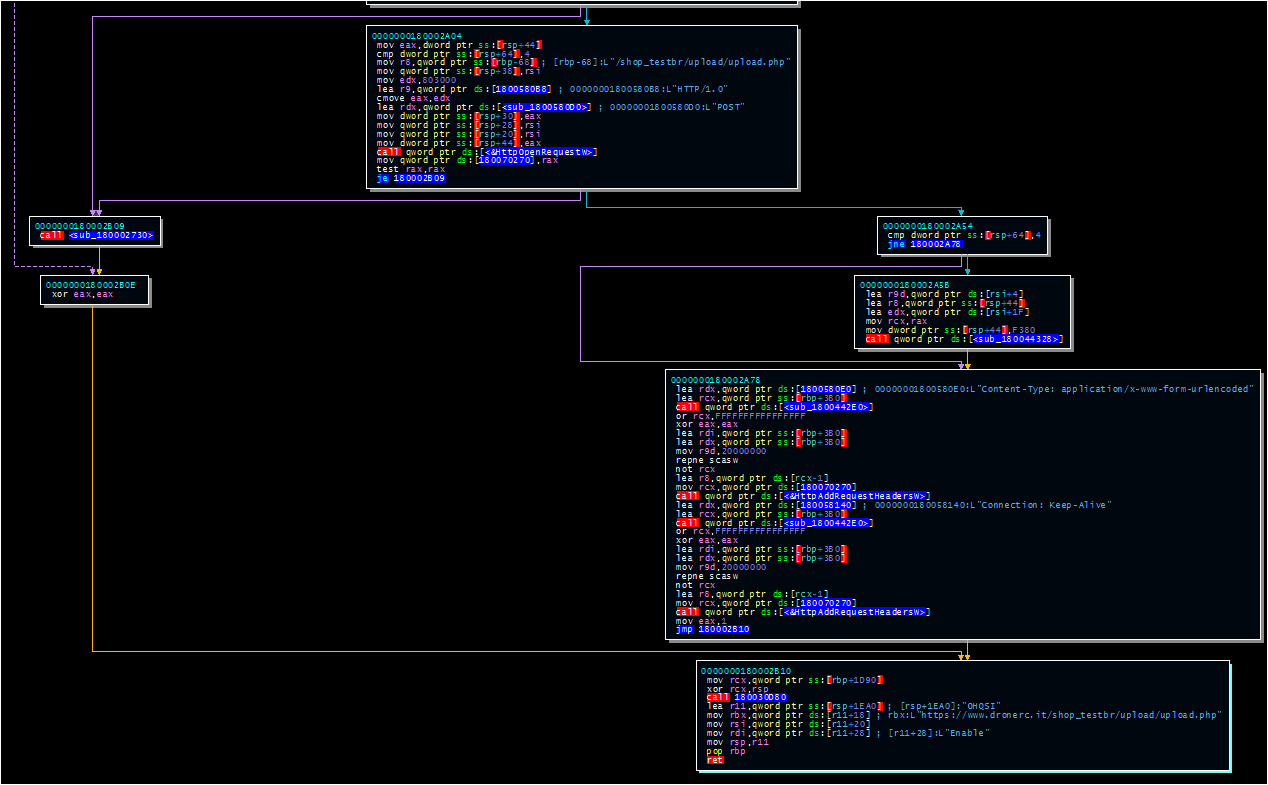
A look at some of the malware mentioned in this Google TAG research.
norfolkinfosec.com/dprk-malw…
- Two-stage (payload in ProgramData)
- AV Check (Kasp, Avast)
- Basic Persistence
- Multiple C2s per payload
More to be done re:C2 comm (unless someone does it first)
#DPRK


New blog post from TAG with details of a North Korean campaign targeting security researchers working on vulnerability research and development.
blog.google/threat-analysis-…
Stay safe out there everyone!

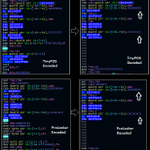
Interesting possible relationship between #TinyPOS + #ProLocker
norfolkinfosec.com/tinypos-a…
I lean towards, "would makes sense if it's the same group," but far from definitive. Was trying to find infrastructure.
@DrunkBinary (for the hashes)
@cyb3rops (for code segments and YARA)


Really awesome to be included in part of the Wired write-up! 🙂 For folks looking for the slides and whitepaper, both are linked here: norfolkinfosec.com/presentat…
Whitepaper has a summary of tool relationships from the #FASTCash adversary + some extra RE.

"What has fundamentally changed between when Barnaby Jack presented and now?" @angcui wired.com/story/atm-hackers-…

Kevin Perlow retweeted
LOVING the live Q&A *DURING* the #BHUSA session with @KevinPerlow on financial malware.
Learning lots.

Looking back at LiteDuke (#APT29/#CozyDuke):
norfolkinfosec.com/looking-b…
Found a copy and wanted to do some RE to build on @ESETresearch's previous great work. Post includes deeper dive into the available commands and some of the techniques used.


Unpacked payload: virustotal.com/gui/file/391b…
Remember, this is old malware (late 2014). That being said, I *do* think it has some really interesting components. Was worth at least going down the rabbit hole.
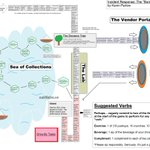
My April Fool's present: Incident Response, the "Bored" Game. Please verb responsibly.
@DrunkBinary @VK_Intel @magerbomb @jdenne79
*Might be worth playing with blank squares and a "dungeon master" who tracks the rolls and reads the squares.

Golang walkthrough - A look back at some old (2017) #Dragonfly / #DYMALLOY "Goodor" using newer tools:
norfolkinfosec.com/a-new-loo…
Always how Goodor *actually* worked. Redress from @joakimkennedy helps answer that question.
CC @DrunkBinary


Analysis of #FIN8 #PoSlurp payload relevant to VISA fuel pump report (incident 2):
norfolkinfosec.com/fuel-pump…
I put the payload on VT (for static analysis): 3d5ae56c6746e0b3ed5b15124264a0d2
Credit to @just_windex for initial shellcode.
cc @DrunkBinary @cyb3rops for tracking/sigs


I wanted to supplement other research out there re:#PoSlurp. Some thoughts:
- LOTS of exit checks
- Seems to need env variable to specifically be set via PowerShell
- Different approach by targeting a specific process
- Interesting registry references (likely persistence)
Analysis of #FrameworkPOS/#GratefulPOS file reported by @VisaSecurity (Incident1)
norfolkinfosec.com/pos-malwa…
Of note-Not sure people's public RE of this smaller file has been accurate. No obvious DNS in this DLL, and memscrp.stp is just an off switch. Details in post
@DrunkBinary


Non-DNS
32ccf851b0b81252aa2bfdf2e8b416cb
0eb7ac6d2d99d702ecc8b86ff90b0aac
576039d7cb54b749af5ed3d3558ee296
DNS
0576380f93f49279491177d96d84ad7e
353b0df3a9efce2d32f6097cab8fffc3
128f75f8c80d65d416c740a6d4c1591e
4ed6cc403d5ea6abae458ba6f43ad4f3