

https://xitter.cf/t.co/tPwrHxOvyU #TechDiary is born. In this place we will publish information about our daily work and things we stumble upon while doing it. #cybersecurity #dfir
Joined June 2020
- Tweets45
- Following40
- Followers64
- Likes17





LIFARS TechDiary retweeted

My technical analysis of #DearCry #ransomware is now online. I would like to demonstrate some techniques of #MalwareAnalysis, and especially #ReverseEngineering in #IDA freeware of malicious sample for educational purposes.
lifars.com/wp-content/upload…

LIFARS TechDiary retweeted

Official #PHP Git Repository Was #Compromised. Remember the #SolarWinds supply chain compromise in December 2020? It seems that a similar issue affects PHP, the server-side #programming language powering over 79% of the #websites on the #Internet. #cyber lifars.com/2021/03/official-…

LIFARS TechDiary retweeted
#Microsoft Exchange–ProxyLogon Vulnerability Analysis. Goal of this case study: summarize technical details of the ProxyLogon vulnerability alongside other vulnerabilities that were used in chain to perform remote code execution in early 2021 Exchange hack lifars.com/knowledge-center/…

LIFARS TechDiary retweeted
Thank you very much. It is my pleasure to participate in @BlackHatEvents.
And of course, kudos also to my great team at @LIFARSLLC, including Viliam and Jaroslava for their work on our tools.
@LIFARSTechDiary #ThreatInteligence #ThreatHunting #DFIR #CyberSec #BlueTeam

@ladislav_b demos LogChecker - a new Windows and Linux tool for scanning log files, developed by LIFARS at #BHASIA Arsenal. It extracts IP addresses, domain names, and hashes from the input file. Learn more here: bit.ly/316wYon
LIFARS TechDiary retweeted

@ladislav_b demos LogChecker - a new Windows and Linux tool for scanning log files, developed by LIFARS at #BHASIA Arsenal. It extracts IP addresses, domain names, and hashes from the input file. Learn more here: bit.ly/316wYon
LIFARS TechDiary retweeted
#MalwareLabDaily 0x4E
Video analysis and #reverseengineering of recent #DearCry #ransomware sample by @ladislav_b.
This ransomware targets Microsoft Exchange servers affected by #ProxyLogon
#IDAFreeware #capa
youtube.com/watch?v=6lSfxsrs…
@LIFARSLLC @LIFARSTechDiary @HexRaysSA

How does #Clubhouse work? Feel free to join this talk in Slovak language.

Talk about #Clubhouse #technology and #security. Today at 20:15 CET.
Poor Connection issues, vulnerabilities, #privacy
---
Dnes o 20:15 miesnosť venovaná techonológiám a bezpečnosti Clubhouse. Sieťová komunikácia, firewall, zraniteľnosti, súkromie, ...
joinclubhouse.com/event/P99O…
Tech people from @LIFARS are also members of this club, and we have own room about #hackers and #attacks every Friday.
@joinClubhouse
Our #CyberSecurity in #Slovakia club on #Clubhouse has its own website.
---
Náš klub Kyberbezpečnosť v SR už má vlastnú webovú stránku. Novinky, plánované miestnosti, poznámky, ďalšie materiály.
kyberklub.sk/
@joinClubhouse #infosec #education #cybersec #security

We took a look at #clubhouse authentication. Can you #bruteforce it? Will you find out if others get unauthorzied access to your account? Let's see in the first part of our series on #clubhousesecurity.
lifars.com/2021/02/clubhouse…
Pridajte sa dnes k nám na diskusiu na #Clubhouse. Pilotná edícia bude o minulých, aktuálnych aj budúcich kybernetických útokoch, o ľudoch a skupinách za nimi a ich obetiach.
joinclubhouse.com/event/xqab…
#cybersecurity #security #infosec #ethicalhacking #cybercrime #Hacking

Discussion about #hackers, #attack, #incident, #breach and #leak with @LIFARSLLC analysts.
Tomorrow, 19 Feb at 6:00 PM CET on @joinclubhouse.
joinclubhouse.com/event/xqab…
“Hackerské útoky včera, dnes a zajtra”. #Clubhouse, 19 Feb 2021, 18:00 CET
I am discussing #hacking and #cybersec with @henrichslezak and Milan Kyselica.
Tomorrow, 19 Feb at 6:00 PM CET on @joinclubhouse. Join us! joinclubhouse.com/event/xqab…
LIFARS TechDiary retweeted
We have developed #Logchecker, a new #tool for log analysis powered by #ThreatIntelligence. It uses #YETI as its backend and supports plaintext and EVTX files. I wrote a blog post about this tool and its usage.
@LIFARSLLC @LIFARSTechDiary @malwarelab_eu
malwarelab.eu/posts/logcheck…

ALT Logchecker - log analysis powered by threat intelligence
LIFARS TechDiary retweeted
𝐈𝐧𝐭𝐫𝐨𝐝𝐮𝐜𝐢𝐧𝐠 𝐓𝐡𝐞 𝐍𝐞𝐰 𝐋𝐨𝐠𝐂𝐡𝐞𝐜𝐤𝐞𝐫 - Log Analysis Tool Powered by Threat Intelligence Developed By LIFARS.com @LIFARSTechDiary lifars.com/knowledge-center/… #Sourcecodes and pre-built binaries are available at #LIFARS #GitHub: lnkd.in/dMC5nhW

#Logchecker by @LIFARSLLC - our new #opensource #tool for scanning log files. It extracts IP addresses, domains and hashes from logs and checks for them in #YETI #ThreatIntel database.
lifars.com/2021/01/introduci…
github.com/Lifars/log-checke…
#DFIR #blueteam
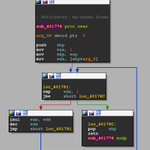
Reflective PE Loader from #Egregor #ransomware. Compare @HexRaysSA decompiler output with and without little help of analyst with adding proper structures to the #IDAPro disassembly
#reversing #malware

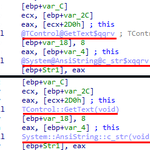
Are you bored of mangled C++ names in #IDAPro? Change it with this quick tip.
This one and much more have been covered during recent #IDATraining by @HexRaysSA. Thank you.
#reversing #malwareanalysis


The #vulnerable versions of #SolarWinds, 2019.4 HF 5 to 2020.2.1 HF 1, released between March and June 2020, include a file containing the #backdoor called #SUNBURST. We wrote a brief guidance on how to check if you have it and if it was already exploited. lifars.com/2020/12/guide-to-…

What is Your toolset for #memoryforensics? Everyone heard of #Volatility and #Rekall, but what about #MemProcFS? It allows You to browse memory objects as files on mounted drive. Processing is super-fast. Try yourself, it is definitely worth a few minutes! #DFIR #digitalforensics

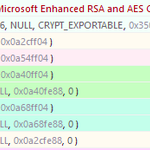
How to easily find out which ciphers are used by #ransomware? Just trace Crypt* API calls from advapi32.dll and if the #malware use them for #encryption, you will see the parameters.
#Ryuk => RSA + AES-256
