
Ransomware, Online Security, and Malware. Owner, Editor in Chief of @bleepincomputer. DM on Signal: LawrenceA.11 * https://xitter.cf/t.co/LXVRoICs8Z
New York
Joined July 2008
- Tweets2.5K
- Following833
- Followers18.2K
- Likes1.6K




Lawrence Abrams retweeted

I regret to inform the community that all that the source code for Vector has been leaked.
This has been tough on the team, most likely, it's being auctioned on the dark web.
🧵 Whoever purchases it will regret it for the reasons in this thread.

1/ We are sharing additional details regarding our investigation into unauthorized access to GitHub's internal repositories.
Yesterday we detected and contained a compromise of an employee device involving a poisoned VS Code extension. We removed the malicious extension version, isolated the endpoint, and began incident response immediately.

New data theft campaign is targeting Okta SSO-connected platforms.
Extortion demands signed by ShinyHunters.
xitter.cf/BleepinComputer/status…

Okta SSO accounts targeted in vishing-based data theft attacks - @LawrenceAbrams
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

My scoop: PornHub extorted by ShinyHunters for the theft of over 200 million activity data records for Premium members.
The data is detailed linking member's emails to what videos they watched, downloaded, and searched for.
xitter.cf/BleepinComputer/status…
🚨PornHub is being extorted by the ShinyHunters extortion group over the theft of over 200 million Premum member activity data records.
Both PornHub and ShinyHunters claim the data was stolen in the recent Mixpanel breach.
bleepingcomputer.com/news/se…

Lawrence Abrams retweeted

The rise and fall of LockBit Gang.
It’s clear that FBI Newark and their partners have a solution even to the most prolific ransomware operation.

The security incident at University of Pennsylvania appears to be a more extensive breach than originally stated.
My scoop: bleepingcomputer.com/news/se…

Lawrence Abrams retweeted

The Clop ransomware gang confirmed to BleepingComputer they are behind the emails, claiming they exploited an Oracle bug to steal the data.
“We not prepared to discuss details at this time. Soon all will become
obvious that Oracle bugged up their core product and once again, the task is on clop to save the day. We do not damage to systems and only expect payment for services we provide to protect hundreds of biggest companies in world.”
Emails claim Oracle data theft in new Clop-linked extortion campaign - @LawrenceAbrams
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

My scoop from earlier today.
A sample shared with me had a full PDF customer engagement report.
Red Hat confirms security incident after hackers claim GitHub breach - @LawrenceAbrams
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

Lawrence Abrams retweeted

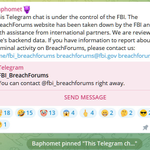
The XSS forum community is actively discussing the situation. However, it appears that moderators are removing all content where the admin (LARVA-27) is being discussed. This was confirmed in a Telegram chat by moderator LARVA-466 (Rehub). The goal is to suppress any narrative that could turn the situation into a newsworthy event and to "troll" Westerners in the process. However, while the xss[.]is domain displays a seizure notice, the backup domain xss[.]as, the .onion site, and the Jabber service at thesecure[.]biz are still online and functioning.


🚨 Suspected admin of xss.is, a top Russian-speaking cybercrime forum, was arrested in Ukraine.
The suspect, active for nearly 20 years, allegedly made €7M facilitating cybercrime.
🇫🇷🇺🇦🇪🇺 Operation led by France with Europol support.
europol.europa.eu/media-pres…

Lawrence Abrams retweeted
Microsoft releases emergency patches for SharePoint RCE flaws exploited in attacks - @LawrenceAbrams
bleepingcomputer.com/news/mi…
bleepingcomputer.com/news/mi…

🚨 Don’t miss our upcoming BleepingComputer webinar with @specopssoftware and @SCMagazine!
We'll discuss how stolen credentials and identity-based attacks have become a favorite way to break into networks.
🗓️July 9th at 2 PM ET
➡️Register here: scworld.com/cybercast/stolen…

FYI, the repackaged AT&T data breach leak on XSS is from the 2021 breach, not the April 2024 Snowflake data theft attacks.
Data matches the 2021 data leaked in March 2024.
bleepingcomputer.com/news/se…

ShinyHunters is the threat cluster to track this year.
They, or threat actors claiming to be, are behind a lot of the attacks we are seeing.
bleepingcomputer.com/news/se…

Looks like RansomEXX ransomware op is still around. 👋
bleepingcomputer.com/news/se…

Lawrence Abrams retweeted

🚨 How was Black Basta structured? What were its members’ roles? How did its infrastructure operate?
Leaked chats reveal a highly organized ransomware group with defined leadership, internal teams, and external affiliates.
More in my article ⬇️
cybercrimediaries.com/post/b…

Lawrence Abrams retweeted

I’ve had a few people flag this with me as a “data breach”. It’s not, it’s authorised access. Not liking that authorisation does not make it a data breach. If one of these guys then accidentally leaks it all over the place to unauthorised parties, *then* it’s a data breach!

“This is the...largest IT security breach in our country’s history.... You can’t un-ring this bell. Once these DOGE guys have access to these data systems, they can ostensibly do with it what they want.” theatlantic.com/technology/a…

Lawrence Abrams retweeted

hackerone.com/reports/295796… is a good example to what platforms should fight against (but they do not!) : low quality hunters. Those guys are taking a lot of resources (and energy) to be managed. That lowers the quality for us all.
#hackerone #bugbounty

Lawrence Abrams retweeted

Wow: USAID paid Microsoft to shut down Windows Phone because it was too secure for the CIA to spy on it
Lawrence Abrams retweeted

New unverified breach: Data allegedly taken from Brazilian lead gen platform Speedio was posted for sale last week. It included 27M email addresses along with company names, addresses and phone numbers. 51% were already in @haveibeenpwned. Read more: darkwebinformer.com/a-threat…
