

@LundukeJournal
Account based inUnited States
About this account
- Account based in
- United States
- Connected via
- United States App Store
Account-level information from X, not a live location or the device used for a specific post.
Tech Journalism with zero ads, & zero Big Tech influence. We cover the Big Tech stories that other publications are afraid to touch.
Joined July 2021
- Tweets10K
- Following682
- Followers39.5K
- Likes48.5K




Number of Conservative led Software Companies, Software Foundations, & Open Source Projects which…
Discriminate based on Race: 0
Discriminate based on Sex: 0
Discriminate based on Religion: 0
Discriminate based on Political Views: 0
Advocate for violence against those they disagree with: 0
Zero.
It’s *always* Leftists.
And Leftists leaders, throughout the computer industry, do all of those things. A *lot*.
The editor and Tech Journalist of OSNews says that the USA and Israel are “F**king war criminal c*nts”.
Background: That particular Tech Journalist, Thom Holwerda, has a long history of attacking Conservatives, Christians, Jews, and Americans… having previously encouraged people to hunt me down and murder me.
Side note: Why do Leftists swear so much?

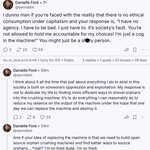
The leader of the elementary OS Linux distribution is very, very angry at capitalism.
“There is no ethical consumption under capitalism.”
He (a man who believes he is a woman) refers to capitalism as an “orphan crushing machine”, says he “[does] everything I can reasonably do” to “replace the machine and destroy it.”
Destroying Capitalism and replacing it with Marxism is a commonly stated goal of many such Leftists within leadership positions of Open Source.

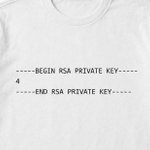
The Indian root Certificate Authority, eMudhra, who caused massive security issues, by setting the private keys of several certificates to easily guessable numbers (such as “4”), has announced that they are going to “Exit the global SSL/TLS Certificate Business”.
Amusing tidbit: eMudhra used the opportunity to claim that they were acting responsibly by “revoking the affected [certificates] within 14 hours of discovery”… after having created the security nightmare… a year and a half earlier.

Super, duper cool.

Left: the humble browser I built for SerenityOS in 2019
Right: SerenityOS running inside an x86 VM (wasm) hosted by that same browser, now all grown-up as @ladybirdbrowser 🤓


Last year, Mullvad (a VPN company) co-founder Daniel Berntsson gave a personal donation of roughly $500k USD to the Swedish Örebro Party -- a political party which calls for stricter immigration policies and "extensive remigration".
What happened next is... predictable.
According to reports, roughly a quarter of the staff of Mullvad joined an internal chat criticizing the donation, with many calling for Berntsson to resign. Which Berntsson refused to do.
After several Leftist outlets in Europe criticized the donation, @mullvadnet issued a statement supporting the co-Founders right to make any donation he wants... but offering customers upset by this a refund on their services.
Then Tor got involved.
Mullvad is the single largest contributor to the Tor Project, providing well over $1 Million USD annually. As you might guess... this made the Leftists very angry.
"highly racist, white supremacist"
"it is the reason I have had to resign as a Tor Browser developer"
With some calling for "a clean break" from "Nazi CEOs".
Tor responded to these attacks with the following statement:
"Tor Project has paused proactive co-branding with Mullvad. That pause applies to joint promotional activity while the technical collaboration continues in alignment with our narrowly scoped agreement. We have also reviewed how Mullvad Browser is described and endorsed on our owned channels, and clarified language suggesting broader alignment between our values. These changes are intended to describe the relationship more accurately and avoid notions of implied endorsement."
The @torproject then by changing the way they describe their relationship with Mullvad from "great value alignment" to a "a narrowly-scoped technical collaboration".
This, as you can imagine, made the Leftists even angrier (because they always get angrier... no matter what).
The attacks on Tor intensified, with Leftists calling their position: "if we get money from right-wing extremists, well, we take it".


Getting LCOS certified as UNIX is *technically* possible -- and would be tremendously amusing.
However, the cost is... a lot. Looks like it would cost roughly $30,000 per year (give or take) to get the official certification.

After the FOSDEM conference rejected a "DEI Devroom" track, Leftists of Open Source are attempting to push forward DEI activism at the largest Open Source conference in Europe.
Here we see the Executive Director of the Software Freedom Conservancy talking about both shoehorning DEI lectures into other (non-DEI) tracks... as well as being part of a "DEI side event" taking place right outside the conference.
Many are attempting to organize such a "DEI event" on the streets directly in front of FOSDEM.


With the PHP security news, it's worth taking a moment to look at the current leadership of PHP.
The Executive Director of the PHP Foundation, Elizabeth Barron (Naramore), has built a career on pushing DEI and Leftist politics in software.
- Worked on "Code of Conduct" and "Developer Inclusion" at GitHub.
- Cofounded a "women and non-binary individuals" PHP organization.
- Worked at The Linux Foundation (CHAOSS) where she wrote a "2021 DEI Audit".
- Her X bio used to read: "DEI in Open Source".
- Regularly posted anti-Trump, anti-MAGA, anti-White, and pro-Baby Murder statements on her @ElizabethN account.
Since becoming the PHP Executive Director she has:
- Started an "Accessibility & Inclusion group".
- Started an initiative to onboard "marginalized and underrepresented groups".


LCOS 0.9.5 Has Landed!
Fixes! More hardware support! 1.0 arrives Nov 1st!
lunduke.com/lcos.html

Indian Root Certificate Authority Sets Private Key to 4
Anyone has been able to make fake HTTPS certificates for over a year.
Many years back, I made a statement that “HTTPS is dangerous” due to significant, and obvious, problems in the design of the Certificate Authority system.
The core point I made: A small, simple mistake with a Root Certificate Authority has massive impacts throughout the system, making it highly likely that there were untold numbers of “fake” certificates which were “trusted”.
It is a “security based on trust” system, where we are asked to blindly trust dozens upon dozens of Root Certificate Authority organizations (from countries around the world) to never make a single mistake (or implement any backdoors for any government they are beholden to).
It is, quite simply, a design that appears specifically made to be abused and manipulated.
I was told that I did not understand how CA’s work.
I was mocked and ridiculed.
Well… as a wise man once said…
Who’s laughing now, Wayne?!
In April of 2025, eMudhra (an Indian Certificate Authority), published 8 intermediate CA keys which were so weak that a small child could guess the numbers in a few seconds.
One of the private keys was, literally, 4.
Just… 4.
This massive problem was not made public until October 17th of this year, when it was discovered by an anonymous guy on the Internet who goes only by “Wayne” (like “Cher”…. but… “Wayne”).
What this means in practical terms: It has been trivially simple, for the last year and a half, to create fake “secure” HTTPS certificates. (One person even created a fake HTTPS certificate for a Google.com subdomain.)
It took Mozilla 3 days, after learning about this (from “Wayne”), before they updated their certificate list (which many open source projects — including curl and Python — rely upon).
As of this moment, many systems are still vulnerable (including macOS).


The progress the @omarchy crew is making in adding hardware support is astoundingly impressive. Latest Apple Silicon Mac Mini is now booting Linux.


In April of 2025, eMudhra (an Indian Certificate Authority), published 8 intermediate CA keys which were so weak that a small child could guess the numbers in a few seconds.
One of the private keys was, literally, 4.
Just… 4.
This massive problem was not made public until October 17th of this year, when it was discovered by an anonymous guy on the Internet who goes only by “Wayne” (like “Cher”…. but… “Wayne”).
What this means in practical terms: It has been trivially simple, for the last year and a half, to create fake “secure” HTTPS certificates. (One person even created a fake HTTPS certificate for a Google.com subdomain.)
It took Mozilla 3 days, after learning about this (from “Wayne”), before they updated their certificate list (which many open source projects — including curl and Python — rely upon).
As of this moment, many systems are still vulnerable (including macOS).